

CVE-2026-95664
 oscerd/cve-2026-95664
Runnable Spring Boot and Quarkus reproducer for CVE-2026-95664, demonstrating Simple expression injection via the CamelAwsS3Key header in…
defensive-toolseducationexploitation+2
oscerd/cve-2026-95664Runnable Spring Boot and Quarkus reproducer for CVE-2026-95664, demonstrating Simple expression injection via the CamelAwsS3Key header in…
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
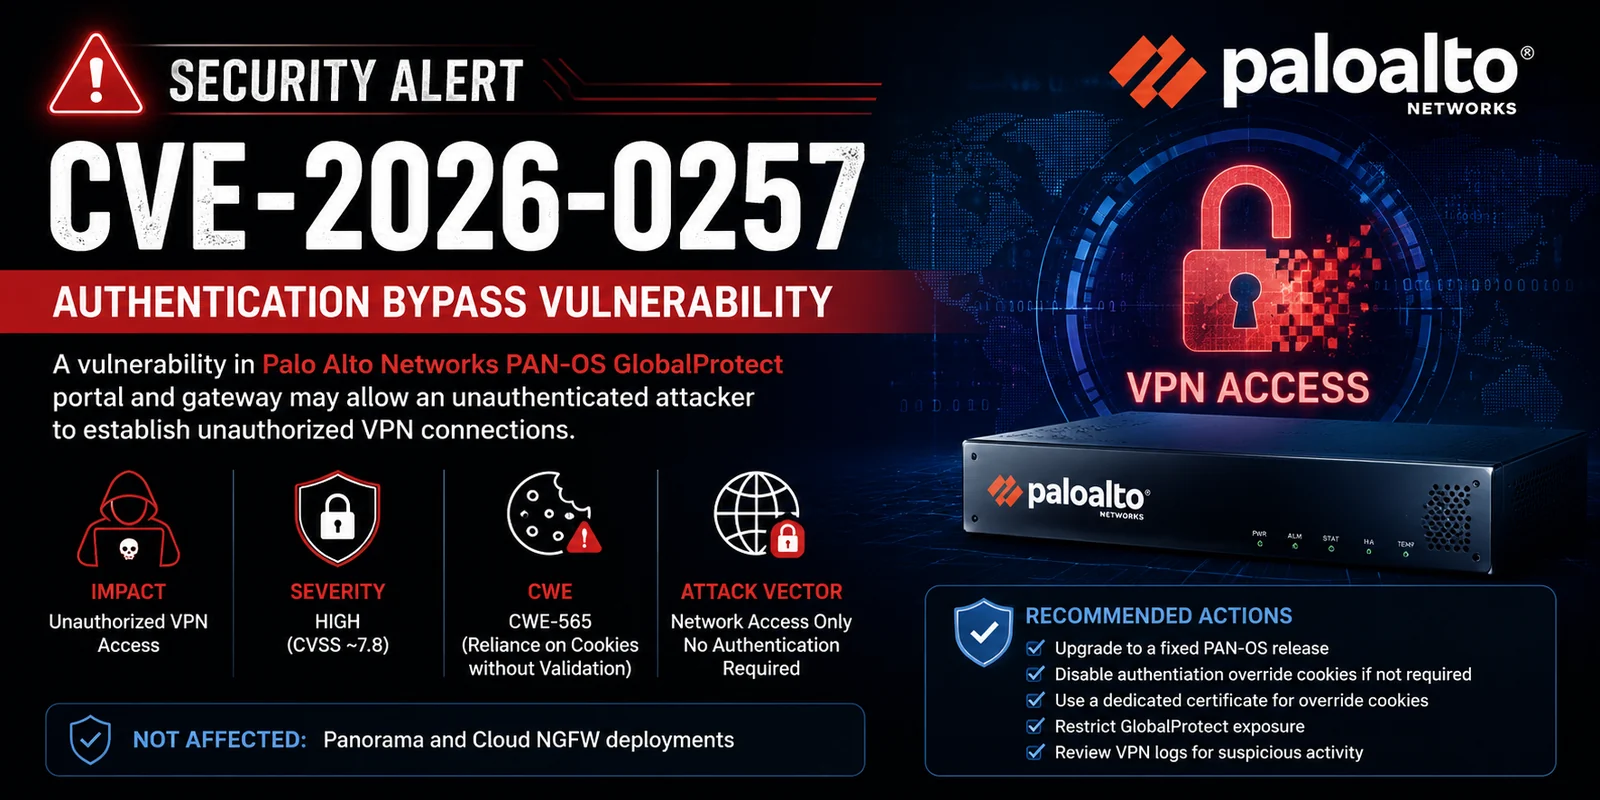 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 guila95/cve-2026-86426
Proof-of-concept and recon framework for CVE-2026-86426, a LibreNMS API authentication bypass via type confusion, extracting SNMP credentials and…
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 abraxas/ats-magick-unsigned
Apache Traffic Server 10.2.0 - High - Remote - File write - unsigned magick convert writes as nobody
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 domssilva/vulnsearch
A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 0xblackash/cve-2026-101767
Advisory and technical research analysis of CVE-2026-101767, a critical unauthenticated RCE in Oracle E-Business Suite Application Object Library,…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 4rdr/proofs
Collection of CVE findings, proof-of-concept references, and vulnerability research notes, including ExploitDB entries and credited security…
 laremontada12/cve-2026-39987-marimo-preauth-rce
CVE-2026-39987 Marimo Pre-auth RCE research, Docker lab reproduction, root cause analysis, and patch validation.
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.