
arcgis-web-shell
 ryanpohlner/arcgis-web-shell
ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
exploitationpayload-developmentpenetration-testing+5
5
ryanpohlner/arcgis-web-shellArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
 oscerd/cve-2026-90885
Runnable proof-of-concept reproducer for CVE-2026-90885, an XXE (CWE-611) in Apache Camel camel-saxon XQuery, with Spring Boot and Quarkus builds and…
 oscerd/cve-2026-95628
Runnable proof-of-concept reproducer for CVE-2026-95628, an absolute-path validation gap in Apache Camel camel-docling, with Spring Boot and Quarkus…
 oscerd/cve-2026-95629
Runnable proof-of-concept reproducer for CVE-2026-95629, a path-traversal flaw in Apache Camel camel-docling where the output-path header reaches…
 oscerd/cve-2026-95664
Runnable Spring Boot and Quarkus reproducer for CVE-2026-95664, demonstrating Simple expression injection via the CamelAwsS3Key header in…
 gmh5225/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
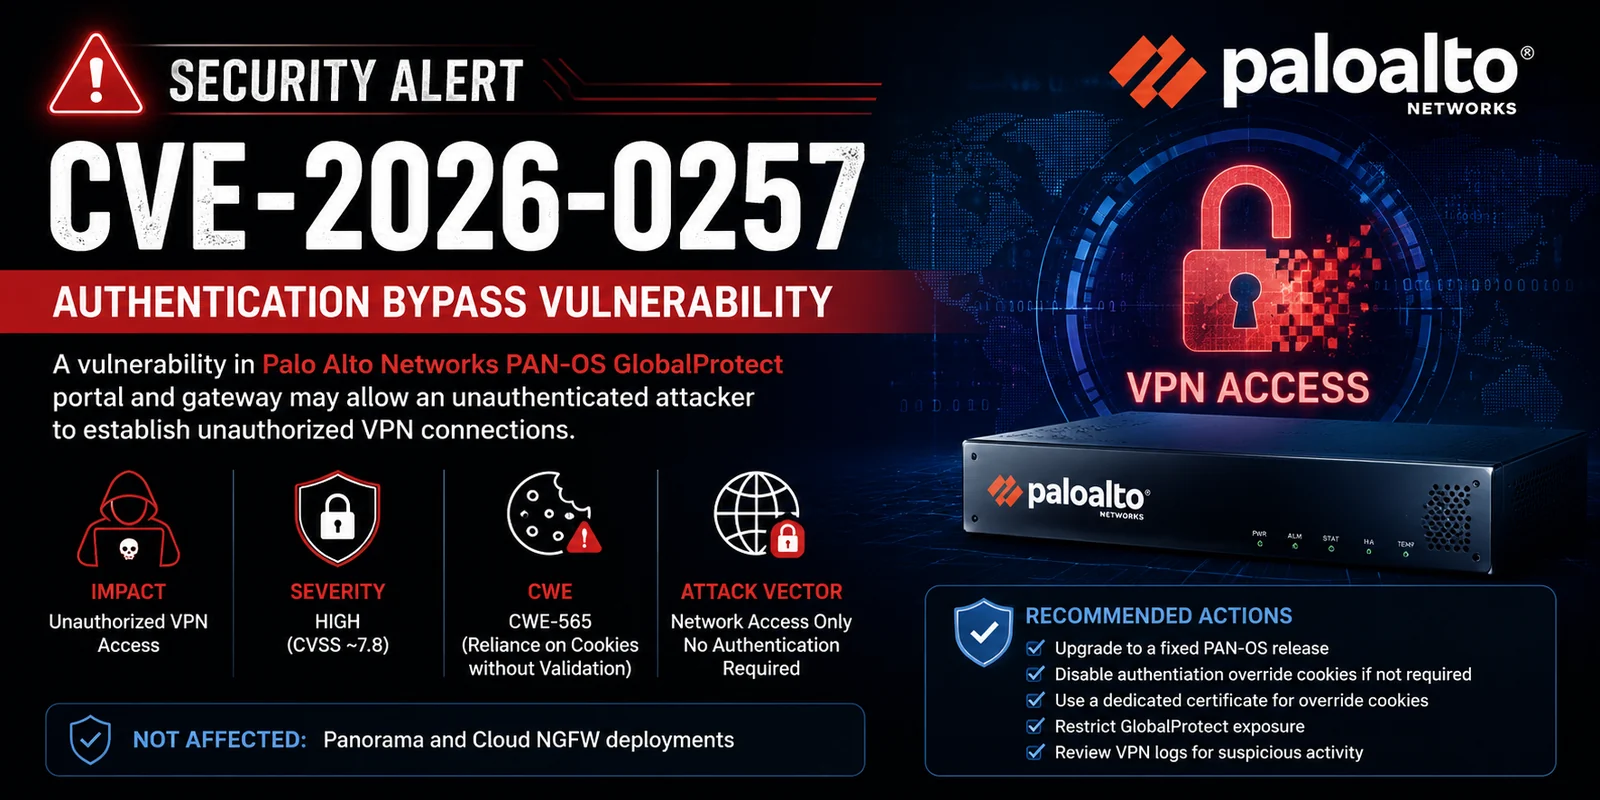 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
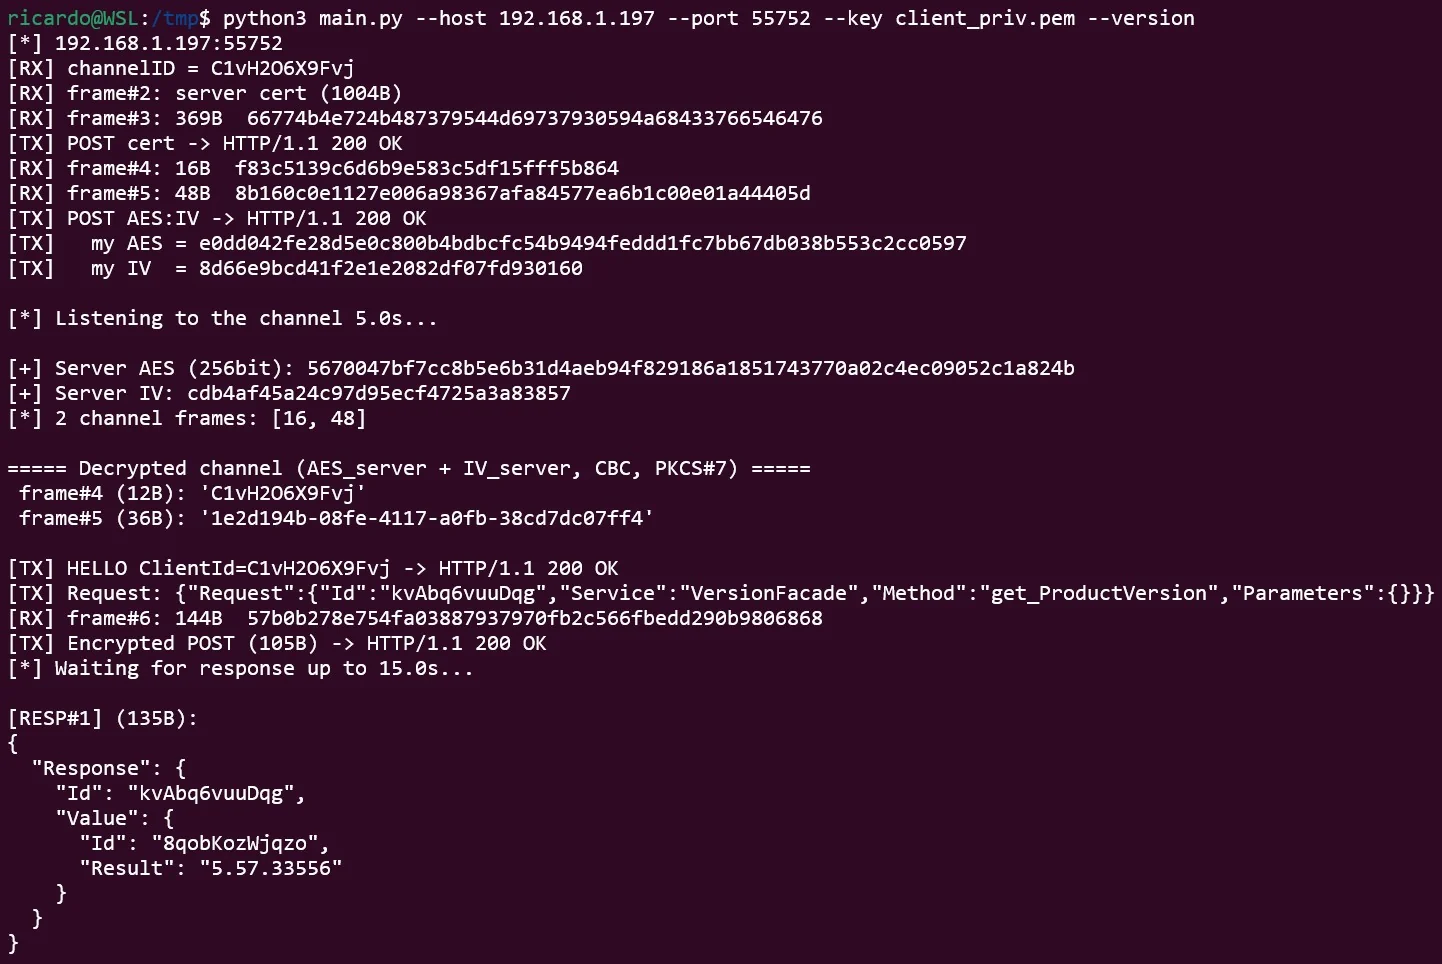 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 d4t4s3c/offensivereverseshellcheatsheet
Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 inforcqb-self/cve-2026-0013-exploit
Proof-of-concept exploit code for CVE-2026-0013, demonstrating the vulnerability for research and validation purposes.
 iamlucif3r/cve-2026-109618-exploit
[PHP2Shell] Golang exploit for CVE-2026-109618 / CVE-2026-109619: Unauthenticated RCE in PHP 5.4–8.5.11 via OOM corruption + session.upload_progress…
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 guila95/cve-2026-86426
Proof-of-concept and recon framework for CVE-2026-86426, a LibreNMS API authentication bypass via type confusion, extracting SNMP credentials and…
 thejesterrrr/cve-2026-19632
Proof-of-concept code and reproduction details for CVE-2026-19632, demonstrating the vulnerability's trigger conditions and impact.
 0xgh057r3c0n/php2shell
One-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.