
XSS-Payloads
 7iosecurity/xss-payloads
Collection of cross-site scripting (XSS) payloads for web application security testing, filter bypass research, and penetration testing engagements.
curated-resourcespayload-developmentpenetration-testing+2
49
7iosecurity/xss-payloadsCollection of cross-site scripting (XSS) payloads for web application security testing, filter bypass research, and penetration testing engagements.
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 xsuperbug/payloads
Collection of PHP-based attack payloads for web exploitation and penetration testing scenarios.
 ryanpohlner/arcgis-web-shell
ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
 gmh5225/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
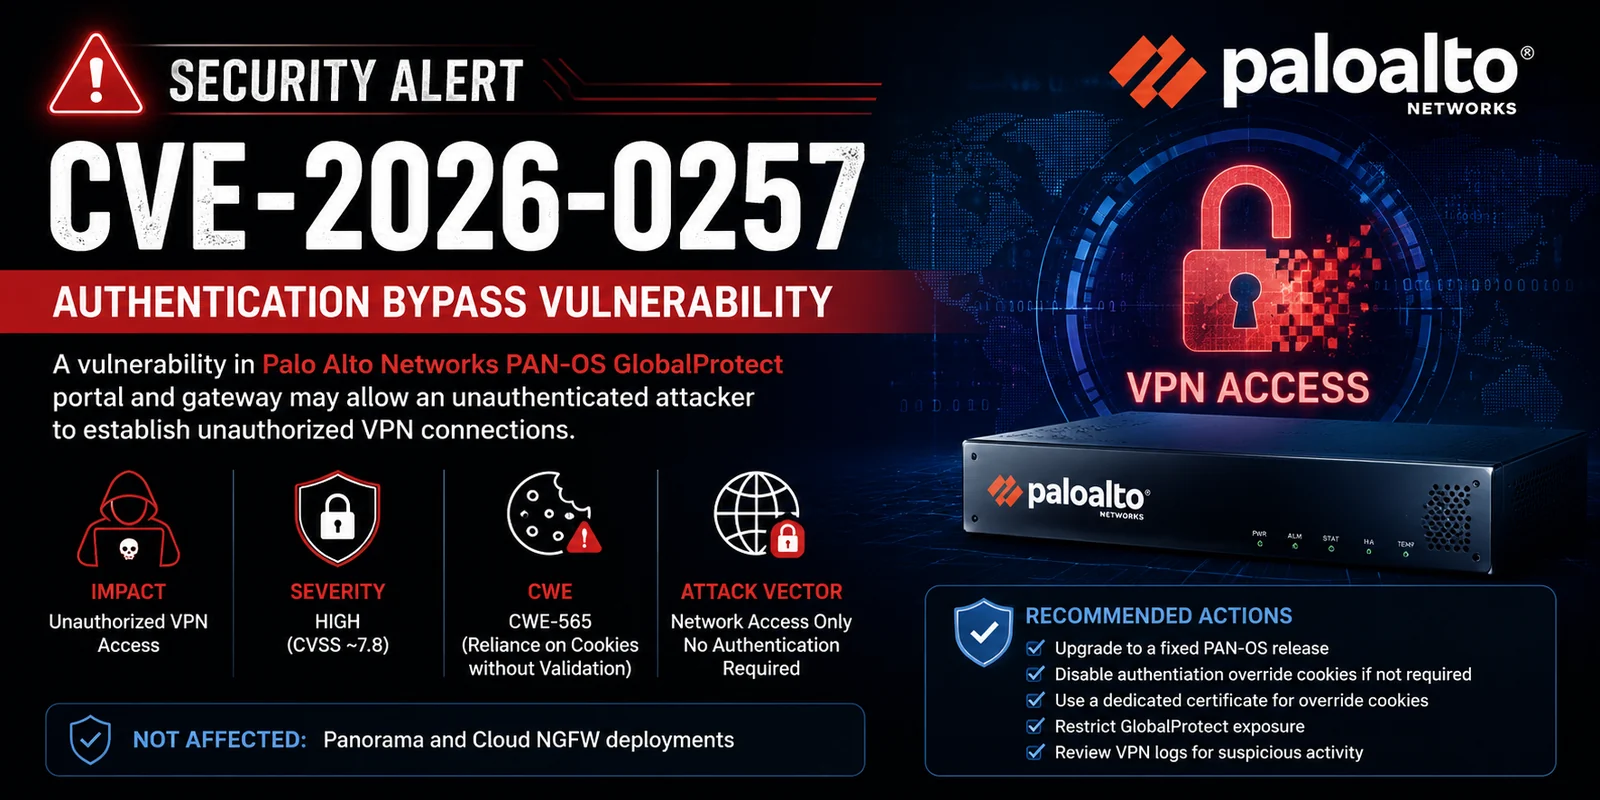 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
 inforcqb-self/cve-2026-0013-exploit
Proof-of-concept exploit code for CVE-2026-0013, demonstrating the vulnerability for research and validation purposes.
 thejesterrrr/cve-2026-19632
Proof-of-concept code and reproduction details for CVE-2026-19632, demonstrating the vulnerability's trigger conditions and impact.
 0xgh057r3c0n/php2shell
One-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 moisestapia/twapt
Deploy your own lab of web application penetration testing with docker and docker-compose, webgoat, dvwap, bwapp and Juice Shop
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
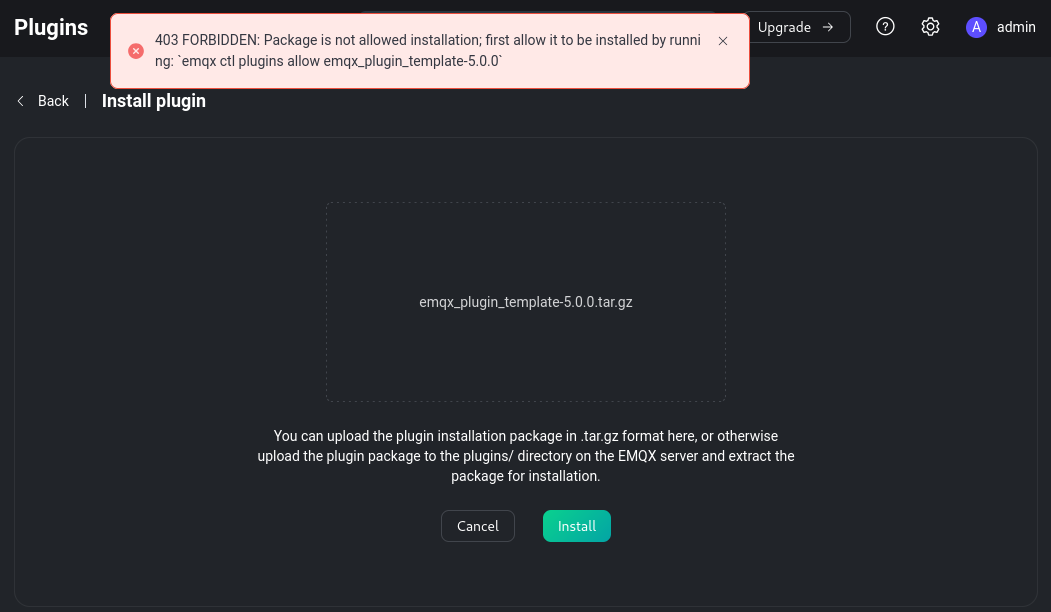 ricardojoserf/emqx-rce
EMQX Dashboard Malicious Plugin leading to RCE
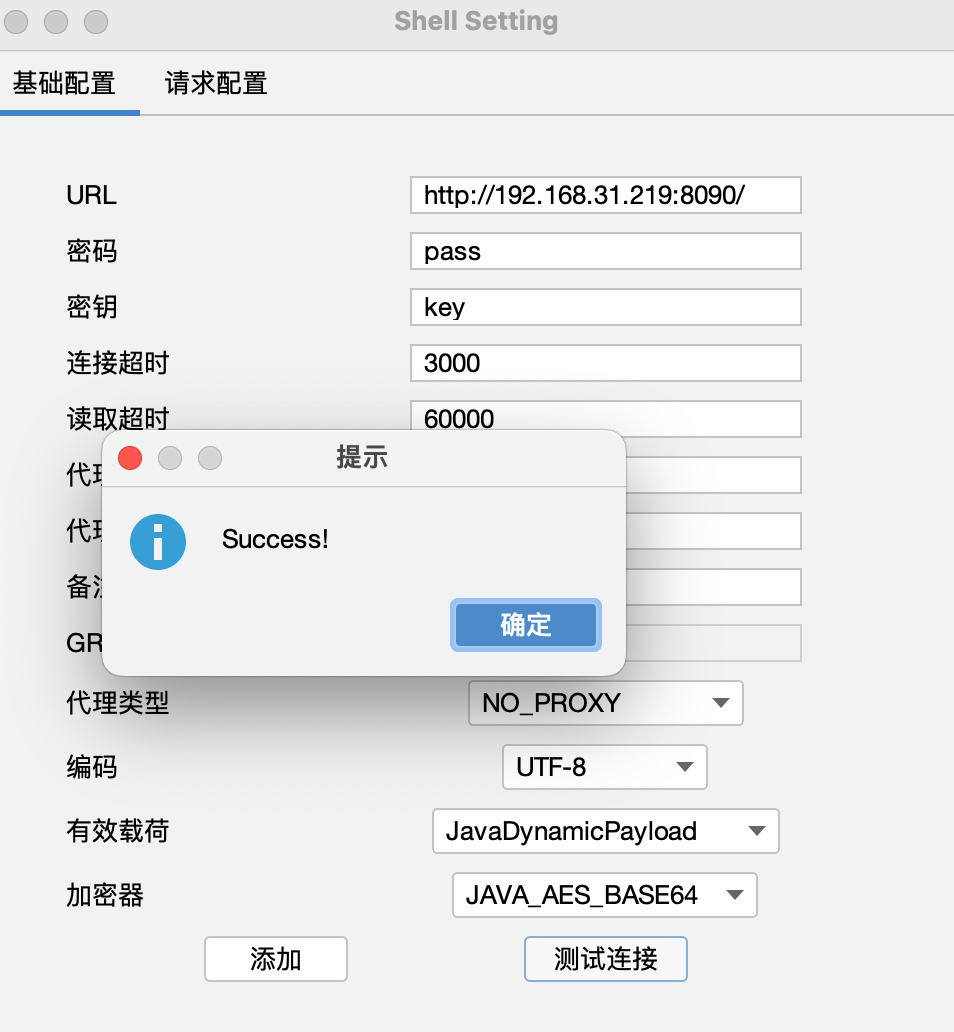 lotus6/confluencememshell
Confluence CVE 2021,2022,2023 利用工具,支持命令执行,哥斯拉,冰蝎 内存马注入