

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.7k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 mzfr/liffy
Local file inclusion exploitation tool
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
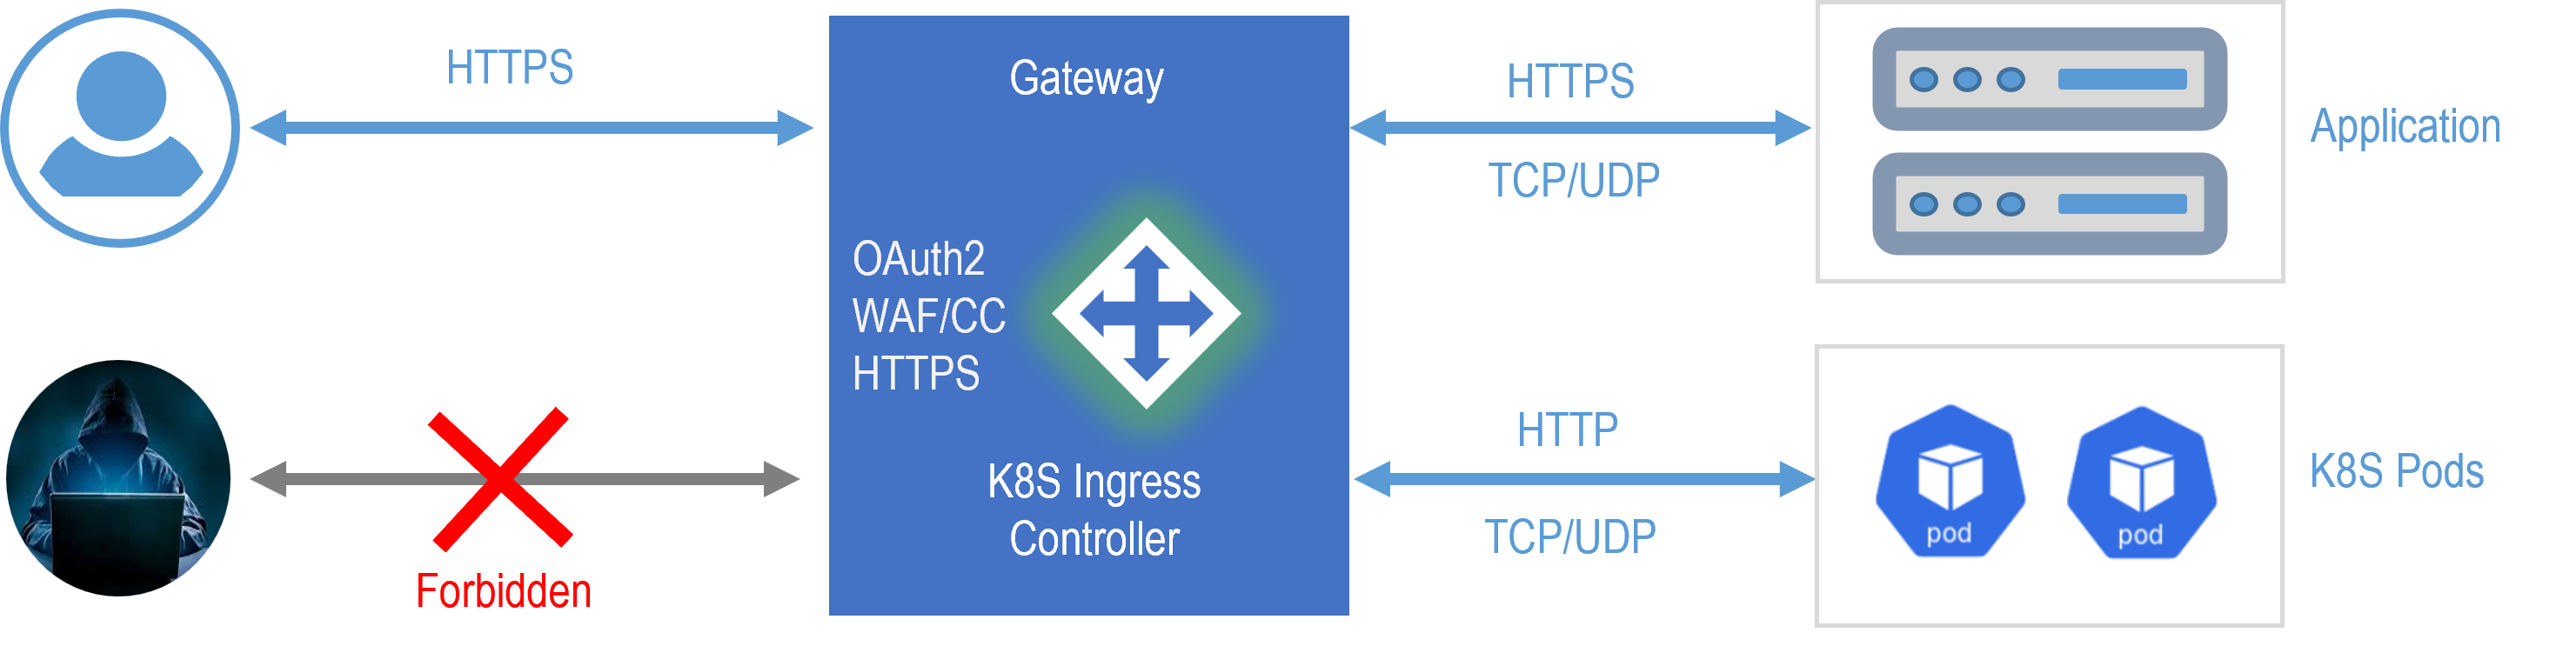 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 clouedoc/autosqli
An automatic SQL Injection tool which takes advantage of ~DorkNet~ Googler, Ddgr, WhatWaf and sqlmap.
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 papamica/waf-checker
Tests your WAF with +160 payloads