

forbidden
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
fuzzingids-ips-evasioninformation-gathering+5
257
ivan-sincek/forbiddenBypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 fabdotnet/cve-2023-27100
Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 yosasasutsut/blackash-cve-2025-53770
Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…
 ianxtianxt/burpsuiefakeip
burp伪造ip爆破脚本
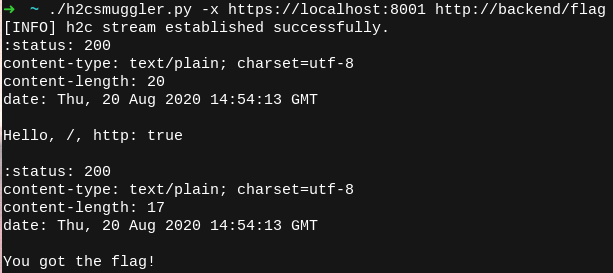 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
 nbs-system/naxsi
NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 d00movenok/htmlsmuggler
✉️ HTML Smuggling generator&obfuscator for your Red Team operations
 zecure/shadowd
The Shadow Daemon web application firewall server
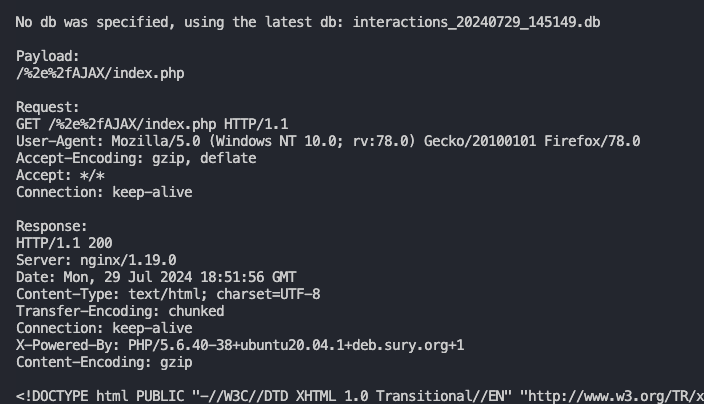 intrudir/bypassfuzzer
Fuzz 401/403/404 pages for bypasses
 nccgroup/demiguise
HTA encryption tool for RedTeams