

ARTEX
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
ai-securityinformation-gatheringnetwork-mapping+9
855
baarai/artexLLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 pulentoski/cve-2024-23897-arbitrary-file-read
Un script realizado en python para atumatizar la vulnerabilidad CVE-2024-23897
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 87achrafg-stack/cve-2026-5513
CVE-2026-5513 — Bookly ≤ 27.2 Stored XSS via Cookie
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 osyanina/westone-cve-2021-21980-scanner
A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.
 splinters-io/blinder
Content-blind reverse proxy for exposure-protected security scanning
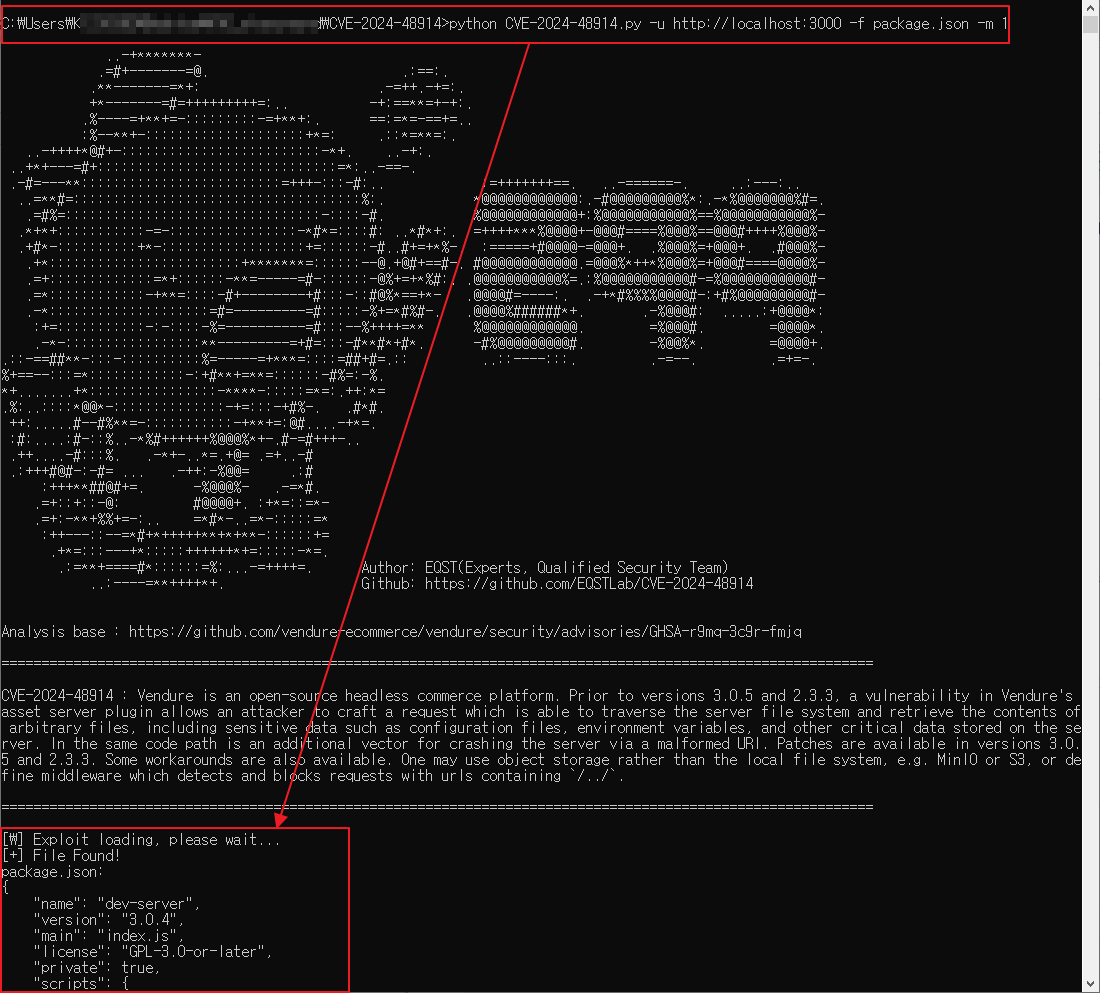 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit