
Advanced-SQL-Injection-Cheatsheet
 kleiton0x00/advanced-sql-injection-cheatsheet
A cheat sheet that contains advanced queries for SQL Injection of all types.
curated-resourceseducationpenetration-testing+4
3.3k
kleiton0x00/advanced-sql-injection-cheatsheetA cheat sheet that contains advanced queries for SQL Injection of all types.
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
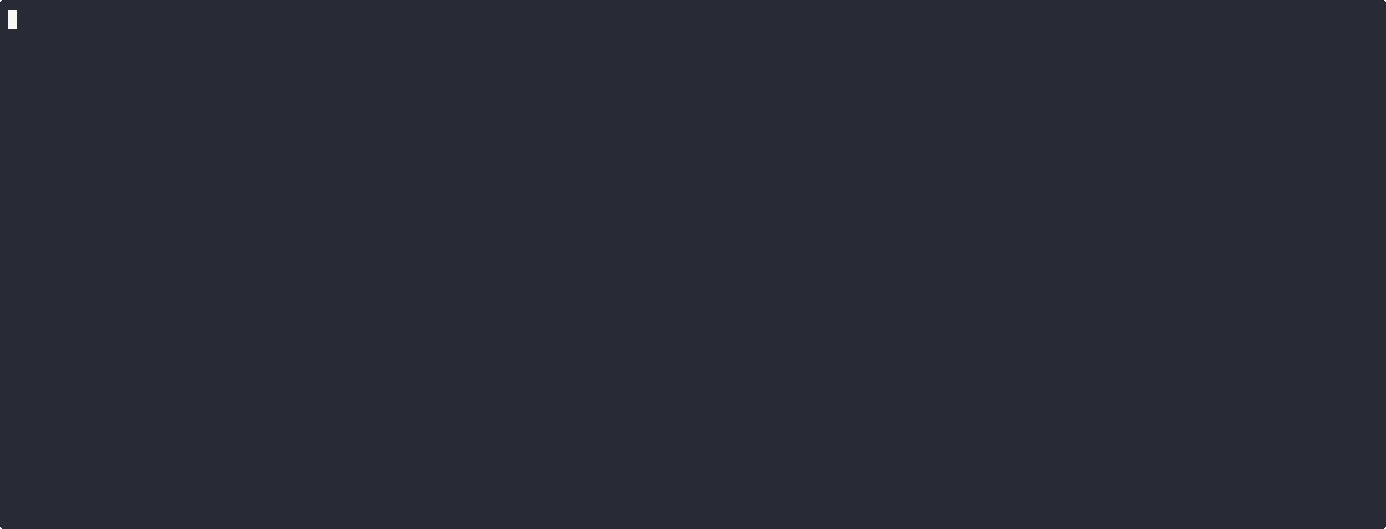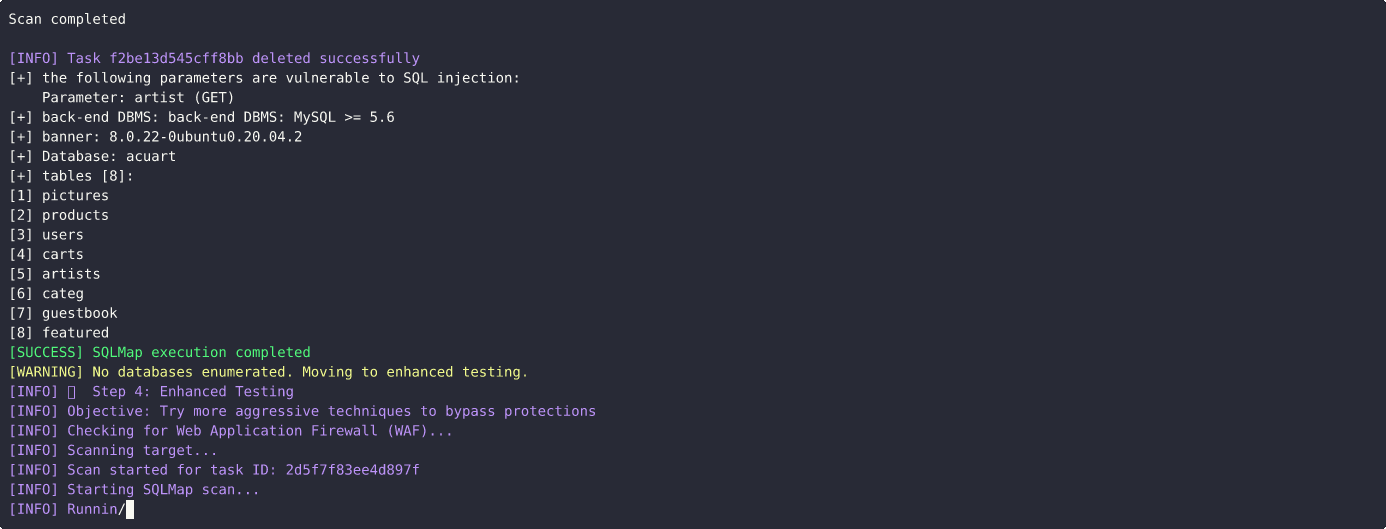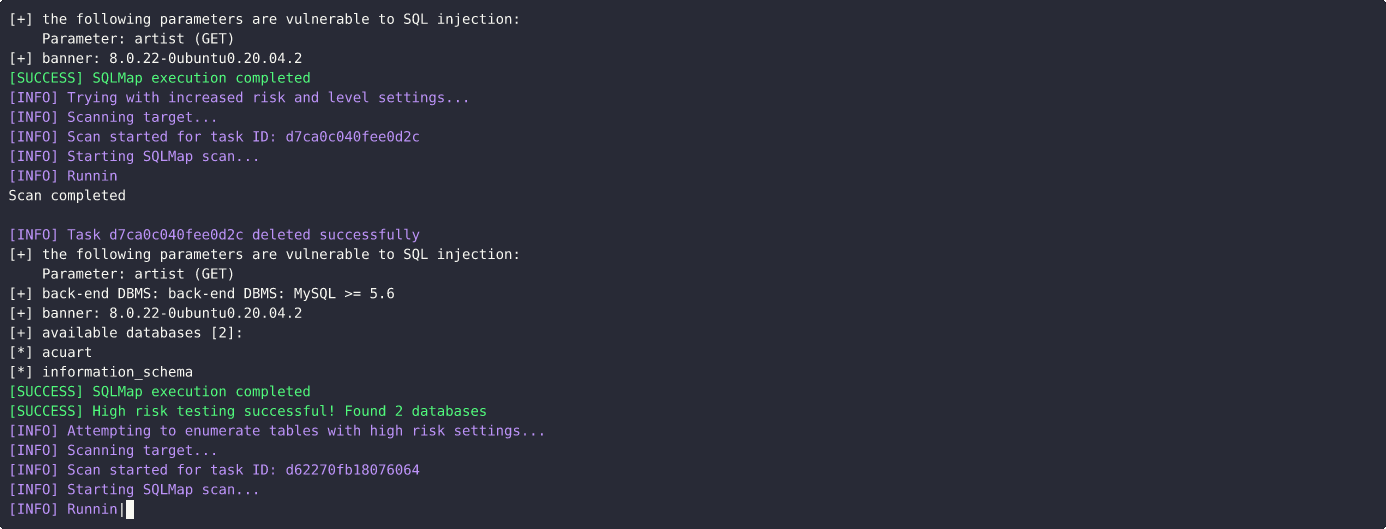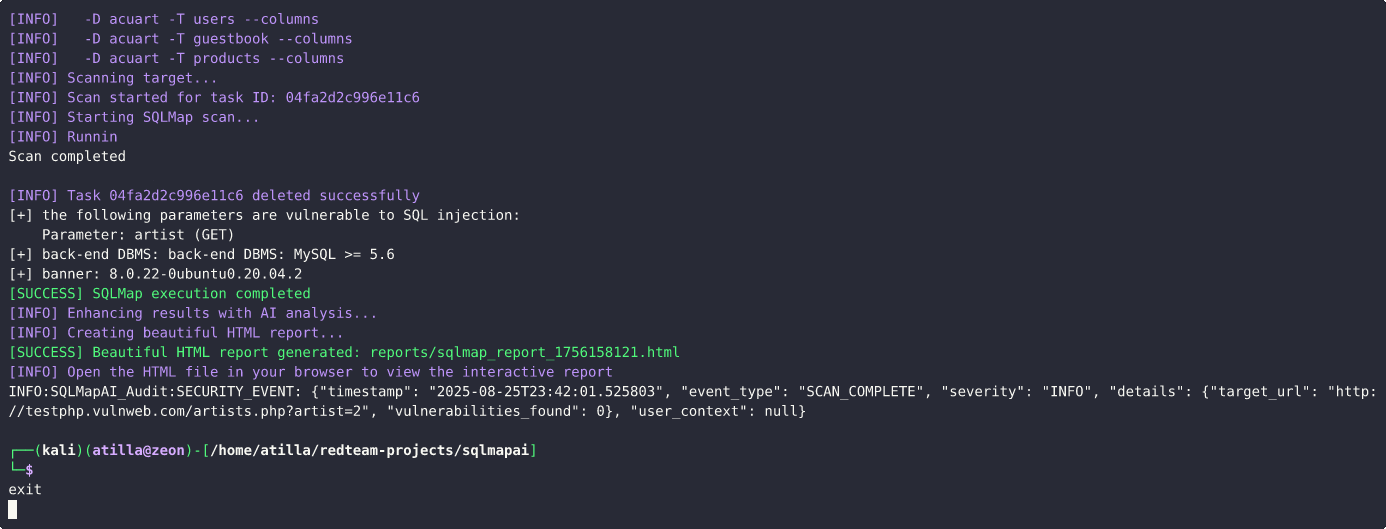 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 keramas/mssqli-duet
SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing
 z3rodayhacks/cve-2026-63030-cve-2026-60137
Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
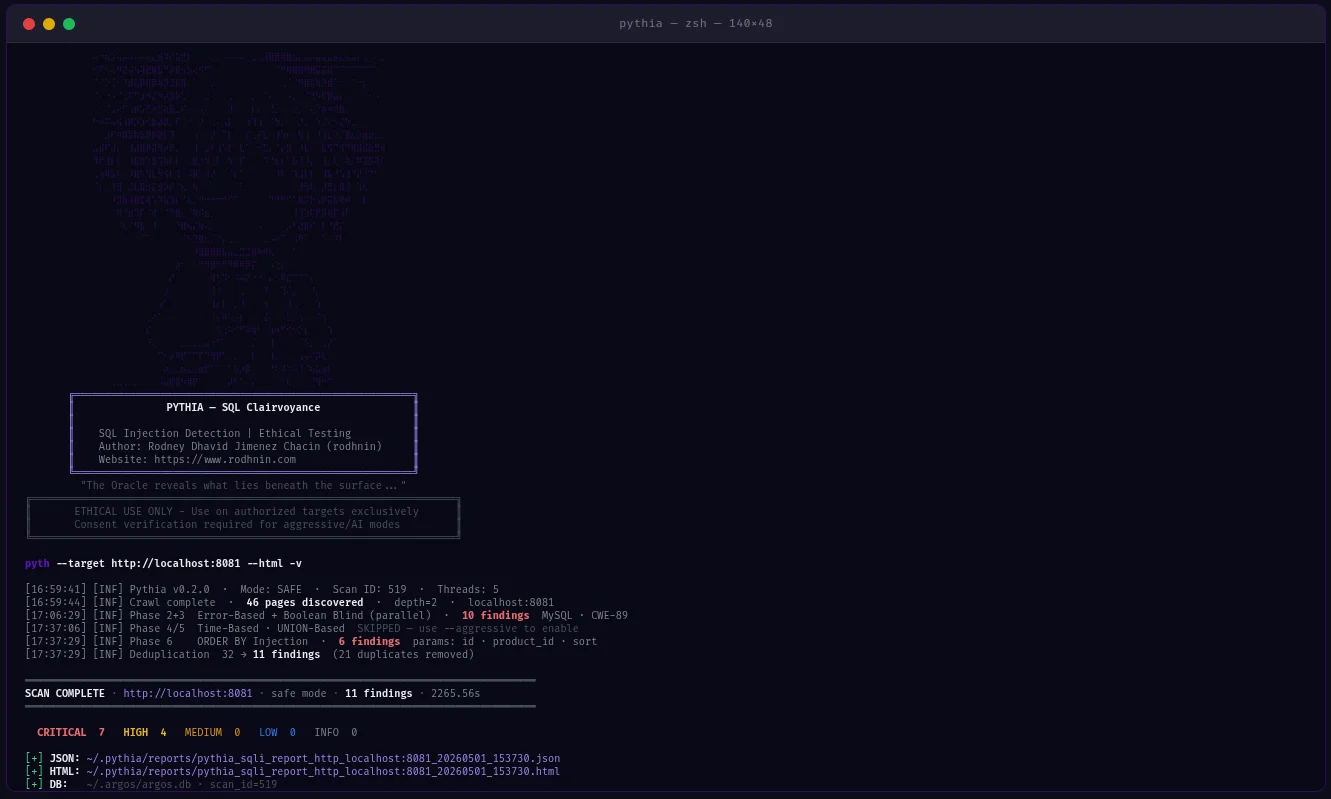 rodhnin/pythia-sql-clairvoyance
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 imbas007/cve-2025-32429-checker
Python-based vulnerability scanner for detecting CVE-2025-32429 SQL injection in XWiki platforms. Supports single/bulk scanning, WAF detection,…
 clouedoc/autosqli
An automatic SQL Injection tool which takes advantage of ~DorkNet~ Googler, Ddgr, WhatWaf and sqlmap.
 bytereaper77/cve-2025-41373
PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 0xhaggis/imperva_gzip_bypass
Exploit for CVE-2021-45468, an Imperva WAF bypass.
 d3vilbug/hackbar
HackBar plugin for Burpsuite
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
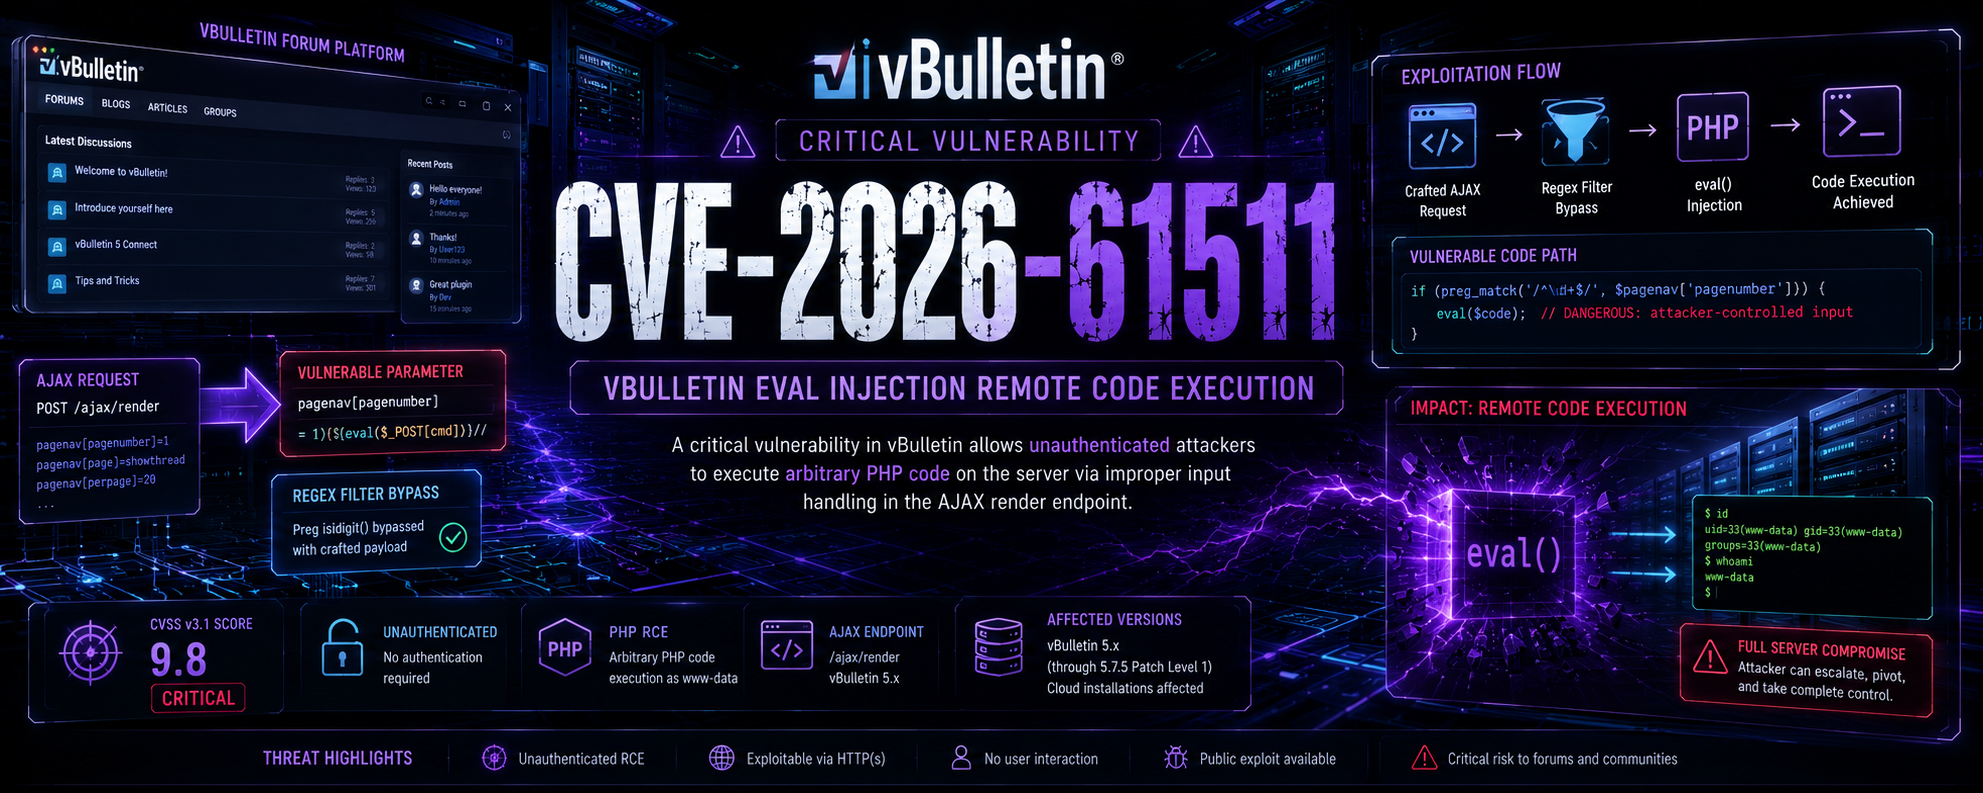 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…