
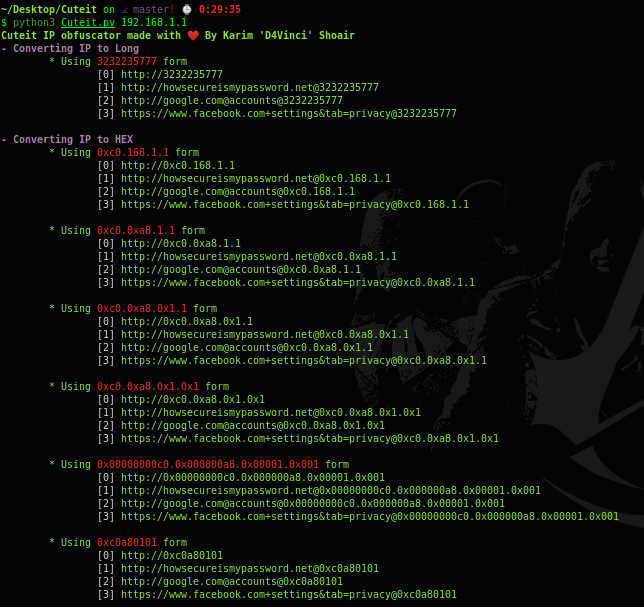
Cuteit
 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
command-and-controlids-ips-evasionpayload-generation+4
d4vinci/cuteitIP obfuscator made to make a malicious ip a bit cuter
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
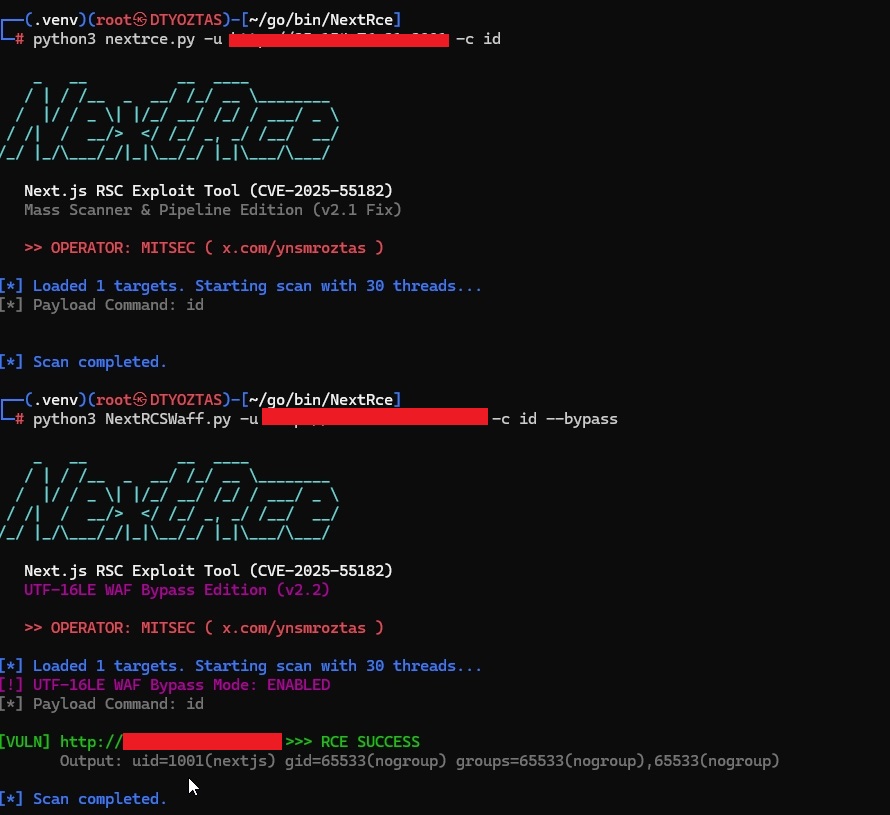 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 pyroxenites/nextjs_rce_exploit_tool
Exploit for CVE-2025-55182 & CVE-2025-66478
 hackersatyamrastogi/react2shell-ultimate
React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
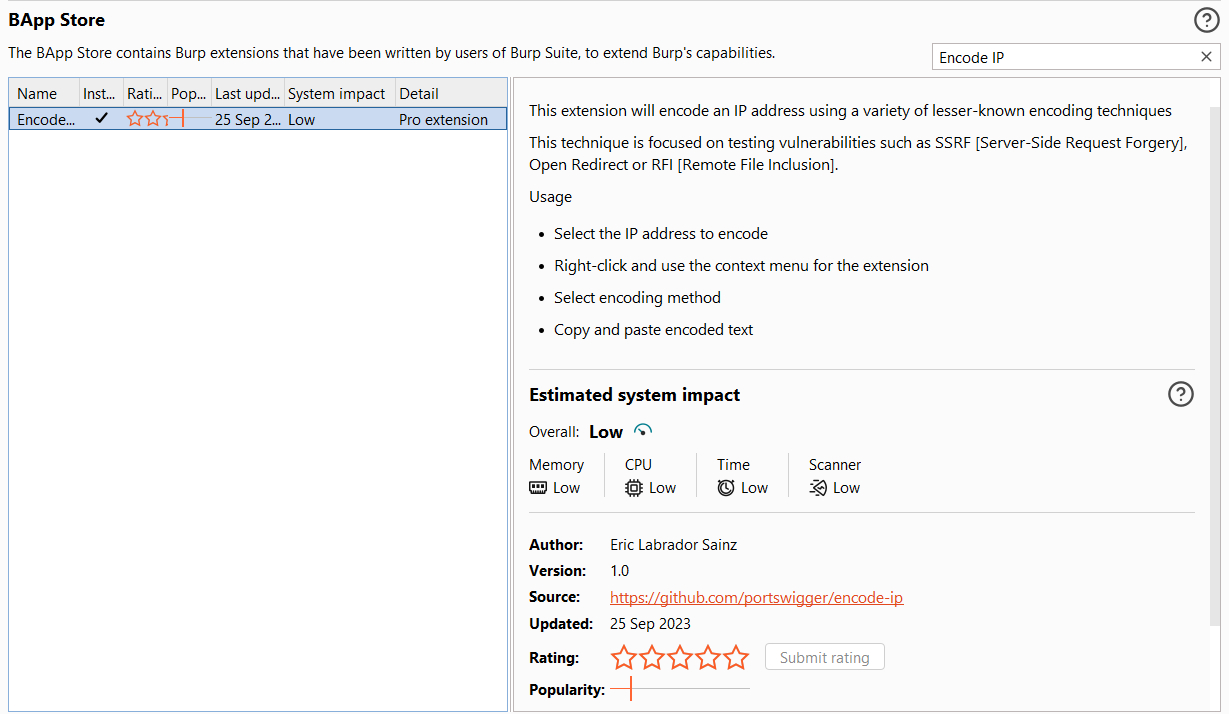 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 night-have-dreams/php-cgi-injector
一個測試CVE-2024-4577和CVE-2024-8926的安全滲透工具
 soltanali0/cve-2025-64446-exploit
Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.
 cybersecurityworks553/log4j-shell-csw
A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 weizman/cve-2020-6519
Proof-of-concept exploit for CVE-2020-6519 - a Chromium zero-day that fully bypasses Content Security Policy (CSP) across platforms, enabling script…