

Zeus-Scanner
 ekultek/zeus-scanner
Advanced reconnaissance utility
captcha-bypassinformation-gatheringport-scanning+4
ekultek/zeus-scannerAdvanced reconnaissance utility
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 yagamiilight/cerberus
一款功能强大的漏洞扫描器,子域名爆破使用aioDNS,asyncio异步快速扫描,覆盖目标全方位资产进行批量漏洞扫描,中间件信息收集,自动收集ip代理,探测Waf信息时自动使用来保护本机真实Ip,在本机Ip被Waf杀死后,自动切换代理Ip进行扫描,Waf信息收集(国内外100+款waf信息)包括安全…
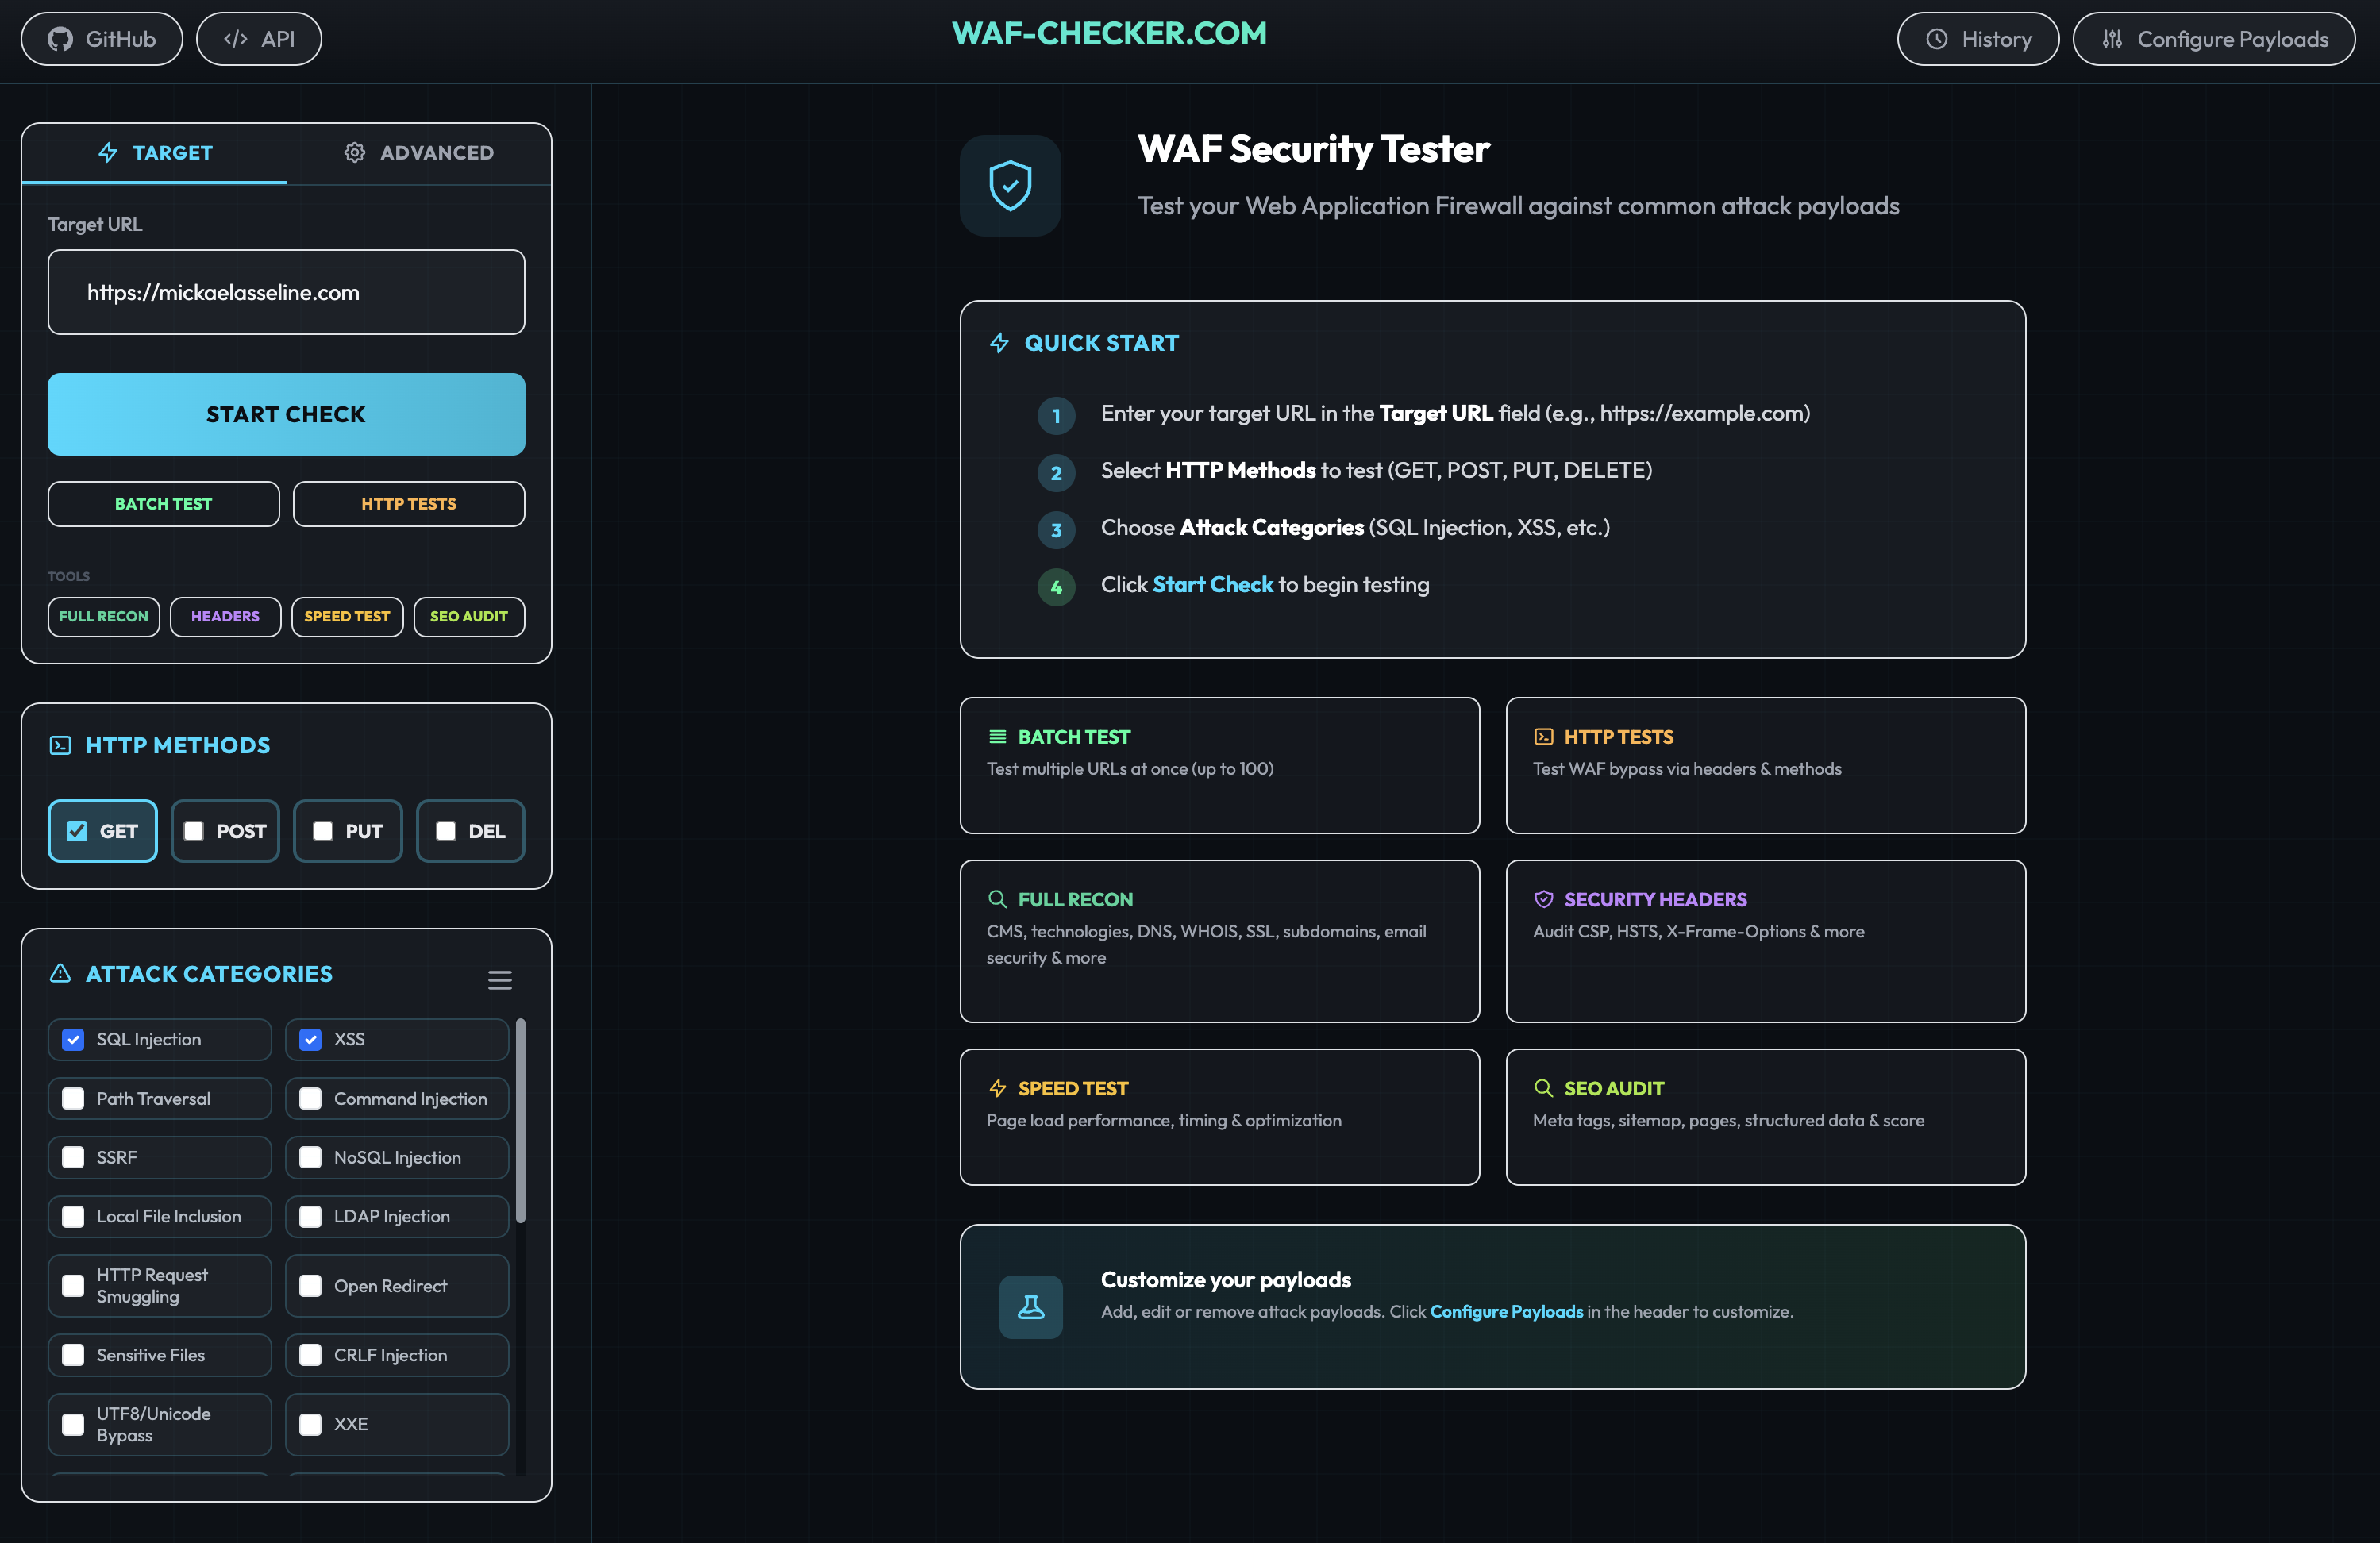 papamica/waf-checker
Tests your WAF with +160 payloads
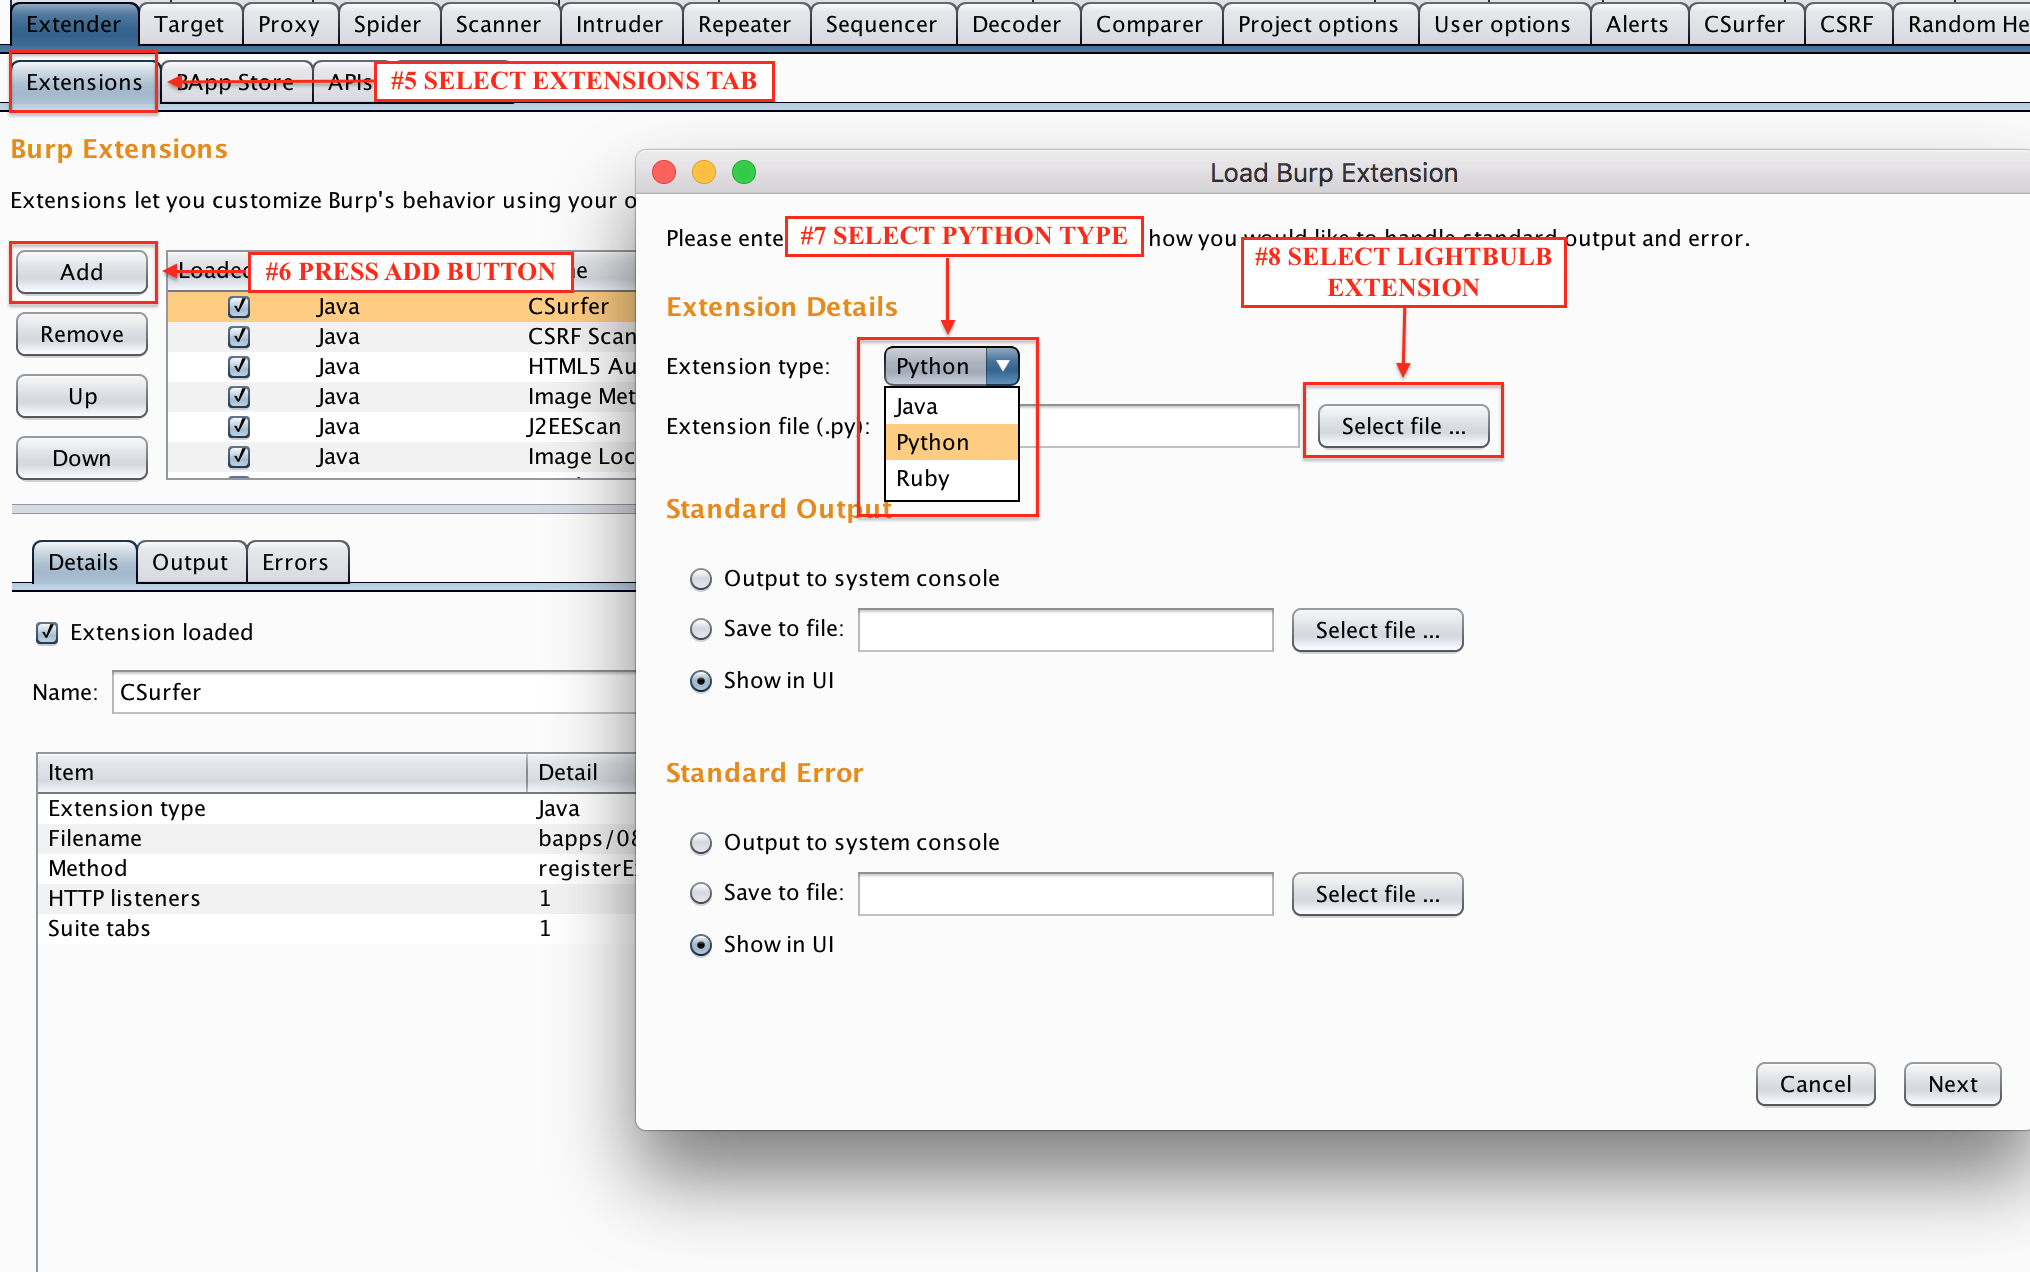 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
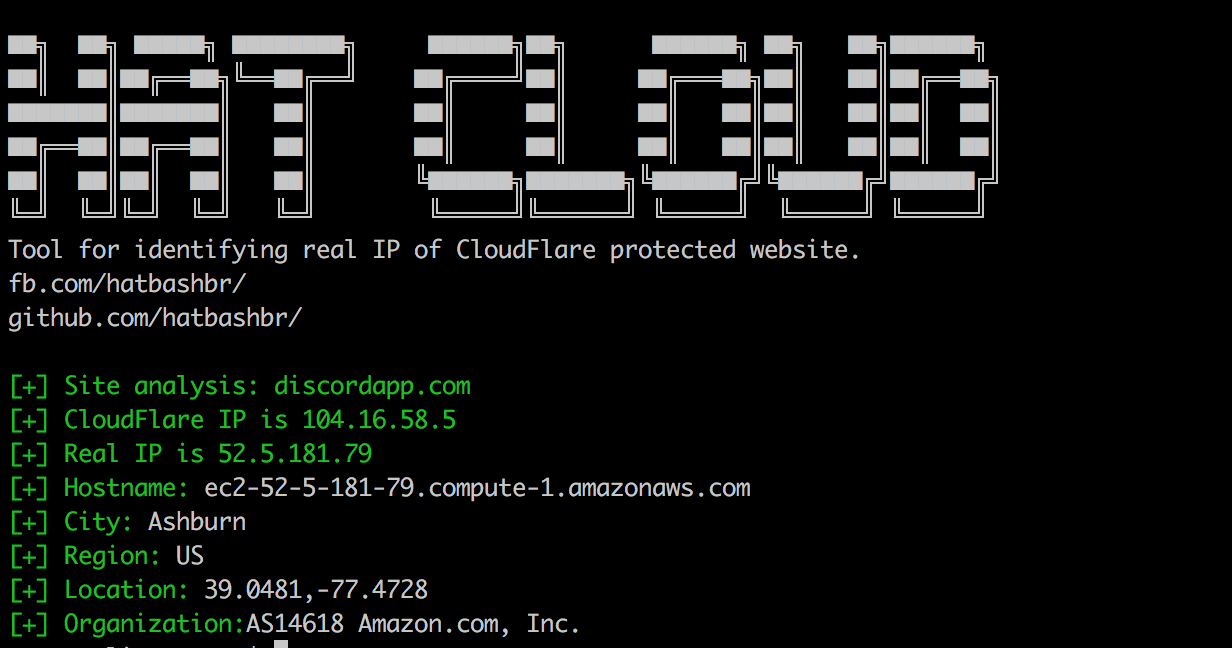
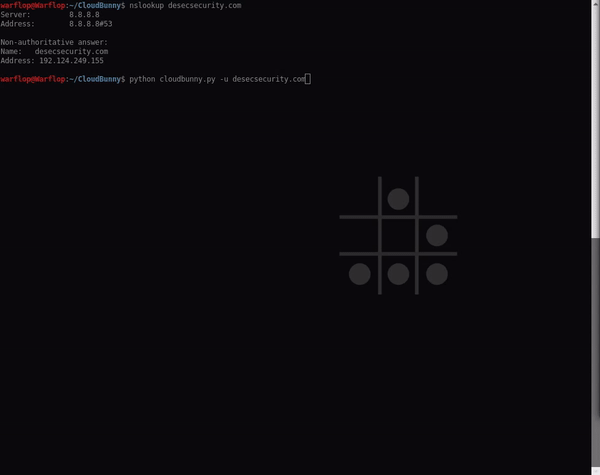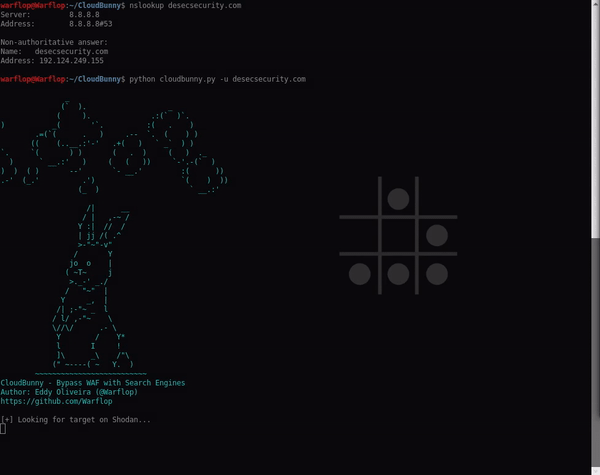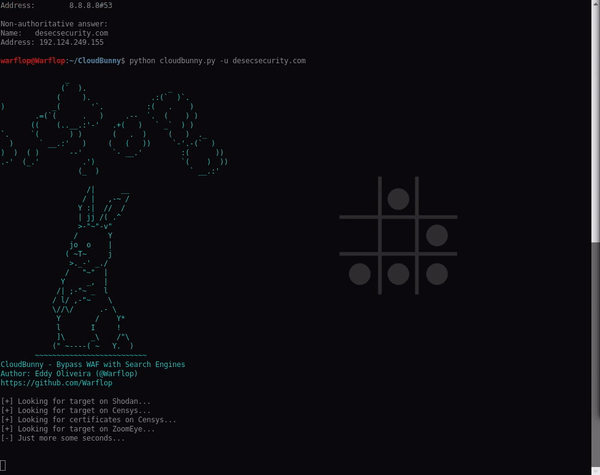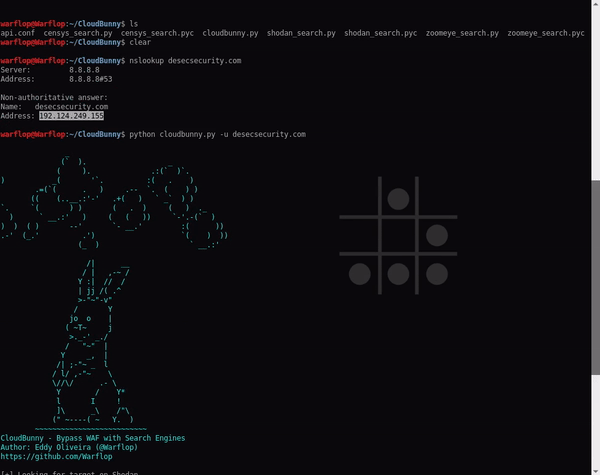 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
 s0md3v/dump
Stuff that doesn't deserves its own repository.
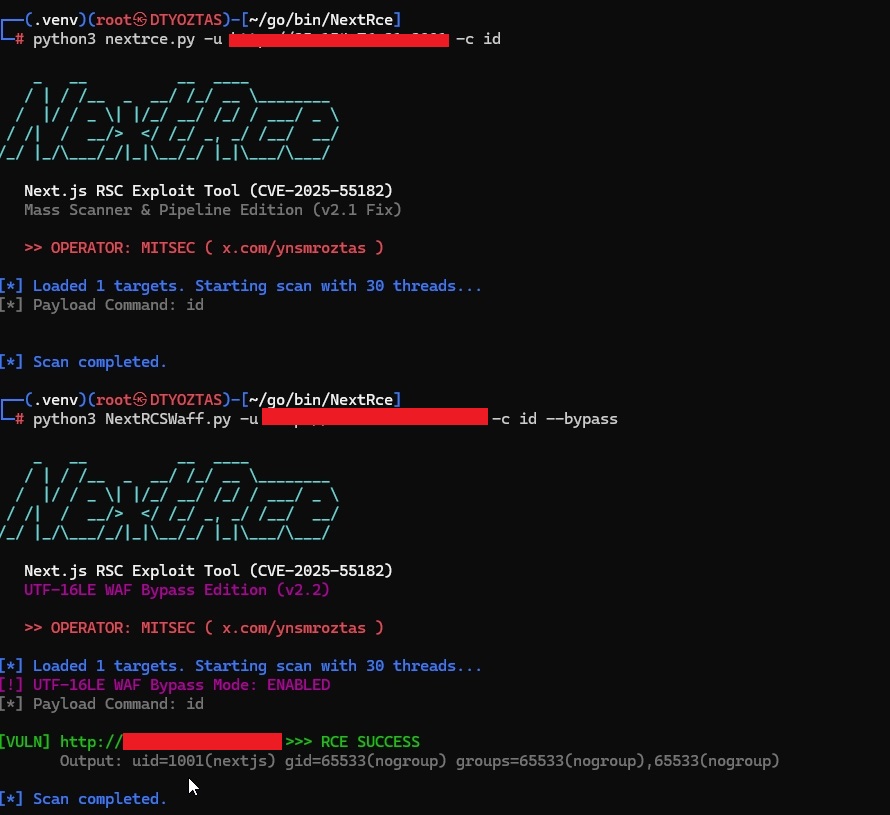 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 samyk/quickjack
Quickjack is a point-and-click tool for intuitively producing advanced clickjacking and frame slicing attacks.
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…