
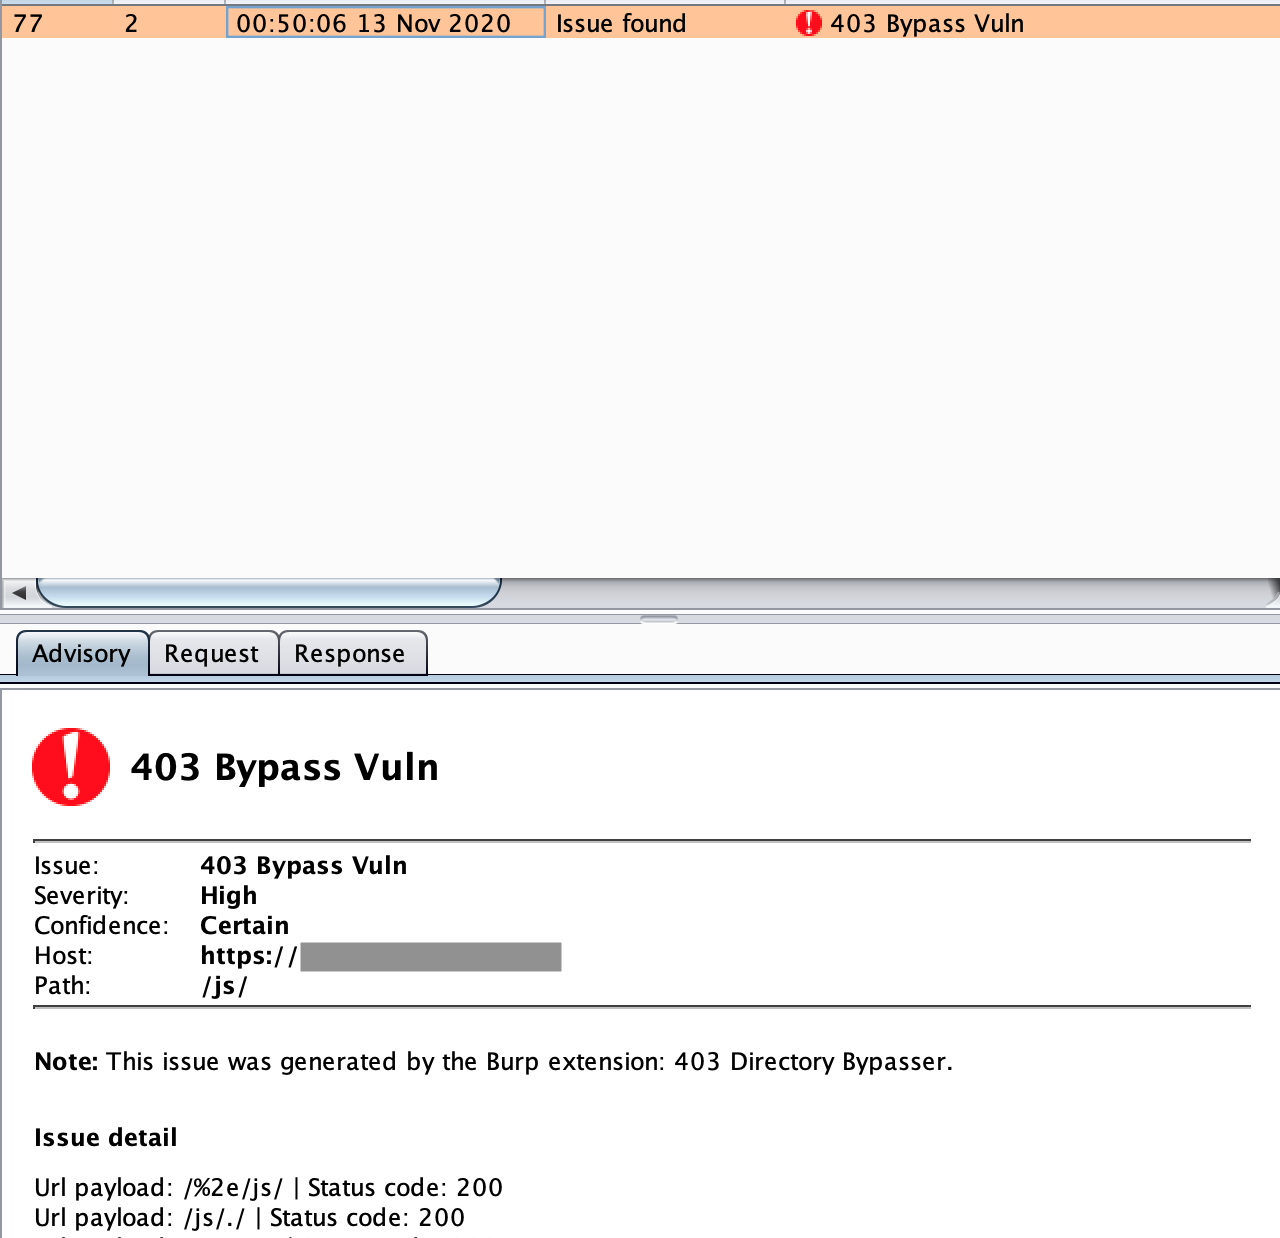
BurpSuite_403Bypasser
 sting8k/burpsuite_403bypasser
Burpsuite Extension to bypass 403 restricted directory
ids-ips-evasioninformation-gatheringpenetration-testing+2
1.7k
sting8k/burpsuite_403bypasserBurpsuite Extension to bypass 403 restricted directory
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 hakluke/hakoriginfinder
Tool for discovering the origin host behind a reverse proxy. Useful for bypassing cloud WAFs!
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 ekultek/zeus-scanner
Advanced reconnaissance utility
 zigoo0/jsonbee
A ready to use JSONP endpoints/payloads to help bypass content security policy (CSP) of different websites.
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 yagamiilight/cerberus
一款功能强大的漏洞扫描器,子域名爆破使用aioDNS,asyncio异步快速扫描,覆盖目标全方位资产进行批量漏洞扫描,中间件信息收集,自动收集ip代理,探测Waf信息时自动使用来保护本机真实Ip,在本机Ip被Waf杀死后,自动切换代理Ip进行扫描,Waf信息收集(国内外100+款waf信息)包括安全…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.
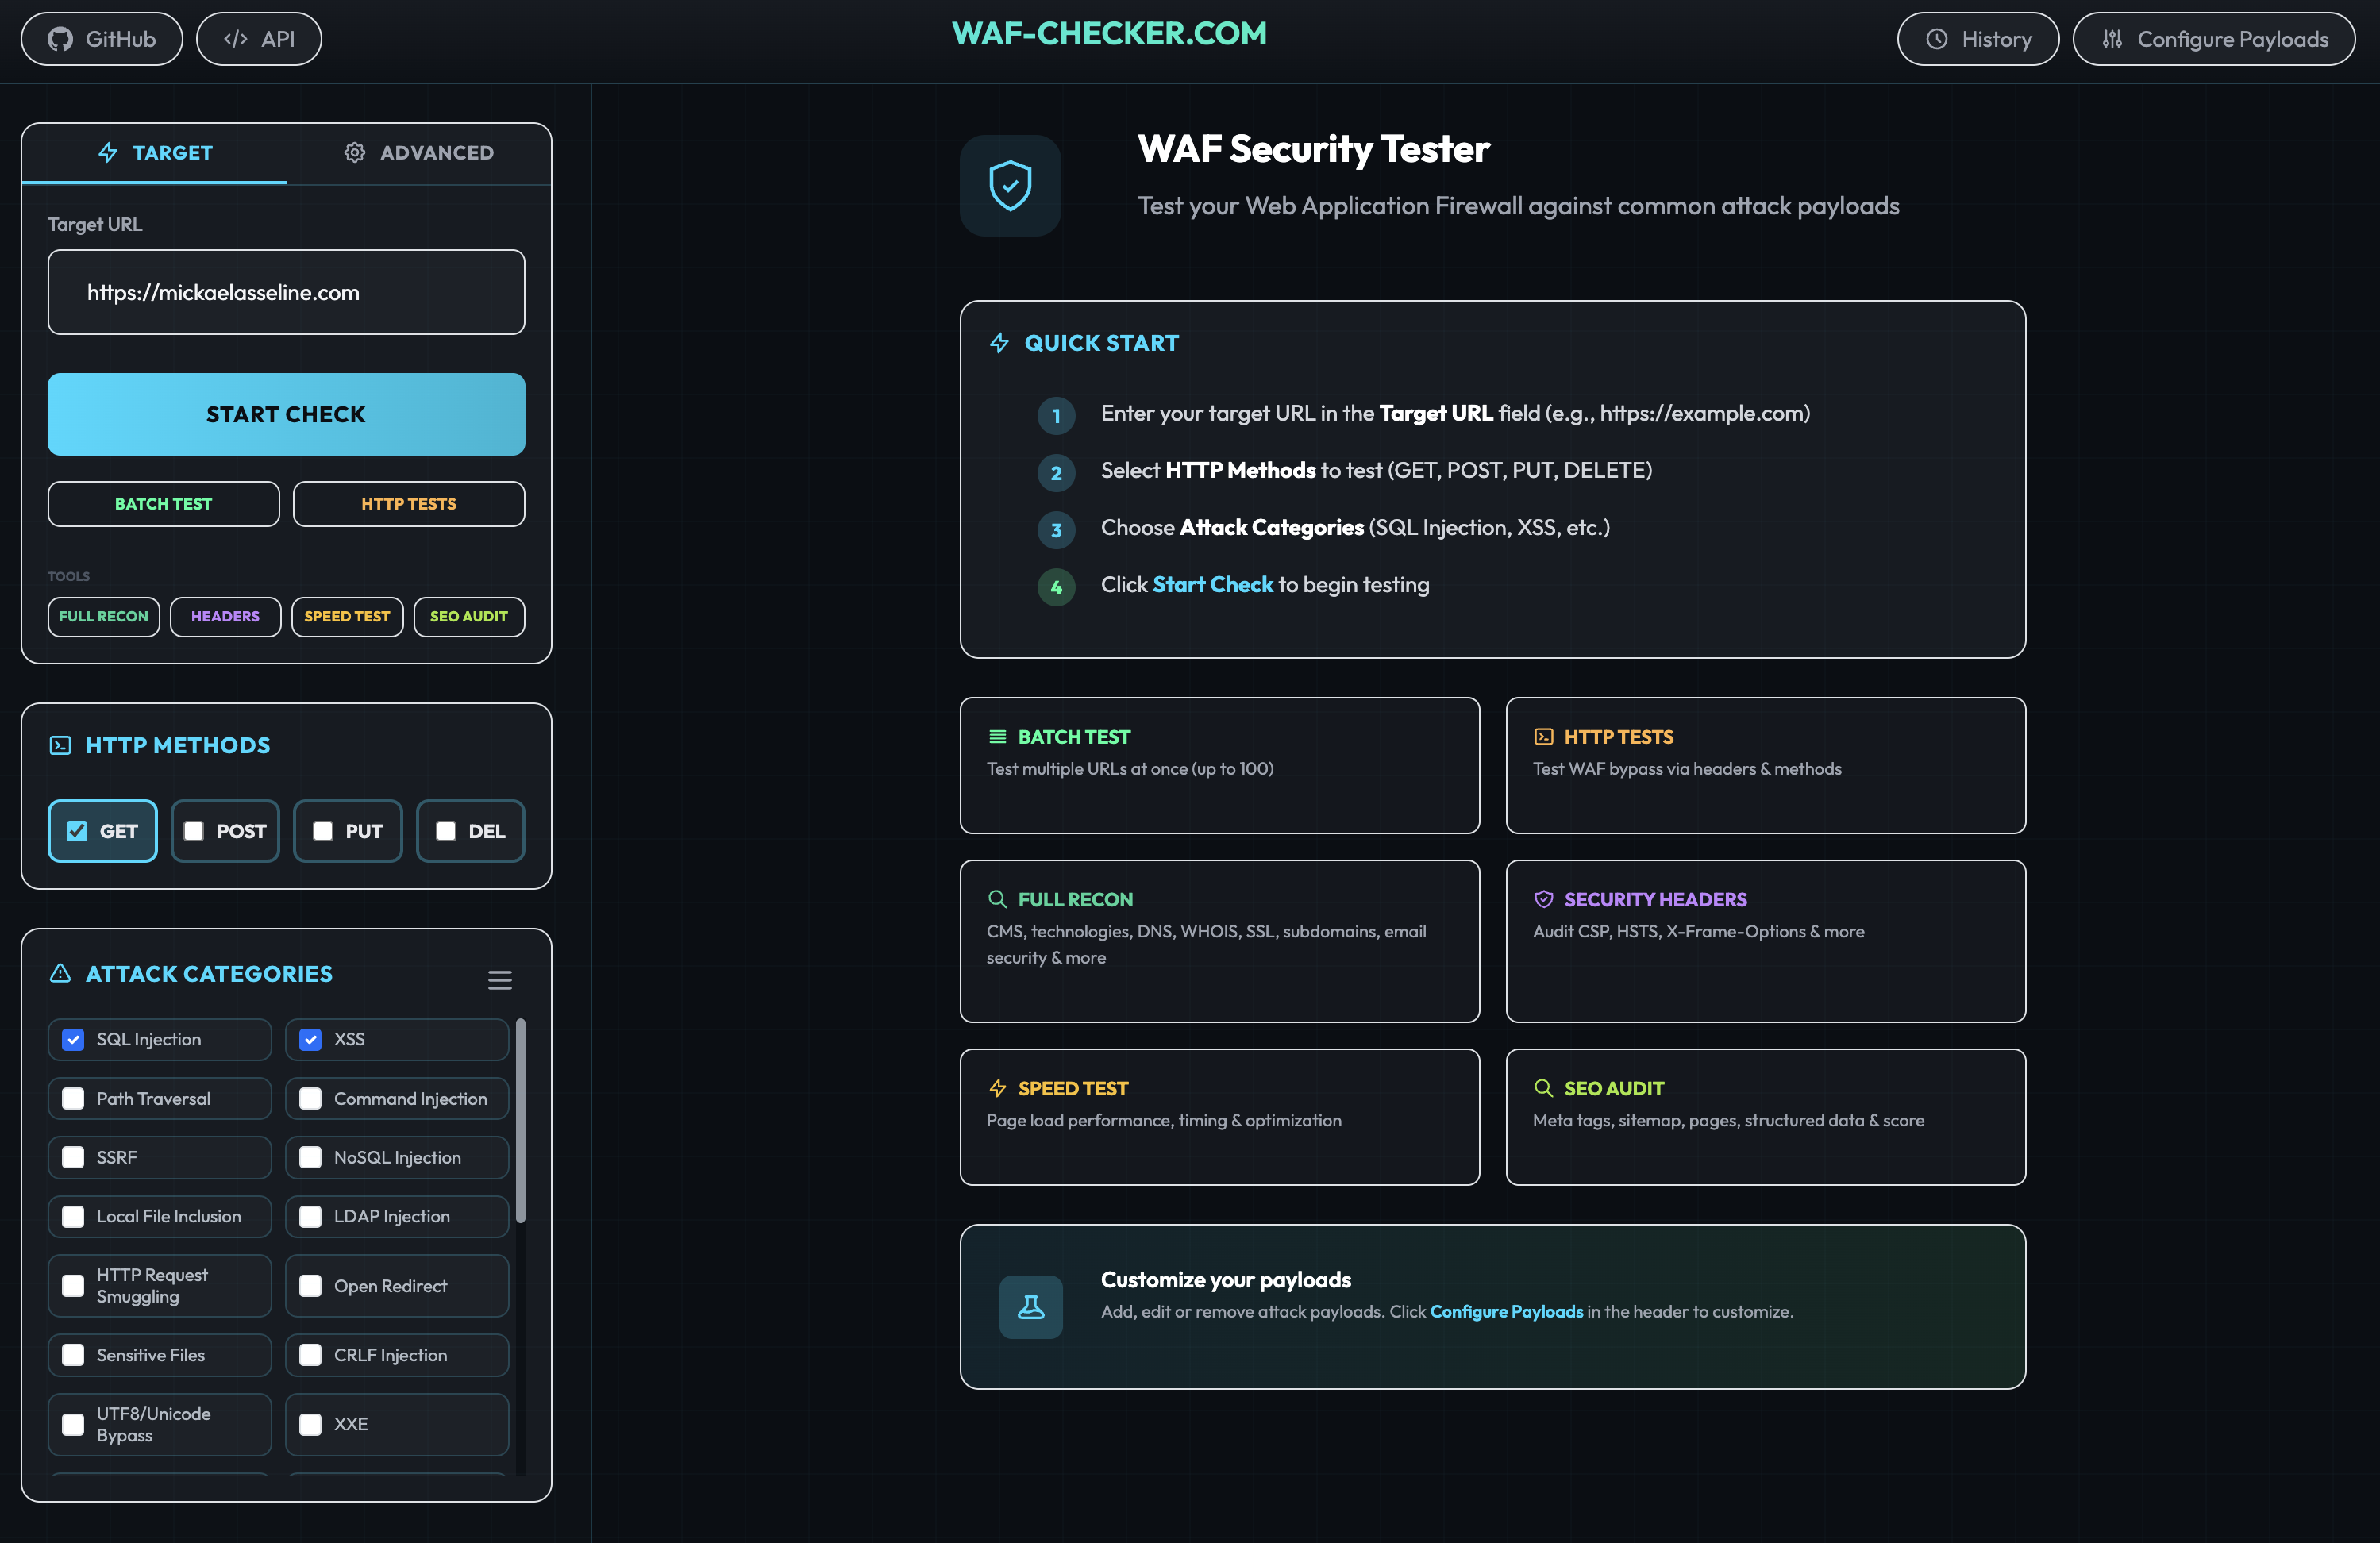 papamica/waf-checker
Tests your WAF with +160 payloads
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
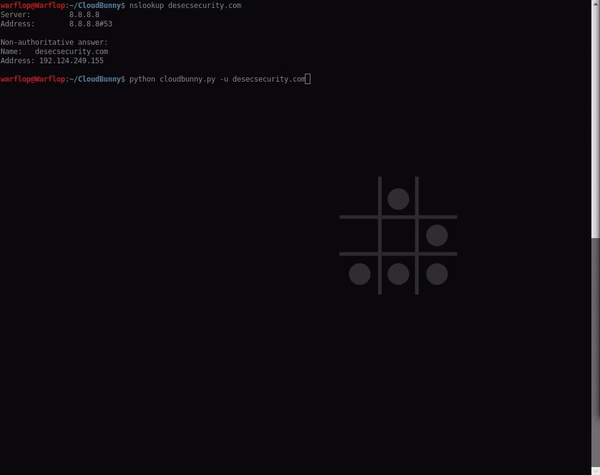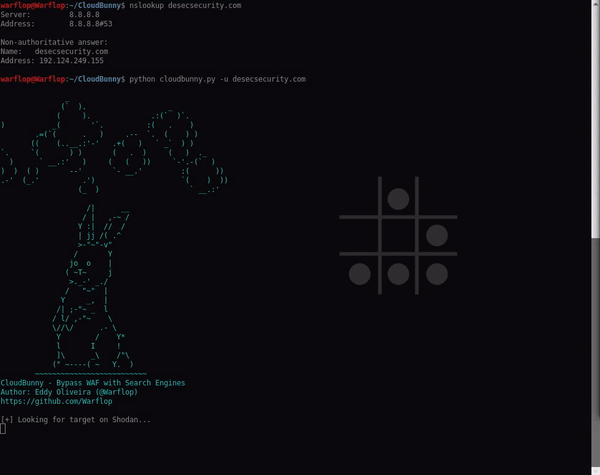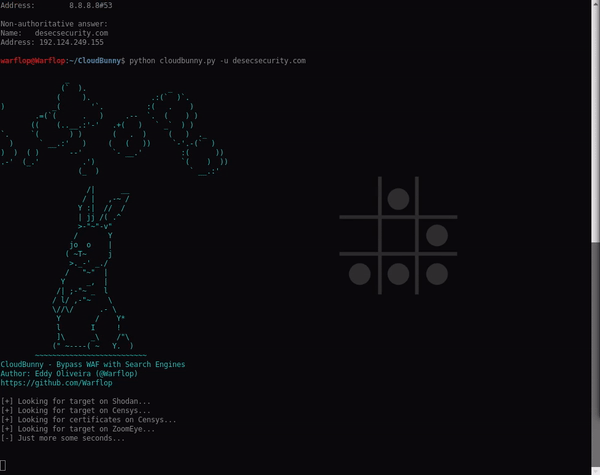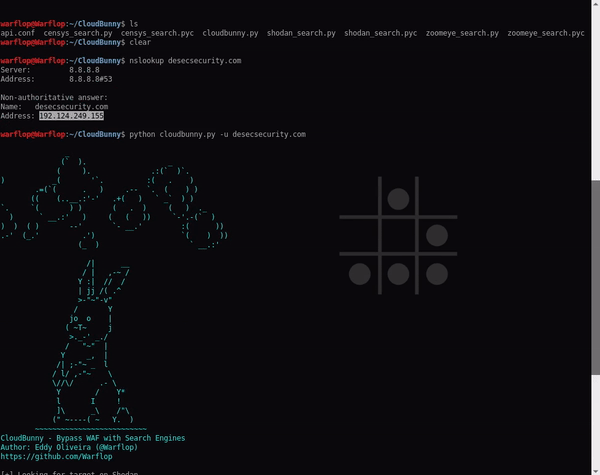 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…