
feroxbuster
 epi052/feroxbuster
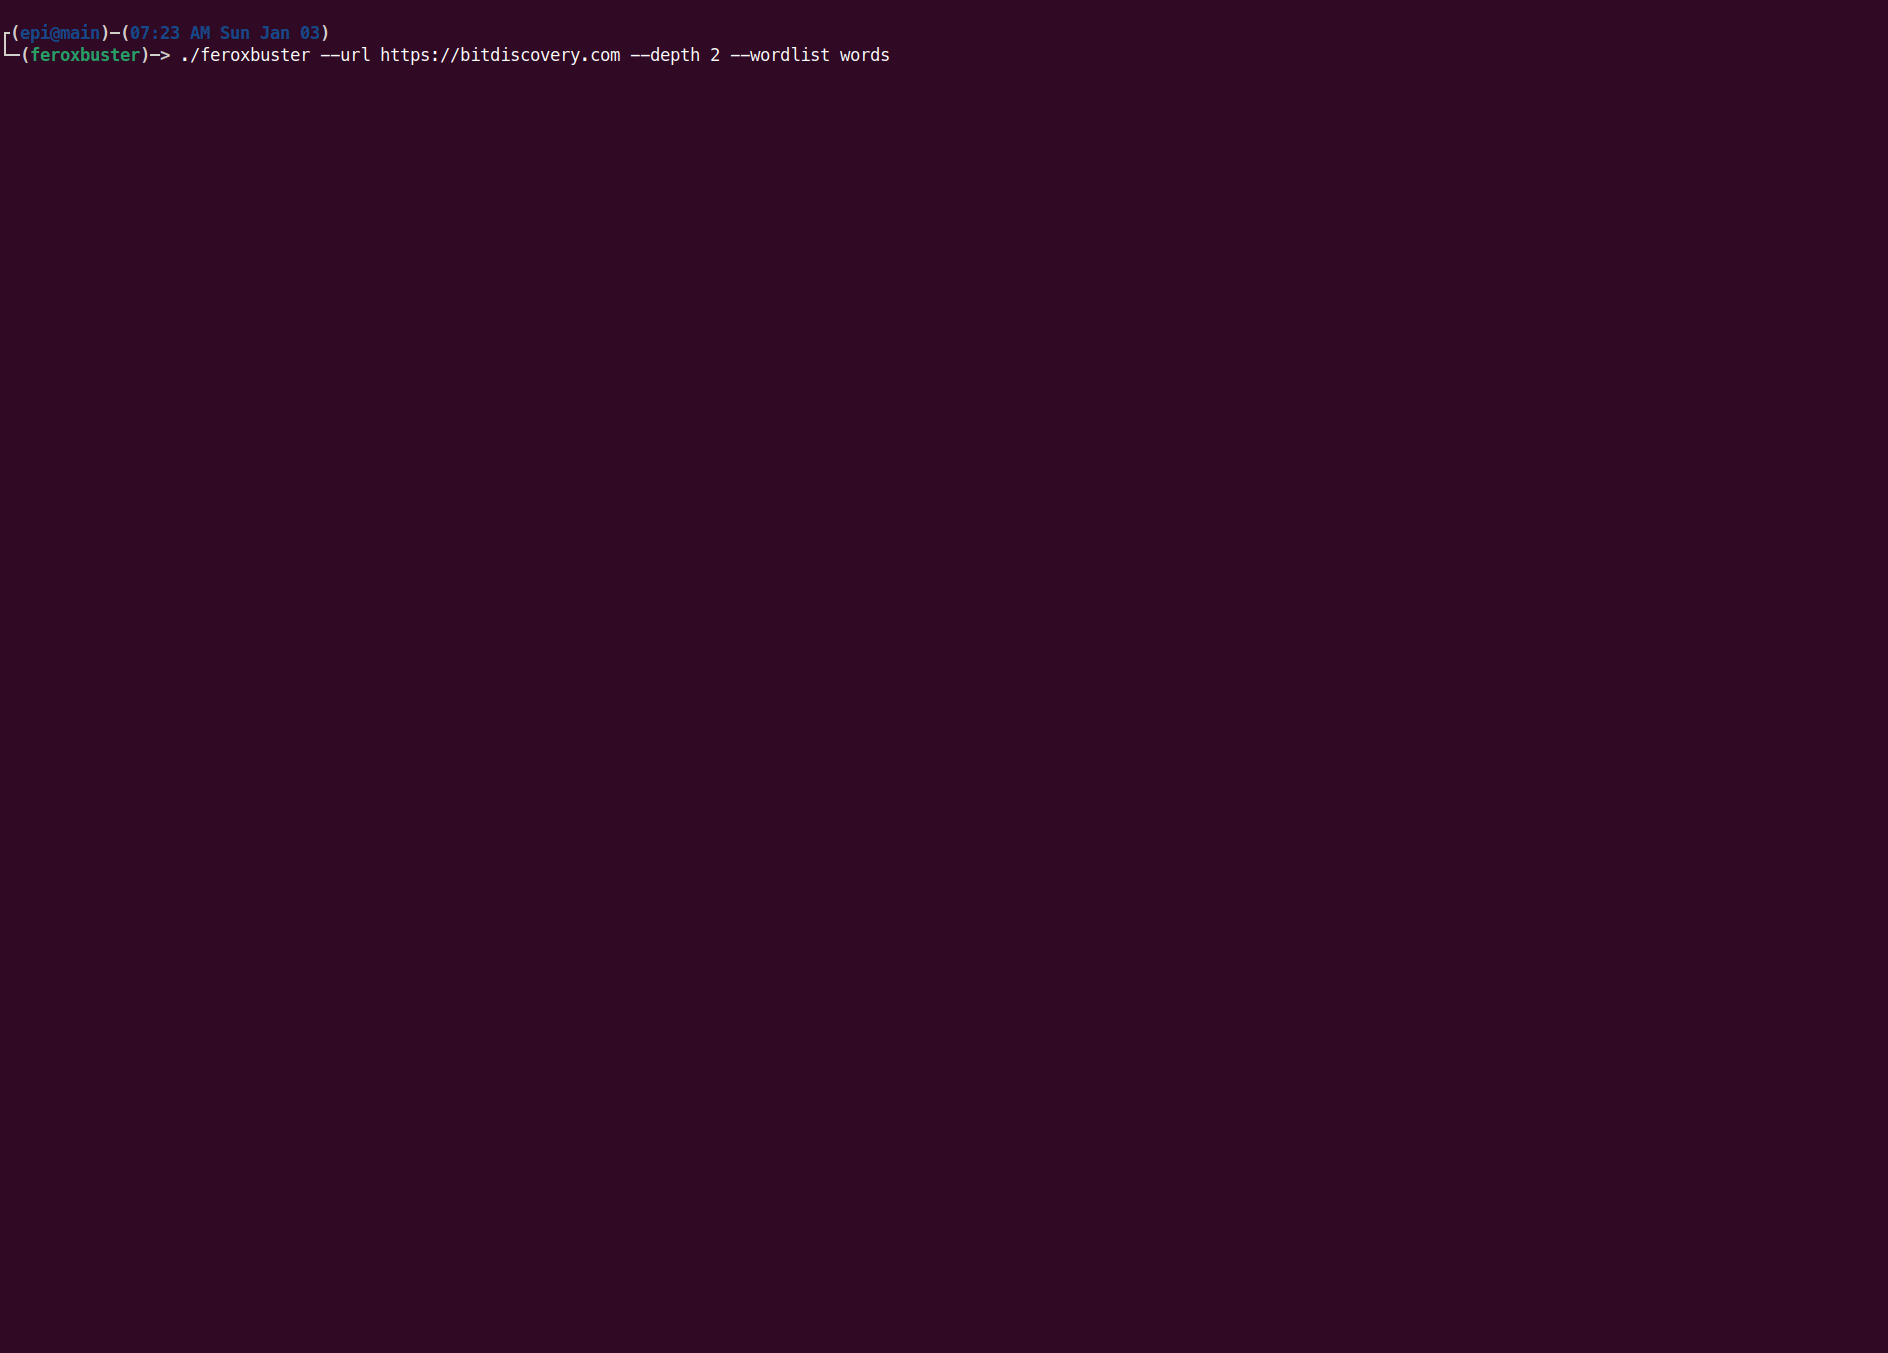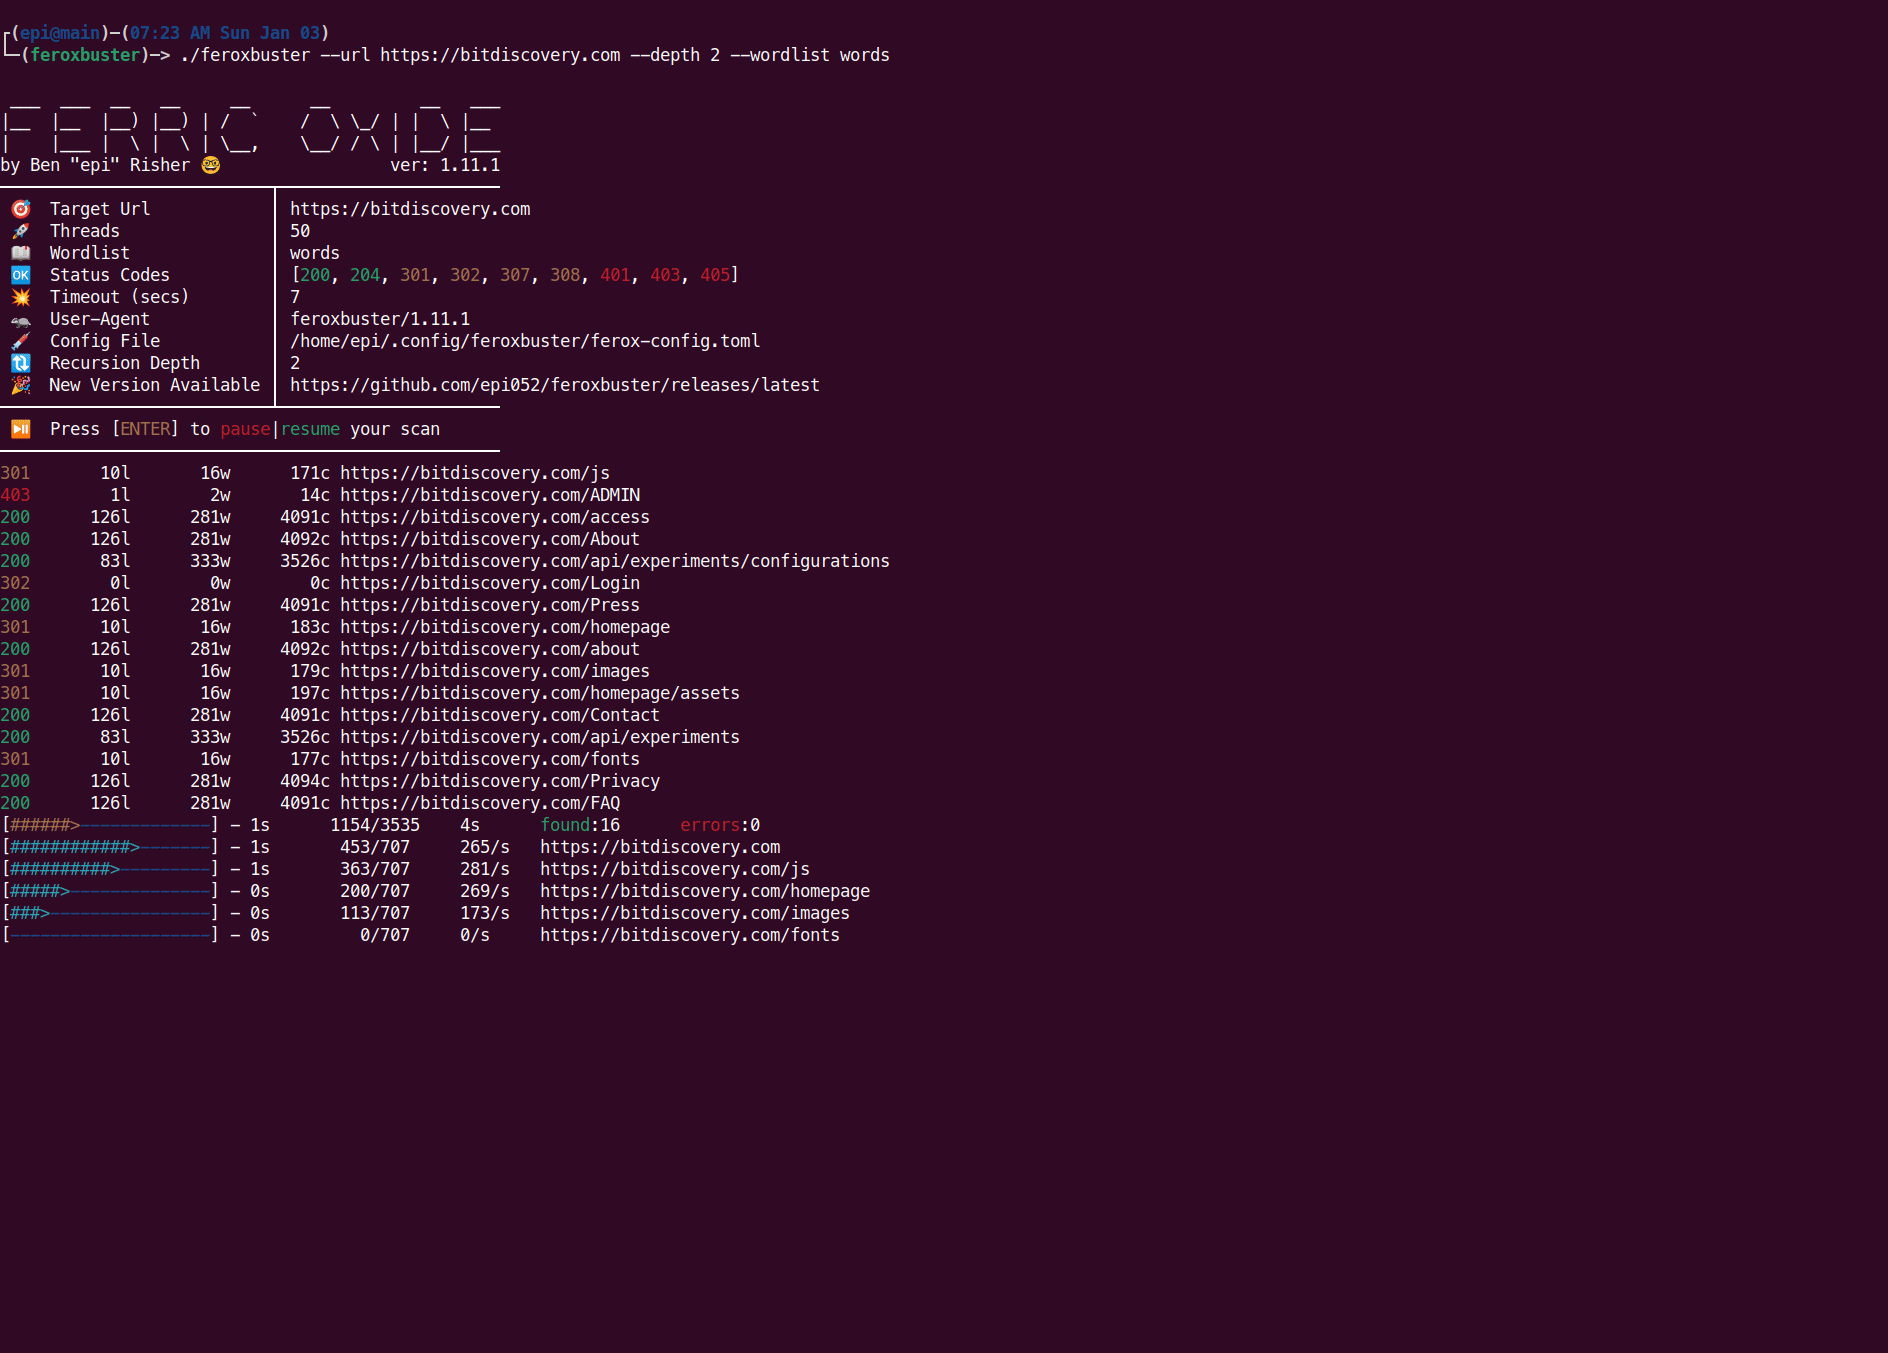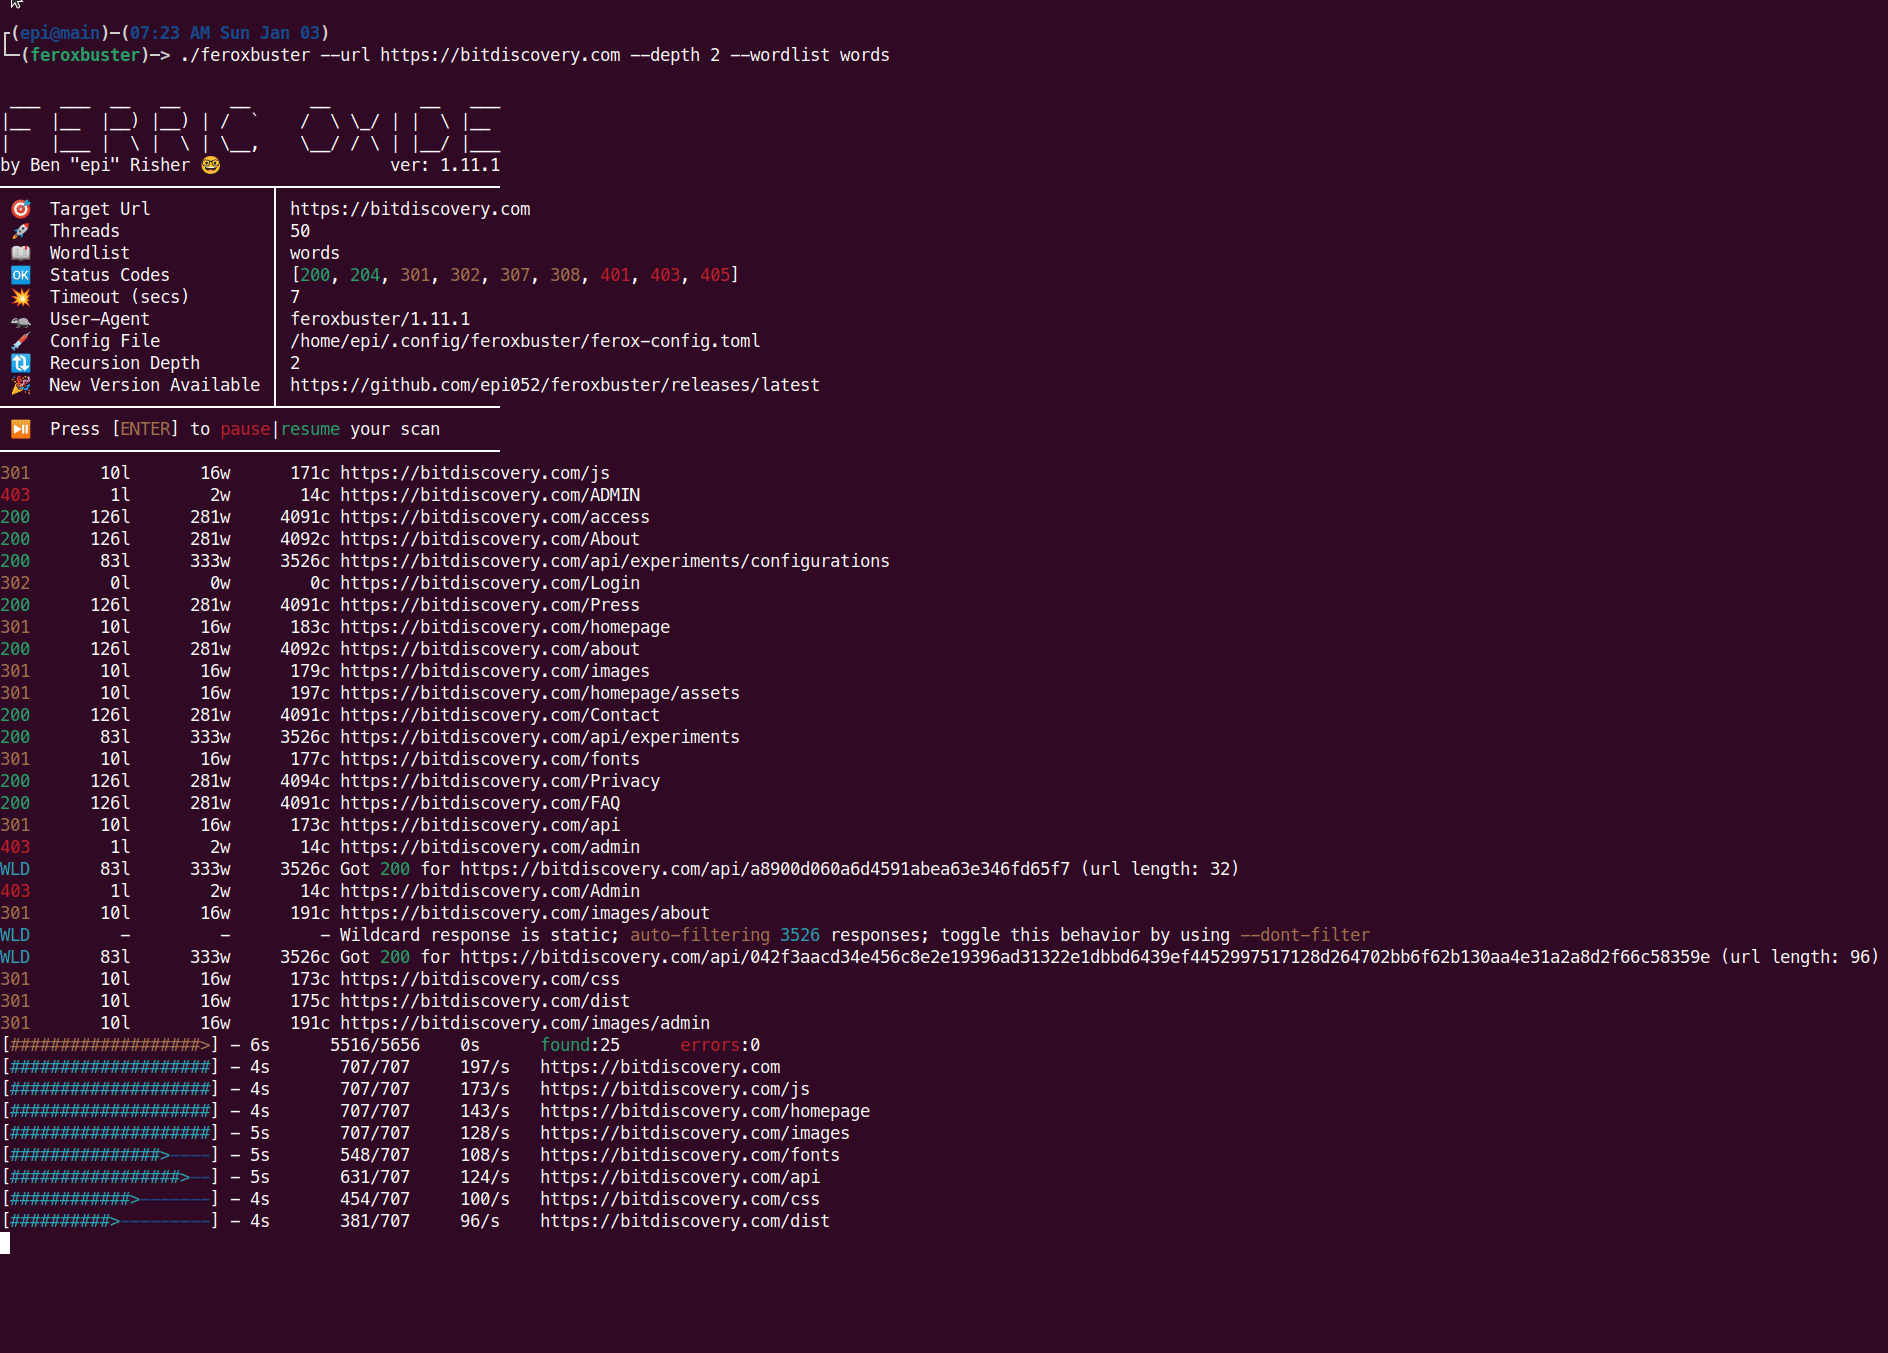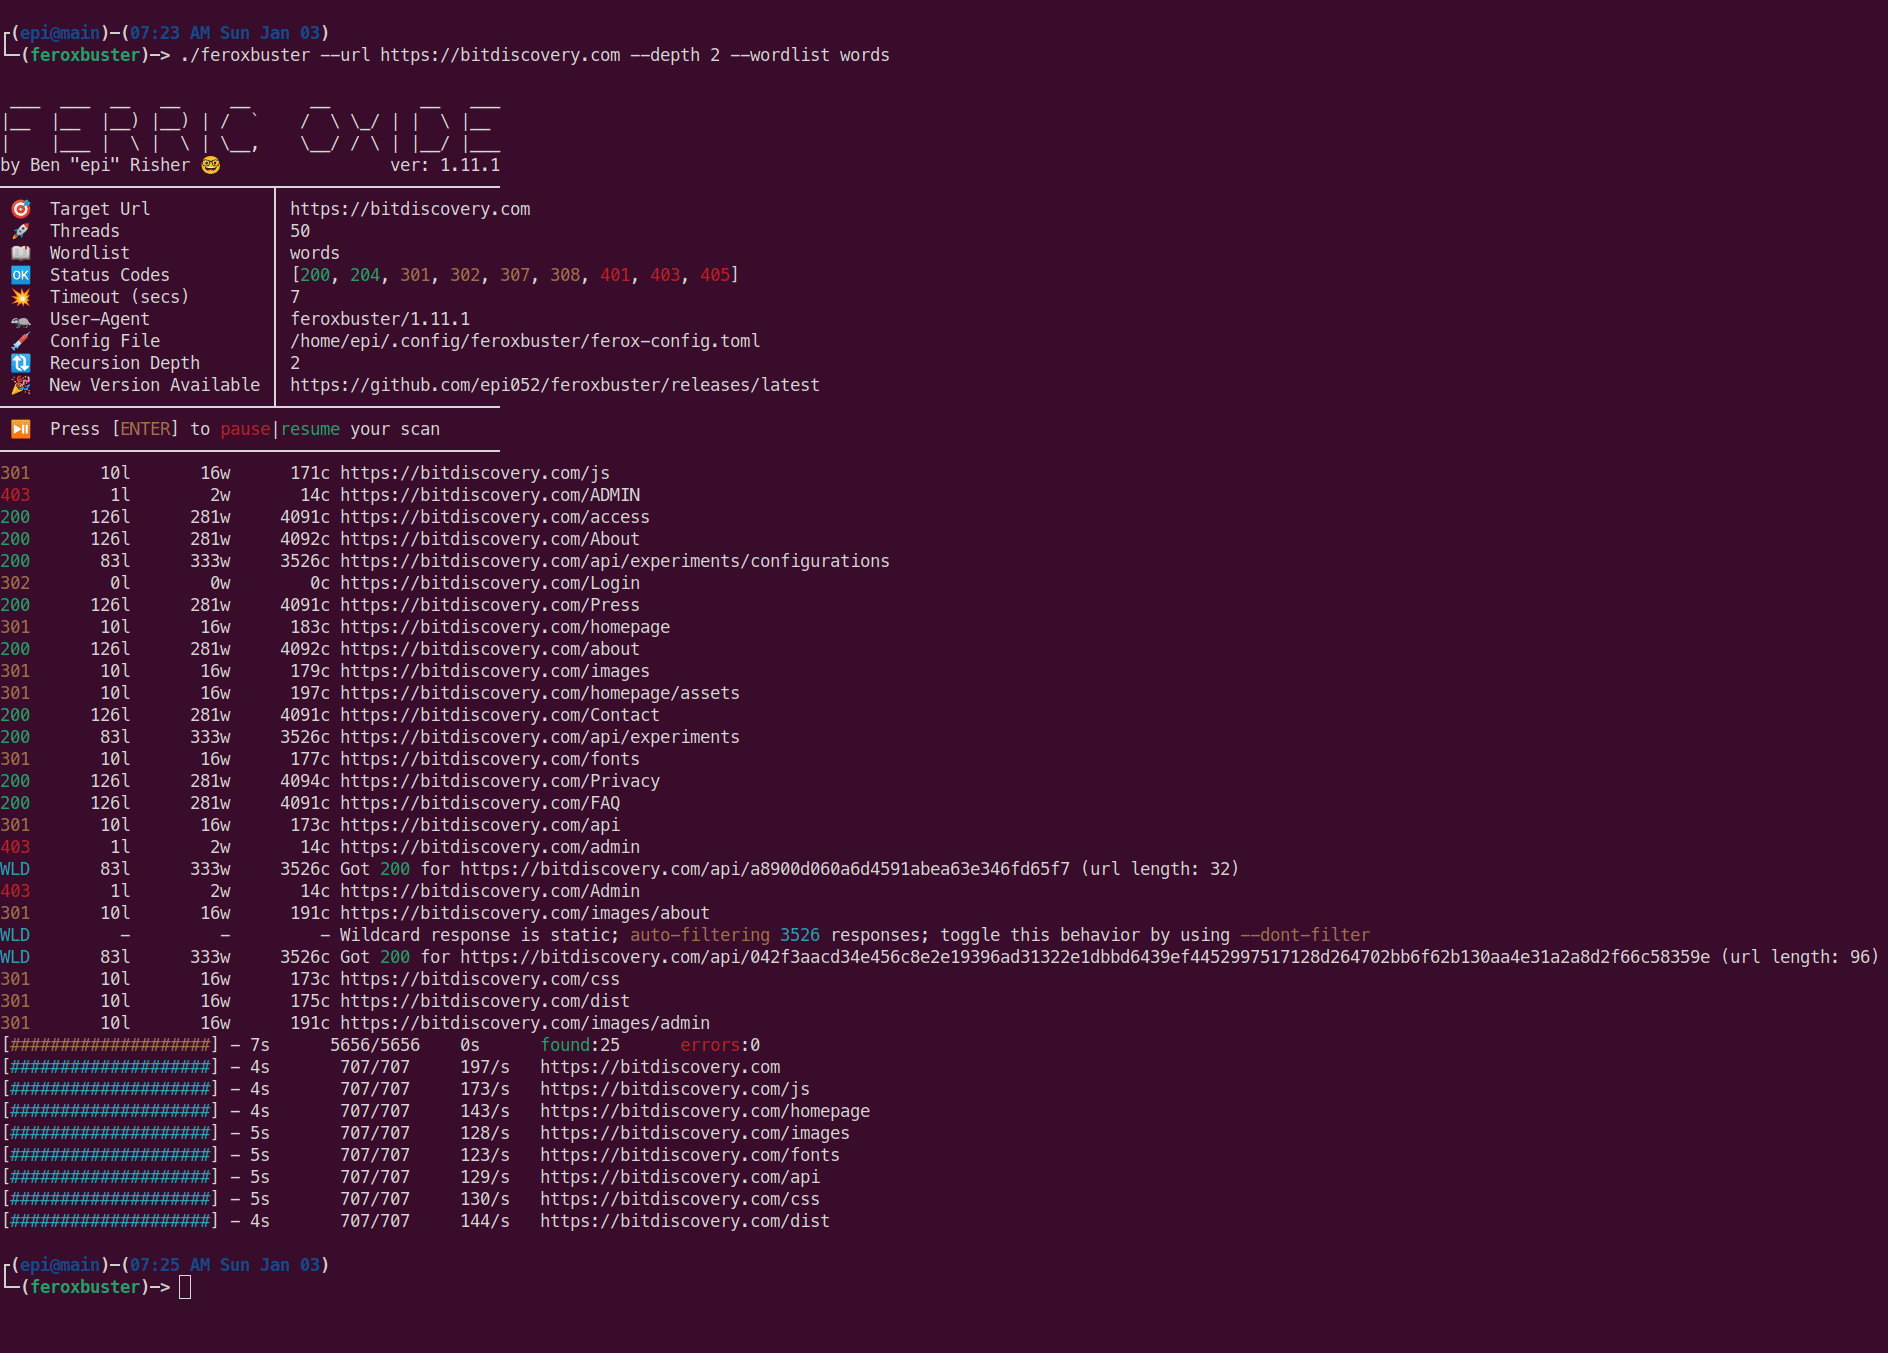
A fast, simple, recursive content discovery tool written in Rust.
api-securityapi-security-testingcrawler+8
8.1k
epi052/feroxbusterA fast, simple, recursive content discovery tool written in Rust.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 blue0x1/xpath
xpath is a fast, multi-technique XPath injection scanner written in Nim. It focuses on practical detection, response comparison, visible extraction,…
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 wyllowsec/magnohost-vulnerabilities-pentest
pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…
 urbanadventurer/whatweb
Next generation web scanner
 franckferman/cve-2025-67906
MISP <= 2.5.27 - Stored Cross-Site Scripting via Workflow Engine (doT.js Template Injection).
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
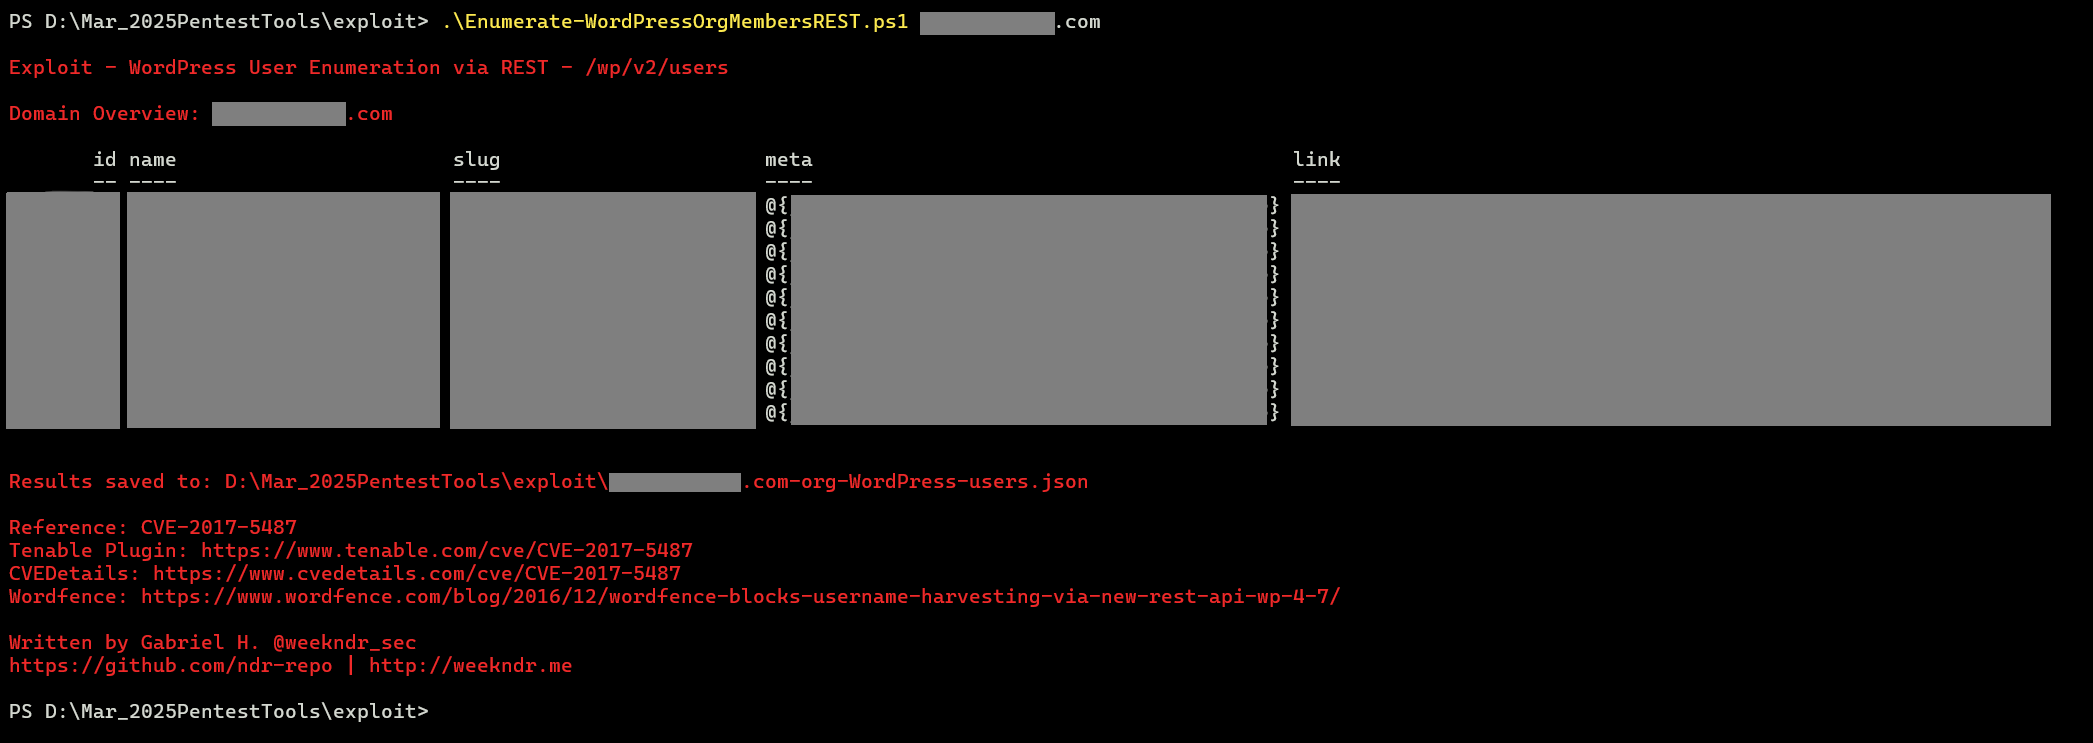 ndr-repo/cve-2017-5487
PoC for CVE-2017-5487 - WordPress User Enumeration via REST
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
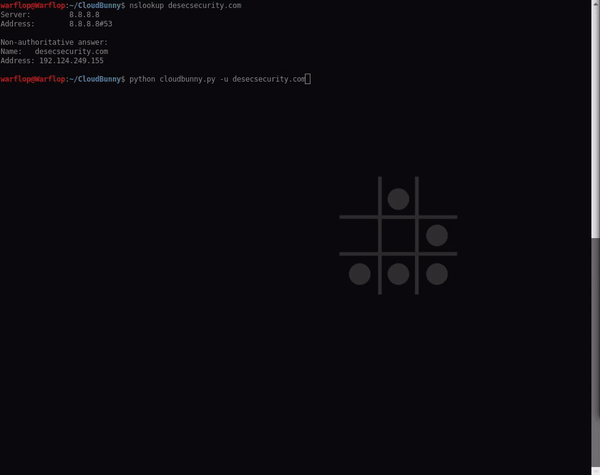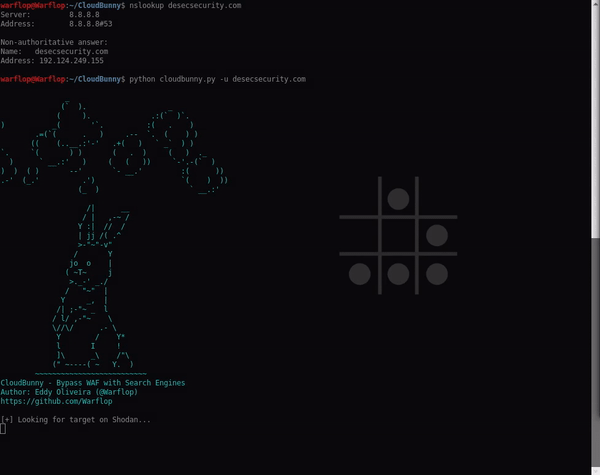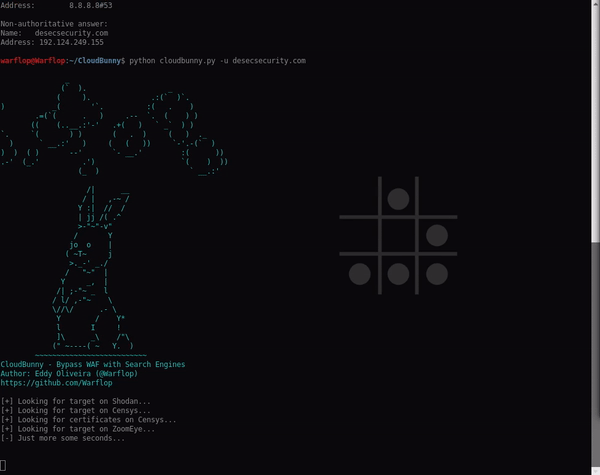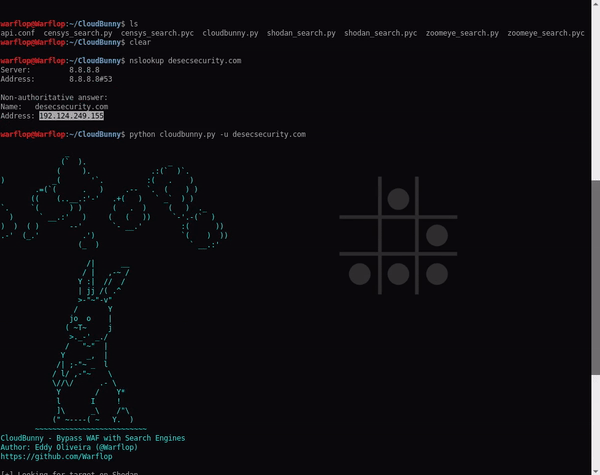 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。