php-cve-2026-10961x-lab-poc

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

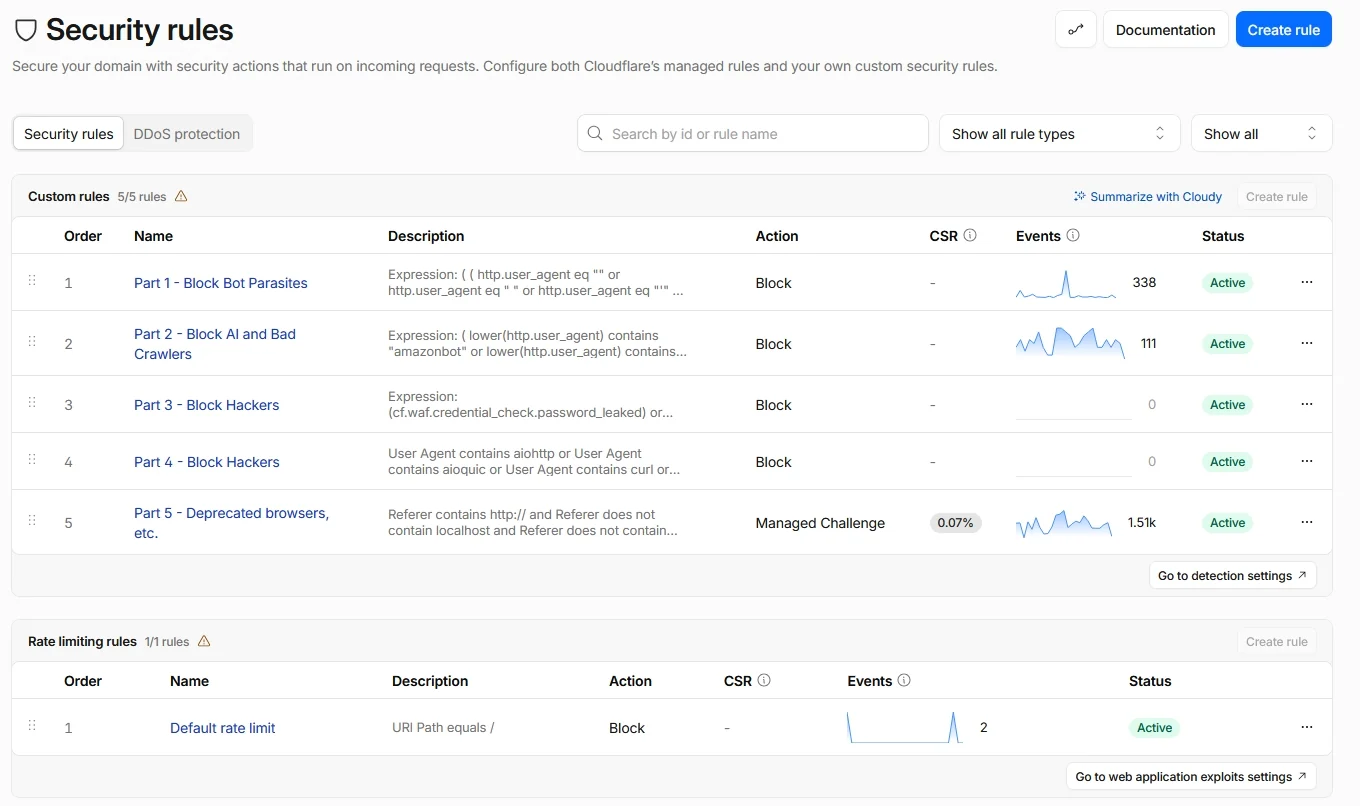
Cloudflare Free Plan security rules (Zero Trust approach) for small websites

Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…

Testing WAF protection against CVE-2021-44228 Log4Shell

A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046

WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab

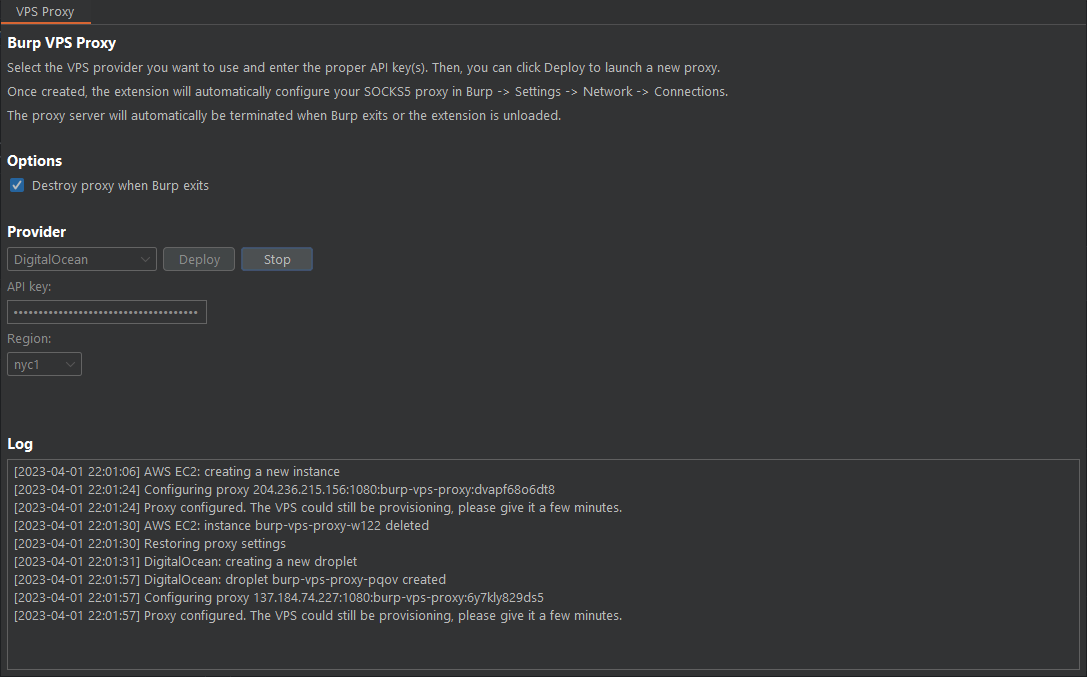
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.

Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.

Burp Plugin to Bypass WAFs through the insertion of Junk Data

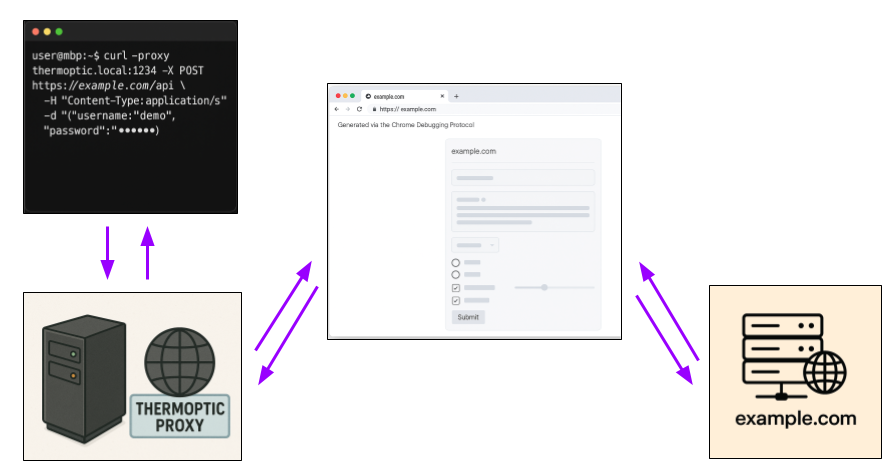
A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.

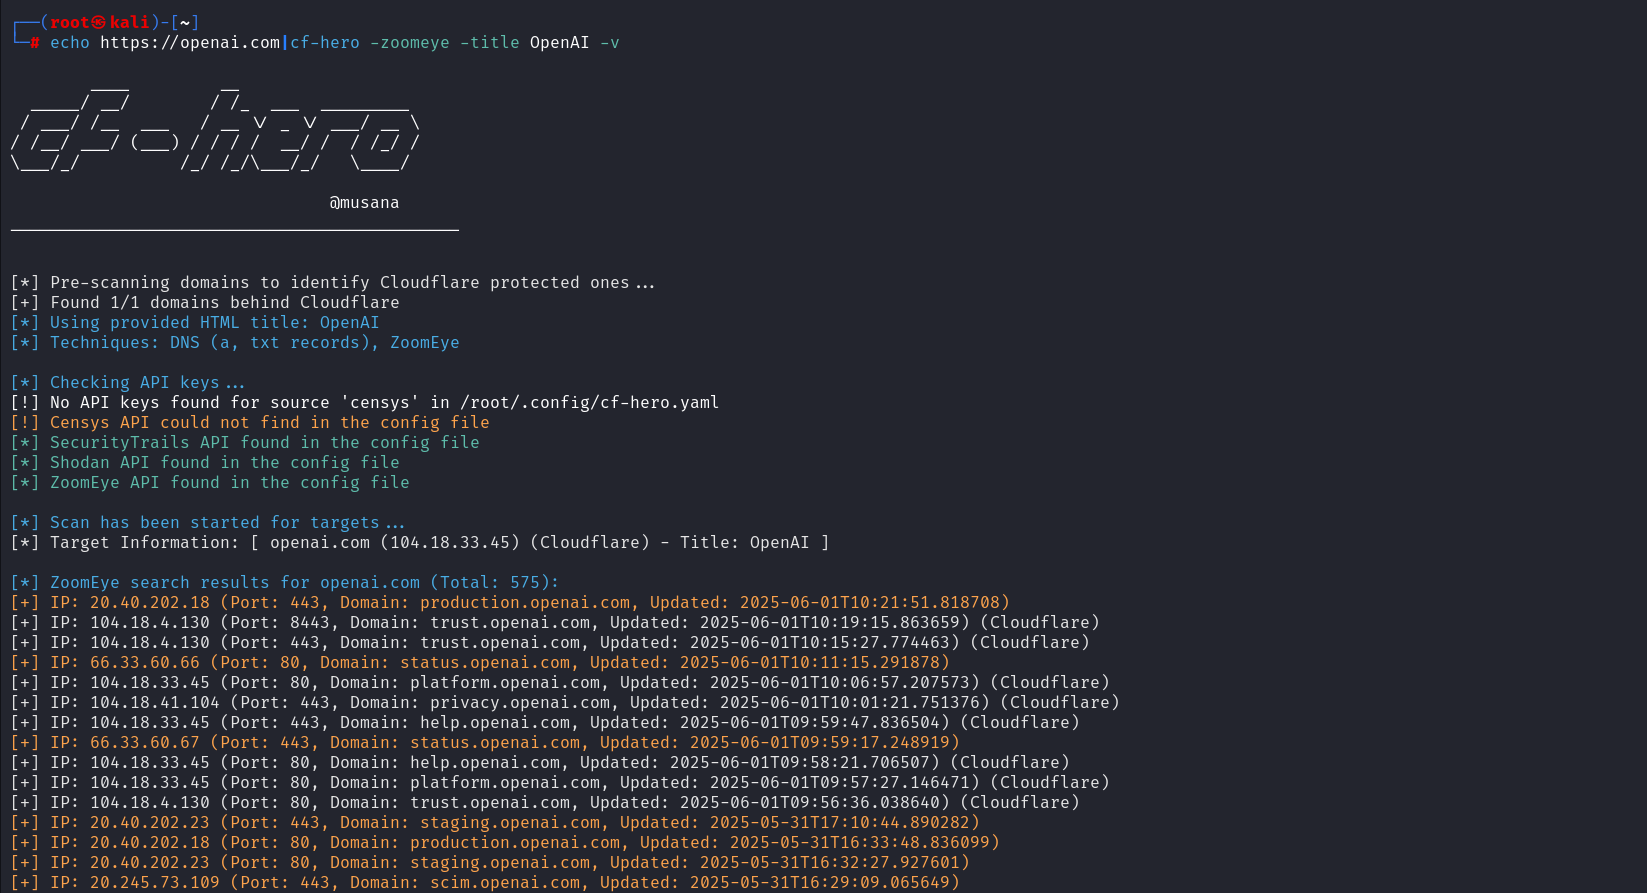
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications