
CVE-2026-87902
 rwxrwxs/cve-2026-87902
Python exploit for CVE-2026-87902, an unauthenticated LFI in WordPress Core ≤7.1.1: fingerprints OPML, detects webroot, abuses the PEAR gadget to…
exploitationinformation-gatheringpayload-generation+7
rwxrwxs/cve-2026-87902Python exploit for CVE-2026-87902, an unauthenticated LFI in WordPress Core ≤7.1.1: fingerprints OPML, detects webroot, abuses the PEAR gadget to…
 lu1sdv/wafmeow
wafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…
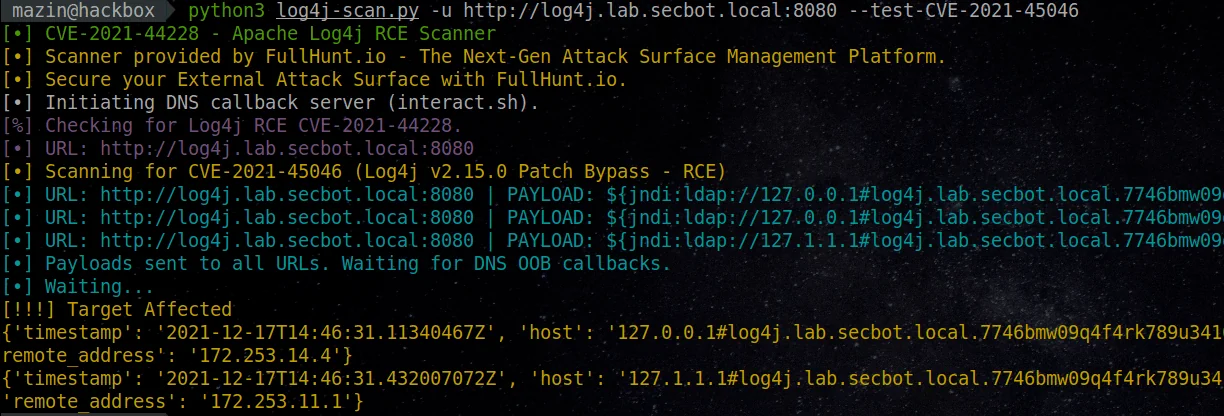 ananya-0306/log-4j-scanner
A fully automated, accurate, and extensive scanner for finding log4j RCE CVE-2021-44228
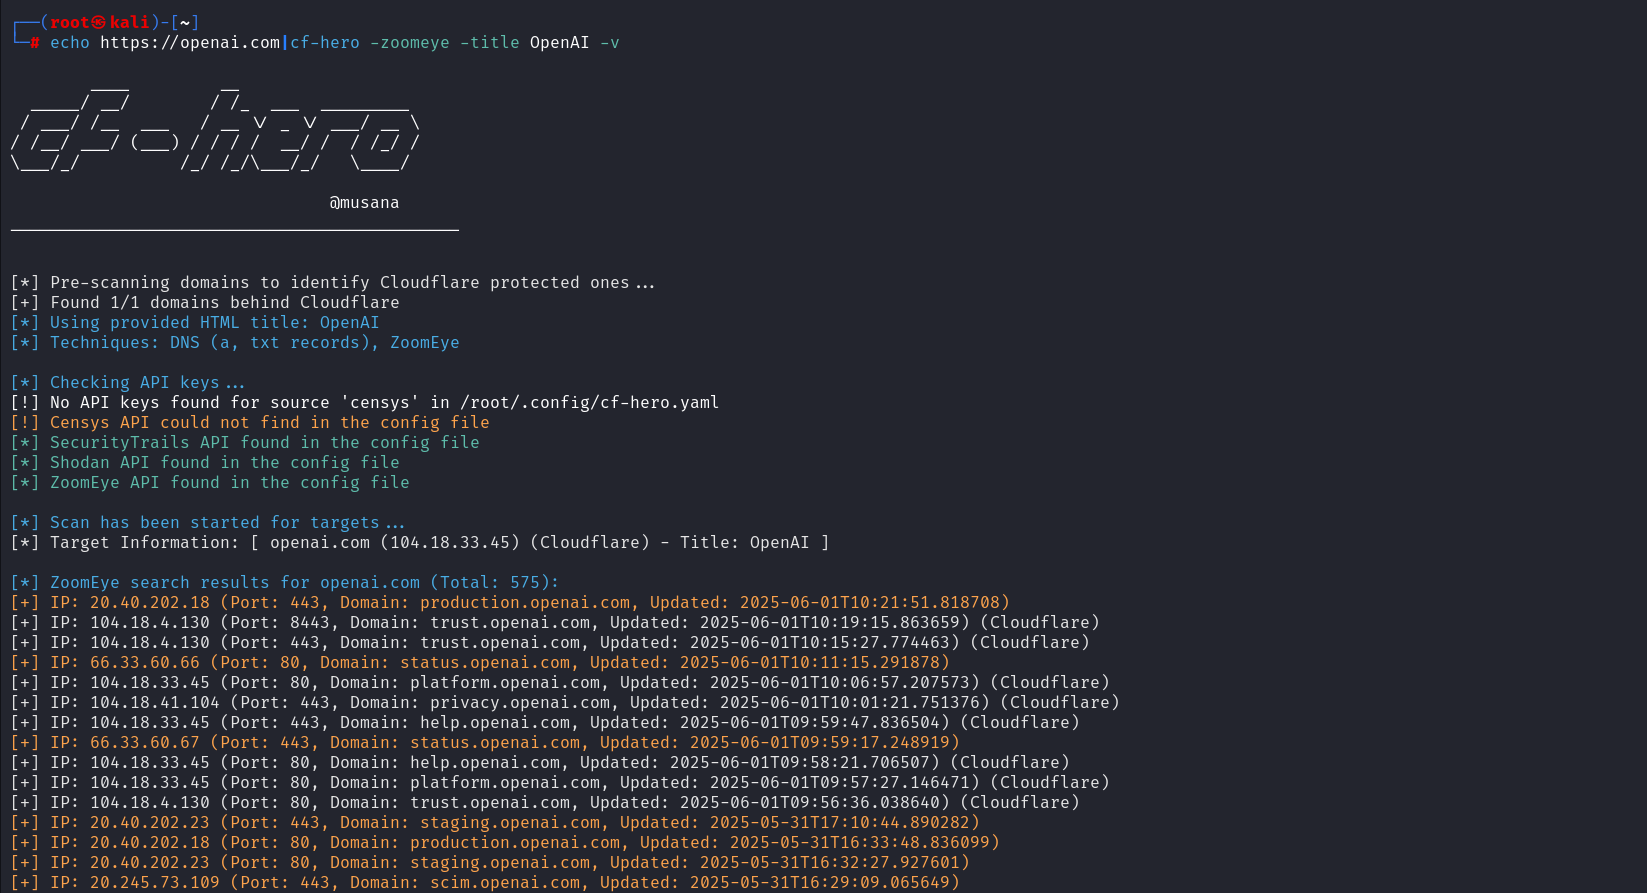 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
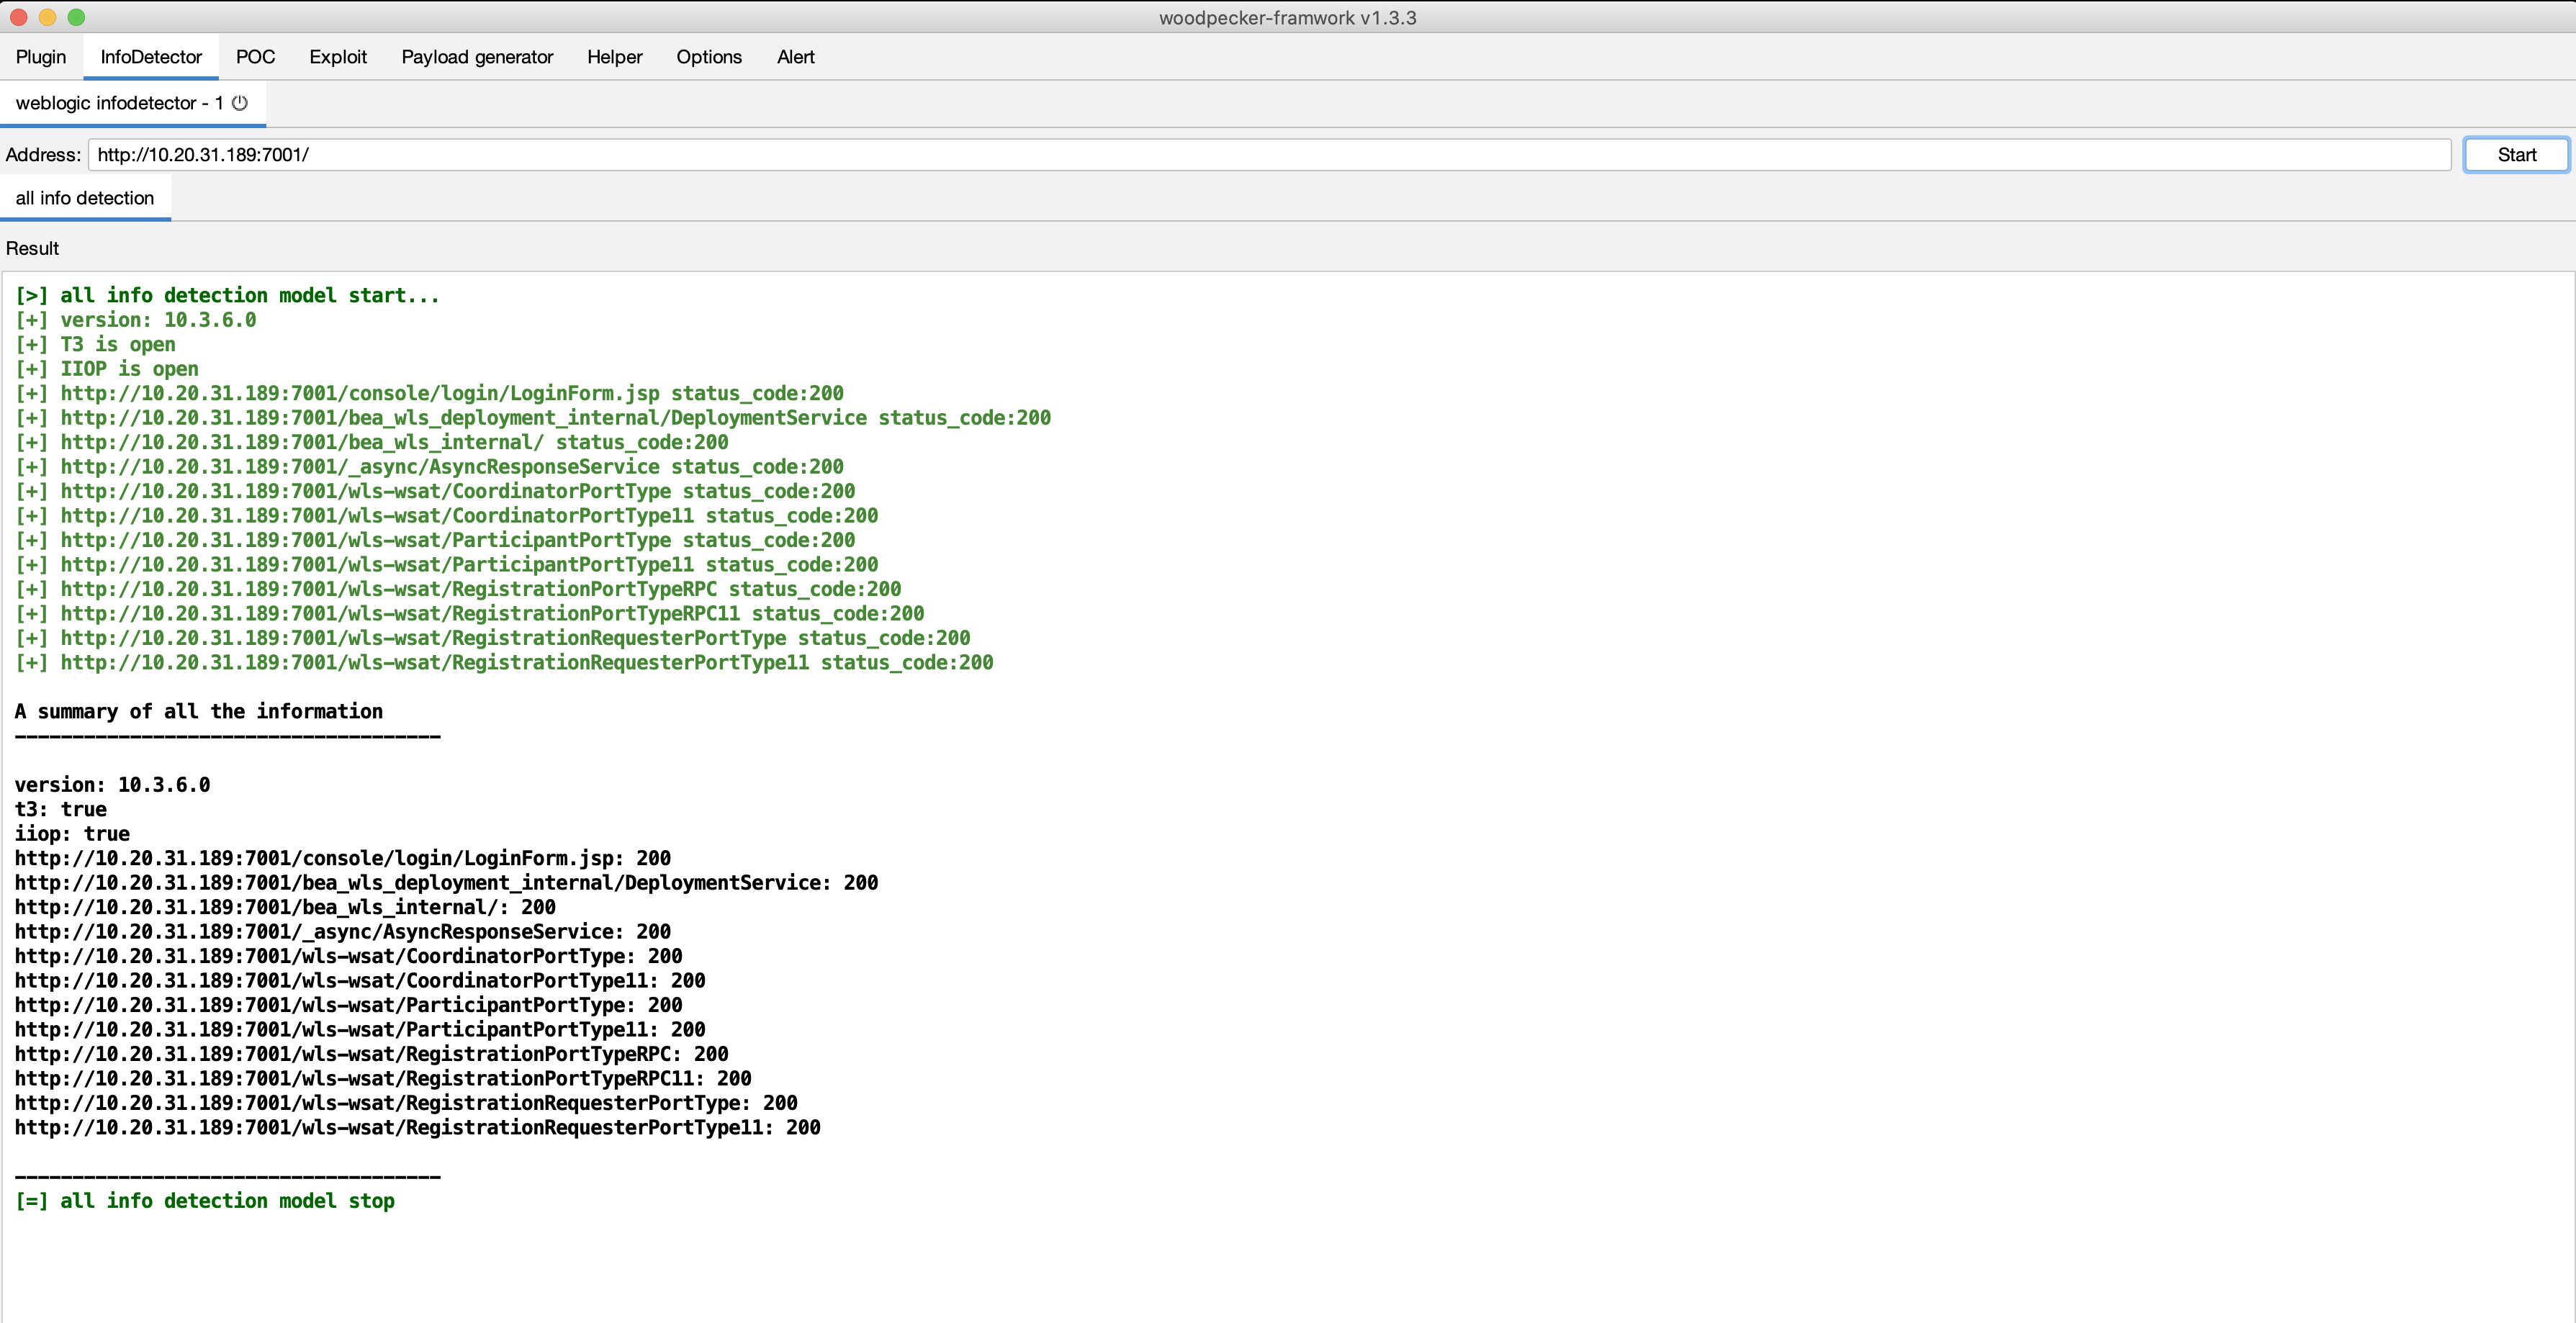 jas502n/woodpecker-plugins
woodpecker-plugins
 blue0x1/xpath
xpath is a fast, multi-technique XPath injection scanner written in Nim. It focuses on practical detection, response comparison, visible extraction,…
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.
 rapticore/ore_react2shell_scanner
CVE-2025-55182 (React2Shell) Scanner
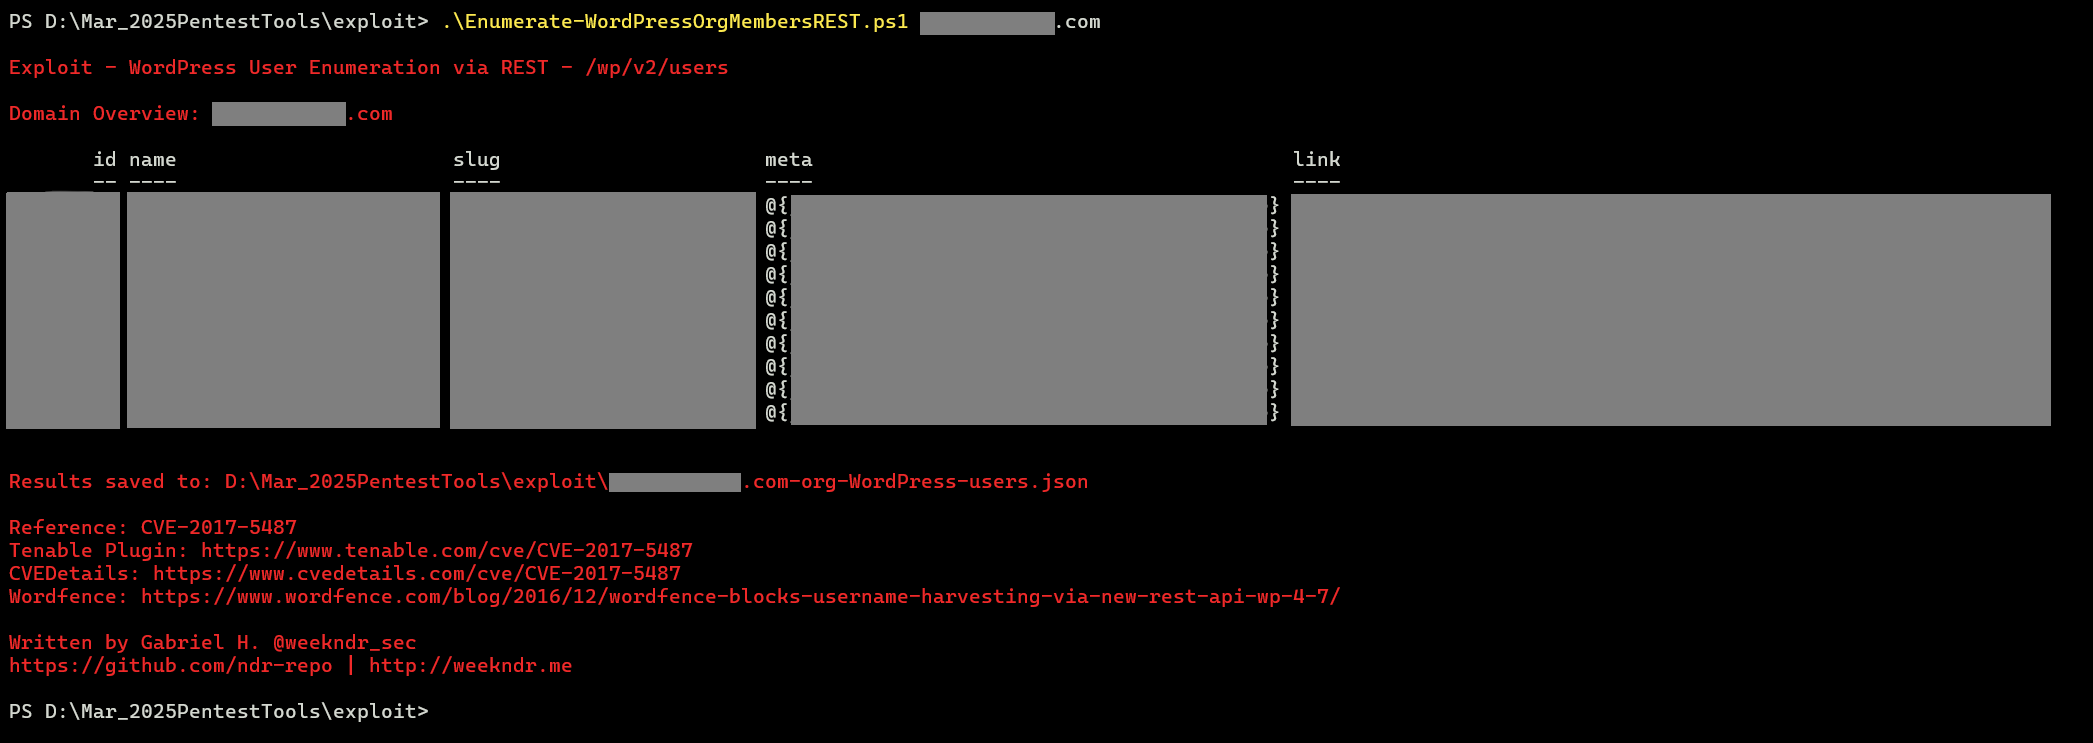 ndr-repo/cve-2017-5487
PoC for CVE-2017-5487 - WordPress User Enumeration via REST
 san-tus/dorkwright
From Dork to Download: Automating Google Dorks with Playwright
 gui-ying233/cve-2025-61638
Proof-of-concept exploit for CVE-2025-61638, a stored XSS vulnerability in MediaWiki's Sanitizer::validateAttributes. Tests for the flaw across…
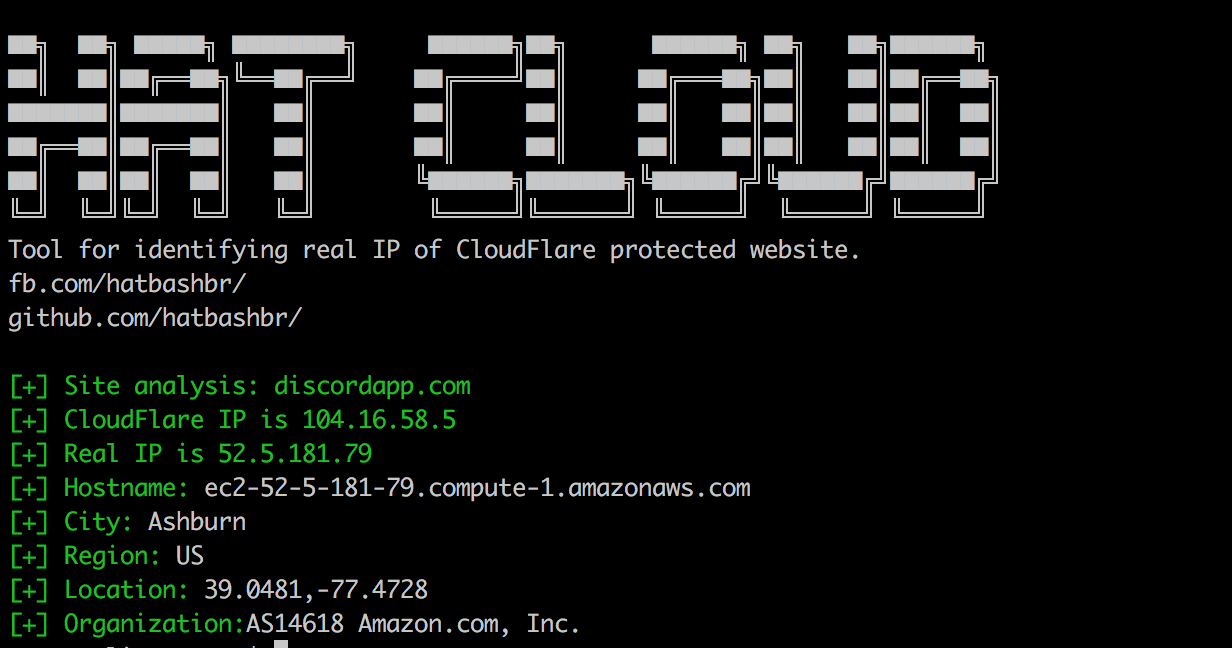
 ekultek/zeus-scanner
Advanced reconnaissance utility
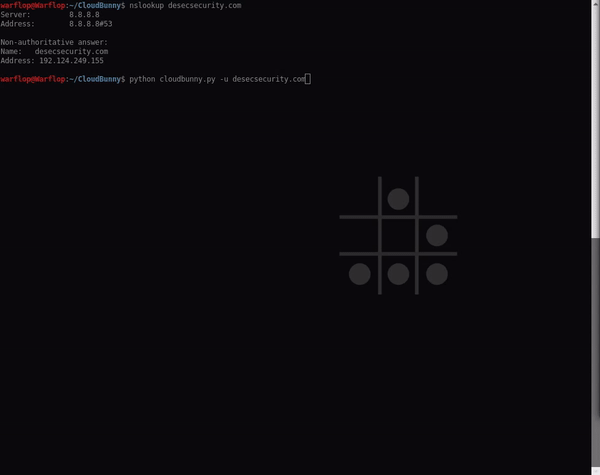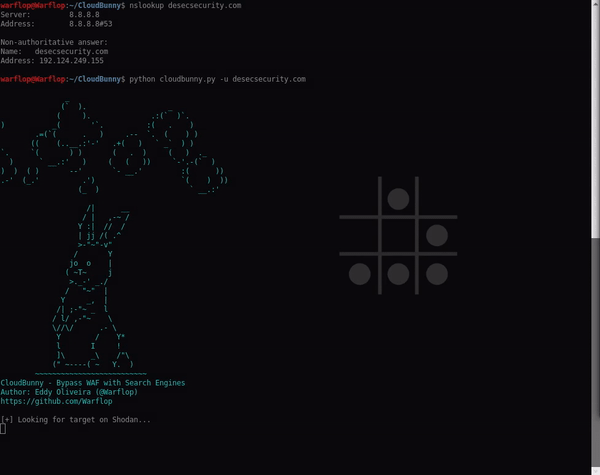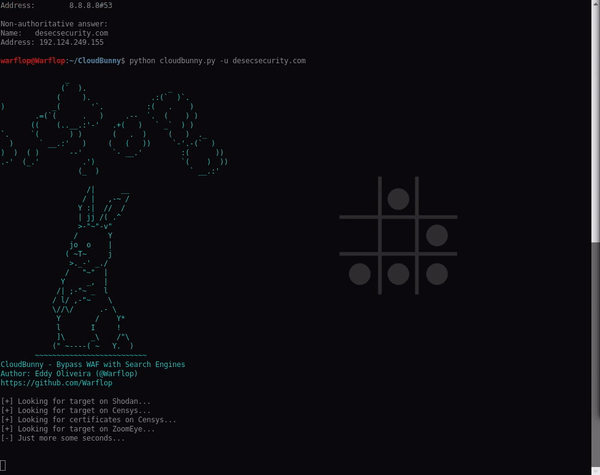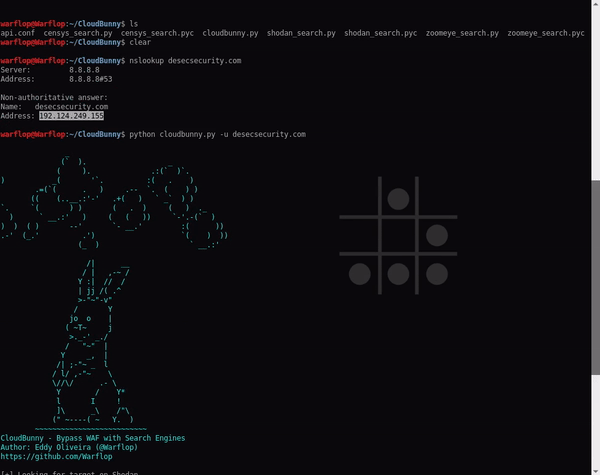 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…