
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
10 results
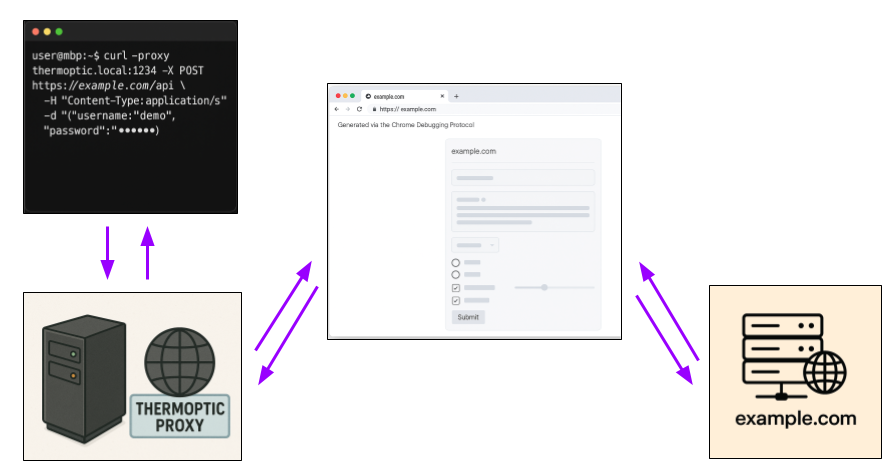
thermoptic preview

thermoptic

GitHubmandatoryprogrammer/thermoptic

A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.
anti-botcaptcha-bypasscrawler+5
1.1k
25 days ago
CVE-2021-44228-Apache-Log4j-Rce preview

CVE-2021-44228-Apache-Log4j-Rce

GitHubtangxiaofeng7/cve-2021-44228-apache-log4j-rce

Apache Log4j 远程代码执行
educationexploitationpayload-generation+4
904 years ago
CVE-2021-44228-Apache-Log4j-Rce preview

CVE-2021-44228-Apache-Log4j-Rce

GitHubyuuki1967/cve-2021-44228-apache-log4j-rce

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…
exploitationpayload-generationpenetration-testing+3
3 years ago
CVE-2021-44228-Apache-Log4j-Rce-main preview

CVE-2021-44228-Apache-Log4j-Rce-main

GitHubravid-checkmarx/cve-2021-44228-apache-log4j-rce-main

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…
exploitationpayload-generationpenetration-testing+4
4 years ago
CVE-2021-44228-Apache-Log4j-Rce preview

CVE-2021-44228-Apache-Log4j-Rce

GitHubkannthu/cve-2021-44228-apache-log4j-rce

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…
exploitationpayload-developmentpenetration-testing+3
4 years ago
Log4Shell preview

Log4Shell

GitHub0xsyr0/log4shell

This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
curated-resourceseducationexploitation+6
71 year ago
cloudbunny preview

cloudbunny

GitHubwarflop/cloudbunny

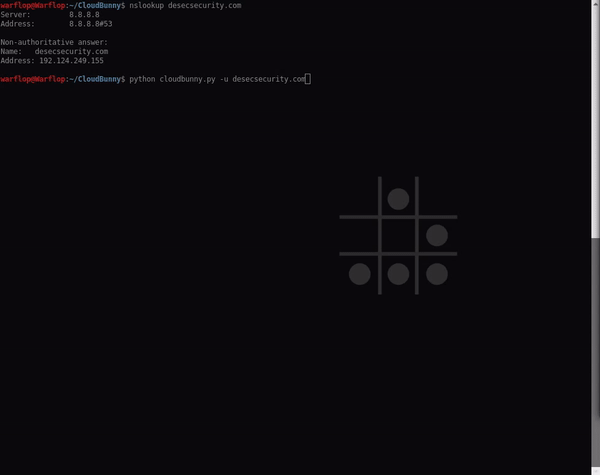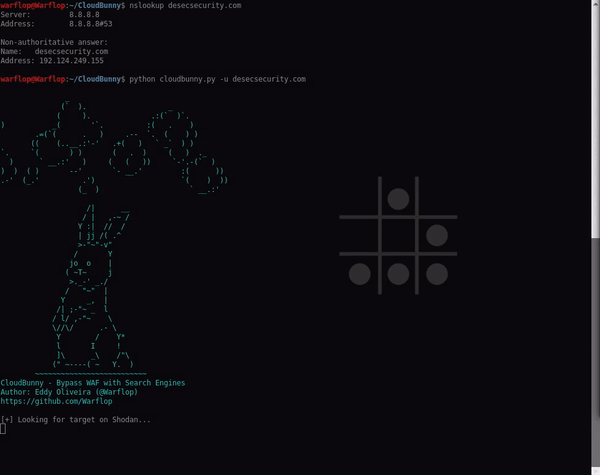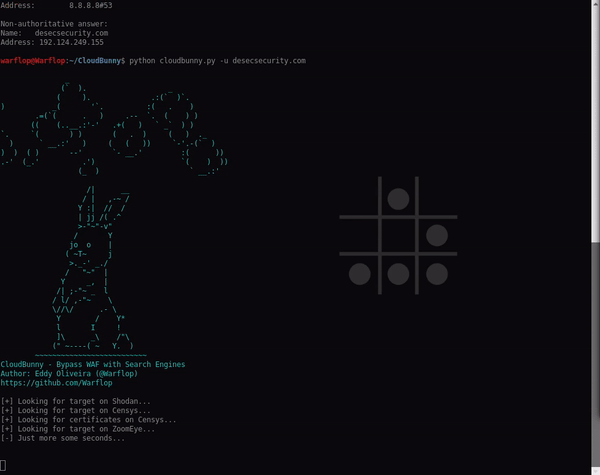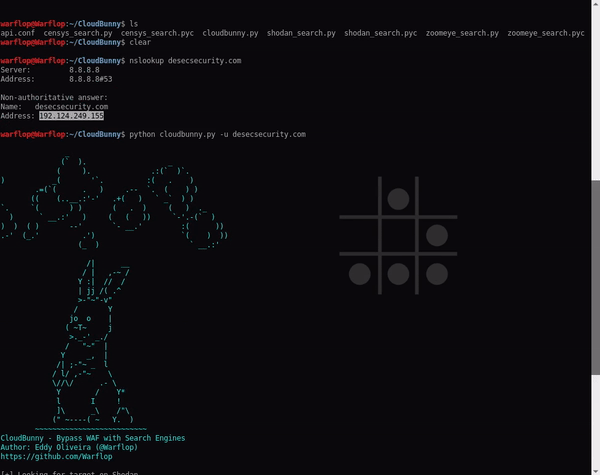
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
information-gatheringosintreconnaissance+2
3752 years ago
pFuzz preview

pFuzz

GitHubredsection/pfuzz

Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
fuzzingpenetration-testingred-teaming+2
1615 years ago
ftw preview

ftw

GitHubcoreruleset/ftw

YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
1431 day ago
CFUnmitigate preview
Archived

CFUnmitigate

GitHubmrakovic-org/cfunmitigate

Layer 7 UAM Bypass

anti-boteducationids-ips-evasion+2
106 years ago