

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
29 results
ip-obfuscation preview

ip-obfuscation

GitHubhackinglz/ip-obfuscation

Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…

educationimpersonation-toolspenetration-testing+6
47
10 months ago
unwaf preview

unwaf

GitHubmmarting/unwaf

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
1928 months ago
sqlmap-ai preview

sqlmap-ai

GitHubatiilla/sqlmap-ai

This script automates SQL injection testing using SQLMap with AI-powered decision making.
payload-generationpenetration-testingvulnerability-scanners+3
4538 months ago
react2shell-scanner preview

react2shell-scanner

GitHuborwagodfather/react2shell-scanner

RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
exploitationpenetration-testingwaf-bypass+3
1810 months ago
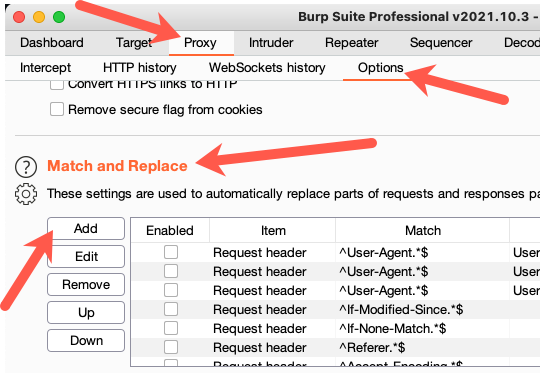
BurpSuiteHTTPSmuggler preview

BurpSuiteHTTPSmuggler

GitHubnccgroup/burpsuitehttpsmuggler

A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
ids-ips-evasionpenetration-testingvulnerability-analysis+3
7447 years ago
Imperva_gzip_WAF_Bypass preview

Imperva_gzip_WAF_Bypass

GitHubbishopfox/imperva_gzip_waf_bypass

Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
ids-ips-evasionpenetration-testingvulnerability-analysis+2
1694 years ago
CVE-2022-31813 preview

CVE-2022-31813

GitHubyiliufeng168/cve-2022-31813

Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…
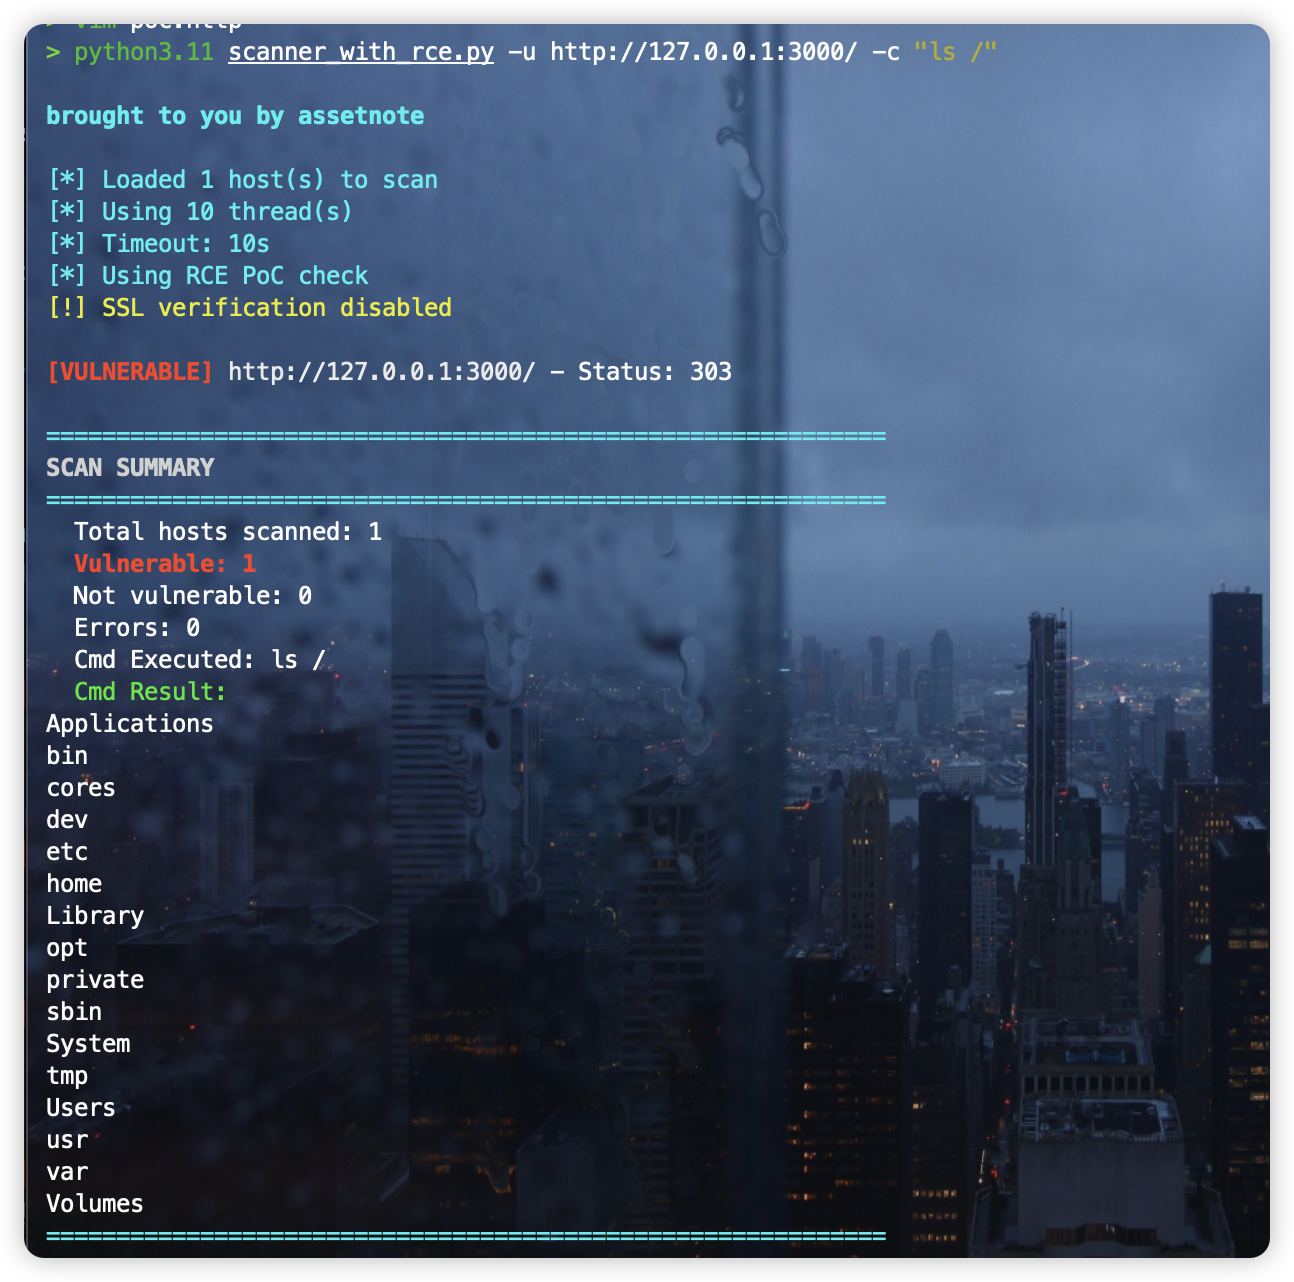
exploitationpenetration-testingvulnerability-analysis+2
7 months ago
CVE-2025-55182-React2Shell preview

CVE-2025-55182-React2Shell

GitHubrsch-io/cve-2025-55182-react2shell

React2Shell (CVE-2025-55182) proof-of-concept (PoC) exploit demonstrating a CRITICAL remote code execution (RCE) vulnerability in modern web…
educationexploitationpayload-generation+4
110 months ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubzzhorc/cve-2025-55182

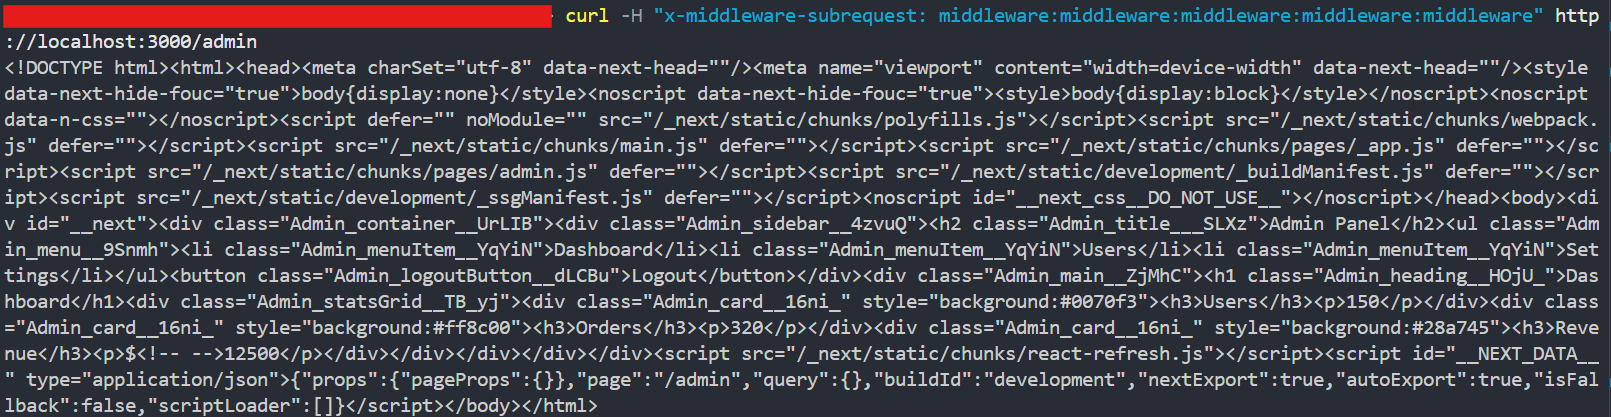
CVE-2025-55182复现环境及RCE回显poc
exploitationpayload-generationpenetration-testing+4
810 months ago
POC-CVE-2025-29927 preview

POC-CVE-2025-29927

GitHubeve-satoru/poc-cve-2025-29927

CVE-2025-29927 Proof of Concept
authentication-authorizationexploitationvulnerability-analysis+3
31 year ago
web-application-firewall- preview

web-application-firewall-

GitHubnithylesh/web-application-firewall-

This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
educationexploitationids-ips-evasion+5
32 years ago
React2Shell_CVE-2025-55182 preview

React2Shell_CVE-2025-55182

GitHubyanoshercohen/react2shell_cve-2025-55182

React2Shell (CVE-2025-55182) Exploit
educationexploitationpayload-development+6
46 months ago
anti-jndi preview

anti-jndi

GitHubph0lk3r/anti-jndi

Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.
defensive-toolsids-ips-evasionmisconfiguration+3
24 years ago
web-threat-mitigation preview

web-threat-mitigation

GitHubbrunoh6/web-threat-mitigation

Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
configuration-auditingdevsecopseducation+8
1 year ago
react2shell-scanner preview

react2shell-scanner

GitHubassetnote/react2shell-scanner

High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
exploitationpayload-generationpenetration-testing+3
2.5k10 months ago
react2shell-scanner preview

react2shell-scanner

GitHubalessiodos/react2shell-scanner

CVE-2025-55182 & CVE-2025-66478 Detection Tool for Next.js RSC RCE
exploitationpenetration-testingvulnerability-scanners+3
110 months ago
CVE-2025-61638 preview
Archived

CVE-2025-61638

GitHubgui-ying233/cve-2025-61638

Proof-of-concept exploit for CVE-2025-61638, a stored XSS vulnerability in MediaWiki's Sanitizer::validateAttributes. Tests for the flaw across…
exploitationinformation-gatheringpenetration-testing+3
12 months ago
React2Shell preview

React2Shell

GitHubprowlsec/react2shell

An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…

command-and-controlexploitationpayload-generation+4
110 months ago
Previous12Next