
CVE-2026-5524-PoC
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Detection, mitigation, and reverse-engineering tooling for CVE-2026-41940 (SessionScribe): the cPanel/WHM unauthenticated session-forgery…

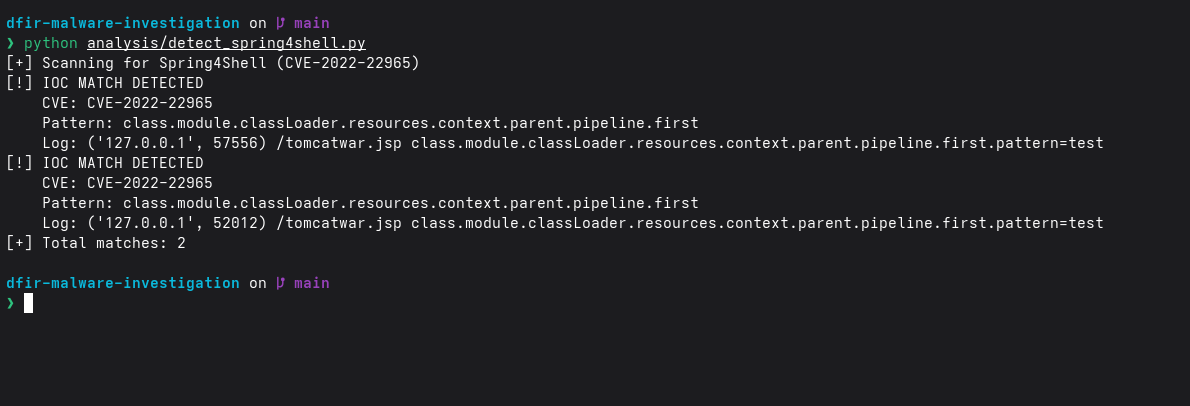
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

MISP <= 2.5.27 - Stored Cross-Site Scripting via Workflow Engine (doT.js Template Injection).

This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder

Enhance your malware detection with WAF + YARA (WAFARAY)

Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)

Automated Tool That Generates The Perfect Meterpreter Powershell Payload