

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.7k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
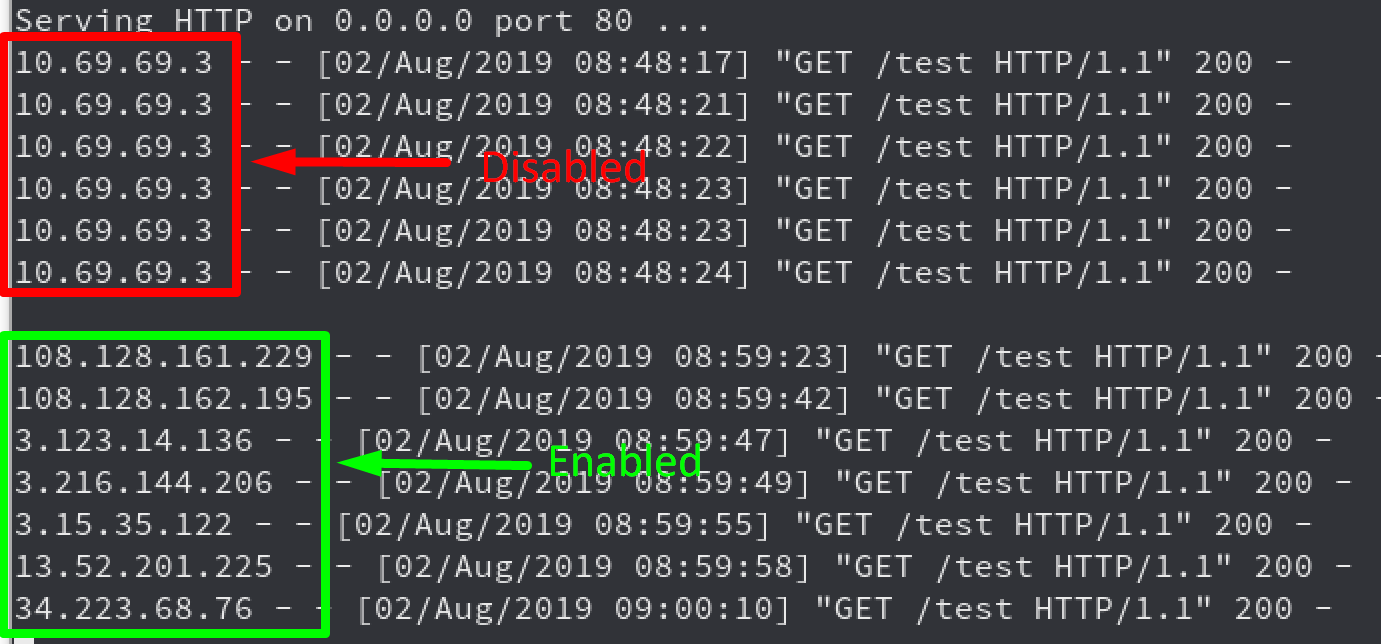 rhinosecuritylabs/iprotate_burp_extension
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.
 clouedoc/autosqli
An automatic SQL Injection tool which takes advantage of ~DorkNet~ Googler, Ddgr, WhatWaf and sqlmap.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
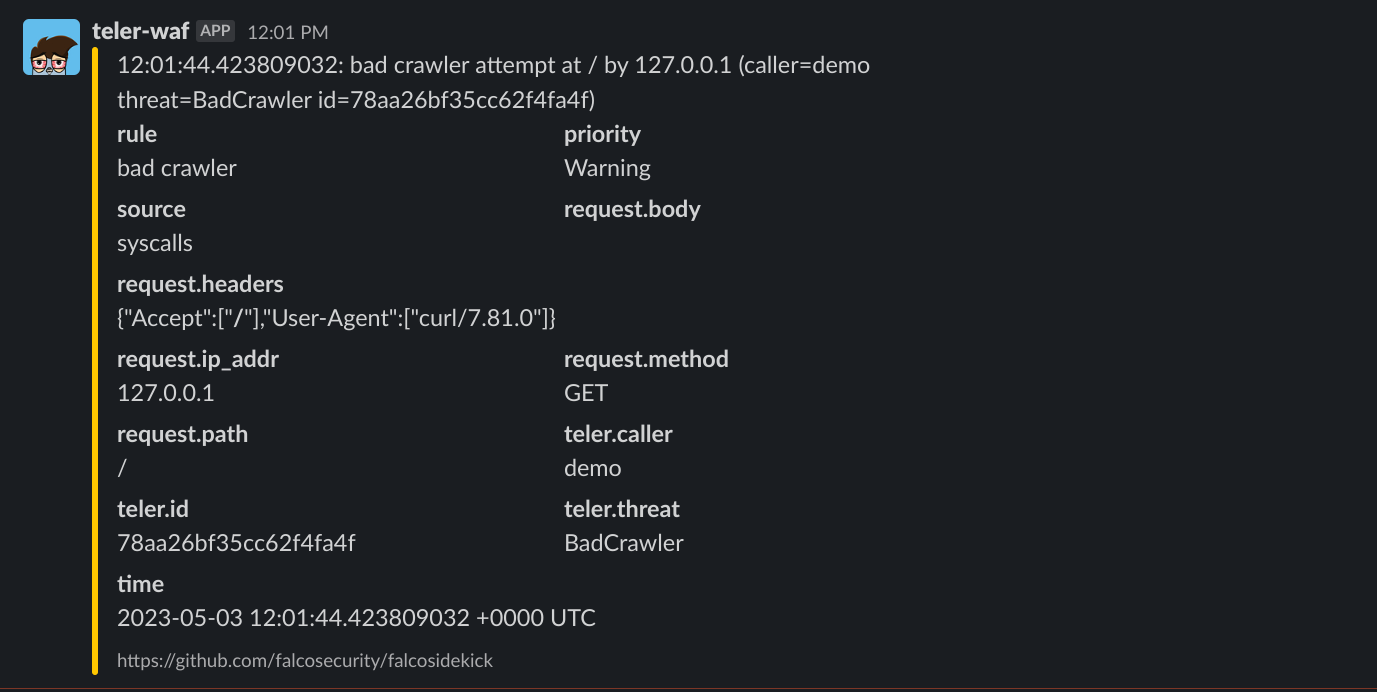 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
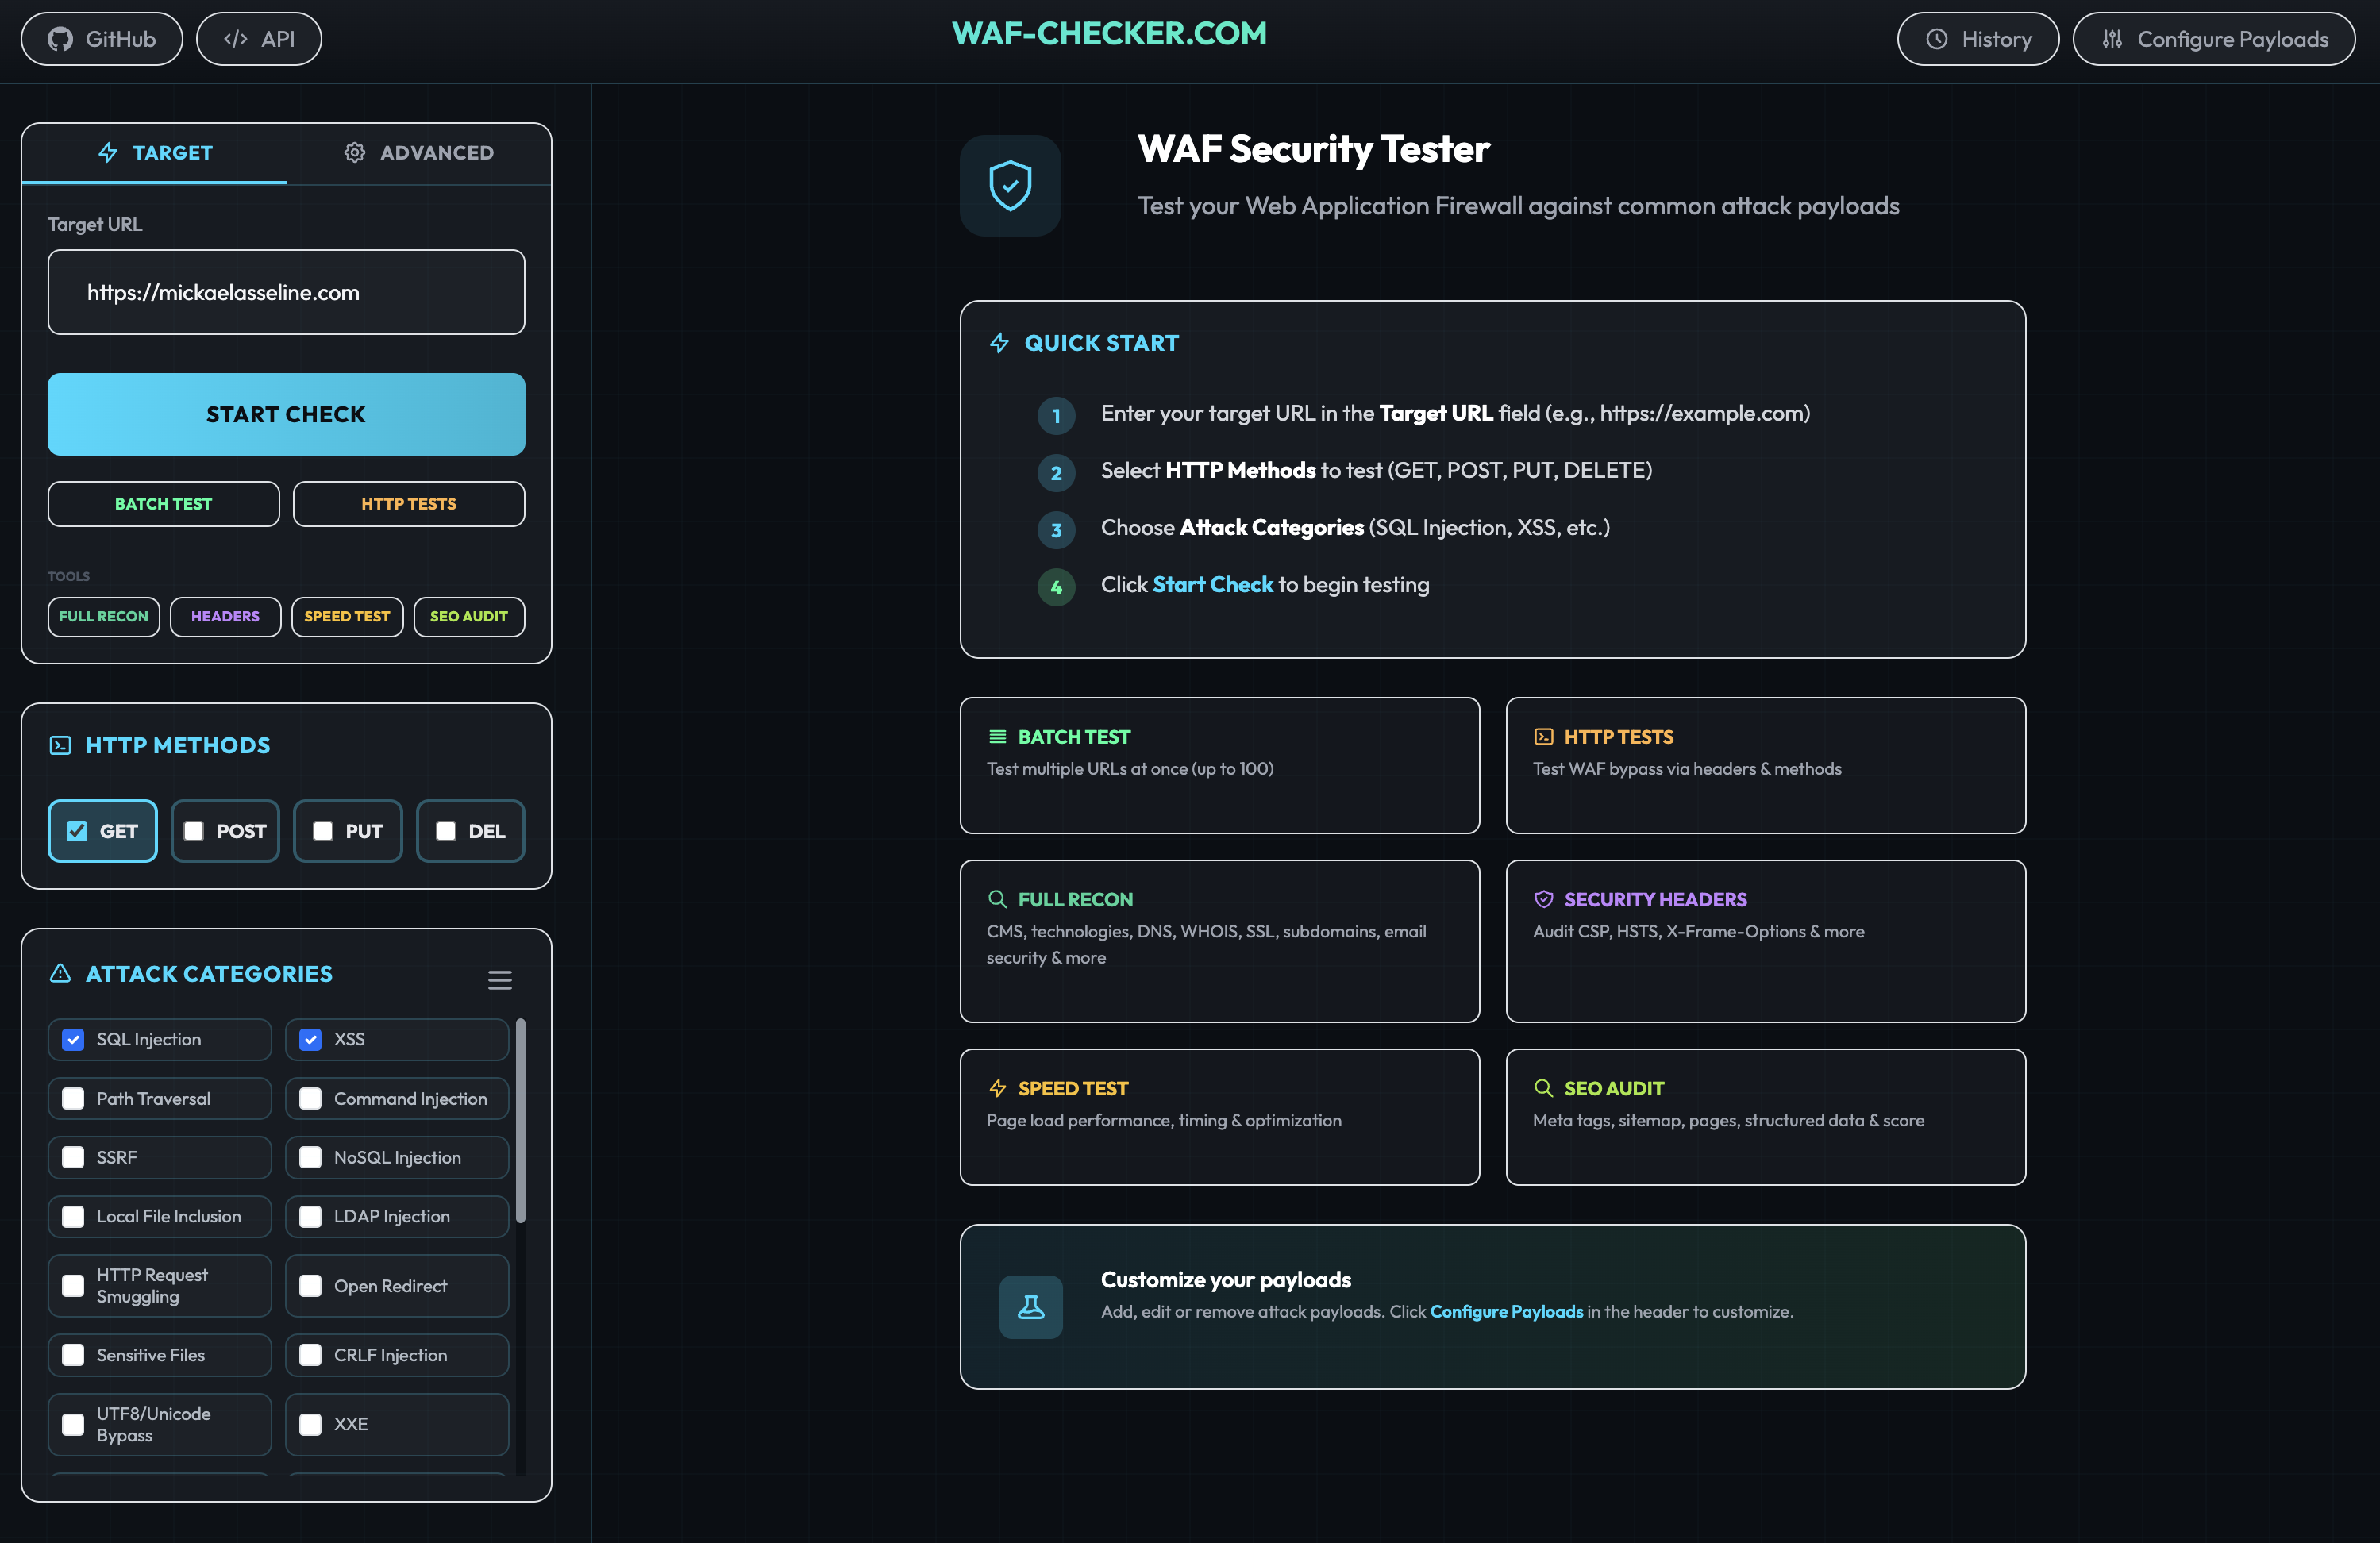 papamica/waf-checker
Tests your WAF with +160 payloads
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 dheerajmadhukar/4-zero-3
403/401 Bypass Methods + Bash Automation + Your Support ;)
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 puliczek/cve-2021-44228-poc-log4j-bypass-words
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
 alt3kx/wafaray
Enhance your malware detection with WAF + YARA (WAFARAY)
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 wysiiwyg/log4j_0day_rce
Log4j-RCE (CVE-2021-44228) Proof of Concept
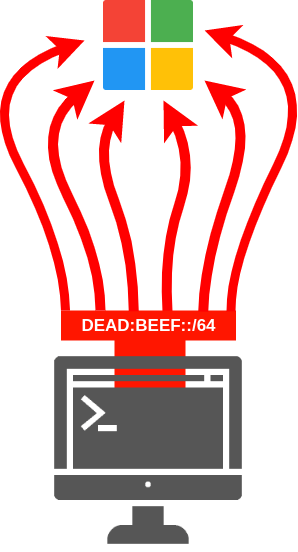 blacklanternsecurity/trevorproxy
A SOCKS proxy written in Python that randomizes your source IP address. Round-robin your evil packets through SSH tunnels or give them billions of…