
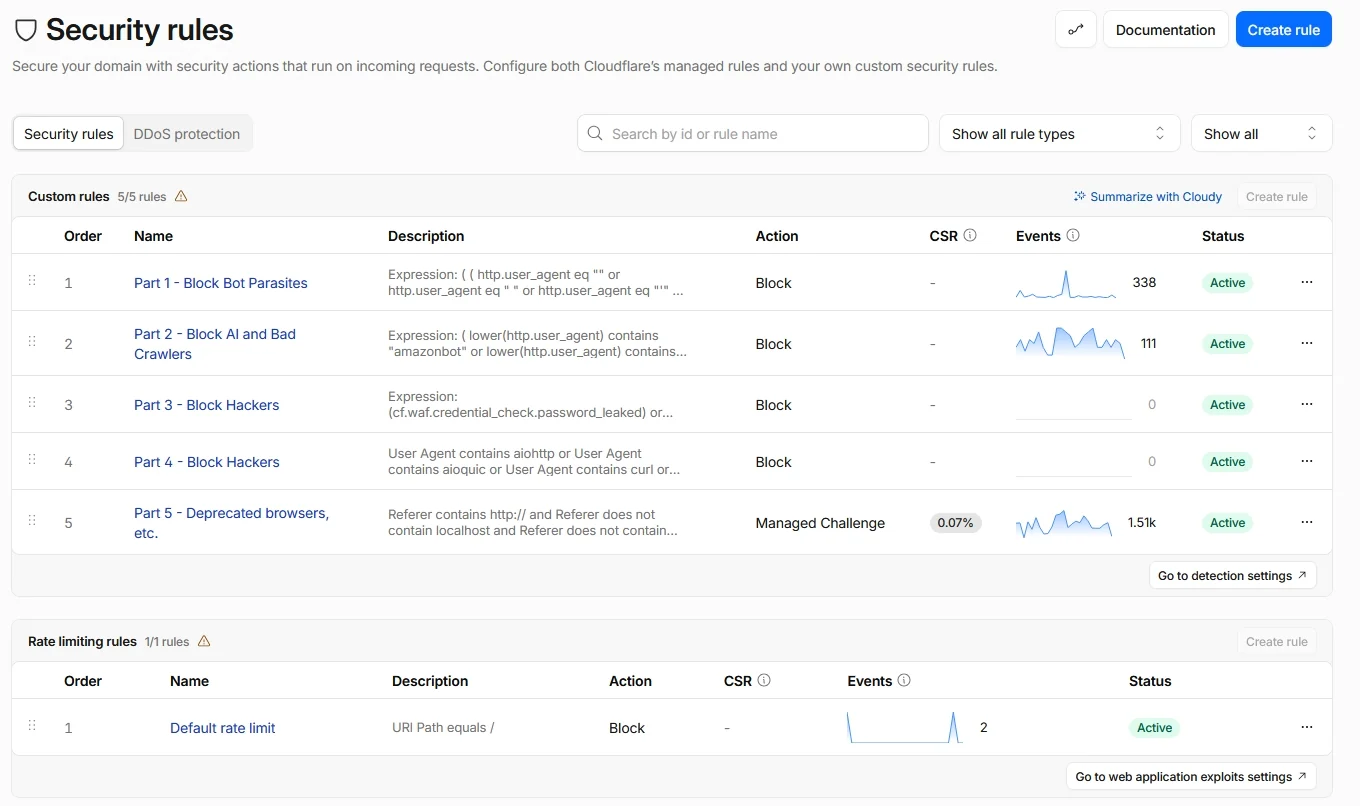
cloudflare-security-art
 buybitart/cloudflare-security-art
Cloudflare Free Plan security rules (Zero Trust approach) for small websites
anti-botconfiguration-auditingcurated-resources+5
225
buybitart/cloudflare-security-artCloudflare Free Plan security rules (Zero Trust approach) for small websites
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
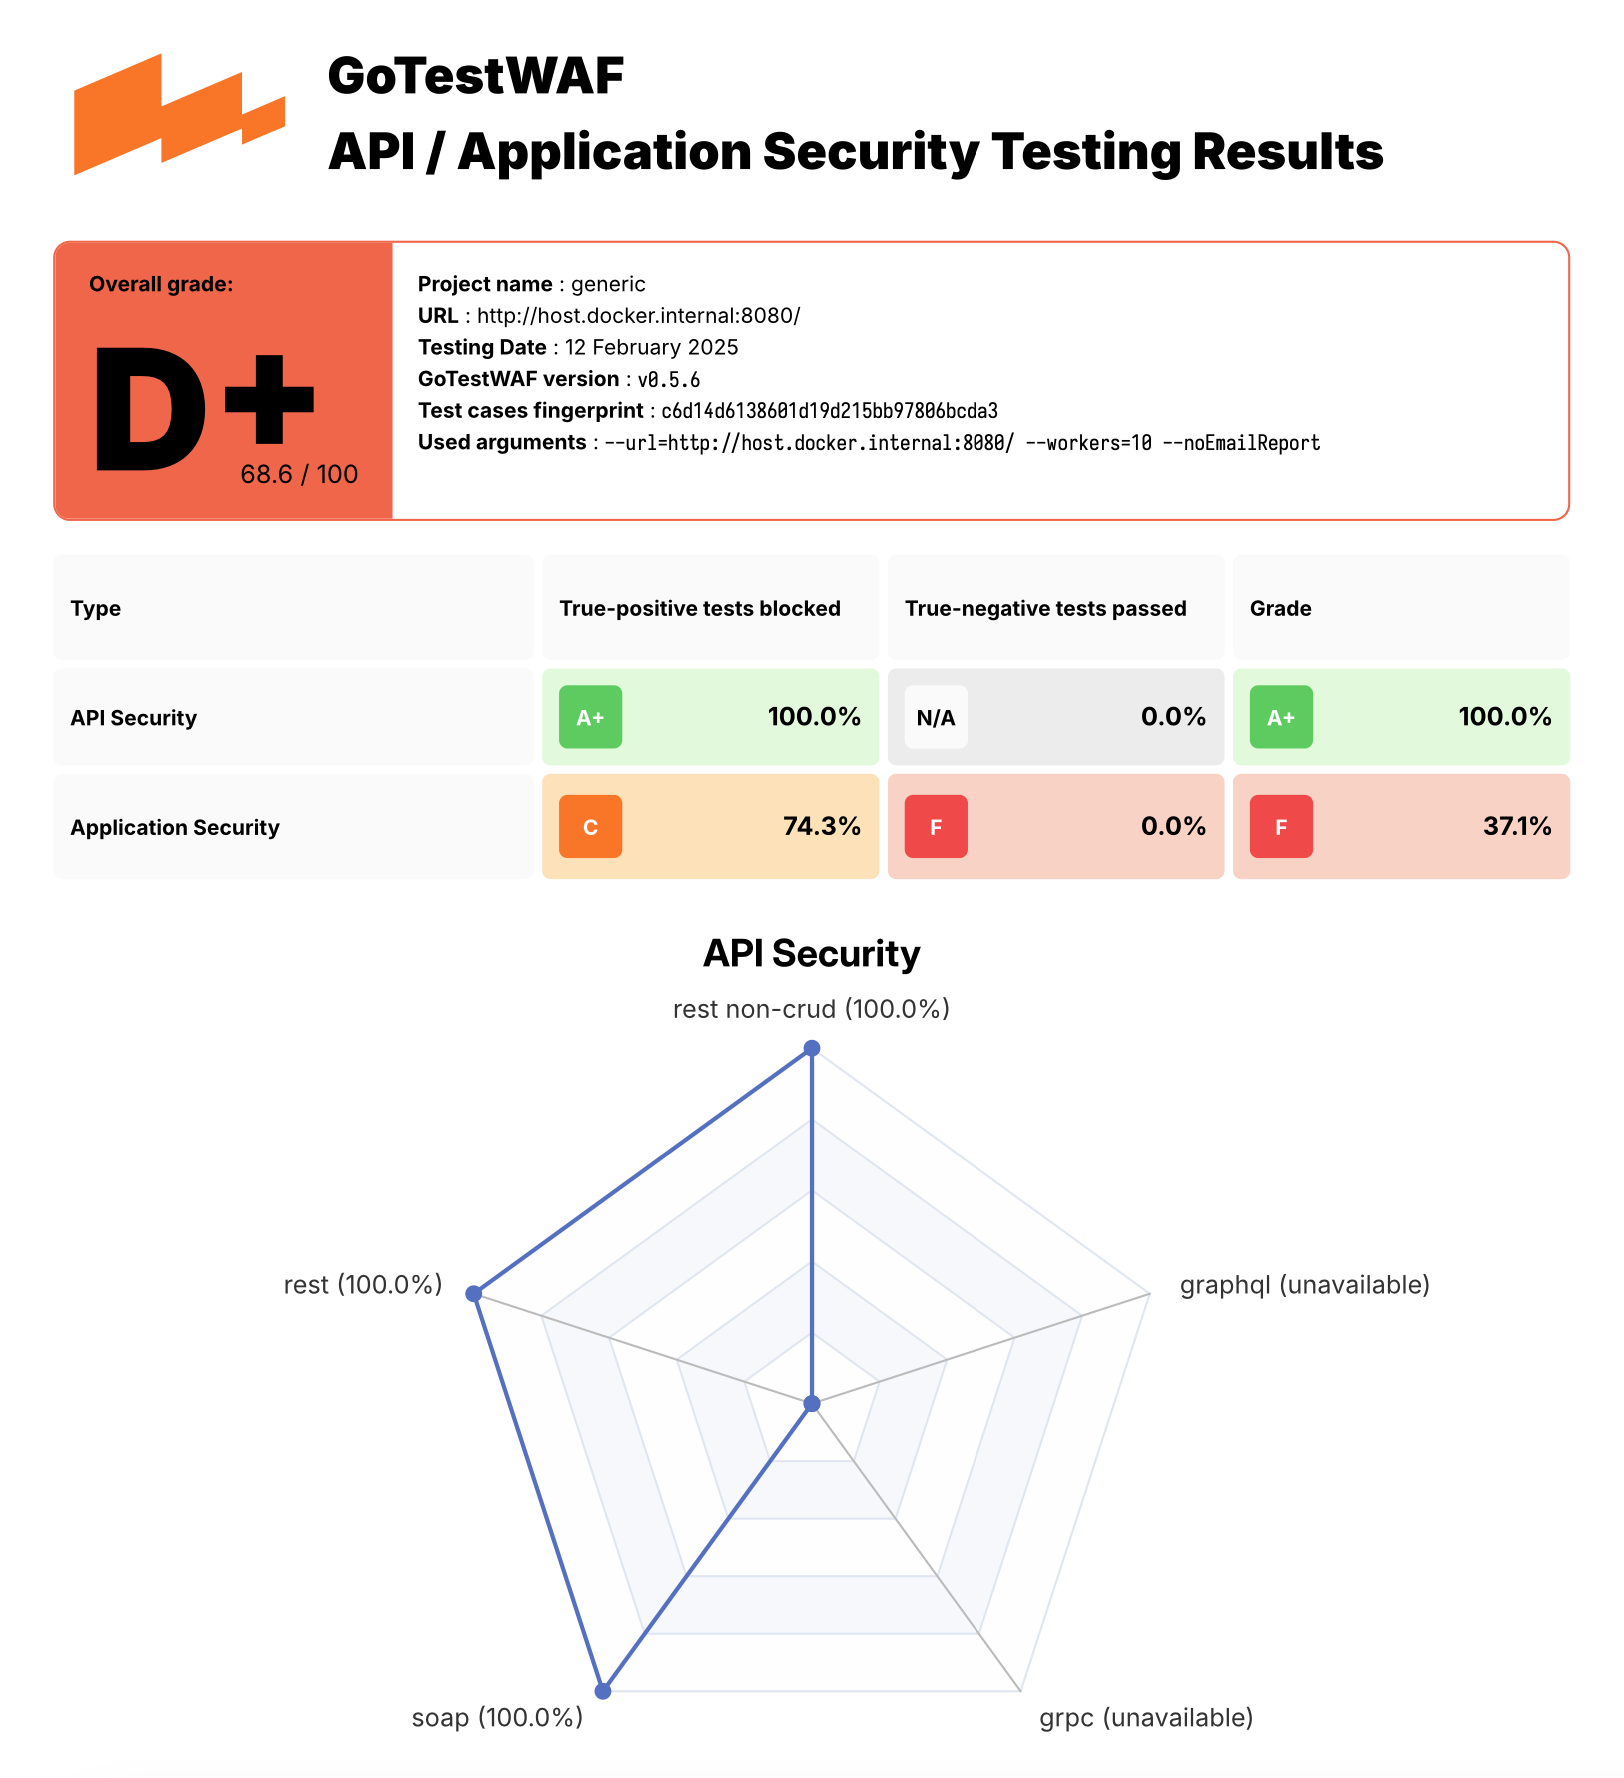 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 nbs-system/naxsi
NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX
 iamblacksolo2-bugbounty/poc2-cve-2025-55182
Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…
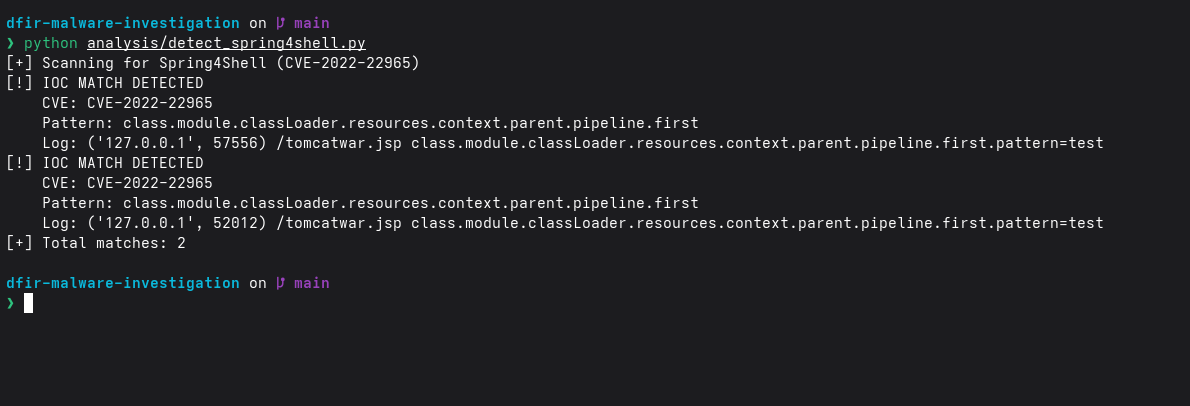 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 wysiiwyg/log4j_0day_rce
Log4j-RCE (CVE-2021-44228) Proof of Concept
 zidansec/cloudpeler
PHP CLI tool that resolves the real origin IP behind CloudFlare-protected websites, returning hostname, organization, geolocation, and DNS data for…