POC-CVE-2025-24813-Apache-Tomcat-Remote-Code-Execution

Este repositorio contiene un exploit automatizado desarrollado con fines educativos y de investigación en ciberseguridad, dirigido a demostrar una…

Este repositorio contiene un exploit automatizado desarrollado con fines educativos y de investigación en ciberseguridad, dirigido a demostrar una…

React2Shell (CVE-2025-55182) proof-of-concept (PoC) exploit demonstrating a CRITICAL remote code execution (RCE) vulnerability in modern web…

Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…

Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.

This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…

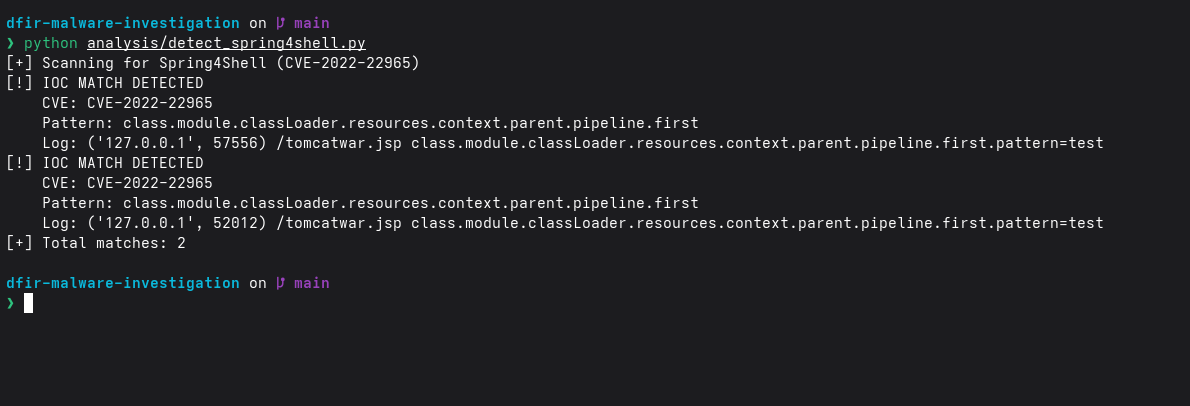
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

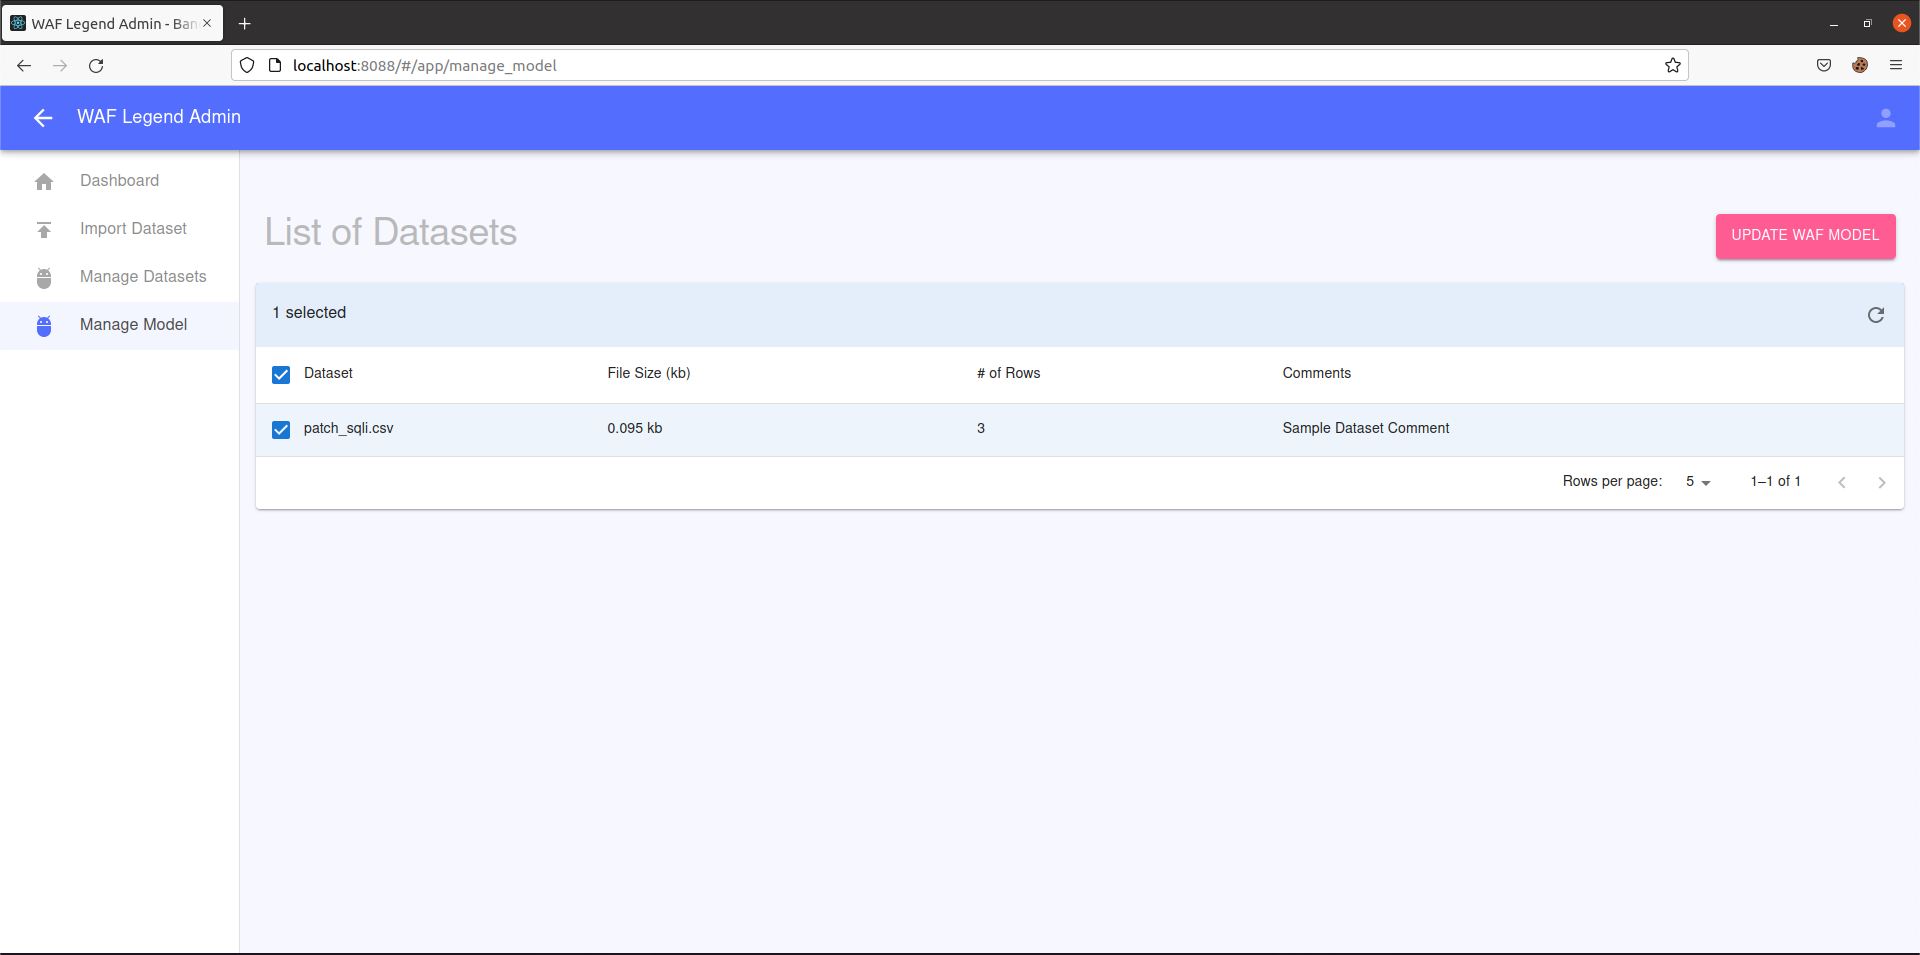
First iteration of ML based Feedback WAF

Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)

Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…

Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.

🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks

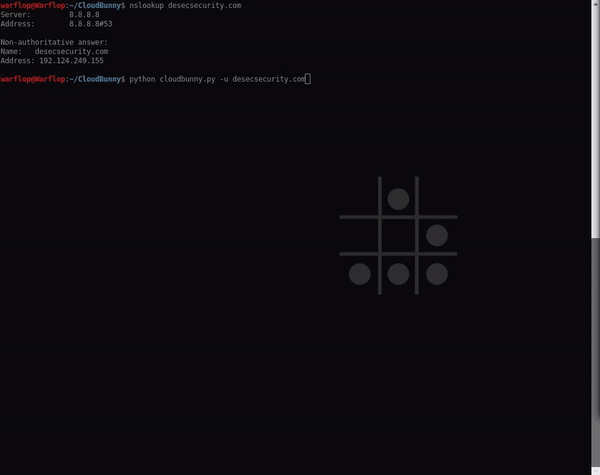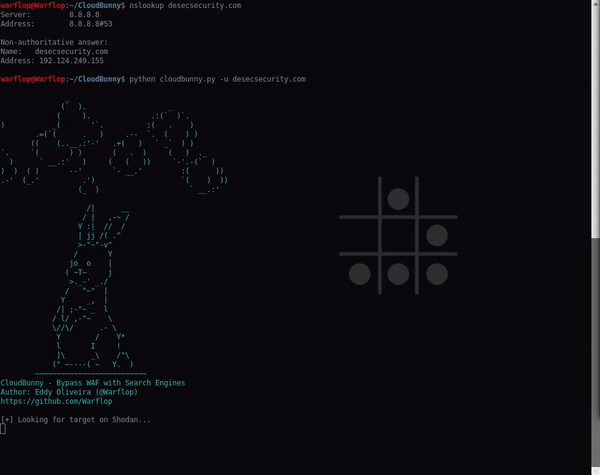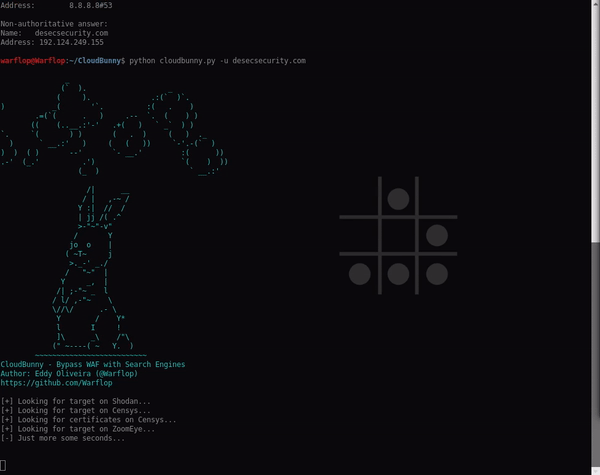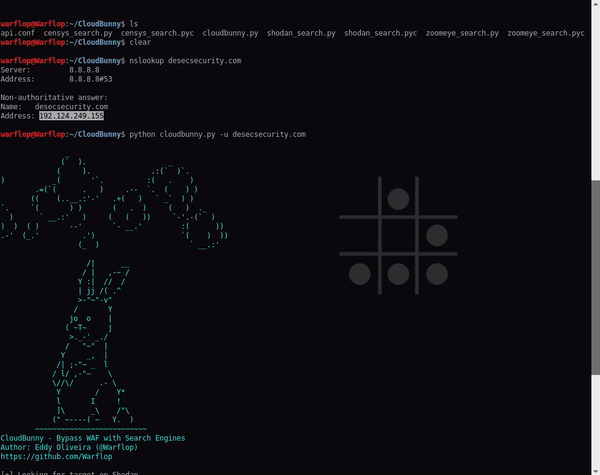
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…

Proof-of-concept exploit for CVE-2025-55182, demonstrating unauthenticated RCE in Next.js App Router via server-side object injection in React Server…

Detailed technical analysis and proof-of-concept exploit for CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol. Covers path…


This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…

Quickjack is a point-and-click tool for intuitively producing advanced clickjacking and frame slicing attacks.