
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
FUCK-CDN preview

FUCK-CDN

GitHub0xshe/fuck-cdn

Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
dns-analysisdns-subdomain-enumerationinformation-gathering+9
169
3 months ago
unwaf preview

unwaf

GitHubmmarting/unwaf

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
1968 months ago
XXERipper preview

XXERipper

GitHubkamalx06/xxeripper

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
131 month ago
ftw preview

ftw

GitHubcoreruleset/ftw

YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…

devsecopspenetration-testingvulnerability-scanners+2
1431 day ago
dalfox preview

dalfox

GitHubhahwul/dalfox

Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…

devsecopsdynamic-code-analysispenetration-testing+5
5.3k8h 4m ago
waf-checker preview

waf-checker

GitHubsech0us3/waf-checker

Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
api-security-testingids-ips-evasioninformation-gathering+6
384 days ago
CVE-2026-1357-POC preview

CVE-2026-1357-POC

GitHubcybertechajju/cve-2026-1357-poc

Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
data-exfiltrationexploitationpenetration-testing+5
98 months ago
CVE-2026-61511-PoC-Exploit preview

CVE-2026-61511-PoC-Exploit

GitHubtc4dy/cve-2026-61511-poc-exploit

CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
database-securityexploitationnetwork-mapping+7
620 days ago
bug-reaper preview

bug-reaper

GitHubshaniidev/bug-reaper

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
api-security-testingctfeducation+8
758 months ago
CVE-2026-87902 preview

CVE-2026-87902

GitHubbhideki/cve-2026-87902

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
21 month ago
wpx preview

wpx

GitHubgreg-randall/wpx

Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
api-security-testingcrawlerinformation-gathering+6
107 months ago
CVE-2025-55182-research preview

CVE-2025-55182-research

GitHubejpir/cve-2025-55182-research

Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…
educationexploitationpapers-research+4
79010 months ago
CVE-2025-61638 preview
Archived

CVE-2025-61638

GitHubgui-ying233/cve-2025-61638

Proof-of-concept exploit for CVE-2025-61638, a stored XSS vulnerability in MediaWiki's Sanitizer::validateAttributes. Tests for the flaw across…
exploitationinformation-gatheringpenetration-testing+3
12 months ago
nmap-log4shell preview

nmap-log4shell

GitHubgiterlizzi/nmap-log4shell

Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…
exploitationnetwork-securitypayload-generation+4
794 years ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubceh-aditya-raj/cve-2025-55182

Proof-of-concept exploit for CVE-2025-55182, demonstrating unauthenticated RCE in Next.js App Router via server-side object injection in React Server…
educationexploitationpayload-development+5
210 months ago
CVE-2017-5487 preview

CVE-2017-5487

GitHubndr-repo/cve-2017-5487

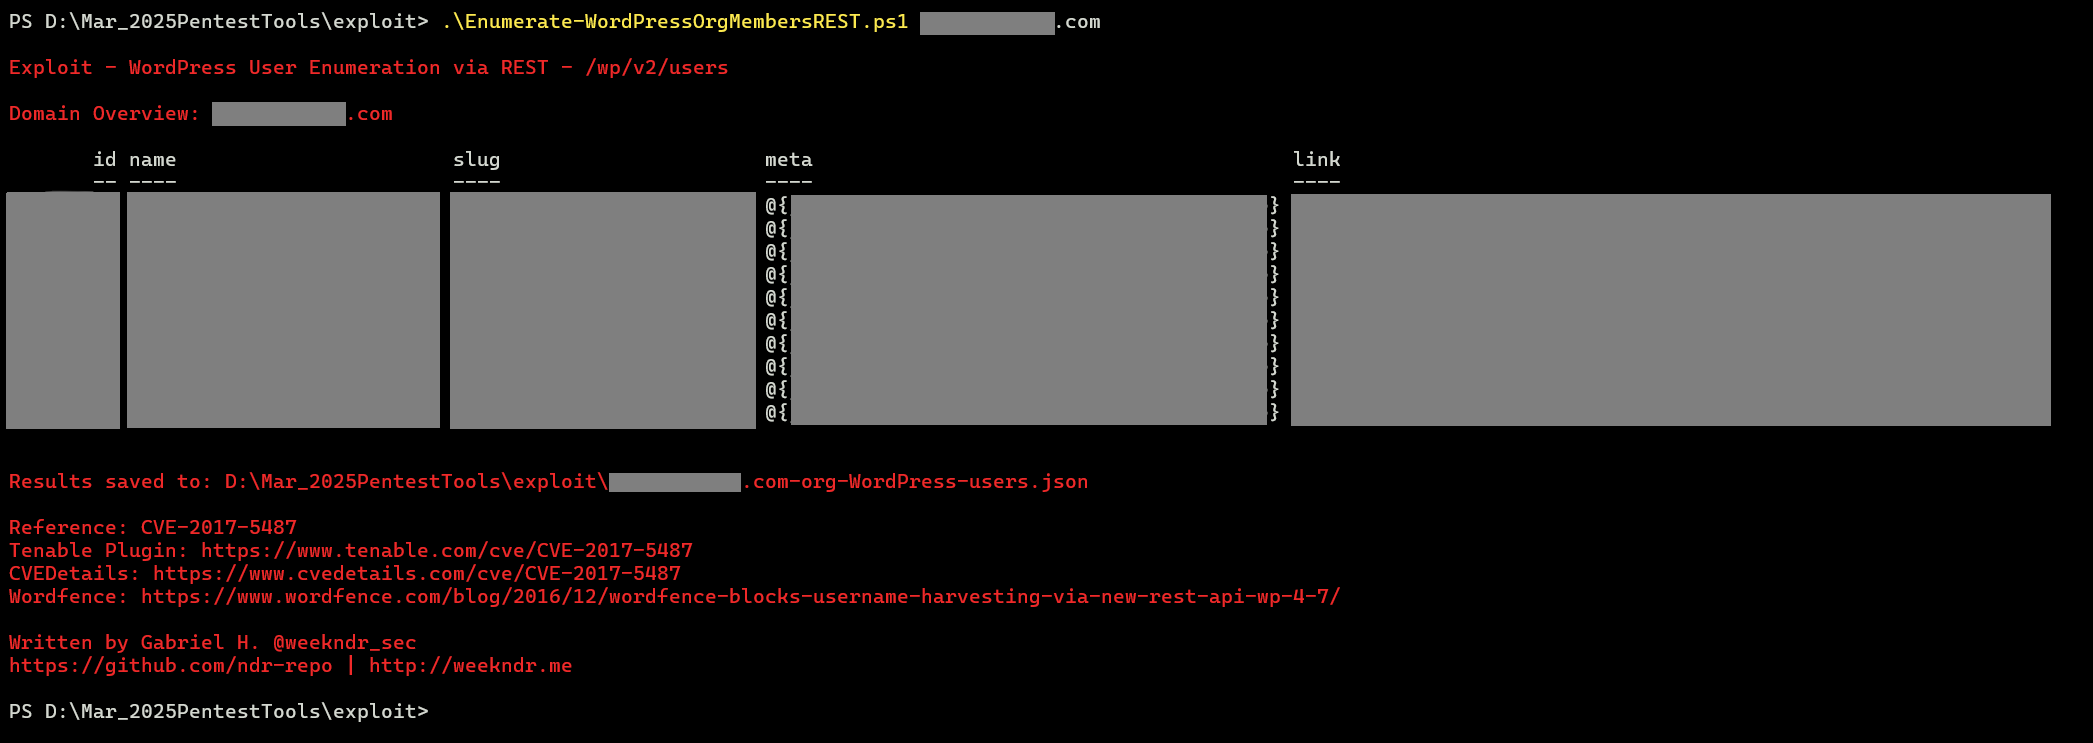
PoC for CVE-2017-5487 - WordPress User Enumeration via REST
information-gatheringpenetration-testingred-teaming+3
1 year ago
CVE-2026-21876 preview

CVE-2026-21876

GitHubmefhika120/cve-2026-21876

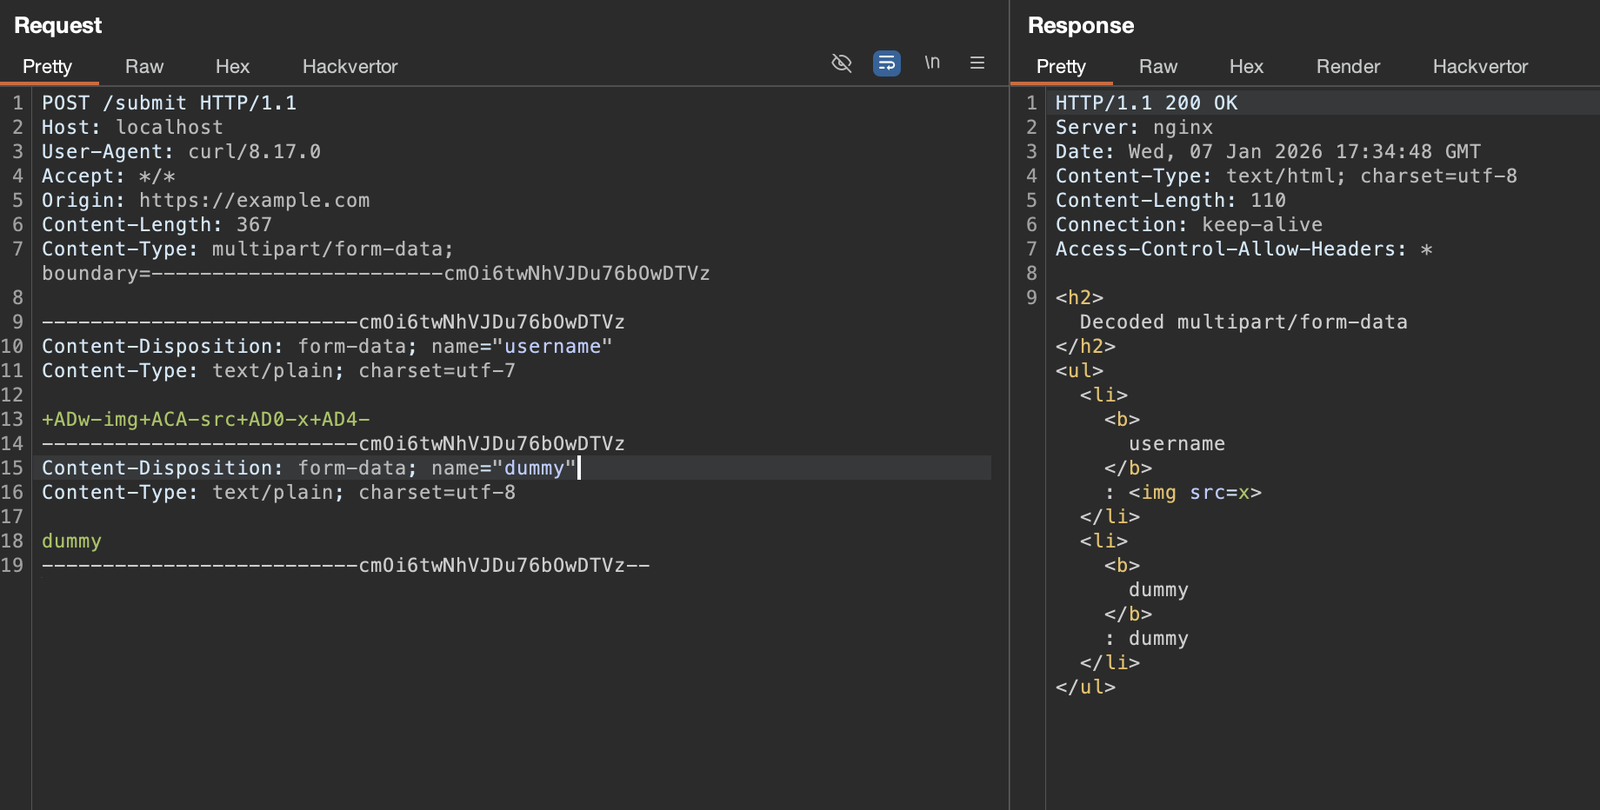
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
exploitationpenetration-testingvulnerability-analysis+2
9 months ago
CVE-2025-59342 preview
Archived

CVE-2025-59342

GitHubbytereaper77/cve-2025-59342

C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…

exploitationpenetration-testingvulnerability-analysis+2
11 year ago
Previous12Next