

LFISuite
 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
exploitationpayload-generationpenetration-testing+3
2.0k
d35m0nd142/lfisuiteTotally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
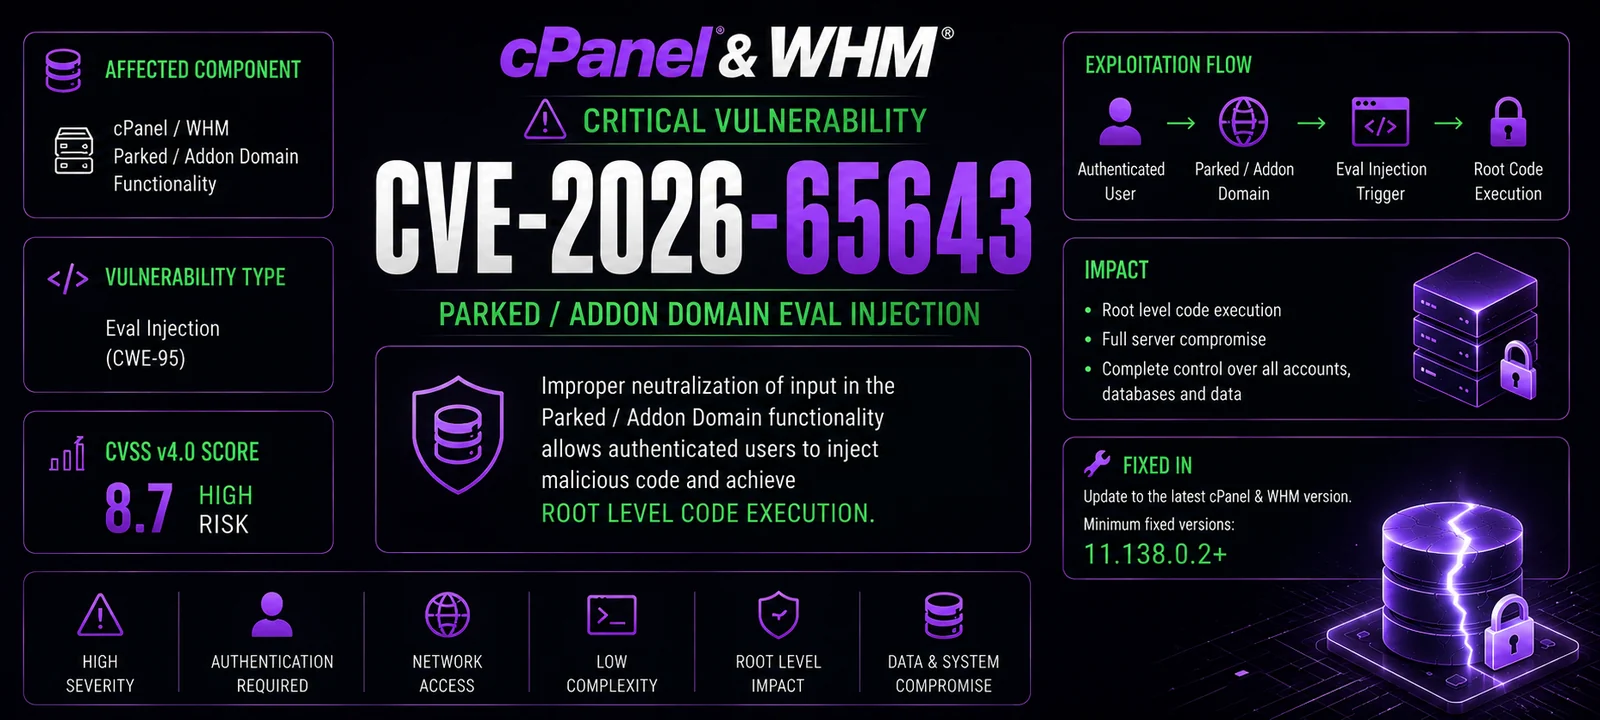 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
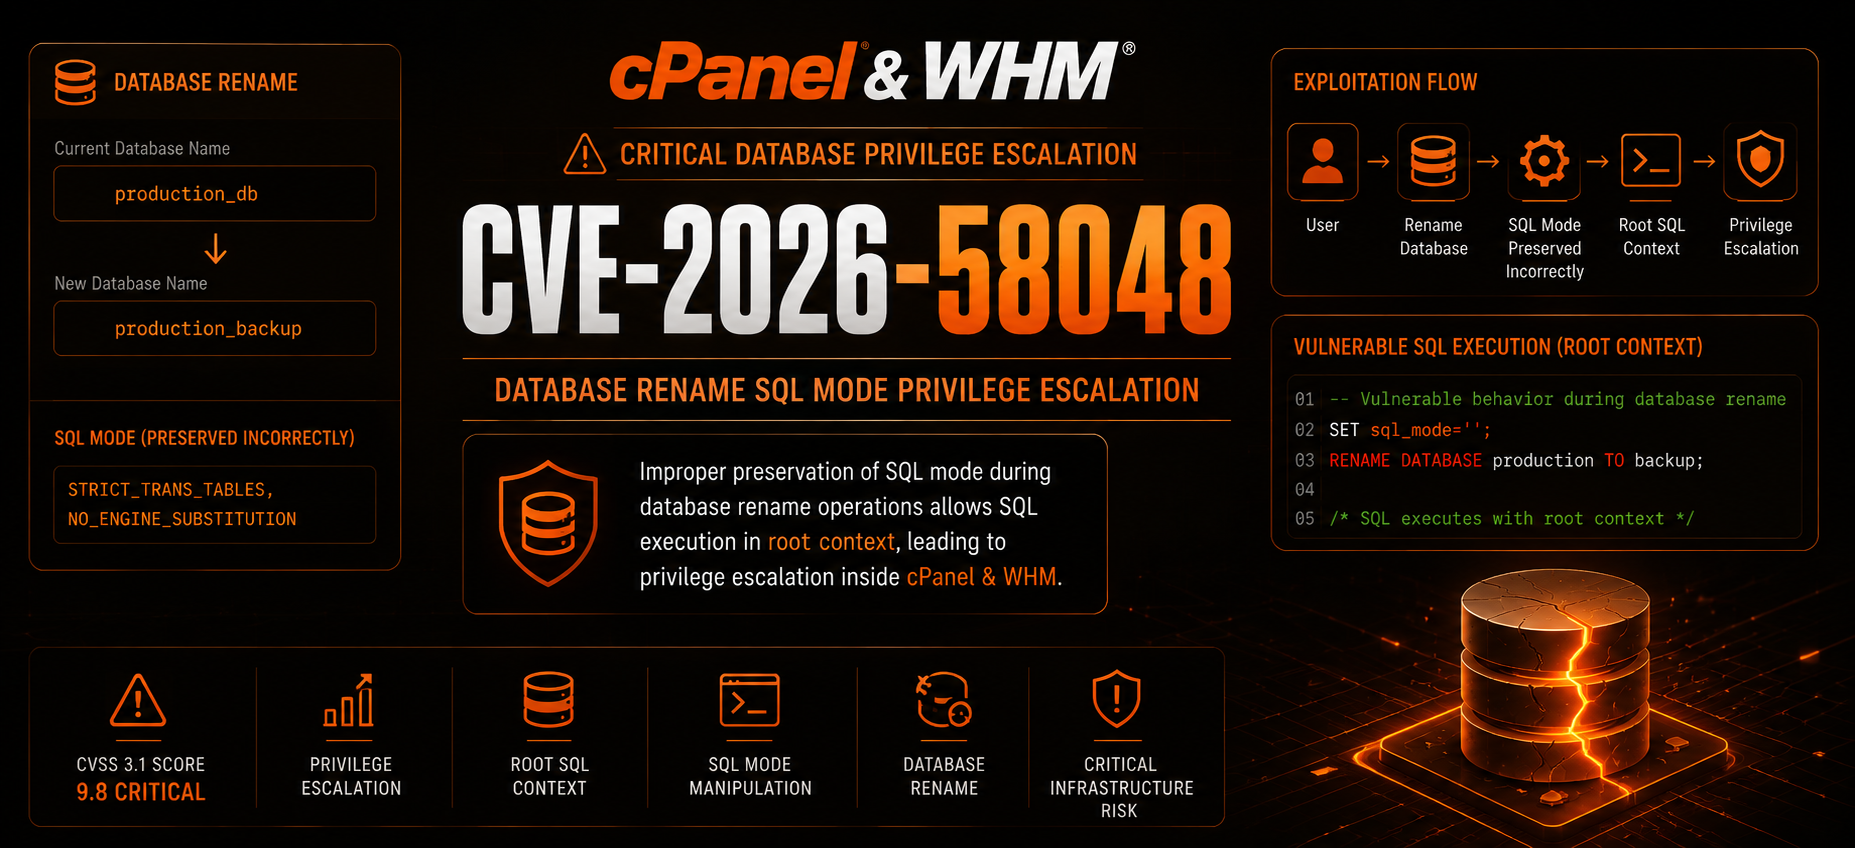 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
 faisalfs10x/gitlab-cve-2021-22205-scanner
Python-based scanner for GitLab CVE-2021-22205 remote code execution, with Shodan integration for target discovery and reverse shell delivery.
 ghxstsec/cve-2026-39987
Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…
 iloveflag/fast-cve-2022-22965
Graphical detection tool for CVE-2022-22965 (Spring4Shell) with one-click reverse shell generation, command execution, and multi-server shell path…
 thumpbo/cve-2026-21962
Exploit script for CVE-2026-21962, enabling remote command execution on vulnerable web servers with single-target, batch, and reverse shell modes.
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 aktia1/megaquagga_pentesting_report
Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…
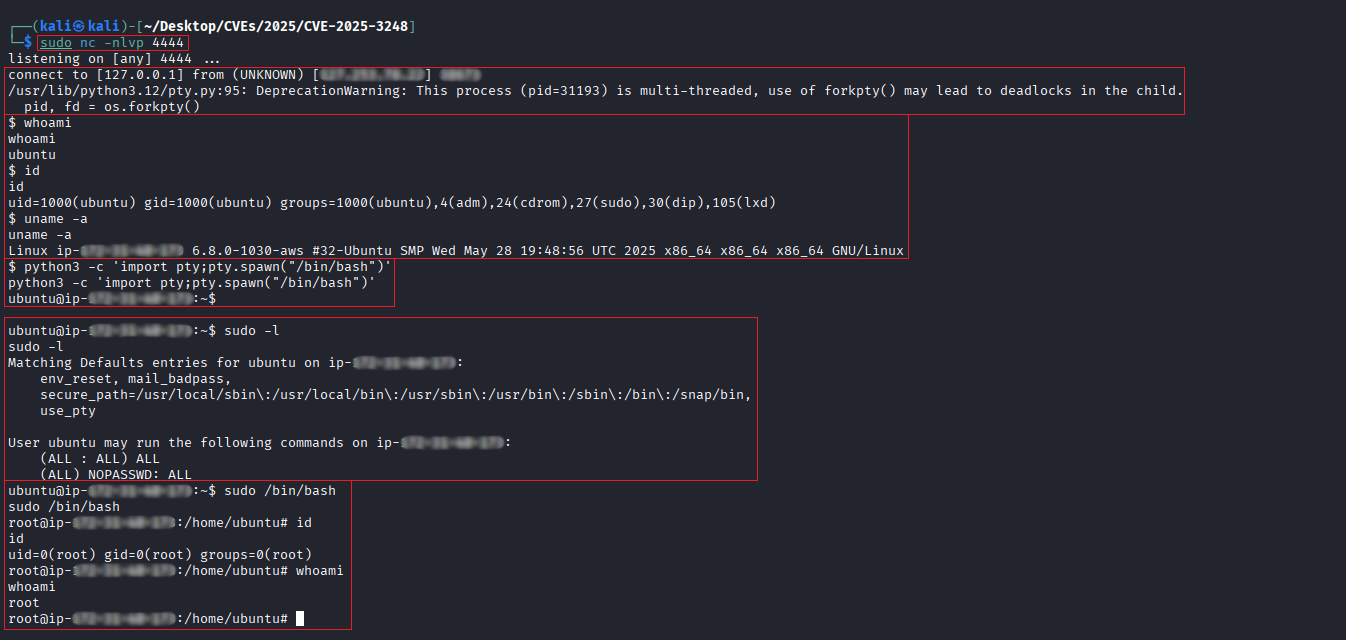 r0otk3r/cve-2025-3248
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 devdanqtuan/cve-2021-22205
Python exploit for CVE-2021-22205, a remote command execution vulnerability in GitLab CE/EE. Supports single-target exploitation, batch scanning, and…
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 pelagornisandersi/windows-7-automated-exploitation-using-metasploit-framework-
Automated bash script which scans an ip for potential vulnerability to eternalblue using nmap and then exploit using metasploit framework which uses…
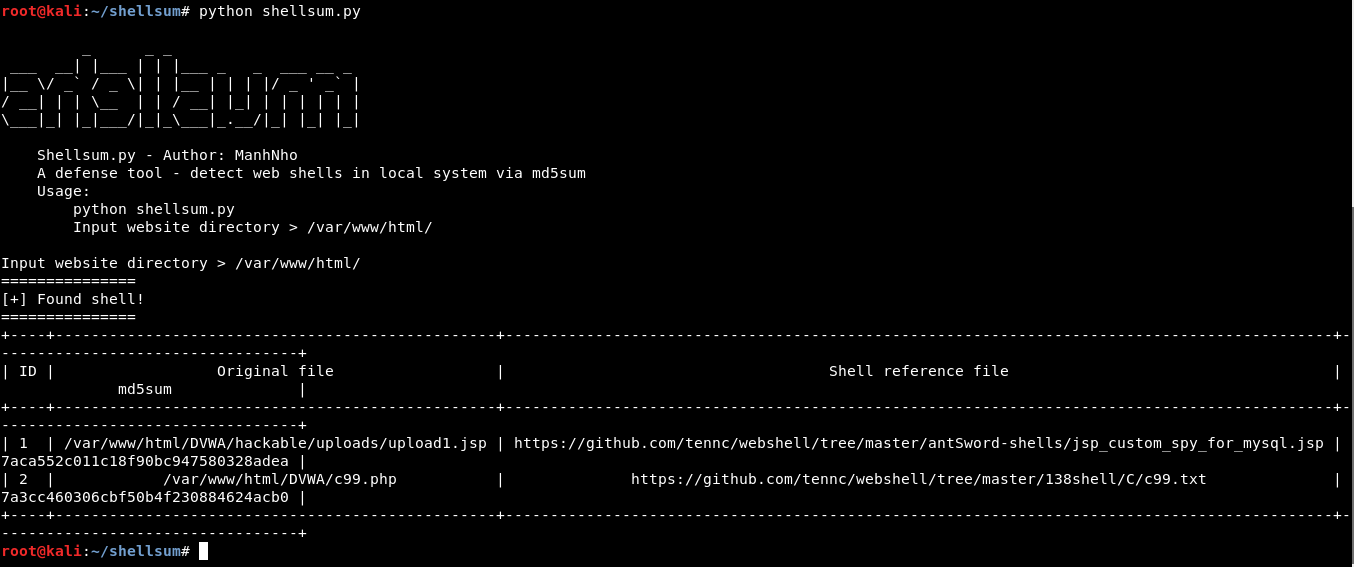 manhnho/shellsum
A defense tool - detect web shells in local directories via md5sum