
CVE-2025-55182-Next.js-RCE
 lucyz1125/cve-2025-55182-next.js-rce
Nextjs RCE Exploit
exploitationpenetration-testingvulnerability-scanners+3
2
lucyz1125/cve-2025-55182-next.js-rceNextjs RCE Exploit
 hyan0116/next.js-rce-cve-2025-55182
next.js rce exploit
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 wagiro/burpbounty
Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and…
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.
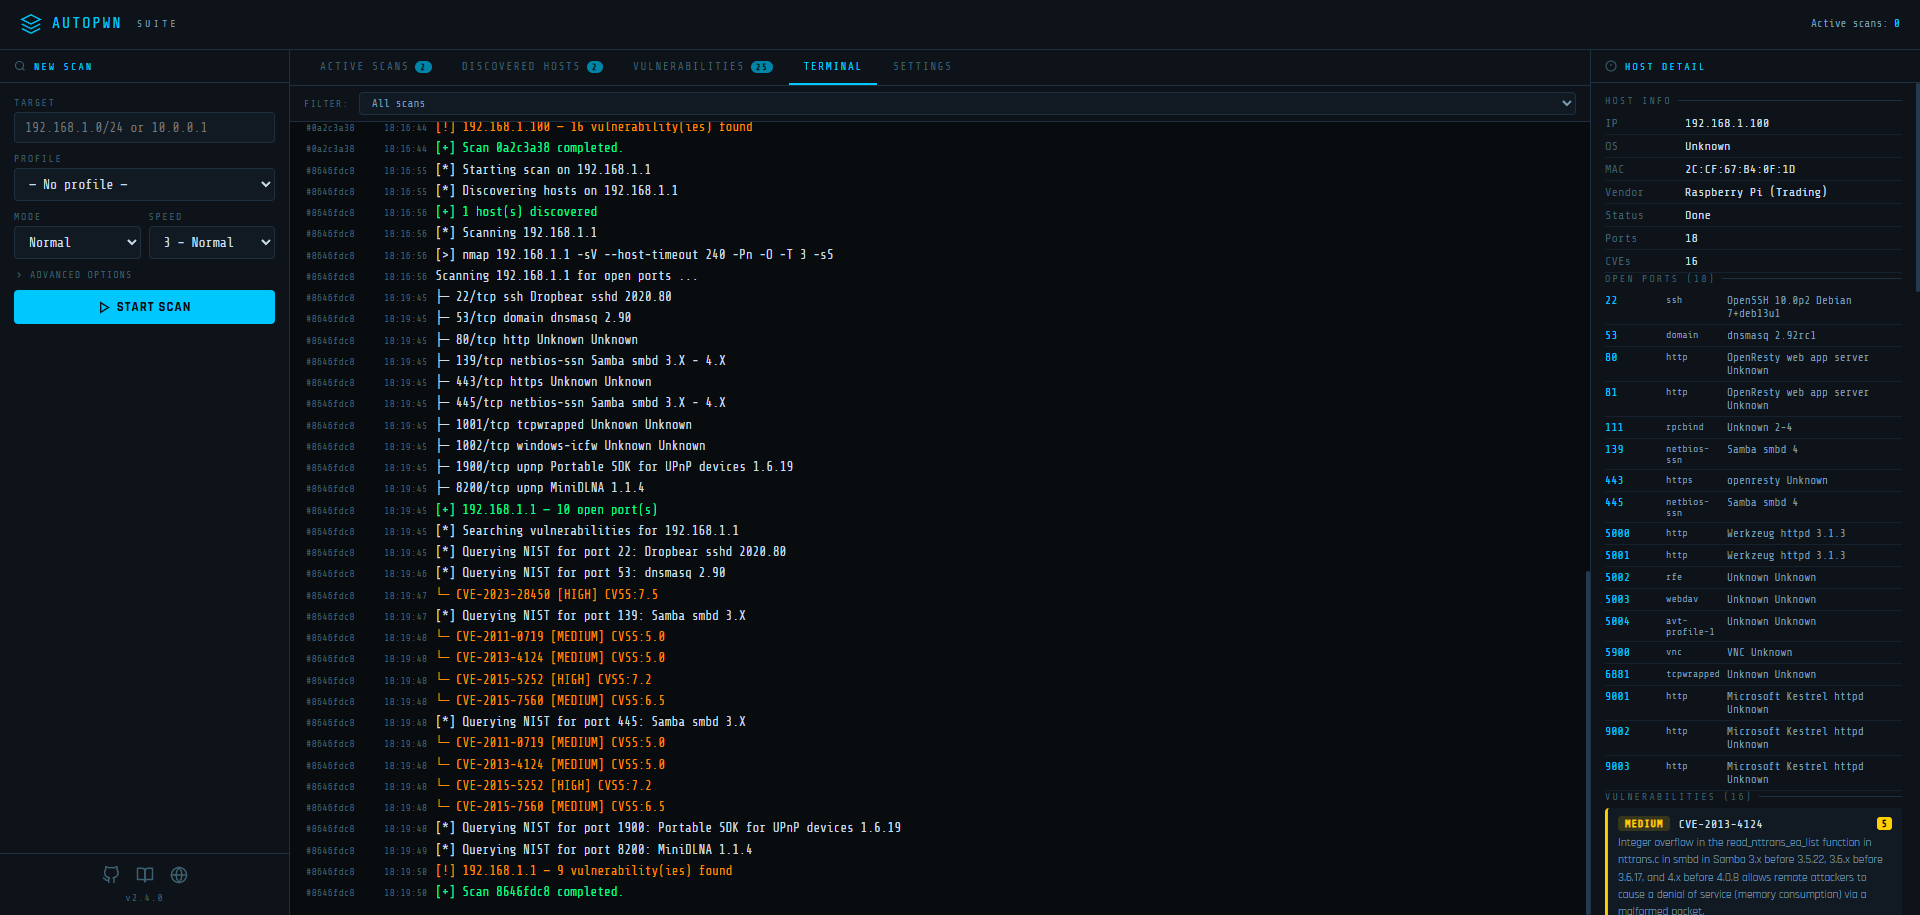 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 musalbas/heartbleed-masstest
Multi-threaded tool for scanning many hosts for CVE-2014-0160.
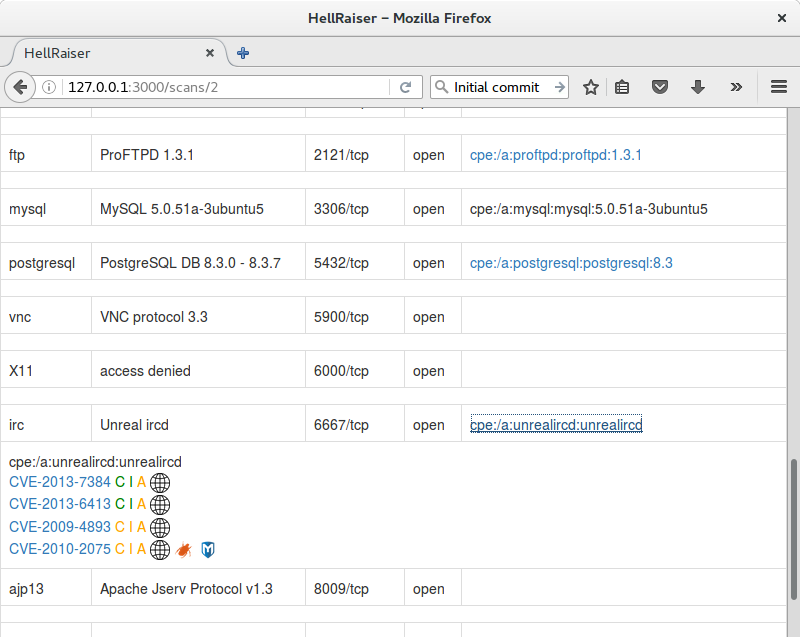 m0nad/hellraiser
Vulnerability scanner using Nmap for scanning and correlating found CPEs with CVEs.
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
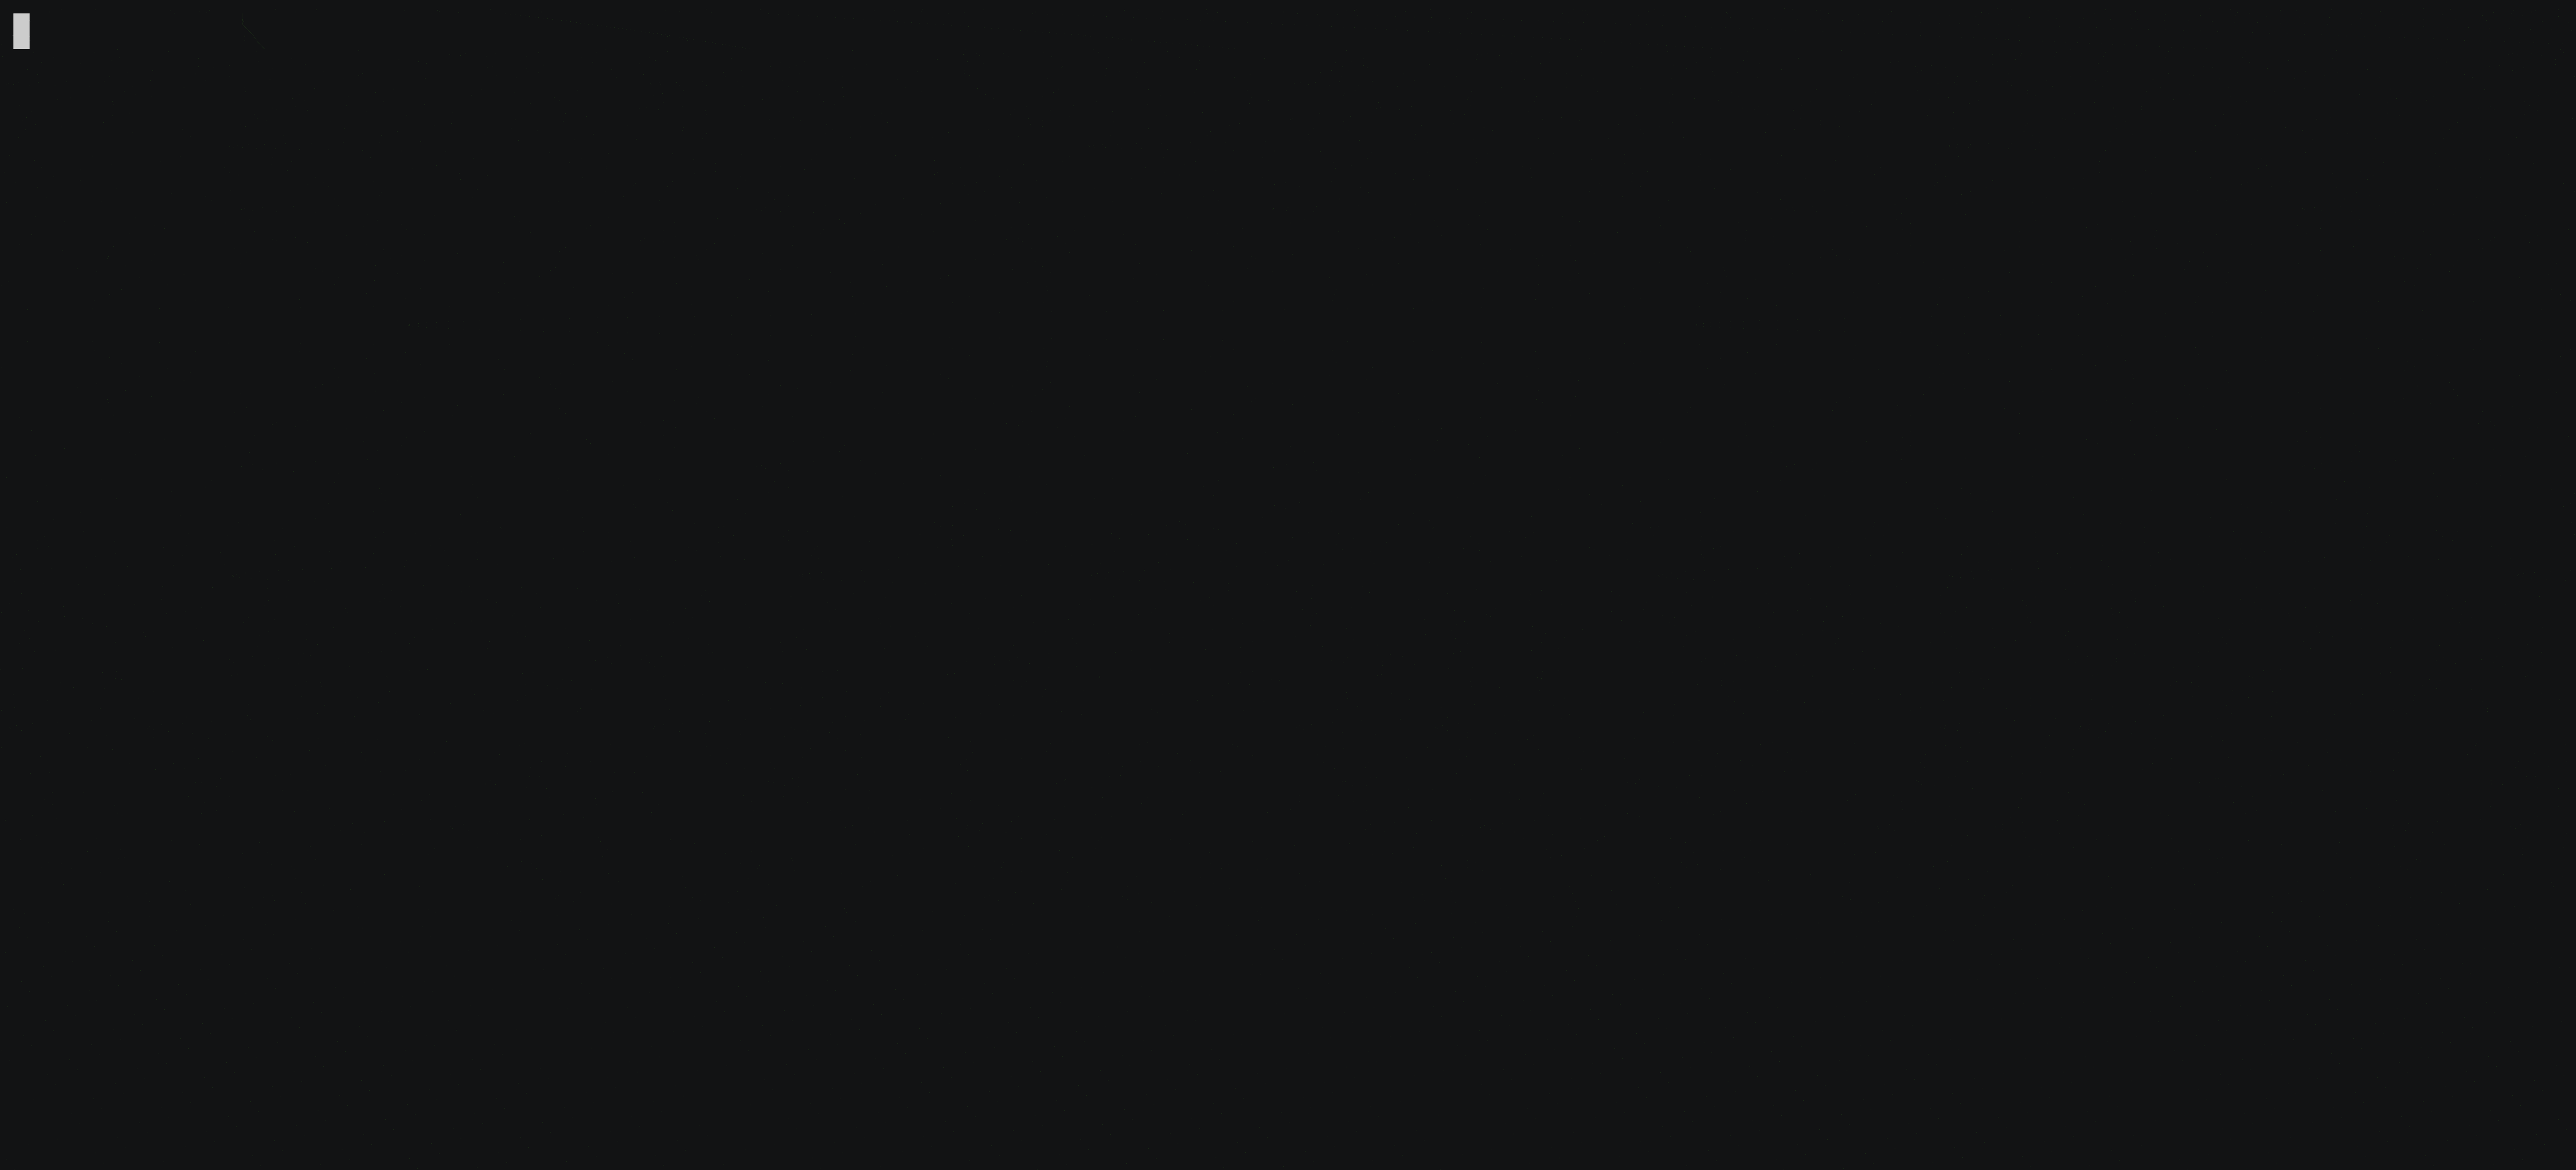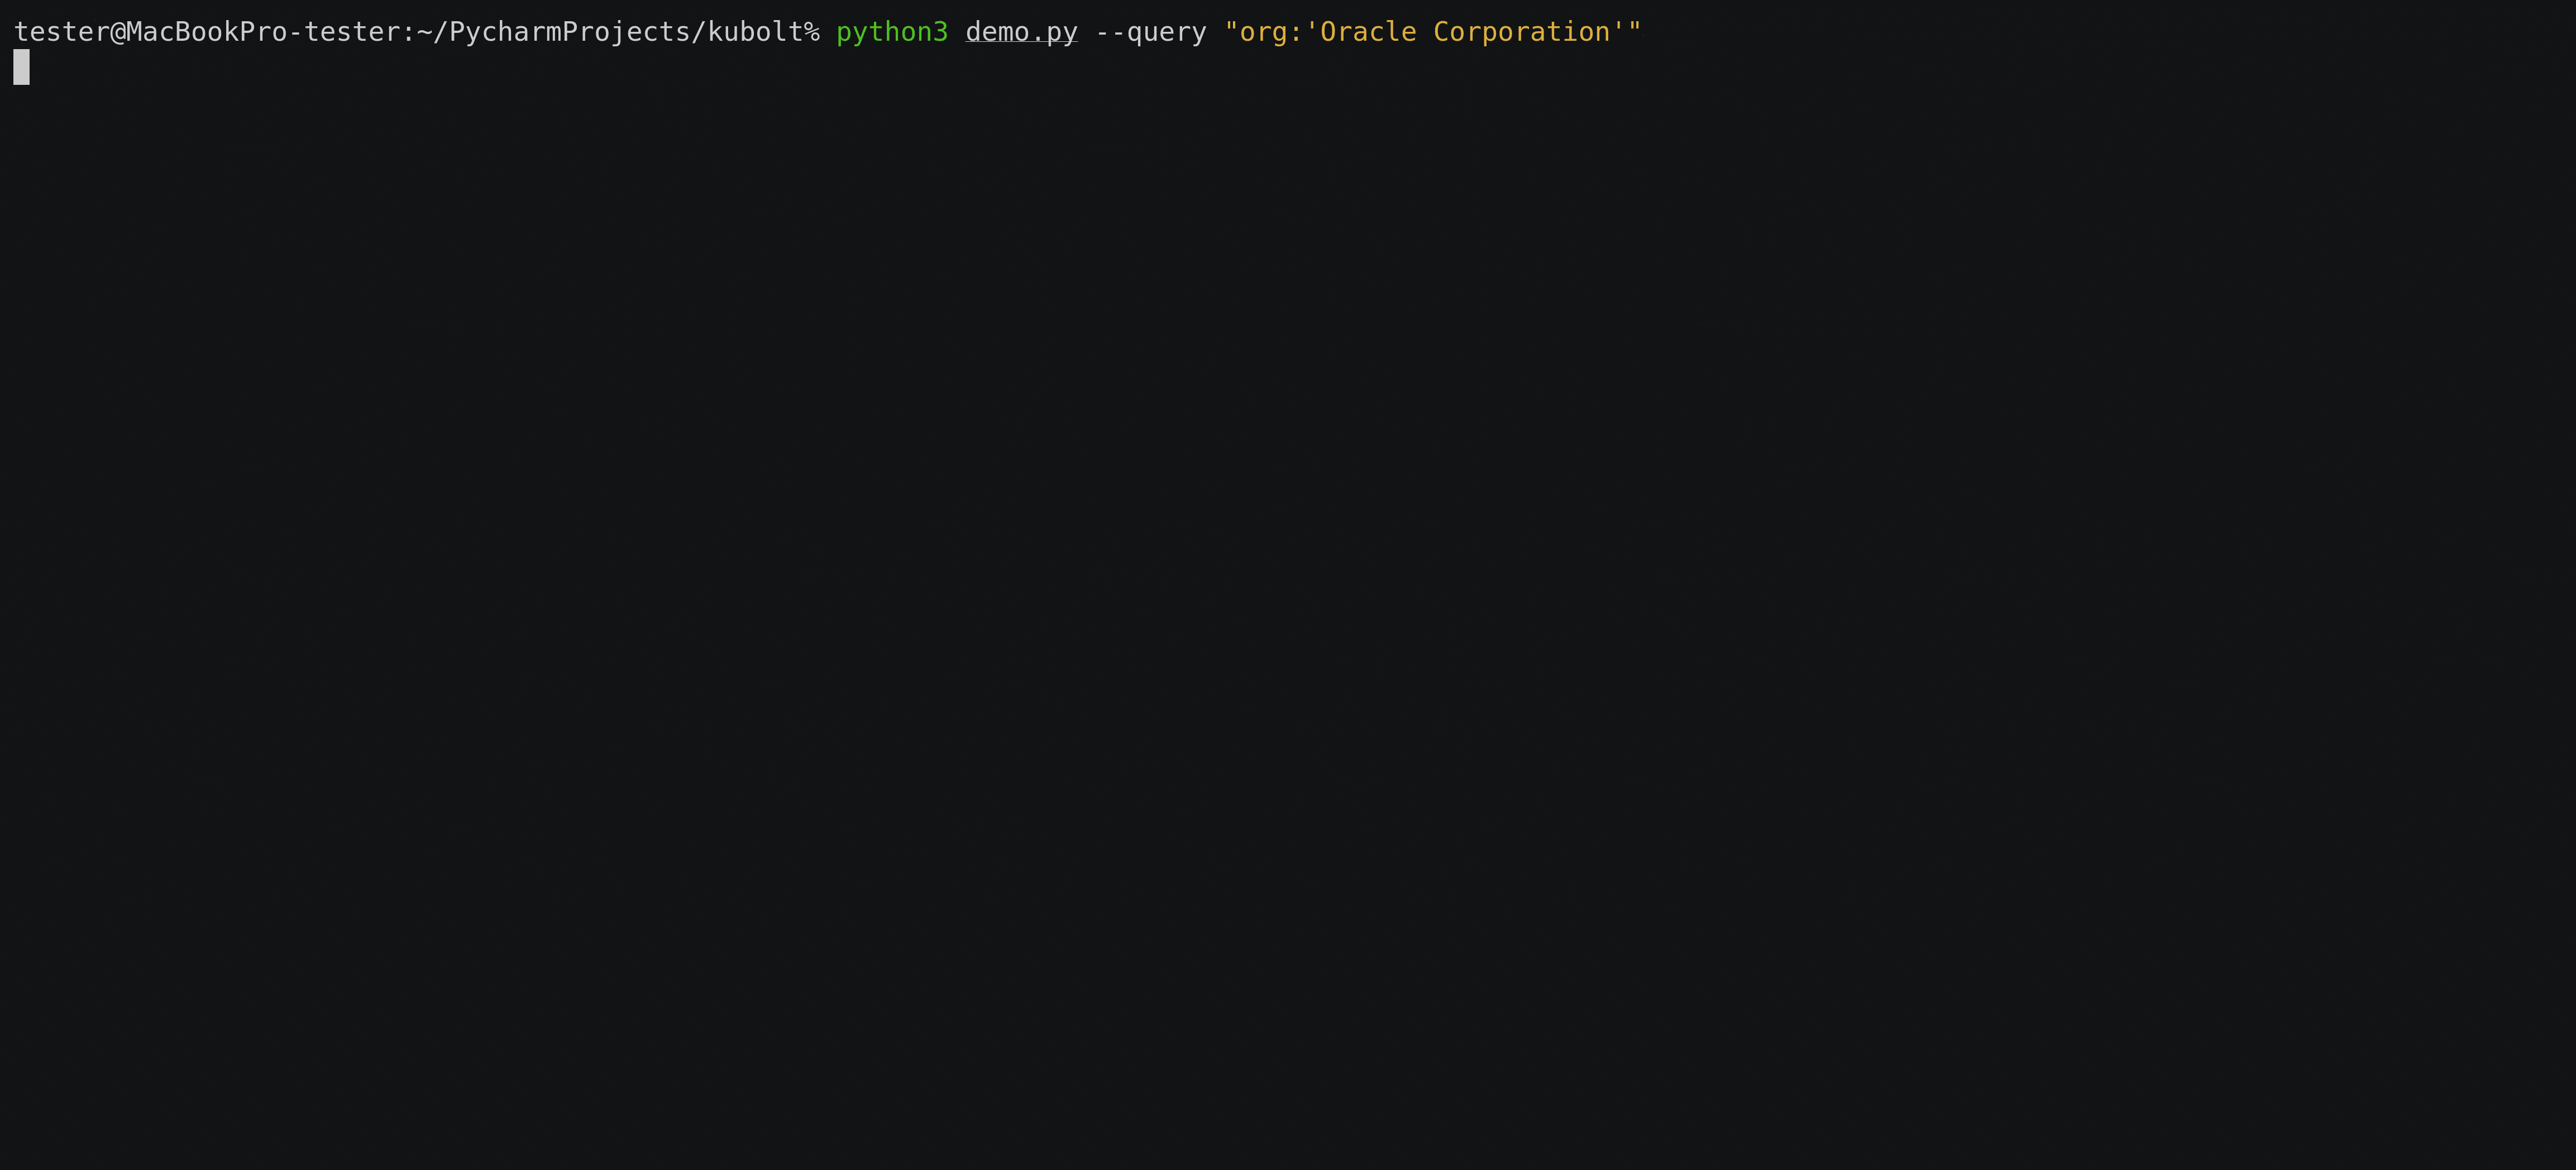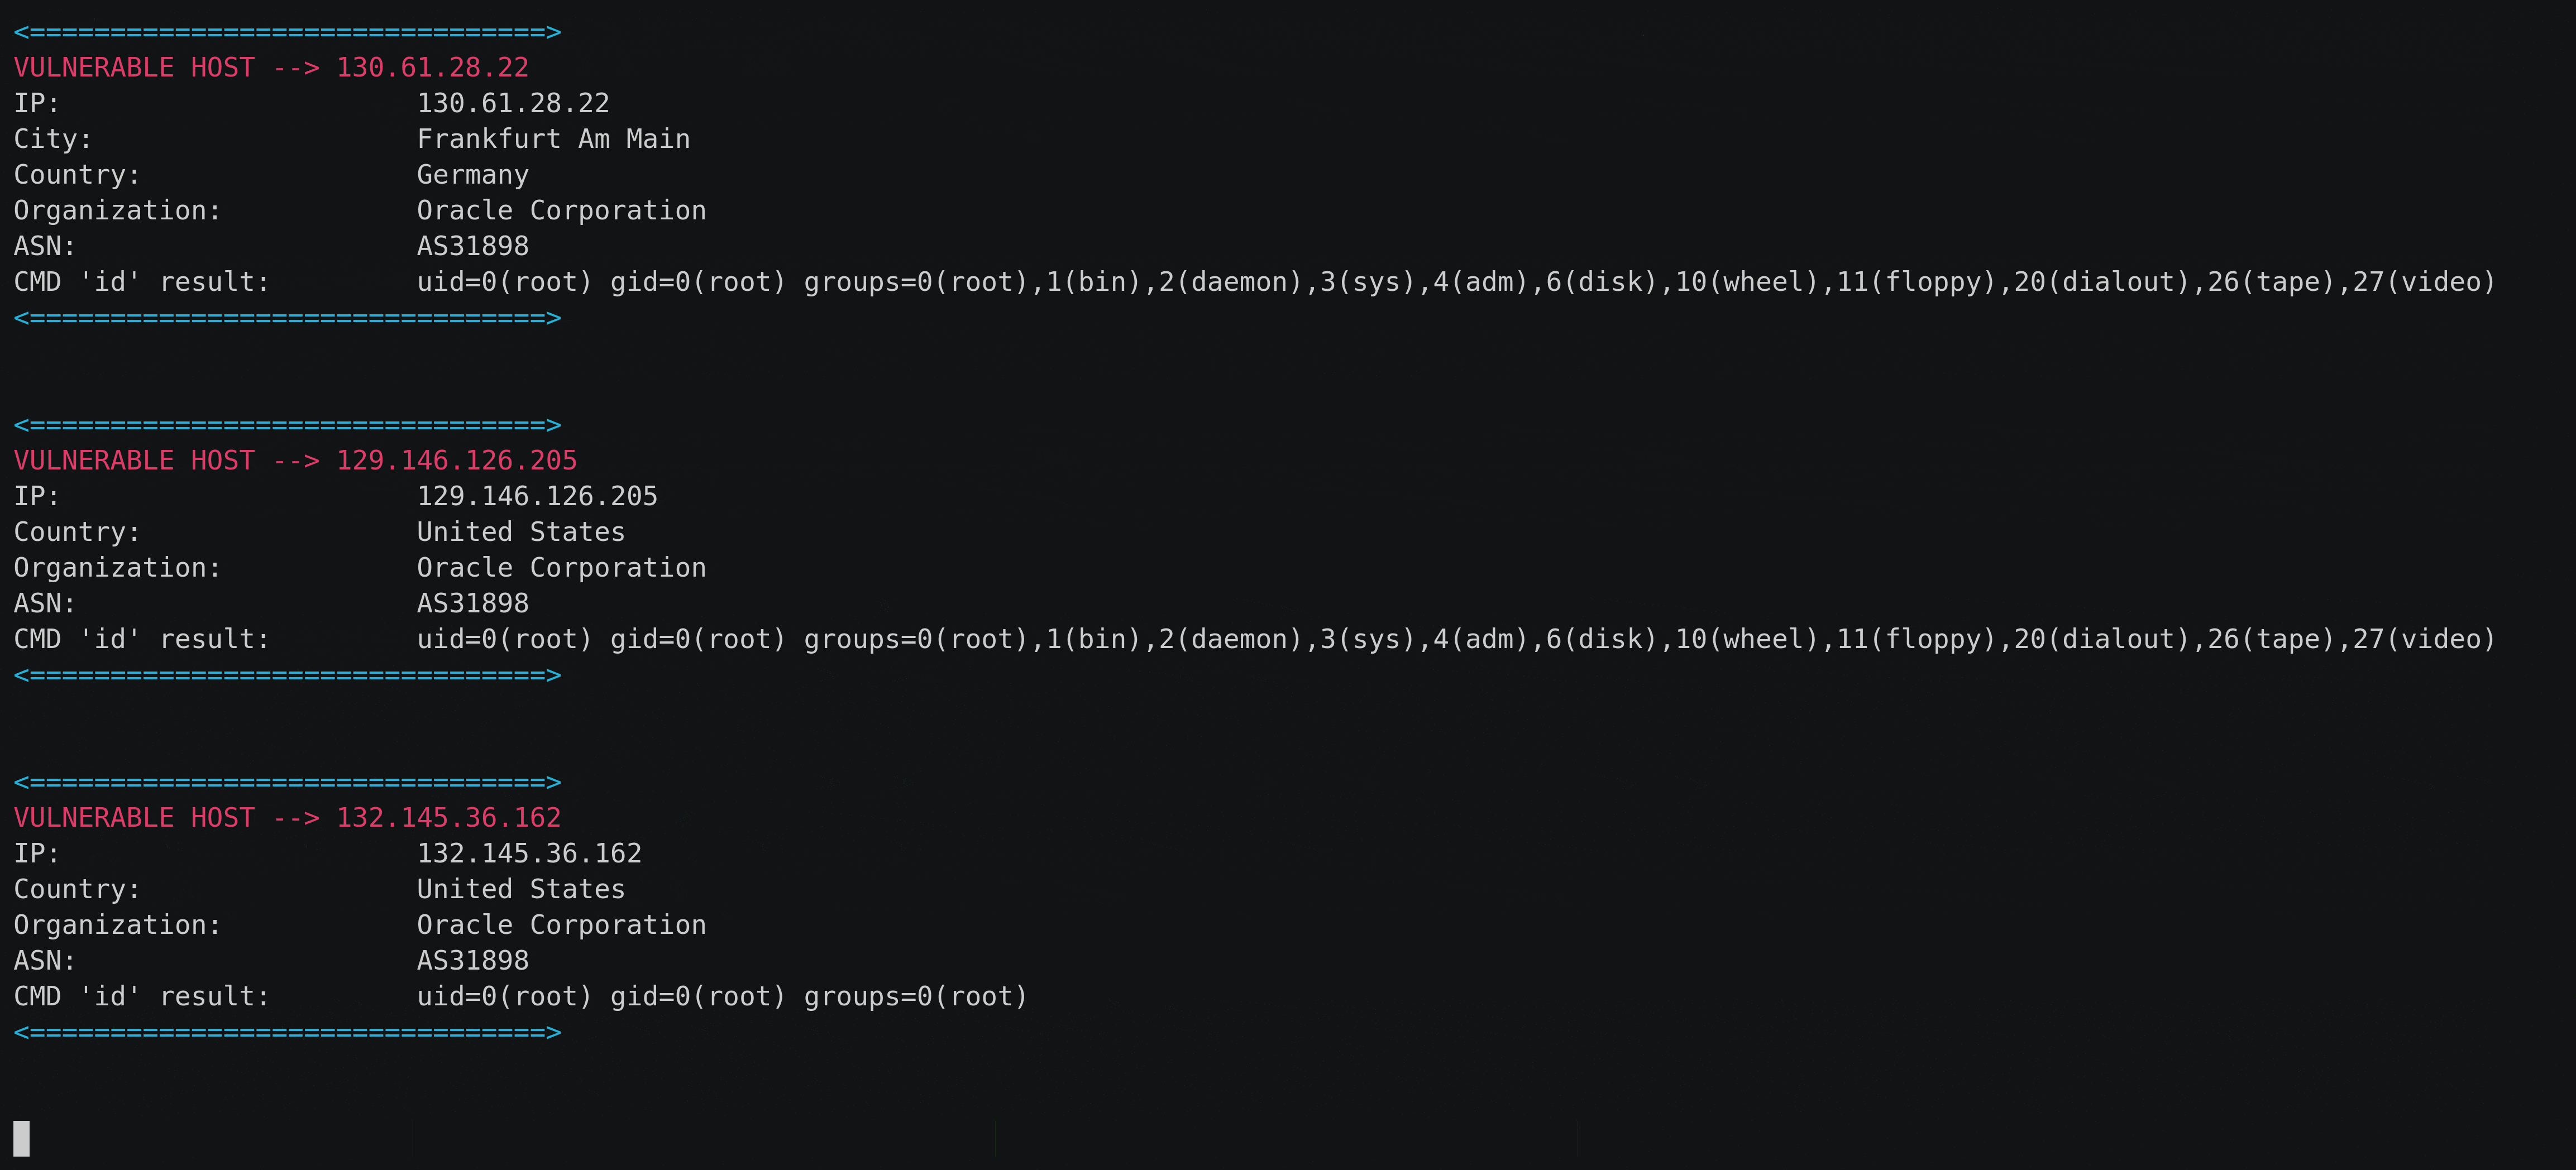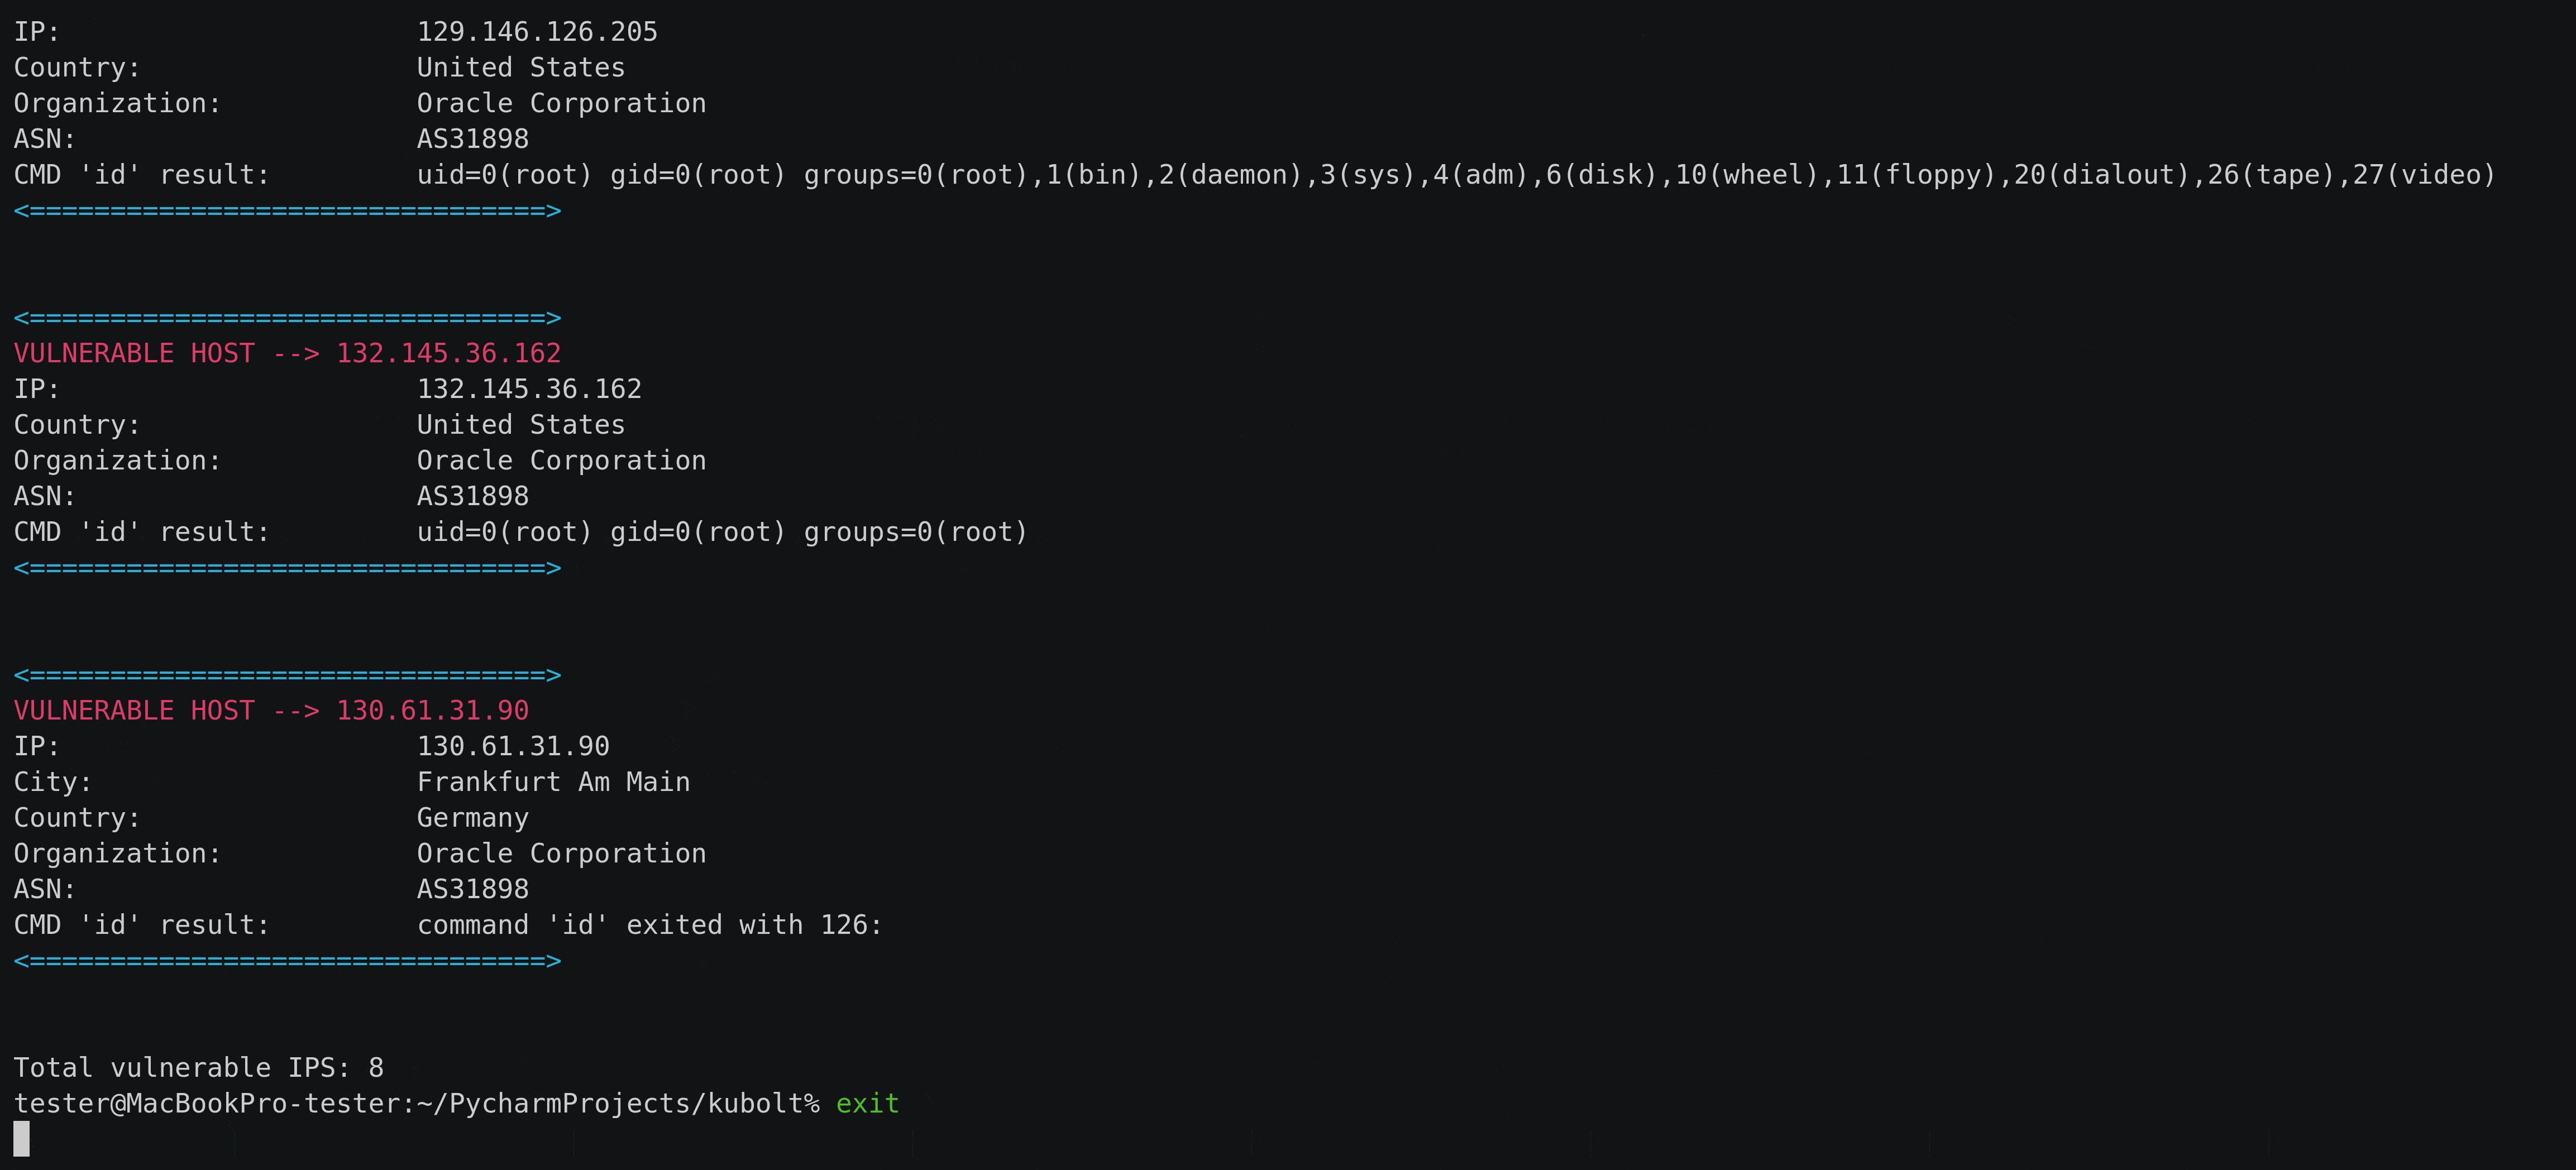 averonesis/kubolt
Kubolt utility for scanning public kubernetes clusters
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 ruppde/rdg_scanner_cve-2020-0609
Scanning for Remote Desktop Gateways (Potentially unpatched CVE-2020-0609 and CVE-2020-0610)
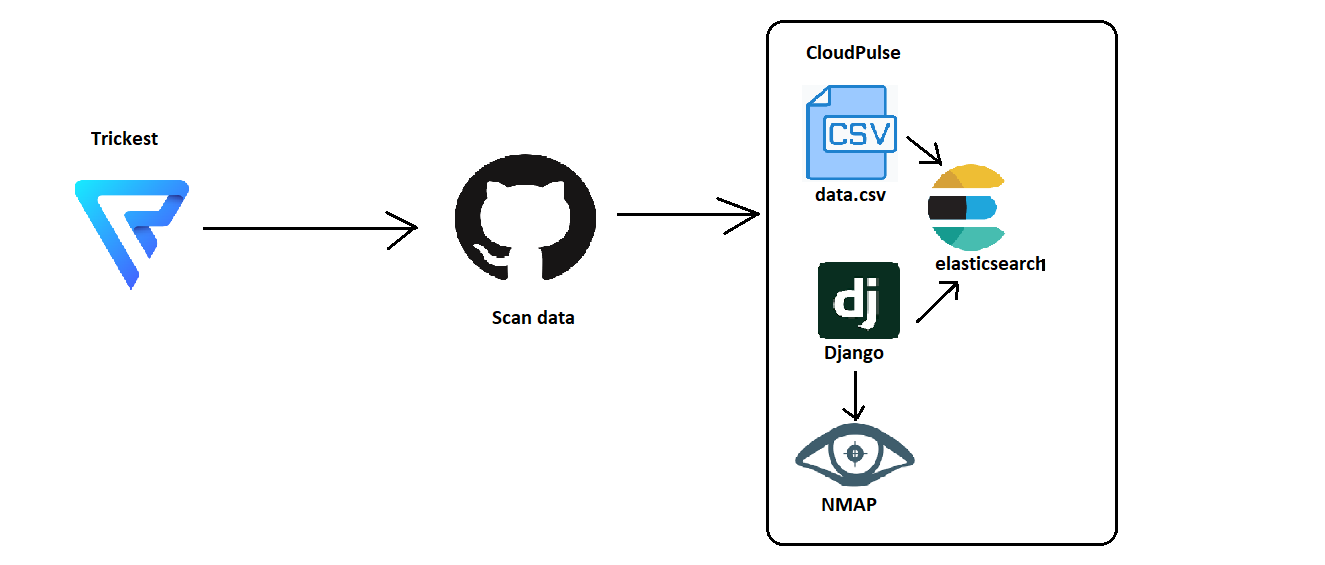 yousseflahouifi/cloudpulse
SSL certificate-based reconnaissance engine for discovering AWS cloud assets, including IPs, subdomains, and domains, with active port scanning for…
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 mithridates1313/proxyshell_poc
POC for scanning ProxyShell(CVE-2021-34523,CVE-2021-34473,CVE-2021-31207)
 dickens88/cve-2020-0796-scanner
This project is used for scanning cve-2020-0796 SMB vulnerability