
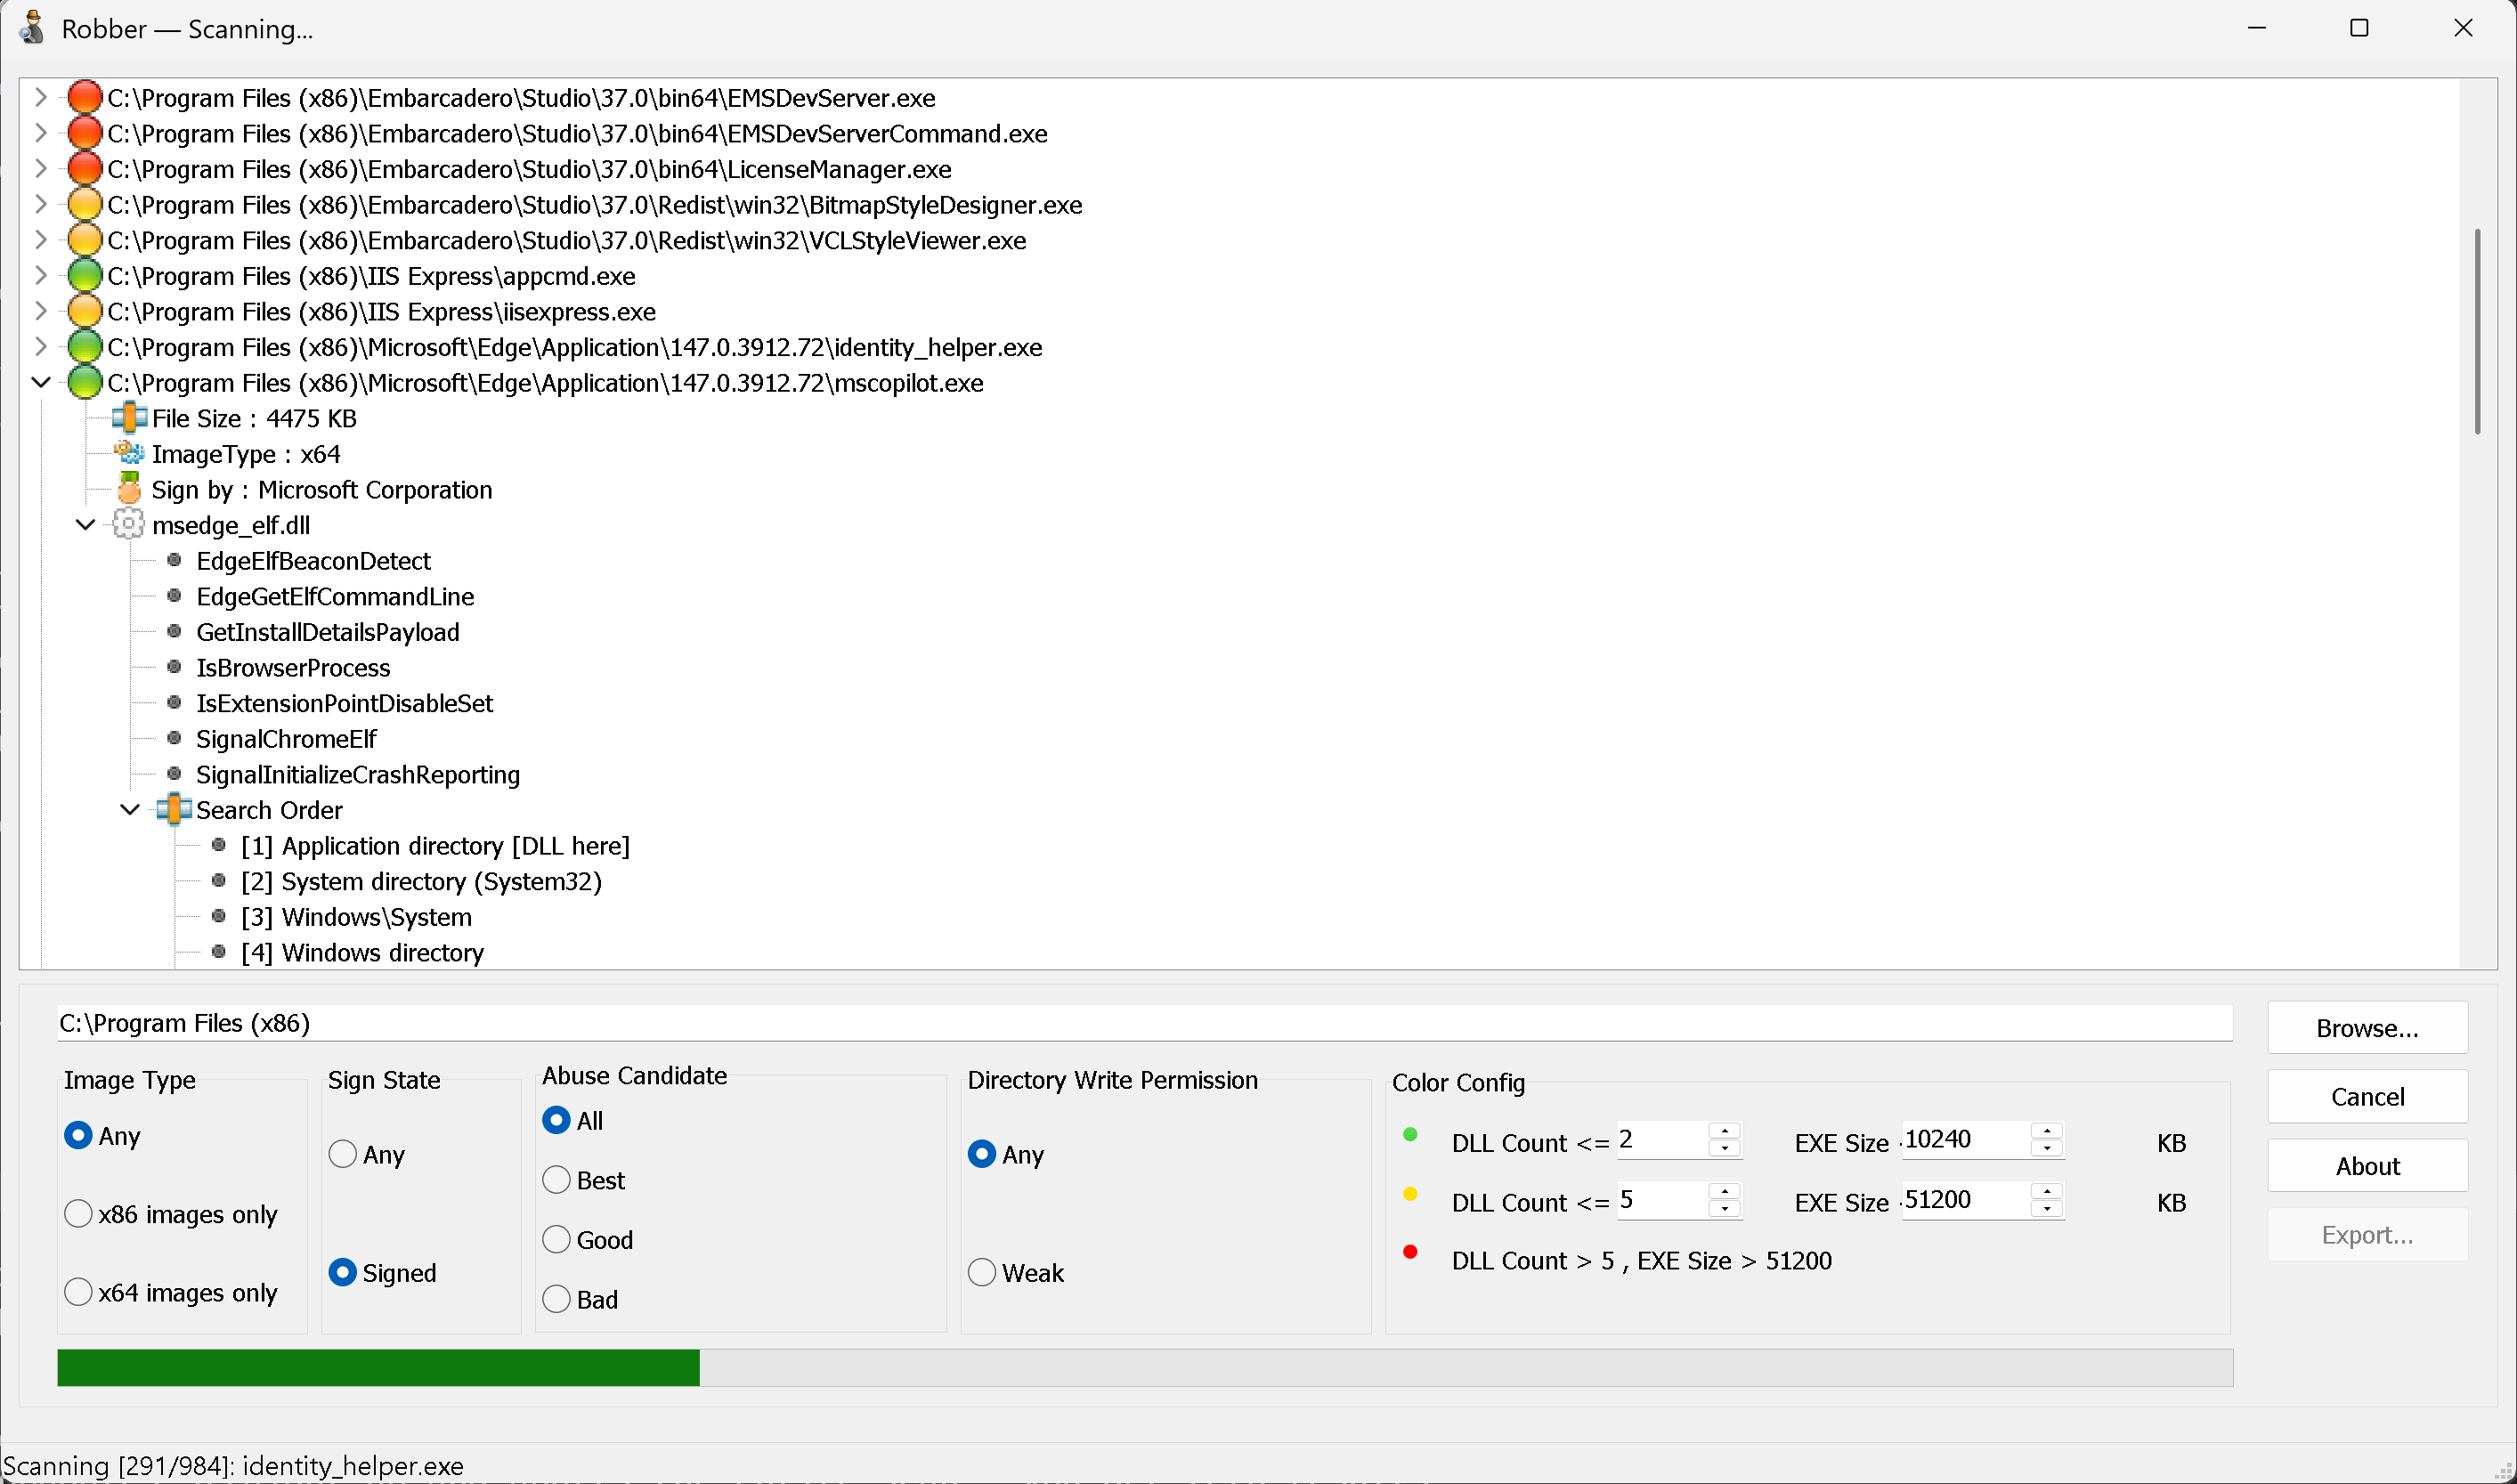
Robber
 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
binary-analysisprivilege-escalationvulnerability-analysis+1
8006 months ago
mojtabatajik/robberRobber is open source tool for finding executables prone to DLL hijacking
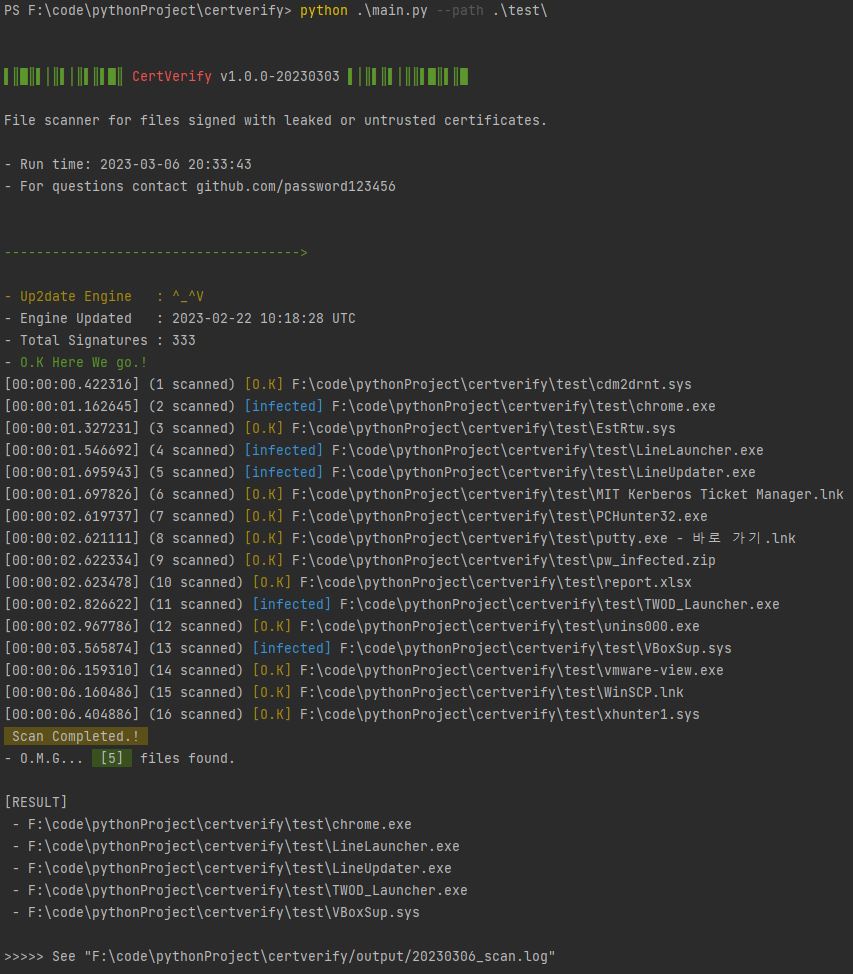 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
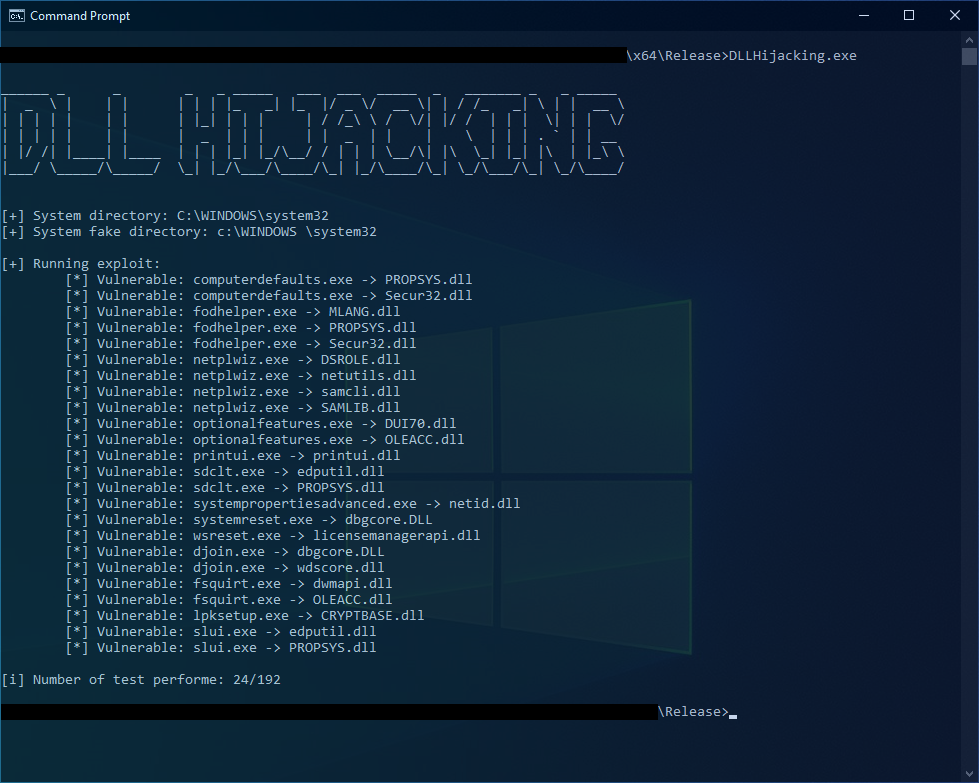 secuproject/dllhijackingscanner
This is a PoC for bypassing UAC using DLL hijacking and abusing the "Trusted Directories" verification.
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…