
broadcom-wps
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
embedded-systems-securityfirmware-analysishardware-iot-security+7
308
qkaiser/broadcom-wpsTools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 lukr54/edk2-security
EDK2 BrotliCustomDecompressLib security findings — coordinated disclosure
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 khaleedbt/netis-cve-2026-36539
Python script that checks Netis routers for CVE-2026-36539, detecting vulnerable devices on a network.
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
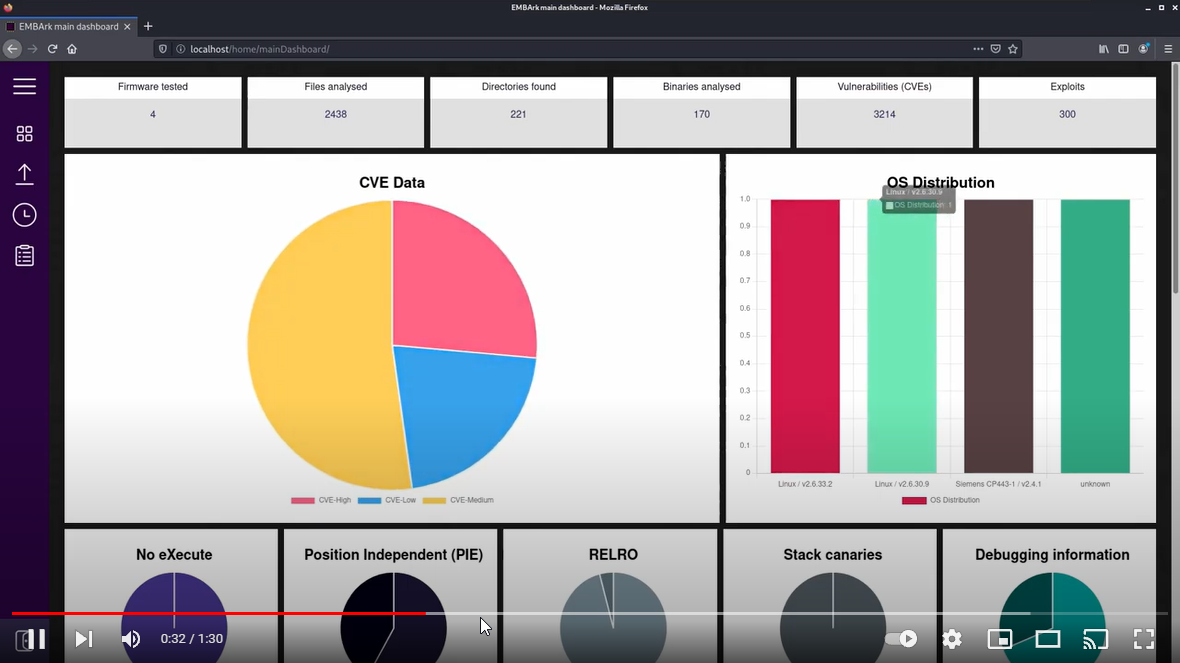 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 gigachadusers/cve-2026-20169
Windows-native IoT vulnerability scanner that discovers exposed management interfaces, tests default credentials, and validates network segmentation…
 ransc0rp1on/ripple20
This comprehensive package contains everything needed to detect, analyze, and remediate Ripple20 (CVE-2020-11898) vulnerabilities in your…
 hmrumman777-beep/netaudit-iot
Research-driven UPnP vulnerability scanner focusing on libupnp 1.6.19 and CVE-2012-5958.
 misakamikato/cve-2017-7921-golang
Hikvision IP camera access bypass exploit, developed by golang.
 killsystema/scan-cve-2026-24061
Scans for CVE-2026-24061 telnetd auth bypass, generating payloads and verifying root access on vulnerable GNU inetutils telnetd devices.
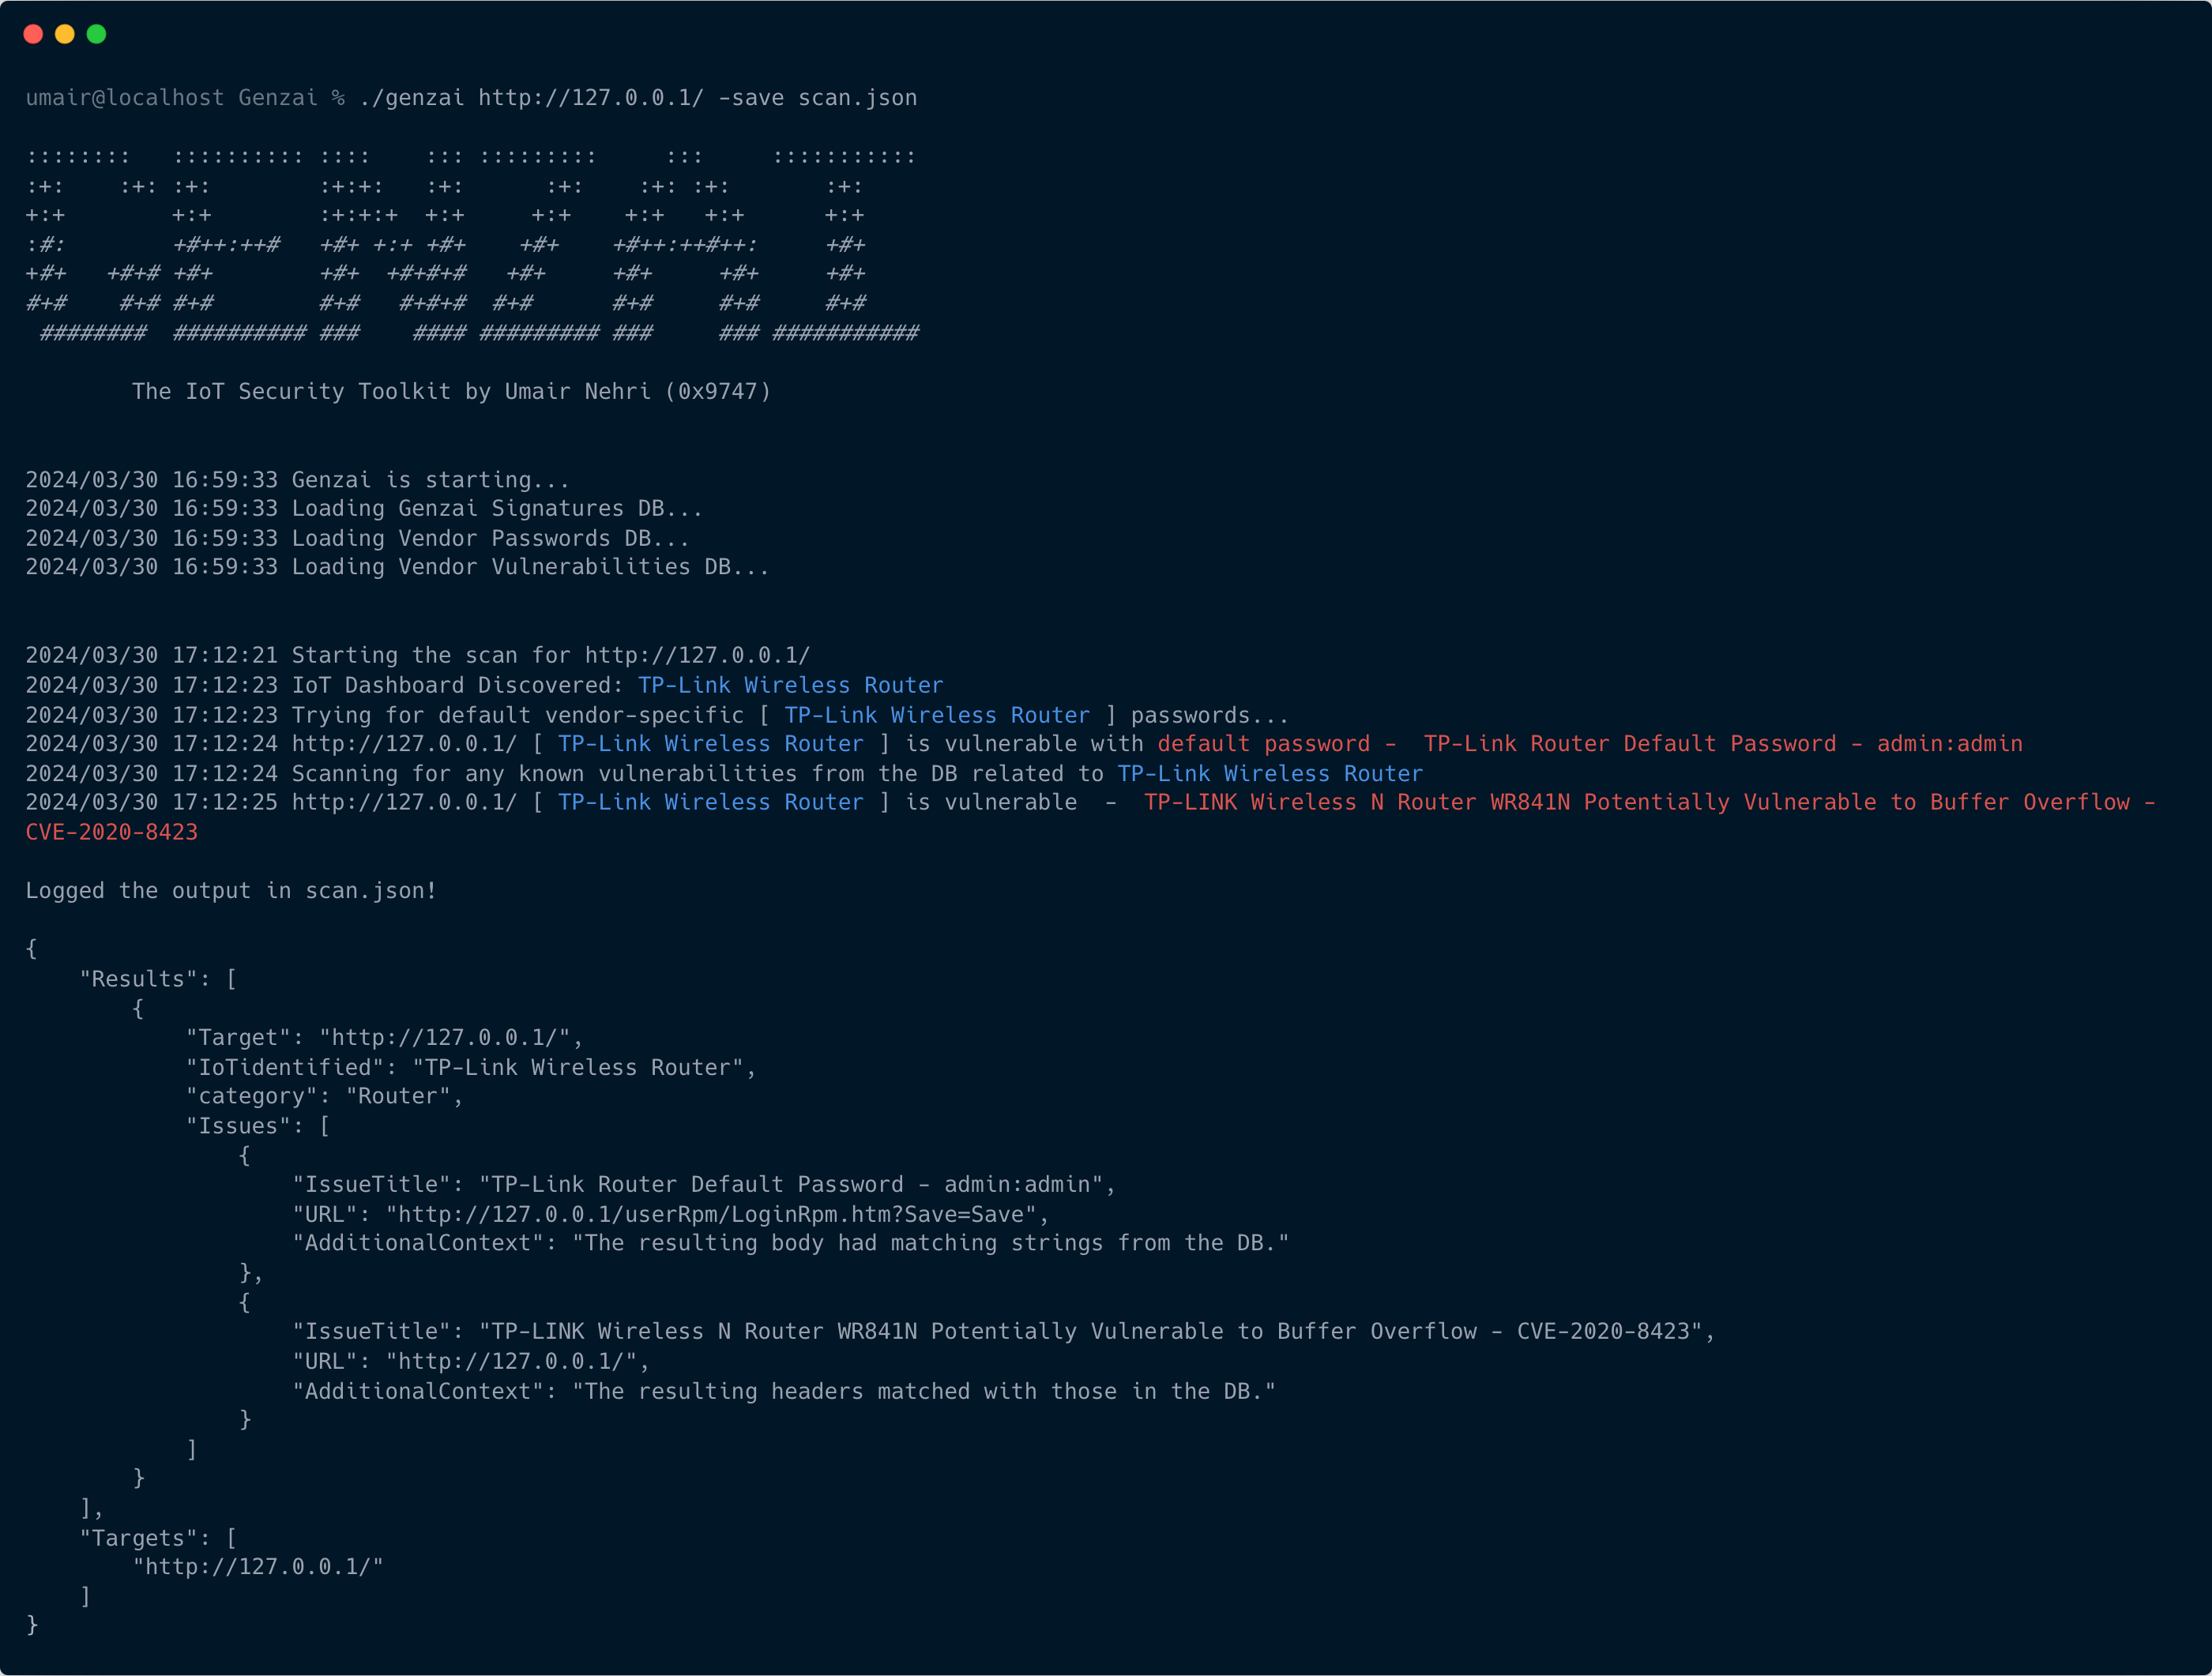 umair9747/genzai
The IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
 binarly-io/fwhunt
The Binarly Firmware Hunt (FwHunt) rule format was designed to scan for known vulnerabilities in UEFI firmware.
 bahaabdelwahed/st
IoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…