

scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
1865 days ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 prasad-1808/tool-29489
This Tool is used to check for CVE-2023-29489 Vulnerability in the provided URL with the set of payloads available
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
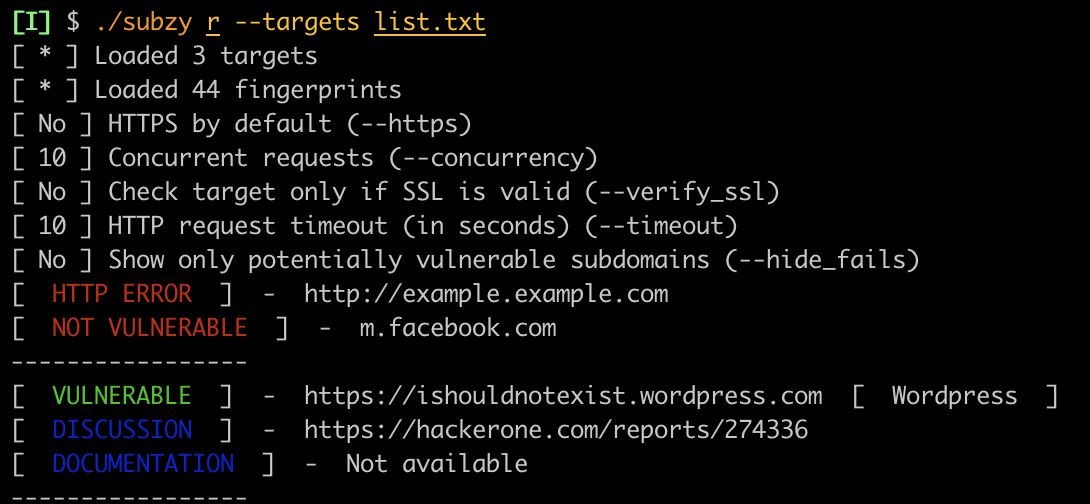 pentestpad/subzy
Subdomain takeover vulnerability checker
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
 sardine-web/cve-2024-6387_check
A security regression (CVE-2006-5051) was discovered in OpenSSH's server (sshd). There is a race condition which can lead to sshd to handle some…
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier
 soy-oreocato/cve-2022-33679_checker
Lightweight Python checker that tests Active Directory credentials for exposure to CVE-2022-33679 (Kerberos AS-REP roast without pre-authentication).…
 lixterclarixe/cve-2020-11019
In FreeRDP less than or equal to 2.0.0, when running with logger set to "WLOG_TRACE", a possible crash of application could occur due to a read of an…
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 chandru-gunasekaran/log4j-fix-cve-2021-44228
Windows Batch Scrip to Fix the log4j-issue-CVE-2021-44228
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 tripwire/openssl-ccs-inject-test
This script is designed for detection of vulnerable servers (CVE-2014-0224.) in a wide range of configurations. It attempts to negotiate using each…
 byezero/nginx-cve-2026-42945-check
Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…
 castaldio86/detect-cve-2019-19781
Detects if a server is vulnerable to CVE-2019-19781 by checking a specified IP address, providing a quick security assessment for this known…
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…