
CVE-2026-102425
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
exploitationpayload-developmentpenetration-testing+5
murrez/cve-2026-102425Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 murrez/cve-2026-101108
Python 3 PoC and mass scanner for CVE-2026-101108, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Vehicle Manager <=6.5.7…
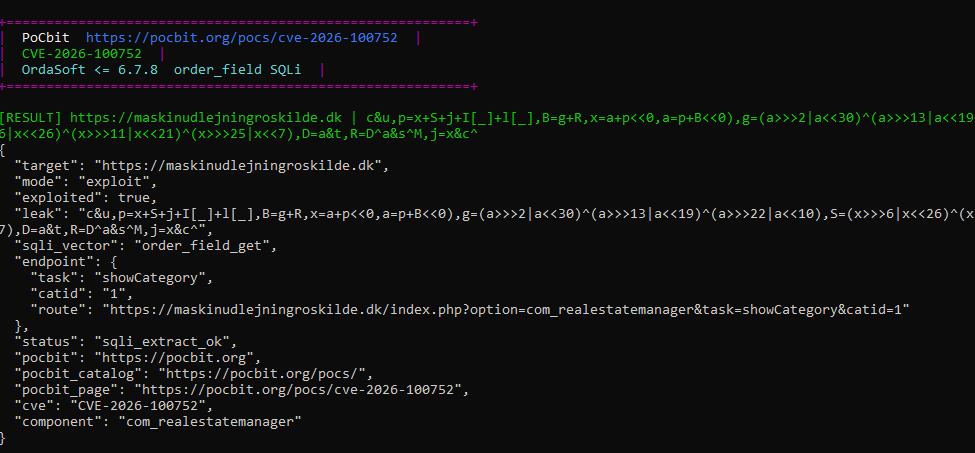 murrez/cve-2026-100752
Python 3 PoC and mass exploit for CVE-2026-100752, an unauthenticated SQL injection in OrdaSoft Joomla Real Estate Manager <=6.7.8 via the…
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
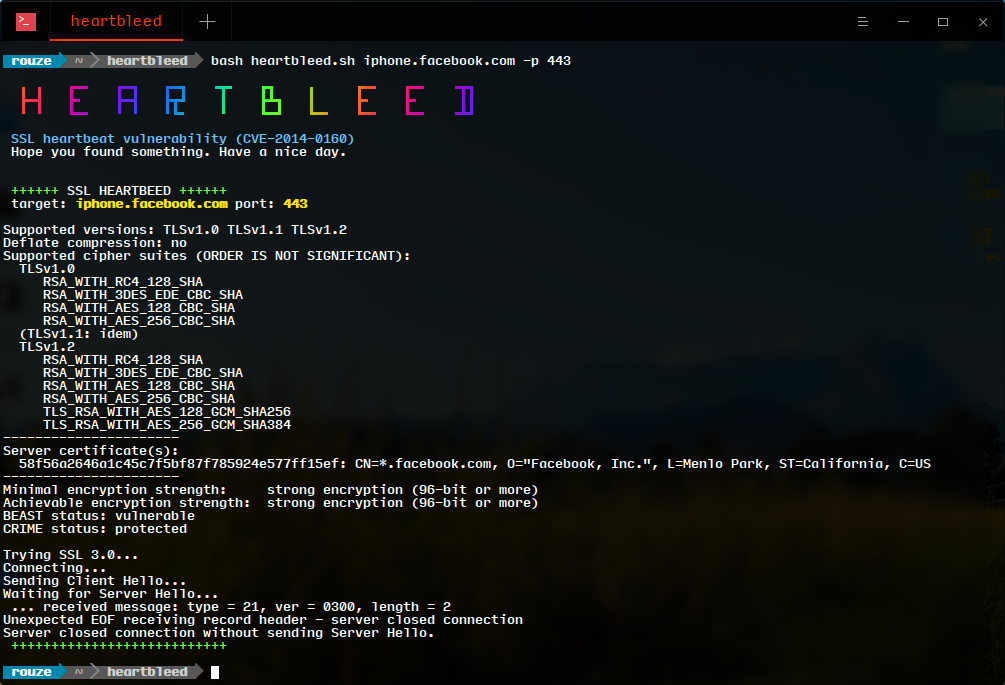 rouze-d/heartbleed
Simple OpenSSL TLS Heartbeat (CVE-2014-0160) Scanner and Exploit (Multiple SSL/TLS versions)
 rxerium/cve-2024-39929
Detection method for Exim vulnerability CVE-2024-39929
 dxc-strikeforce/burp-log4j-hammertime
Burp Active Scan extension to identify Log4j vulnerabilities CVE-2021-44228 and CVE-2021-45046
 proactiverisk/heartbleed-extention
A firefox extension and checker for CVE-2014-0160
 j0lt-github/react2shell-burp
Burp Suite extension for detecting CVE-2025-55182 (React2Shell) unsafe deserialization vulnerability. Features safe digest check, PoC redirect mode,…
 f0ng/text4shellburpscanner
Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.
 crynomore/cve-2024-34102
Burp Suite extension for detecting and testing CVE-2024-34102, a critical web vulnerability, enabling automated security assessment and exploitation…
 j0lt-github/mongobleedburp
Burp Suite extension to detect CVE-2025-14847 (MongoBleed) via manual leak tests from a dedicated UI tab.
 rootharpy/cve-2025-14172-nuclei-template
The WP Page Permalink Extension plugin (<= 1.5.4) allows authenticated users with insufficient privileges to trigger the AJAX action…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
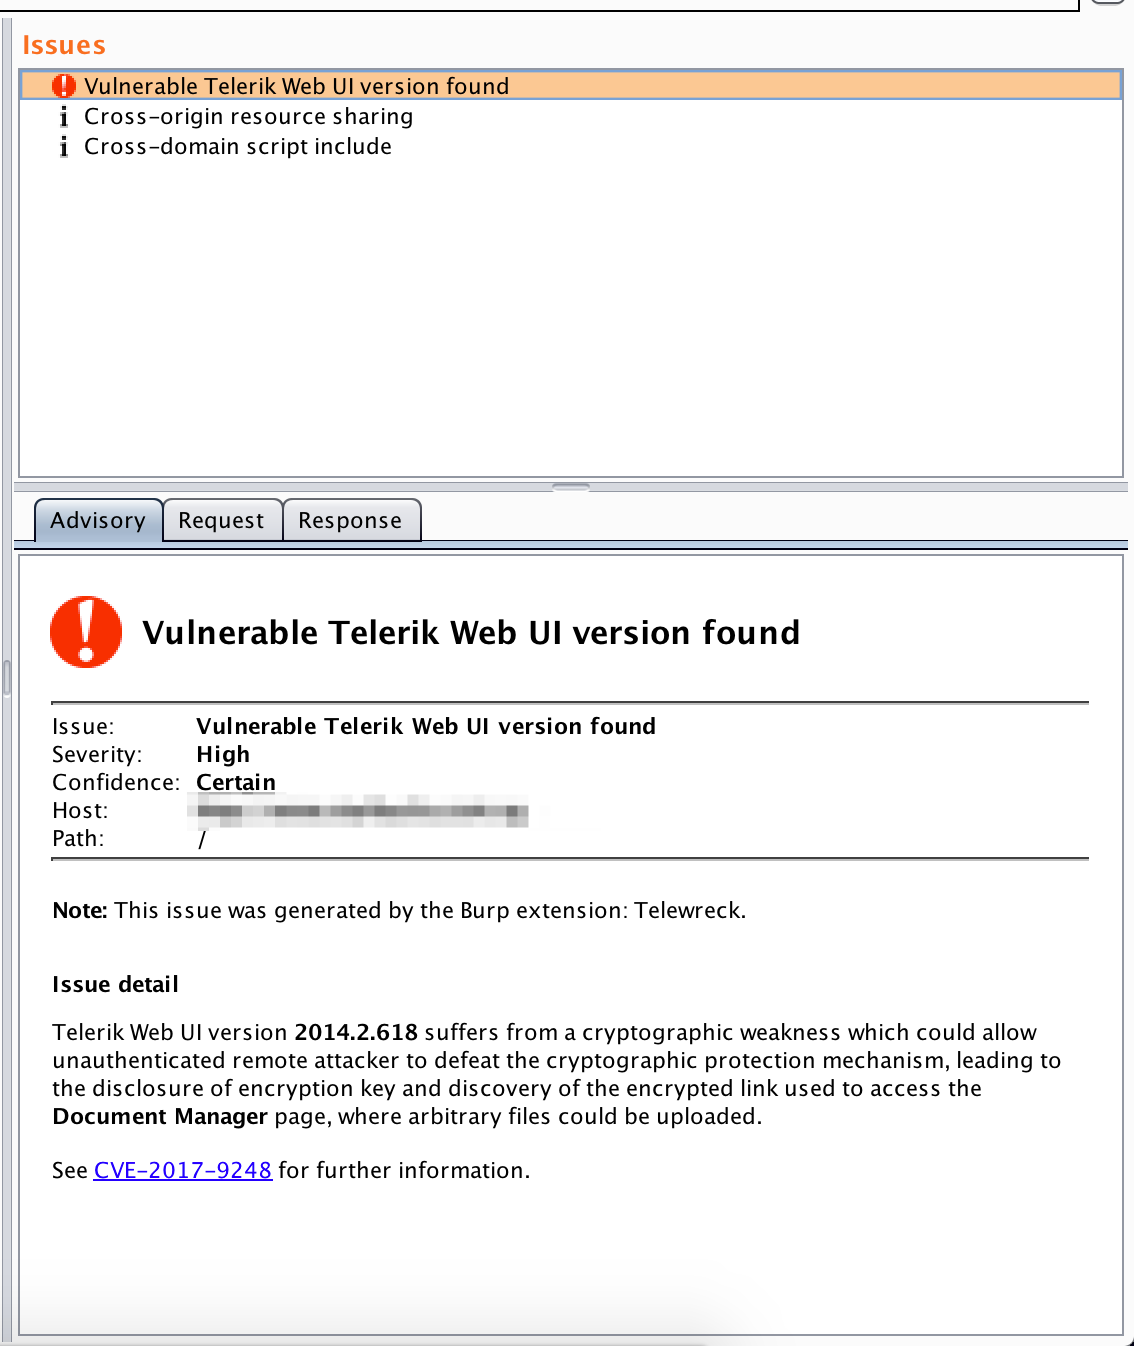 capt-meelo/telewreck
A Burp extension to detect and exploit versions of Telerik Web UI vulnerable to CVE-2017-9248.
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…