
ftw
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
142
coreruleset/ftwYAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
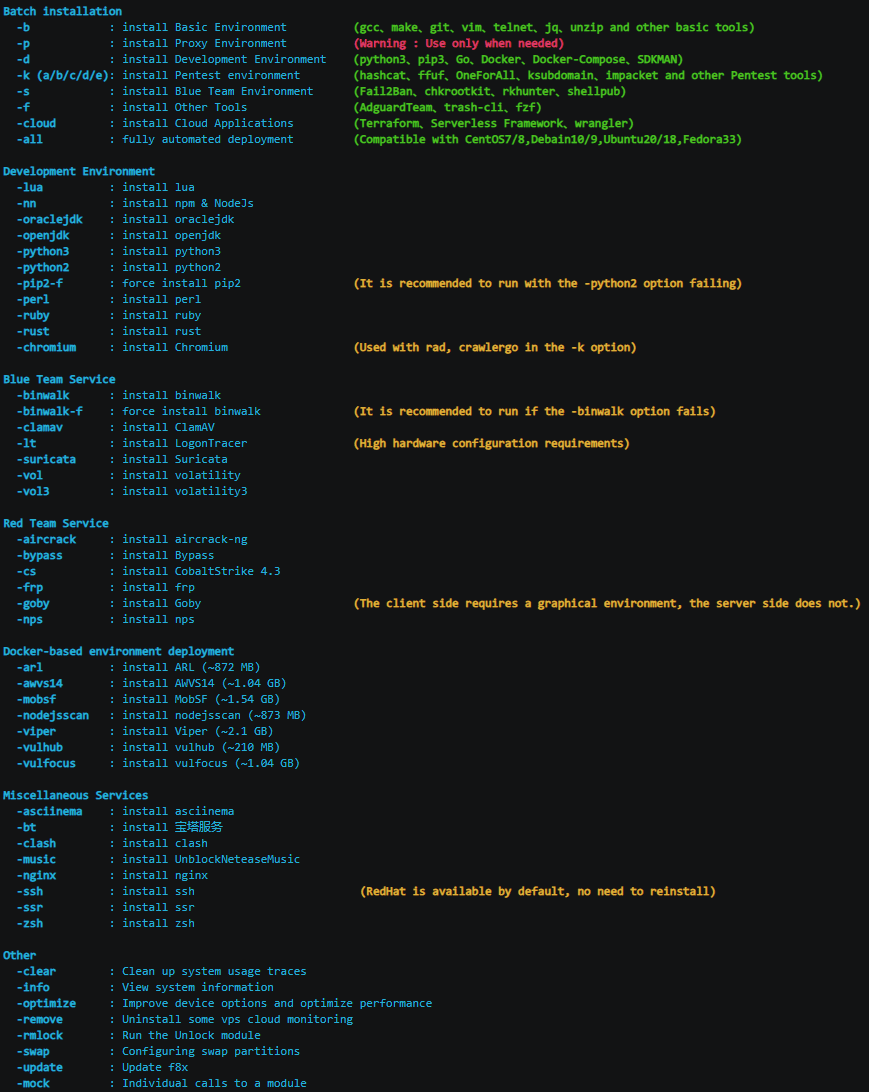 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 cream-sec/cve-2019-0708-msf--
CVE-2019-0708-Msf-验证
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
 notsosecure/blacklist3r
Audits ASP.NET applications for pre-published machine keys to detect ViewState deserialization vulnerabilities and insecure forms authentication…
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 daryllundy/cve-2025-53770
Network-based vulnerability scanner for detecting systems vulnerable to CVE-2025-53770 (unsafe deserialization). Includes PowerShell and Python…
 horkimhab/cve-2026-60121-cve-2026-61498
CVE-2026-60121, CVE-2026-61498 - Draft
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
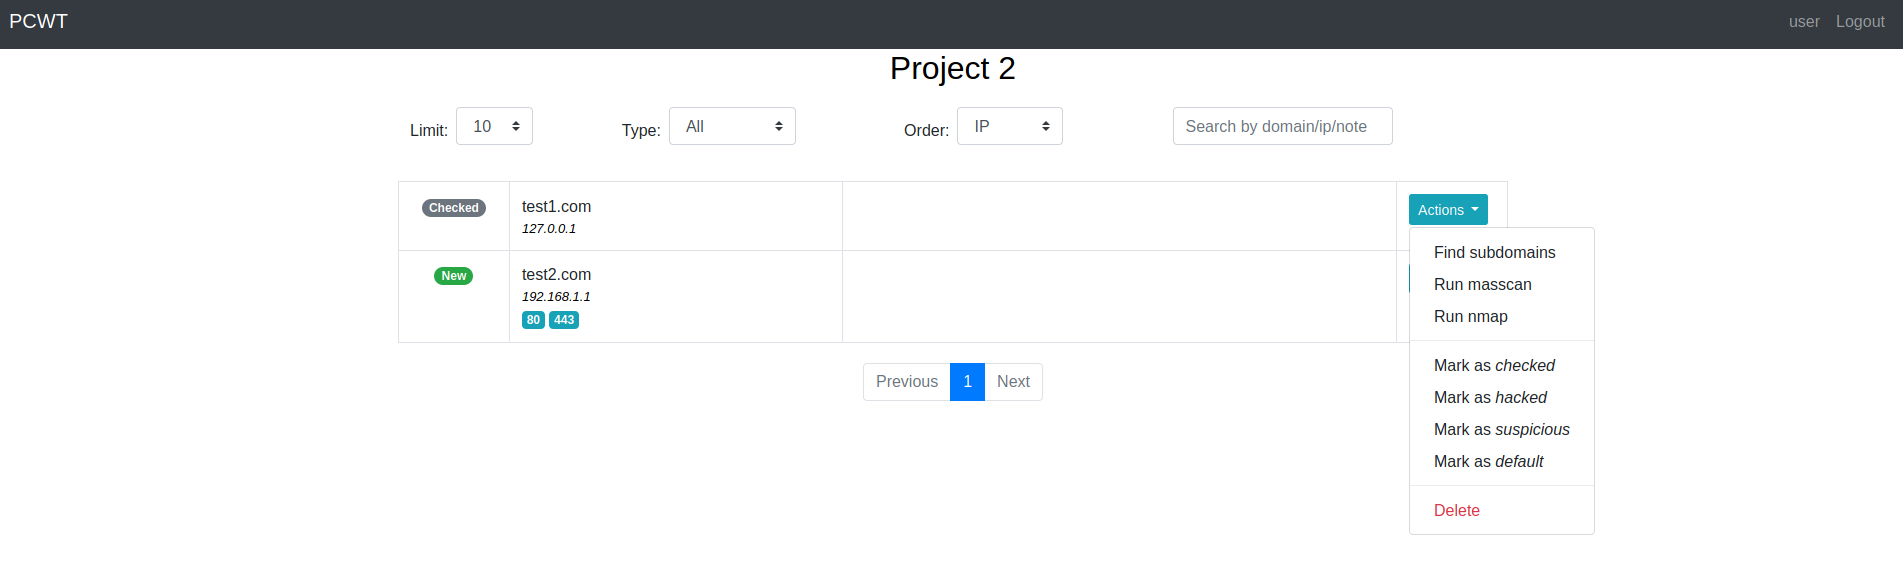 ascr0b/pcwt
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 horkimhab/cve-2026-15826-cve-2026-15748
Multithreaded Python scanner for CVE-2026-15826 and CVE-2026-15748; checks target lists, supports verbose logging, configurable threads, and custom…
 mrmtwoj/cve-2024-6387
regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…