
URL_CHECKER
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
api-security-testingeducationmachine-learning+3
1
mannansainicyber/url_checkerHybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 sn1r/mass-assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…
 impact-i/x8-burp
Hidden parameters discovery suite
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 klairmanraj/vulnerability-risk-assessment-tvra-enterprise-network
Qualitative TVRA for multi-VLAN enterprise lab scoring stored XSS and EternalBlue via CVSS v3.0 with ZAP, Nessus, and Wireshark evidence.
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 bandit92/cve2022-1388_testapi
A Test API for testing the POC against CVE-2022-1388
 prestonhashworth/cve-2025-55182
CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…
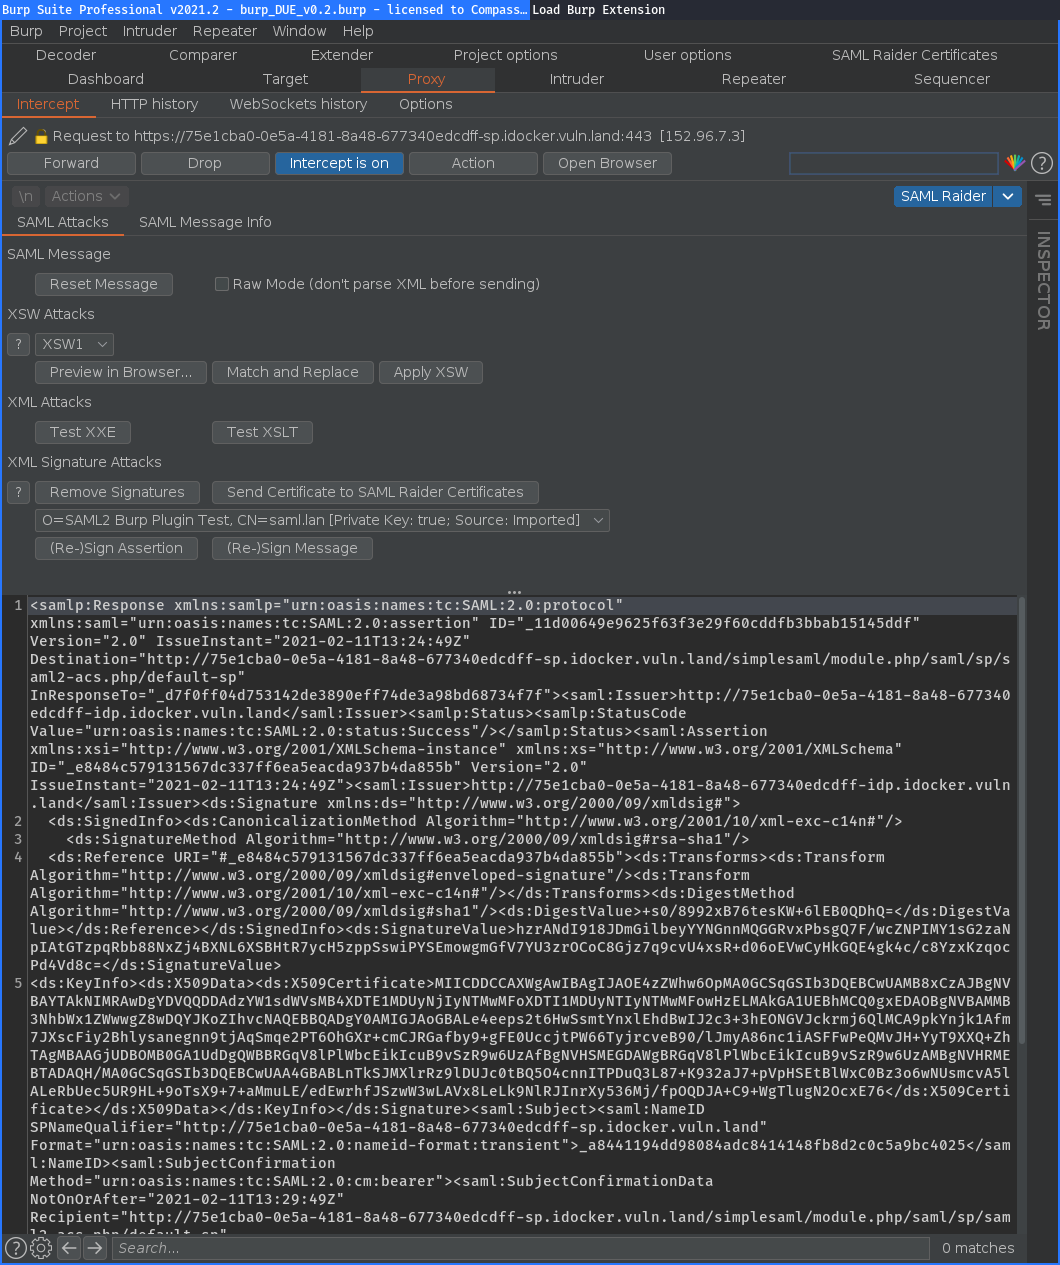 compasssecurity/samlraider
SAML2 Burp Extension
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions