flounder
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
ai-securitycode-analysisdynamic-analysis-sandboxing+5
525
adshao/flounderAutonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
 nccgroup/raccoon
Salesforce object access auditor
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 g4bri-3l3/hostbadger
Windows host hardening auditor and remediation tool in PowerShell: CIS, DISA STIG, Essential Eight checks, reversible fixes, optional AI analysis
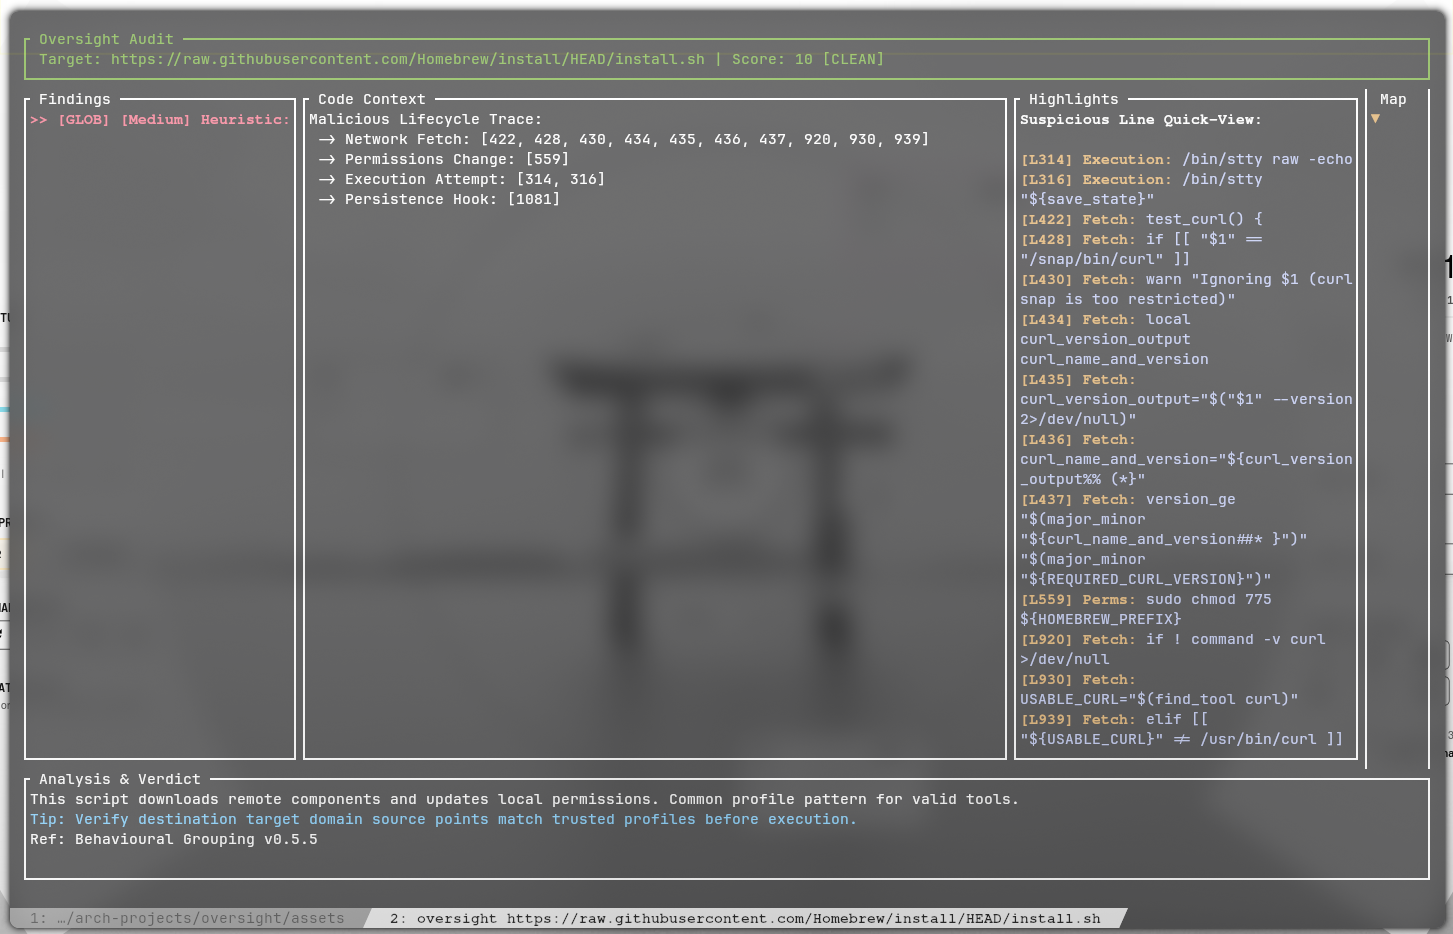 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 kabiri-labs/sshfinder
Parallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 developerfred/cve-2022-31199
Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 algosecure/pollenisator
Collaborative pentest tool with highly customizable tools