
copy-fail-cve-2026-31431
 erdemozgen/copy-fail-cve-2026-31431
Go port of the Copy Fail PoC for CVE-2026-31431, a Linux kernel authencesn flaw enabling a 4-byte write into page cache via AF_ALG and splice.…
binary-exploitationeducationexploitation+2
8
erdemozgen/copy-fail-cve-2026-31431Go port of the Copy Fail PoC for CVE-2026-31431, a Linux kernel authencesn flaw enabling a 4-byte write into page cache via AF_ALG and splice.…
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 percivalll/copy-fail-cve-2026-31431-statically-poc
Static Go proof-of-concept for CVE-2026-31431, leveraging Linux AF_ALG and splice(2) to trigger the vulnerability. Provides prebuilt binaries for…
 wanlichangchengwanlichang/cve-2024-23692-rce
Exploit for CVE-2024-23692, a remote code execution vulnerability in Rejetto HTTP File Server (HFS) 2.3 and below. Includes mass scanning with zmap…
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 arianeblow/nagiosxi-rce-all-version-cve-2021-40345
RFI to RCE Nagios/NagiosXI exploitation
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 d4rkb0n3/cve-2022-24715-go
Go-based exploit for Icinga Web 2 (CVE-2022-24715) enabling remote code execution against vulnerable instances. Port of original Python PoC.
 any3ite/cve-2023-38646-metabase-reverseshell
Go-based exploit for CVE-2023-38646 in Metabase, enabling remote code execution and reverse shell connection to an attacker-controlled host.
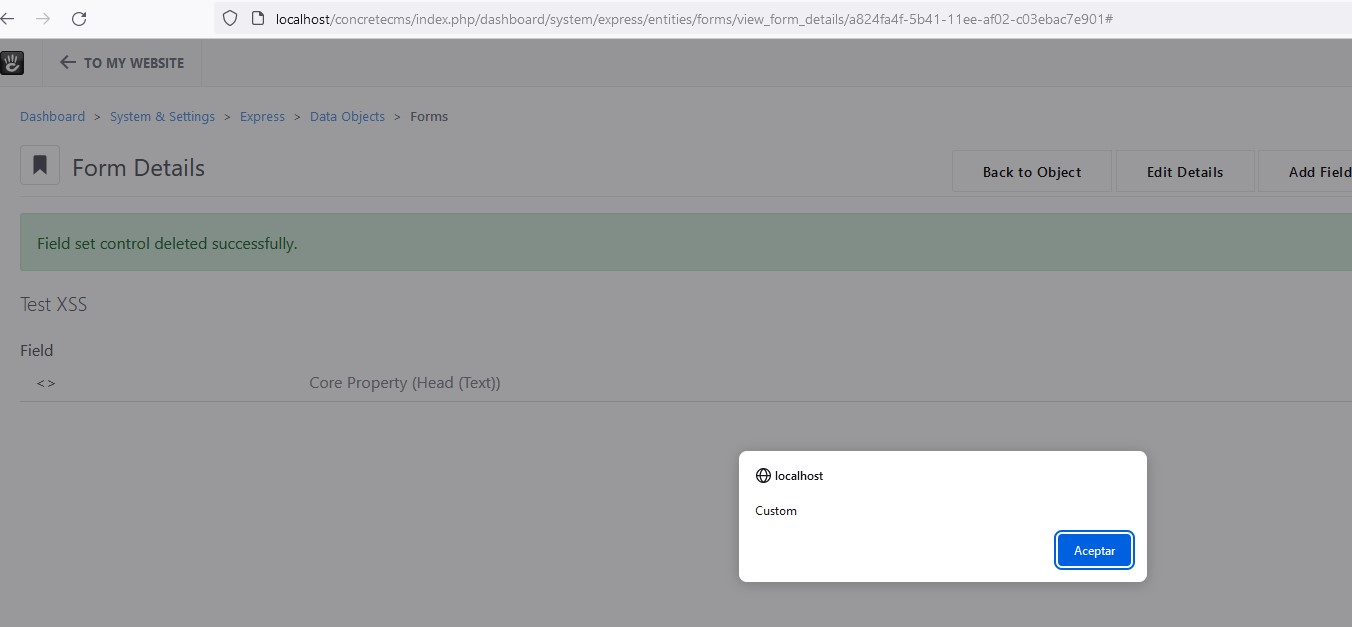 sromanhu/cve-2023-44761_concretecms-stored-xss---forms
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Form of the…
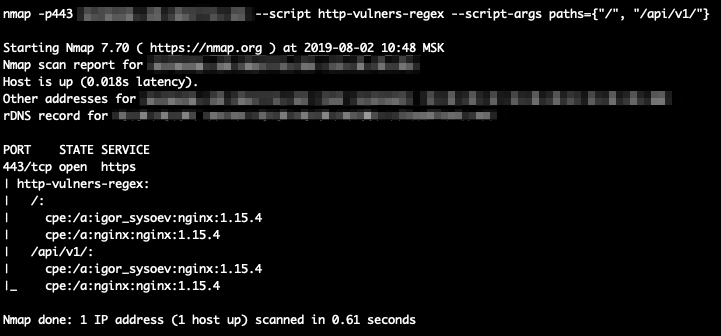 vulnerscom/nmap-vulners
Nmap NSE script that queries the Vulners API to identify known vulnerabilities (CVEs) for detected network services, enhancing standard port scanning…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 alexbakker/log4shell-tools
Tool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046
 unixpickle/cve-2018-4407
Crash macOS and iOS devices with one packet
 1337g/cve-2017-17215
CVE-2017-17215 HuaWei Router RCE (NOT TESTED)
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 oscerd/cve-2026-40564
CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…