
HUNT
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
curated-resourcespenetration-testingvulnerability-analysis+3
2.3k
bugcrowd/huntFlags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 cervantessec/cervantes
Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…
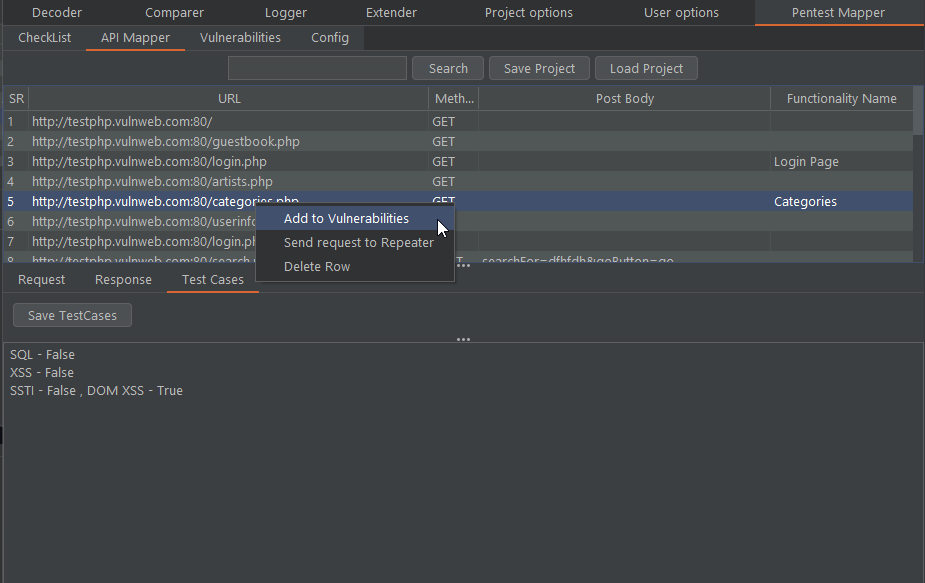 anof-cyber/pentest-mapper
A Burp Suite Extension for pentester and bug bounty hunters an to maintain checklist, map flows, write test cases and track vulnerabilities
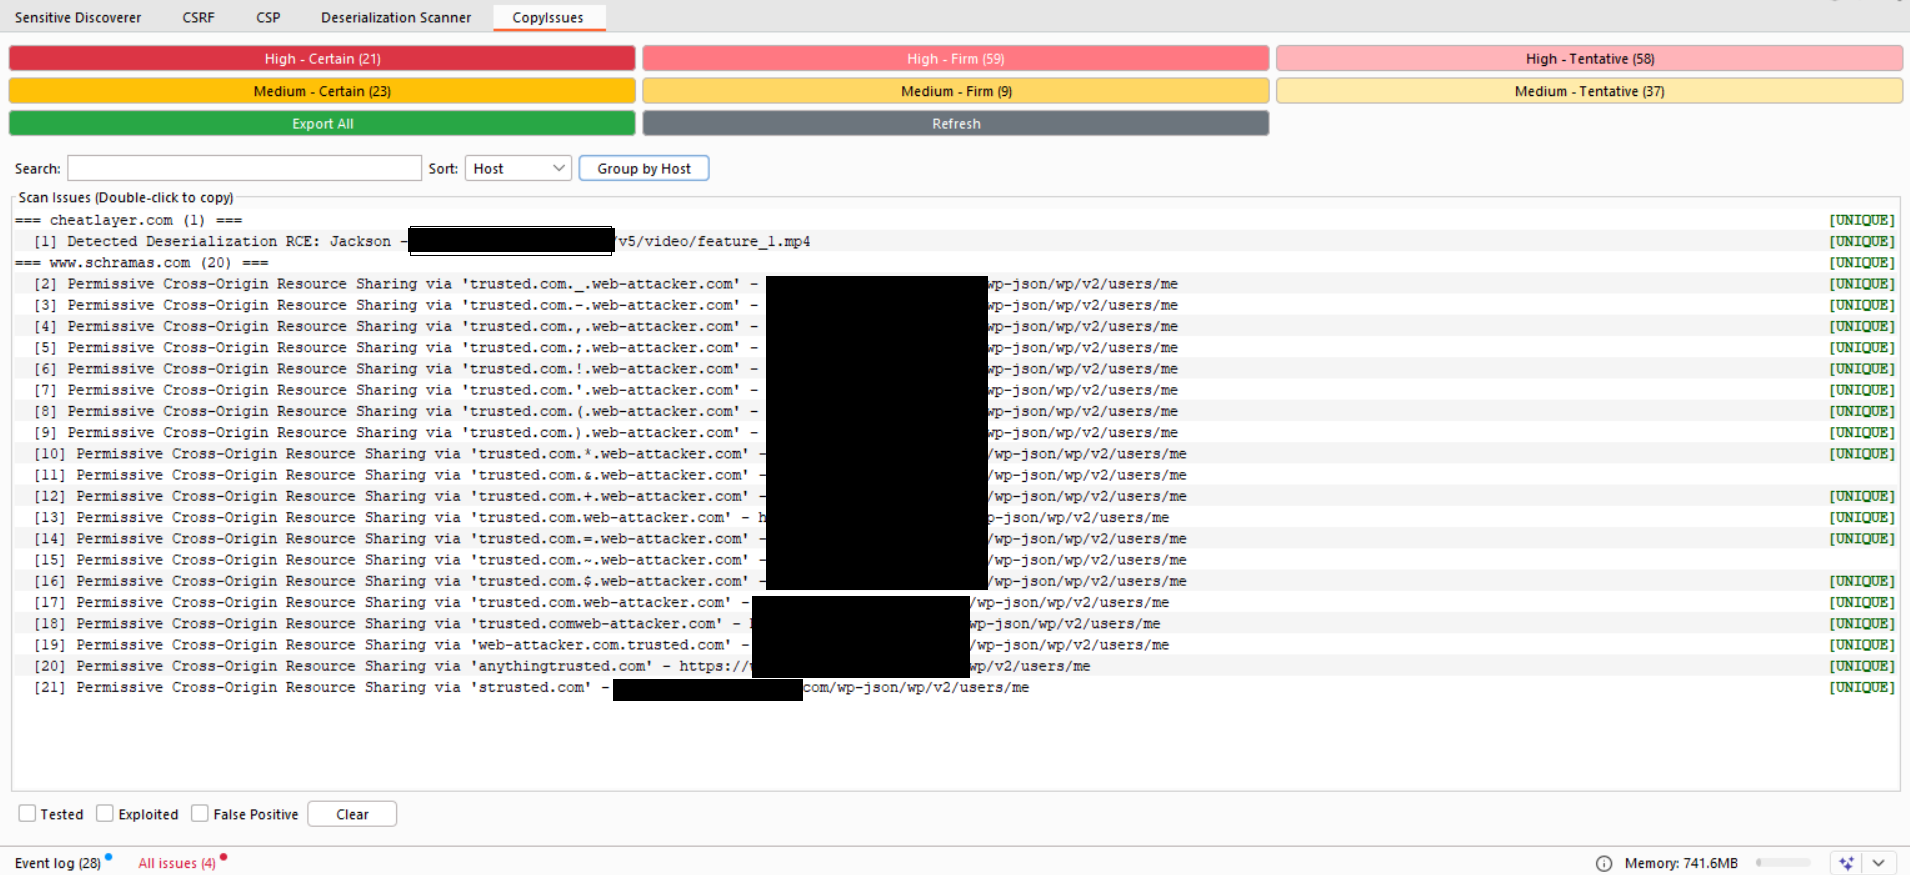 teycir/burpcopyissues
Burp suite extension that lets you easily copy issues
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
 projectdiscovery/collaborator
BurpSuite Standard/Private Collaborator Library
 loneyers/spring4shell
Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
 keith-amateur/cve-2022-1040
Save the trouble to open the burpsuite...
 egi08/cve-2024-10914
CVE-2024-10914_Manual testing with burpsuite
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…