
CVE-2026-24061
 k3ystr0k3r/cve-2026-24061
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
authenticationauthentication-authorizationcommand-and-control+8
3
k3ystr0k3r/cve-2026-24061A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers

 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 epsylon/prommetrix
Prommetrix can obtain relevant information from the instances of 'Node Exporter' executed by 'Prometheus'.
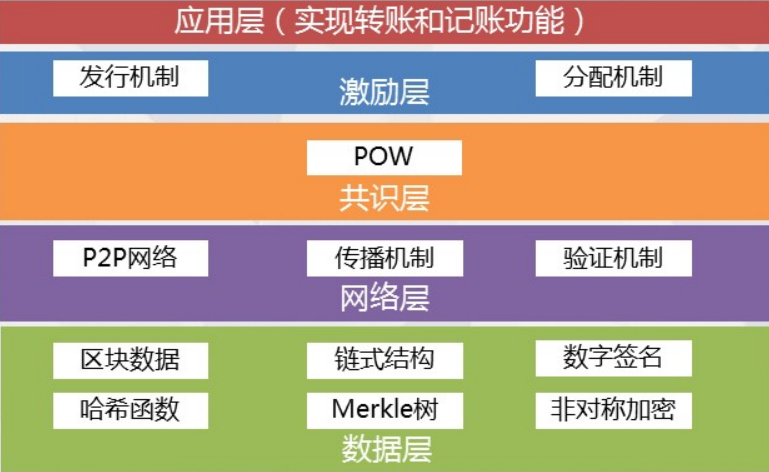 al1ex/blockchainconstruction
BlockChain Security Construction
 tausifzaman/cve-2026-3844
PoC exploit for CVE-2026-3844, a critical unauthenticated file upload vulnerability in the WordPress Breeze plugin leading to RCE.

 d3adp3nguin/cve-2023-33105-transient-dos-in-wlan-host-and-firmware
This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…
 binarymasc/cve-2026-46242
Aarch64 proof-of-concept checker for CVE-2026-46242 'Bad Epoll', triggering the Linux kernel epoll close-vs-close use-after-free race to validate…
 razureink/cve-2025-2783-chrome_sandbox_escape_reproduction
CVE Reproduction: cve-2025-2783-chrome_sandbox_escape_reproduction
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 tatosec/cve-2026-33017-langflop
CVE-2026-33017 Langflow RCE PoC
 george0papasotiriou/cve-2026-23002-5g-nas-message-buffer-overflow-in-gnodeb
Simulated 5G gNodeB NAS parser with stack buffer overflow PoC for CVE-2026-23002; a crafted NAS message triggers remote code execution.
 l0lsec/cve-2020-5148
CVE-2020-5148 - Forced Authentication in the SonicWall UTM SSO Agent. The agent probes unvalidated workstations as Domain Admin, so one outbound web…
 0xbassiouny1337/cve-2024-42009
This script exploits a stored XSS vulnerability (CVE-2024-42009) in Roundcube Webmail version 1.6.7. It injects a malicious payload into the webmail…
 tungduongnt/cve-2014-0160.
Docker-based lab environment for exploiting CVE-2014-0160 (Heartbleed) to leak sensitive memory from nginx web servers, with Snort IDS detection…
 hsw109/cve-2018-10933
Education purpose for CVE-2018-10933